
Magisk
 topjohnwu/magisk
Android customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
android-securitymobile-securityprivilege-escalation
topjohnwu/magiskAndroid customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 google/artemis
Natural-language Android automation agent that drives real devices via ADB, captures Logcat and screenshots, and exposes an MCP server for AI IDEs…
 r0rt1z2/ghostlock
Kernel root exploit (CVE-2026-43499) for some Amazon devices
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 zenyxx-xd/rootmyvivo
One-click root for vivo/iQOO devices on locked bootloader | CVE-2026-43499 + KernelSU
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
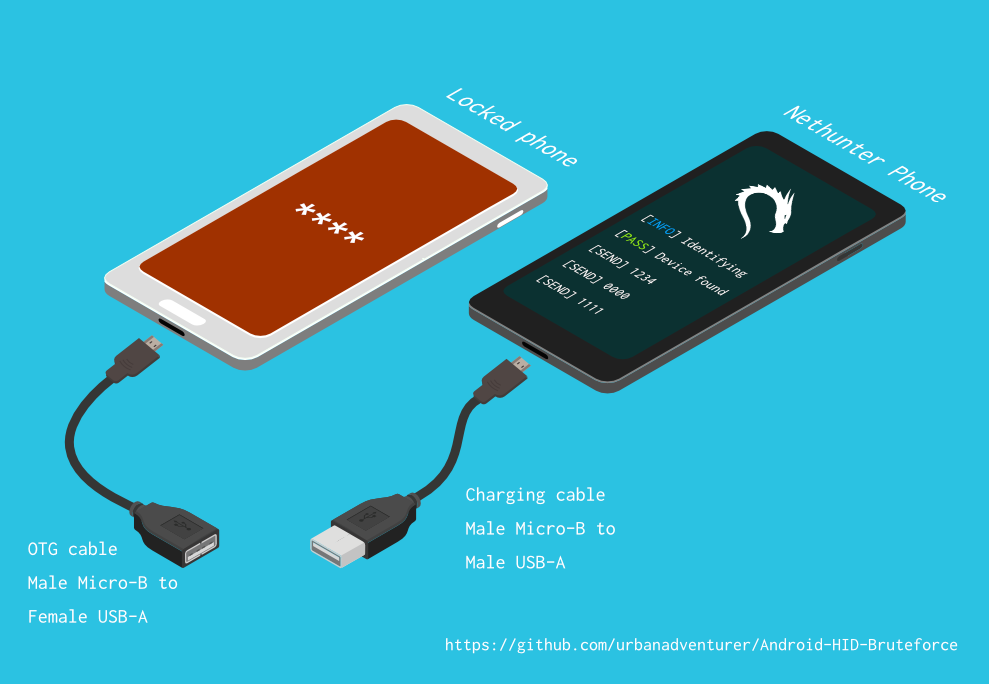 urbanadventurer/android-pin-bruteforce
Unlock an Android phone (or device) by bruteforcing the lockscreen PIN. Turn your Kali Nethunter phone into a bruteforce PIN cracker for Android…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 joinchang/ghostlock-oneplus
GhostLock (CVE-2026-43499) kernel exploit for Android devices with locked bootloader
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 zenyxx-xd/rootmyvivo-exploit
GhostLock (CVE-2026-43499) exploit fork for RootMyVivo Neo — iQOO Neo 11 (PD2520, SM8750, 6.6.89). For authorized research on own devices only.
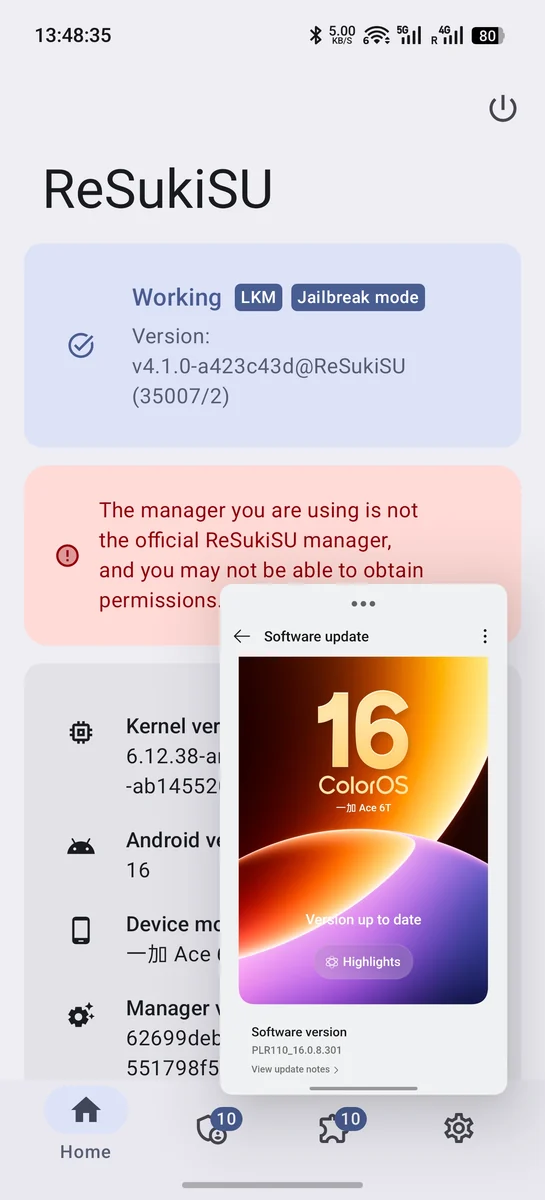 xiaobailovesstirring/ghostlock-k419-adapter
GhostLock (CVE-2026-43499) adapter for 4.19.152-perf+ Android kernel
 cuteaplane/ghostlock-for-oneplus15t
(CVE-2026-43499)内核漏洞利用程序,适用于未解锁 Bootloader 的一加15T.
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis