Archived
AhMyth-Android-RAT
 ahmyth/ahmyth-android-rat
Android Remote Administration Tool
android-securitycommand-and-controlpayload-generation+3
5.2k
ahmyth/ahmyth-android-ratAndroid Remote Administration Tool
 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 entysec/ghost
Ghost Framework is an Android post-exploitation framework that exploits the Android Debug Bridge to remotely access an Android device.
 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 trinadh465/frameworks_base_aosp10_r33_cve-2023-20909
Android framework base repository containing patches and analysis for CVE-2023-20909, a vulnerability in the Android operating system.
 trinadh465/platform_frameworks_base_cve-2023-21281
Android platform framework patch for CVE-2023-21281, addressing a security vulnerability in the Android framework.
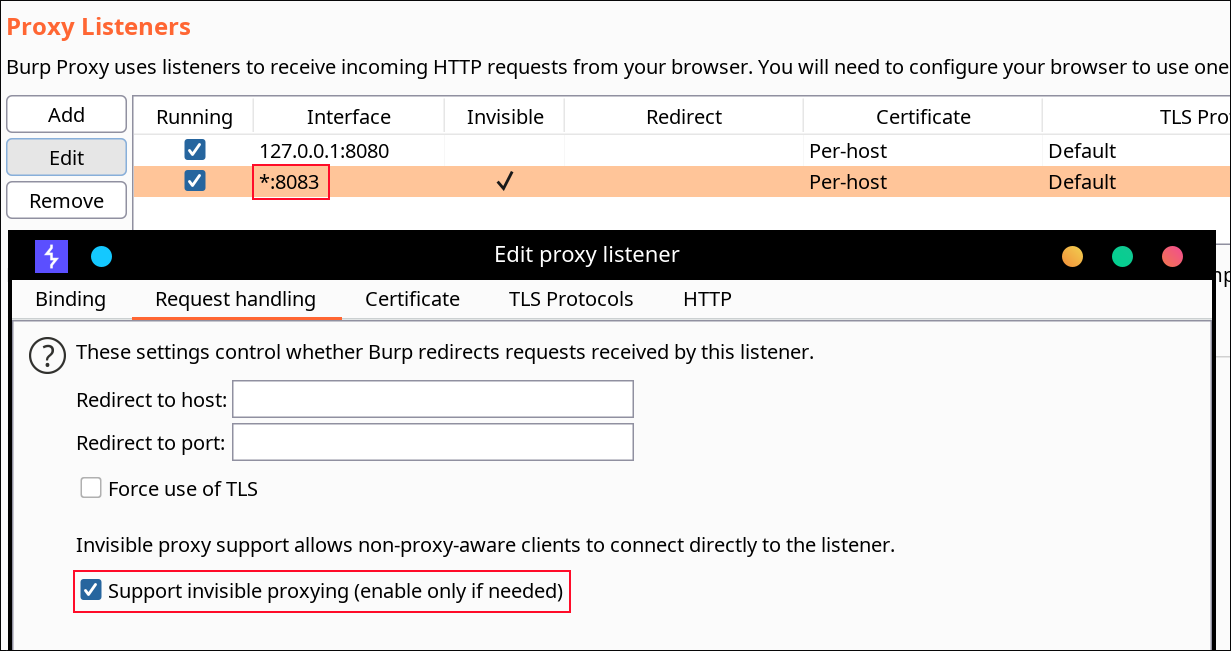 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
 trinadh465/frameworks_base_cve-2023-20944
Analyzes and patches Android framework vulnerability CVE-2023-20944, providing security fixes for the Android platform.
 abrarkhan/g3_frameworks_av_cve-2024-0023
Proof-of-concept exploit for CVE-2024-0023 in Android's frameworks/av, implemented in C++ to demonstrate the media framework vulnerability.