
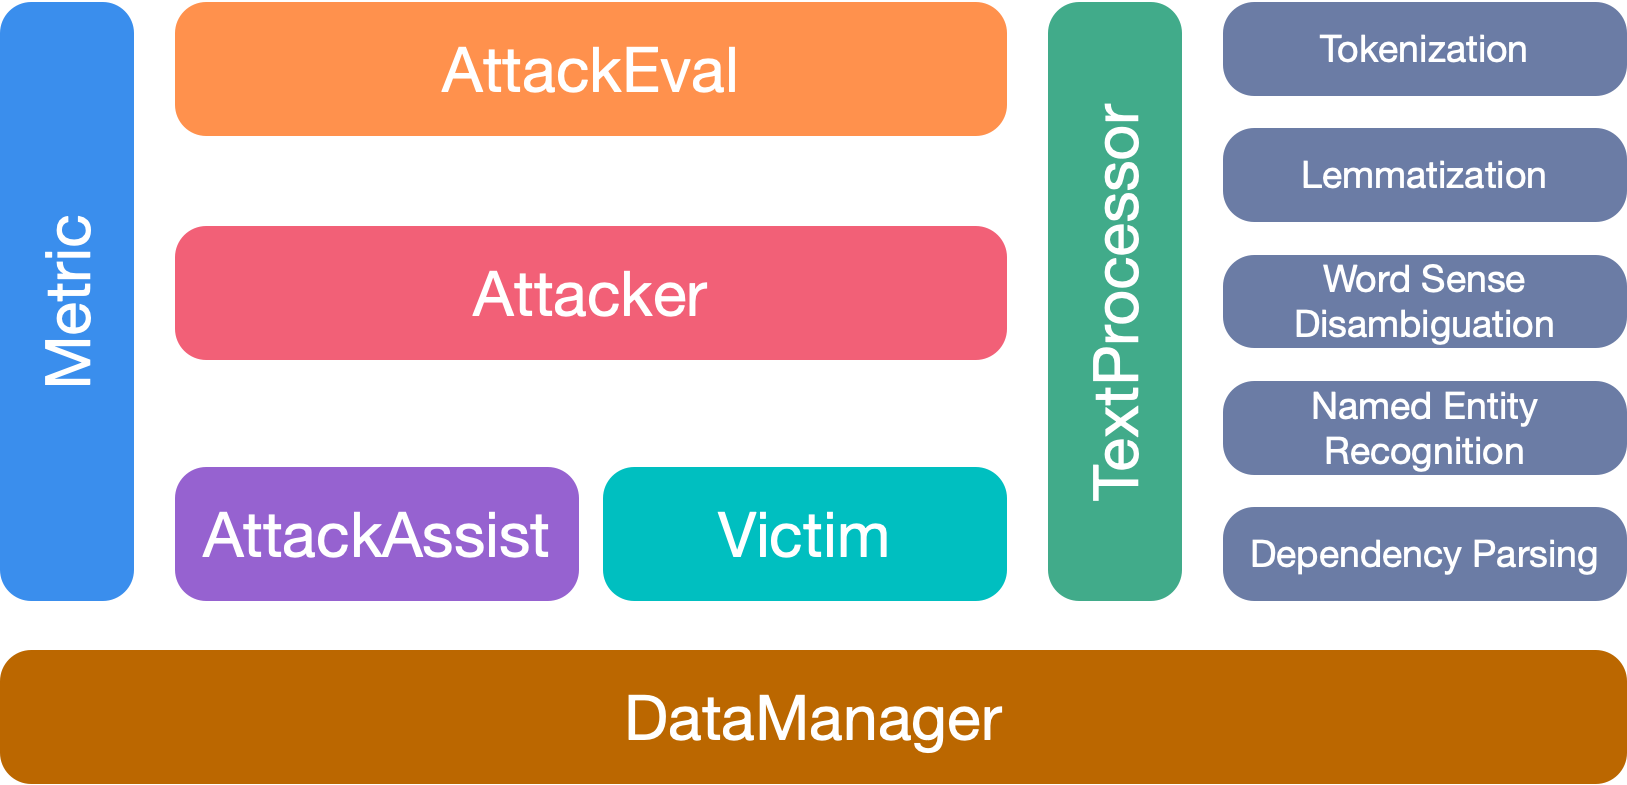
OpenAttack
 thunlp/openattack
An Open-Source Package for Textual Adversarial Attack.
adversarial-attackai-securityeducation+2
thunlp/openattackAn Open-Source Package for Textual Adversarial Attack.
 swe-agent/swe-agent
LLM-powered agent that autonomously fixes GitHub issues, finds cybersecurity vulnerabilities, and solves CTF challenges using configurable tool-use…
 appsecco/vulnerable-mcp-servers-lab
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.
 bishopfox/local-llm-ctf
A small go harness that uses Ollama to orchestrate LLMs in a restricted process flow
 projectdiscovery/openrisk
openrisk is a tool that generates a risk score based on the results of a Nuclei scan.
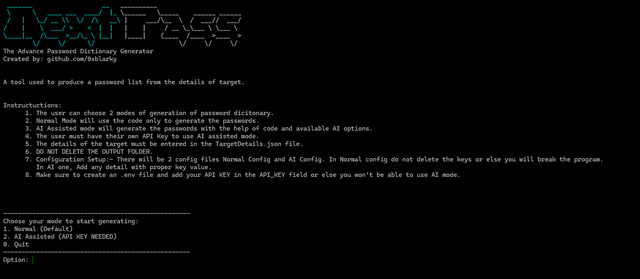 0xblarky/nextpass
A tool which can be used to generate password list or dictionary from the details of the target
 owasp/www-project-top-10-for-large-language-model-applications
OWASP Top 10 for Large Language Model Apps (Part of the GenAI Security Project)
 robertcprice/ncpu
Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
 cisco-talos/deceive
DECeption with Evaluative Integrated Validation Engine (DECEIVE): Let an LLM do all the hard honeypot work!
 george0papasotiriou/cve-2026-23001-hugging-face-transformers-model-deserialization-arbitrary-code-via-pickle-
Proof-of-concept for CVE-2026-23001: demonstrates RCE through unsafe pickle deserialization in Hugging Face Transformers by crafting a malicious…
 a3-n/xpfarm
Free XP on bug bounty, vulnerability scanning by wrapping well maintained tools, to perform automated tests. Alongside AI agents for binary analysis,…
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
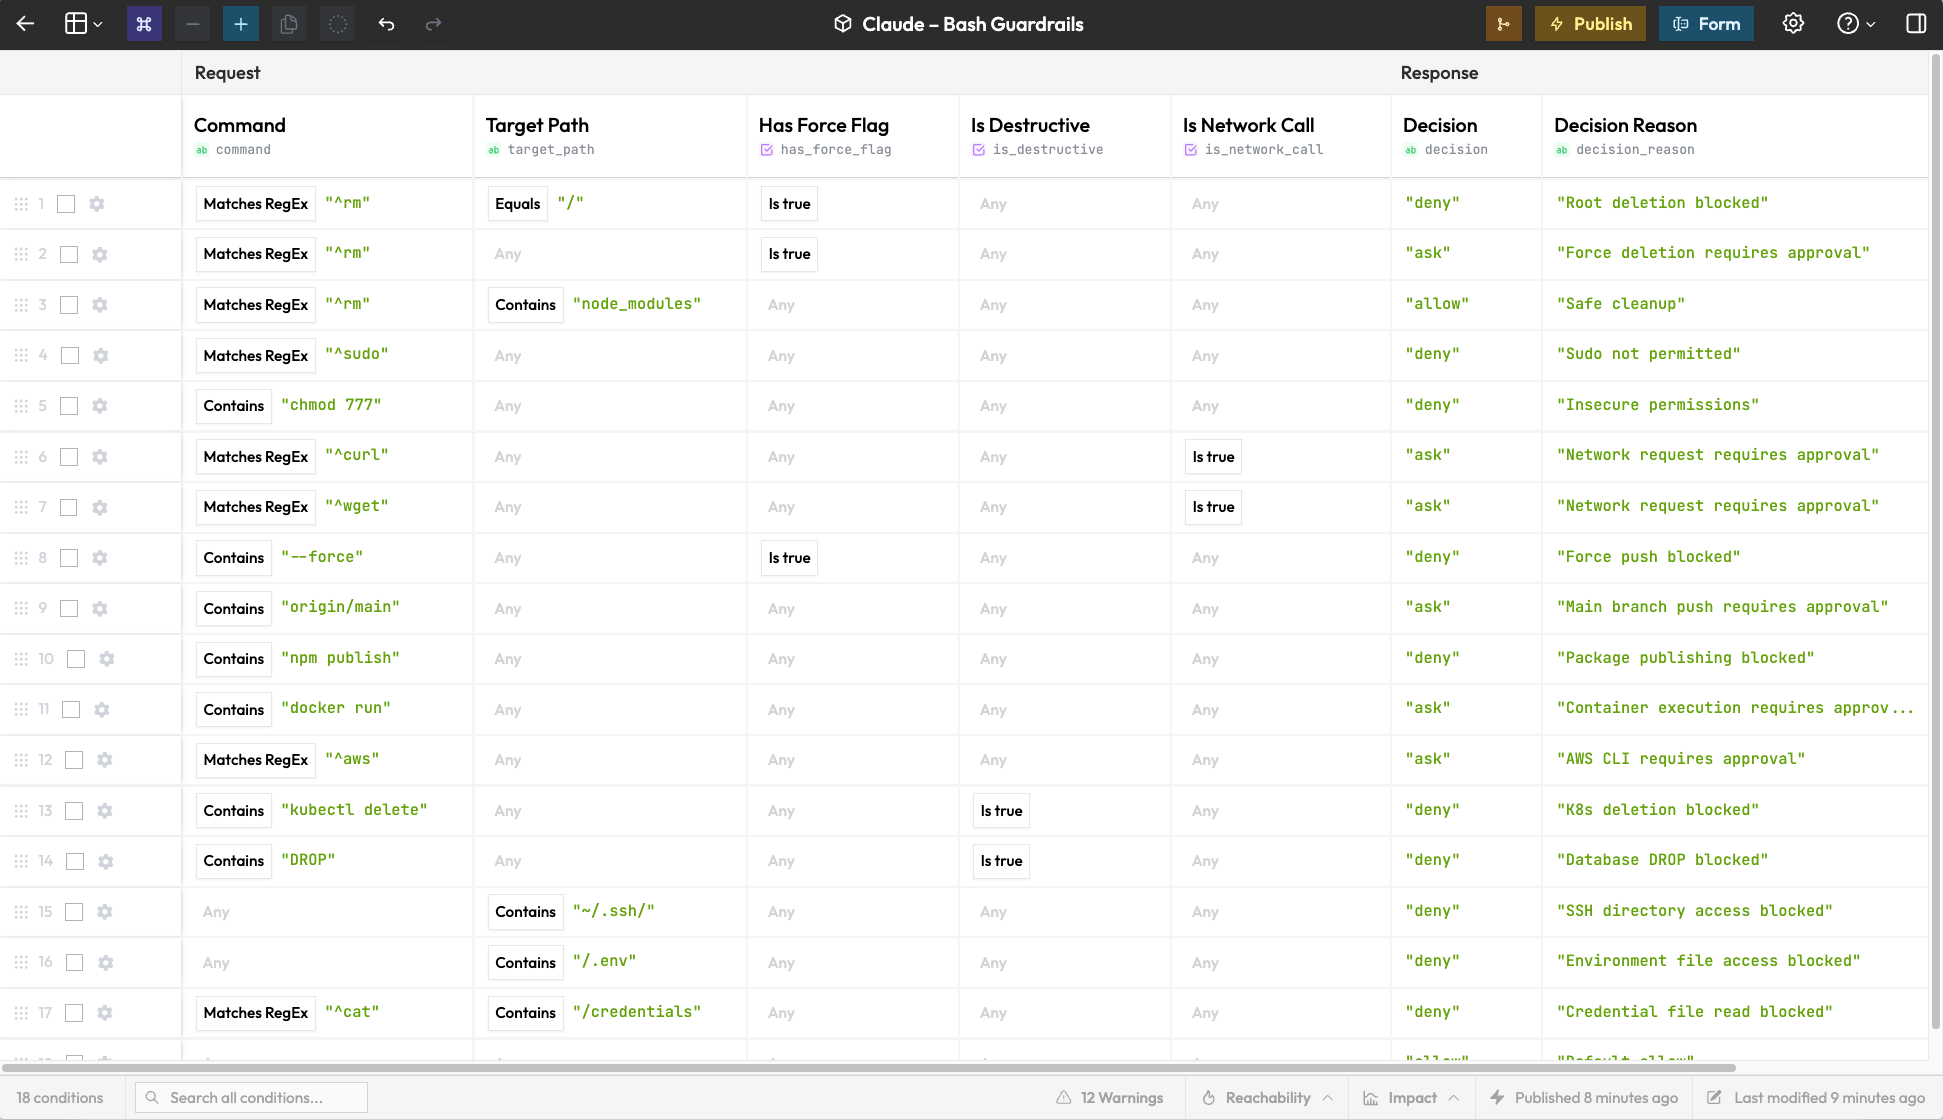 rulebricks/claude-code-guardrails
Real-time guardrails for Claude Code tool calls.