
power-pwn
 mbrg/power-pwn
An offensive/defense security toolset for discovery, recon and ethical assessment of AI Agents
ai-securitycloud-securityinformation-gathering+8
mbrg/power-pwnAn offensive/defense security toolset for discovery, recon and ethical assessment of AI Agents
 shuvonsec/claude-bug-bounty
AI-powered bug bounty hunting toolkit that works with or without subscription.
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 microsoft/whatthehack
A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
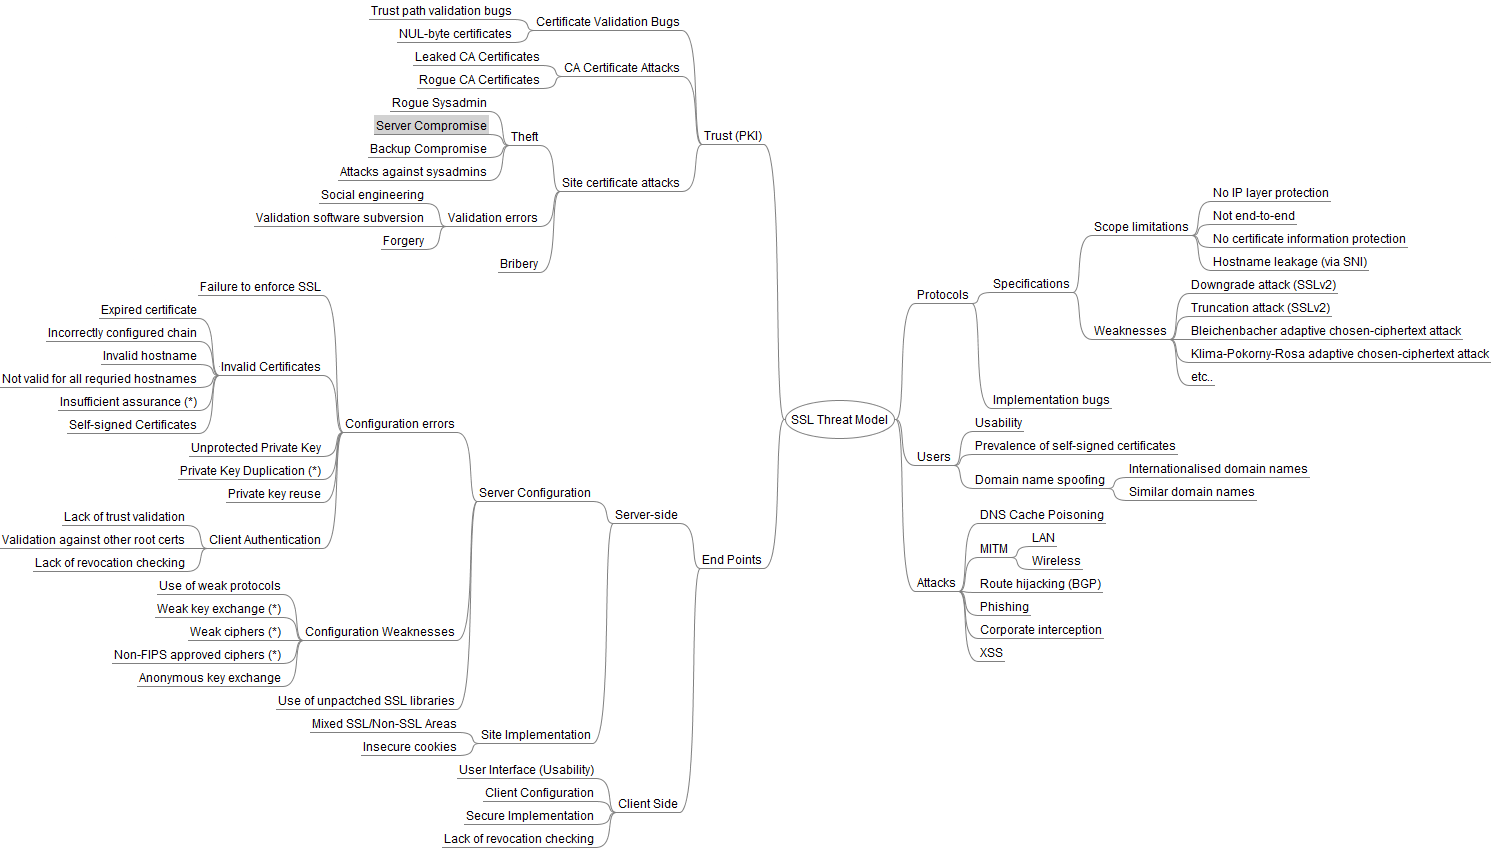 taleliyahu/threat_model_examples
A collection of real-world threat model examples across various technologies, providing practical insights into identifying and mitigating security…
 osxninja/cybersecurity-projects
This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
 makerchecker/makerchecker
Open-source security gateway & static scanner for AI agents. Enforce role-based access control (RBAC), human-in-the-loop approvals, segregation of…
 backbay-labs/hush
Portable security rules for the action boundary of AI agents
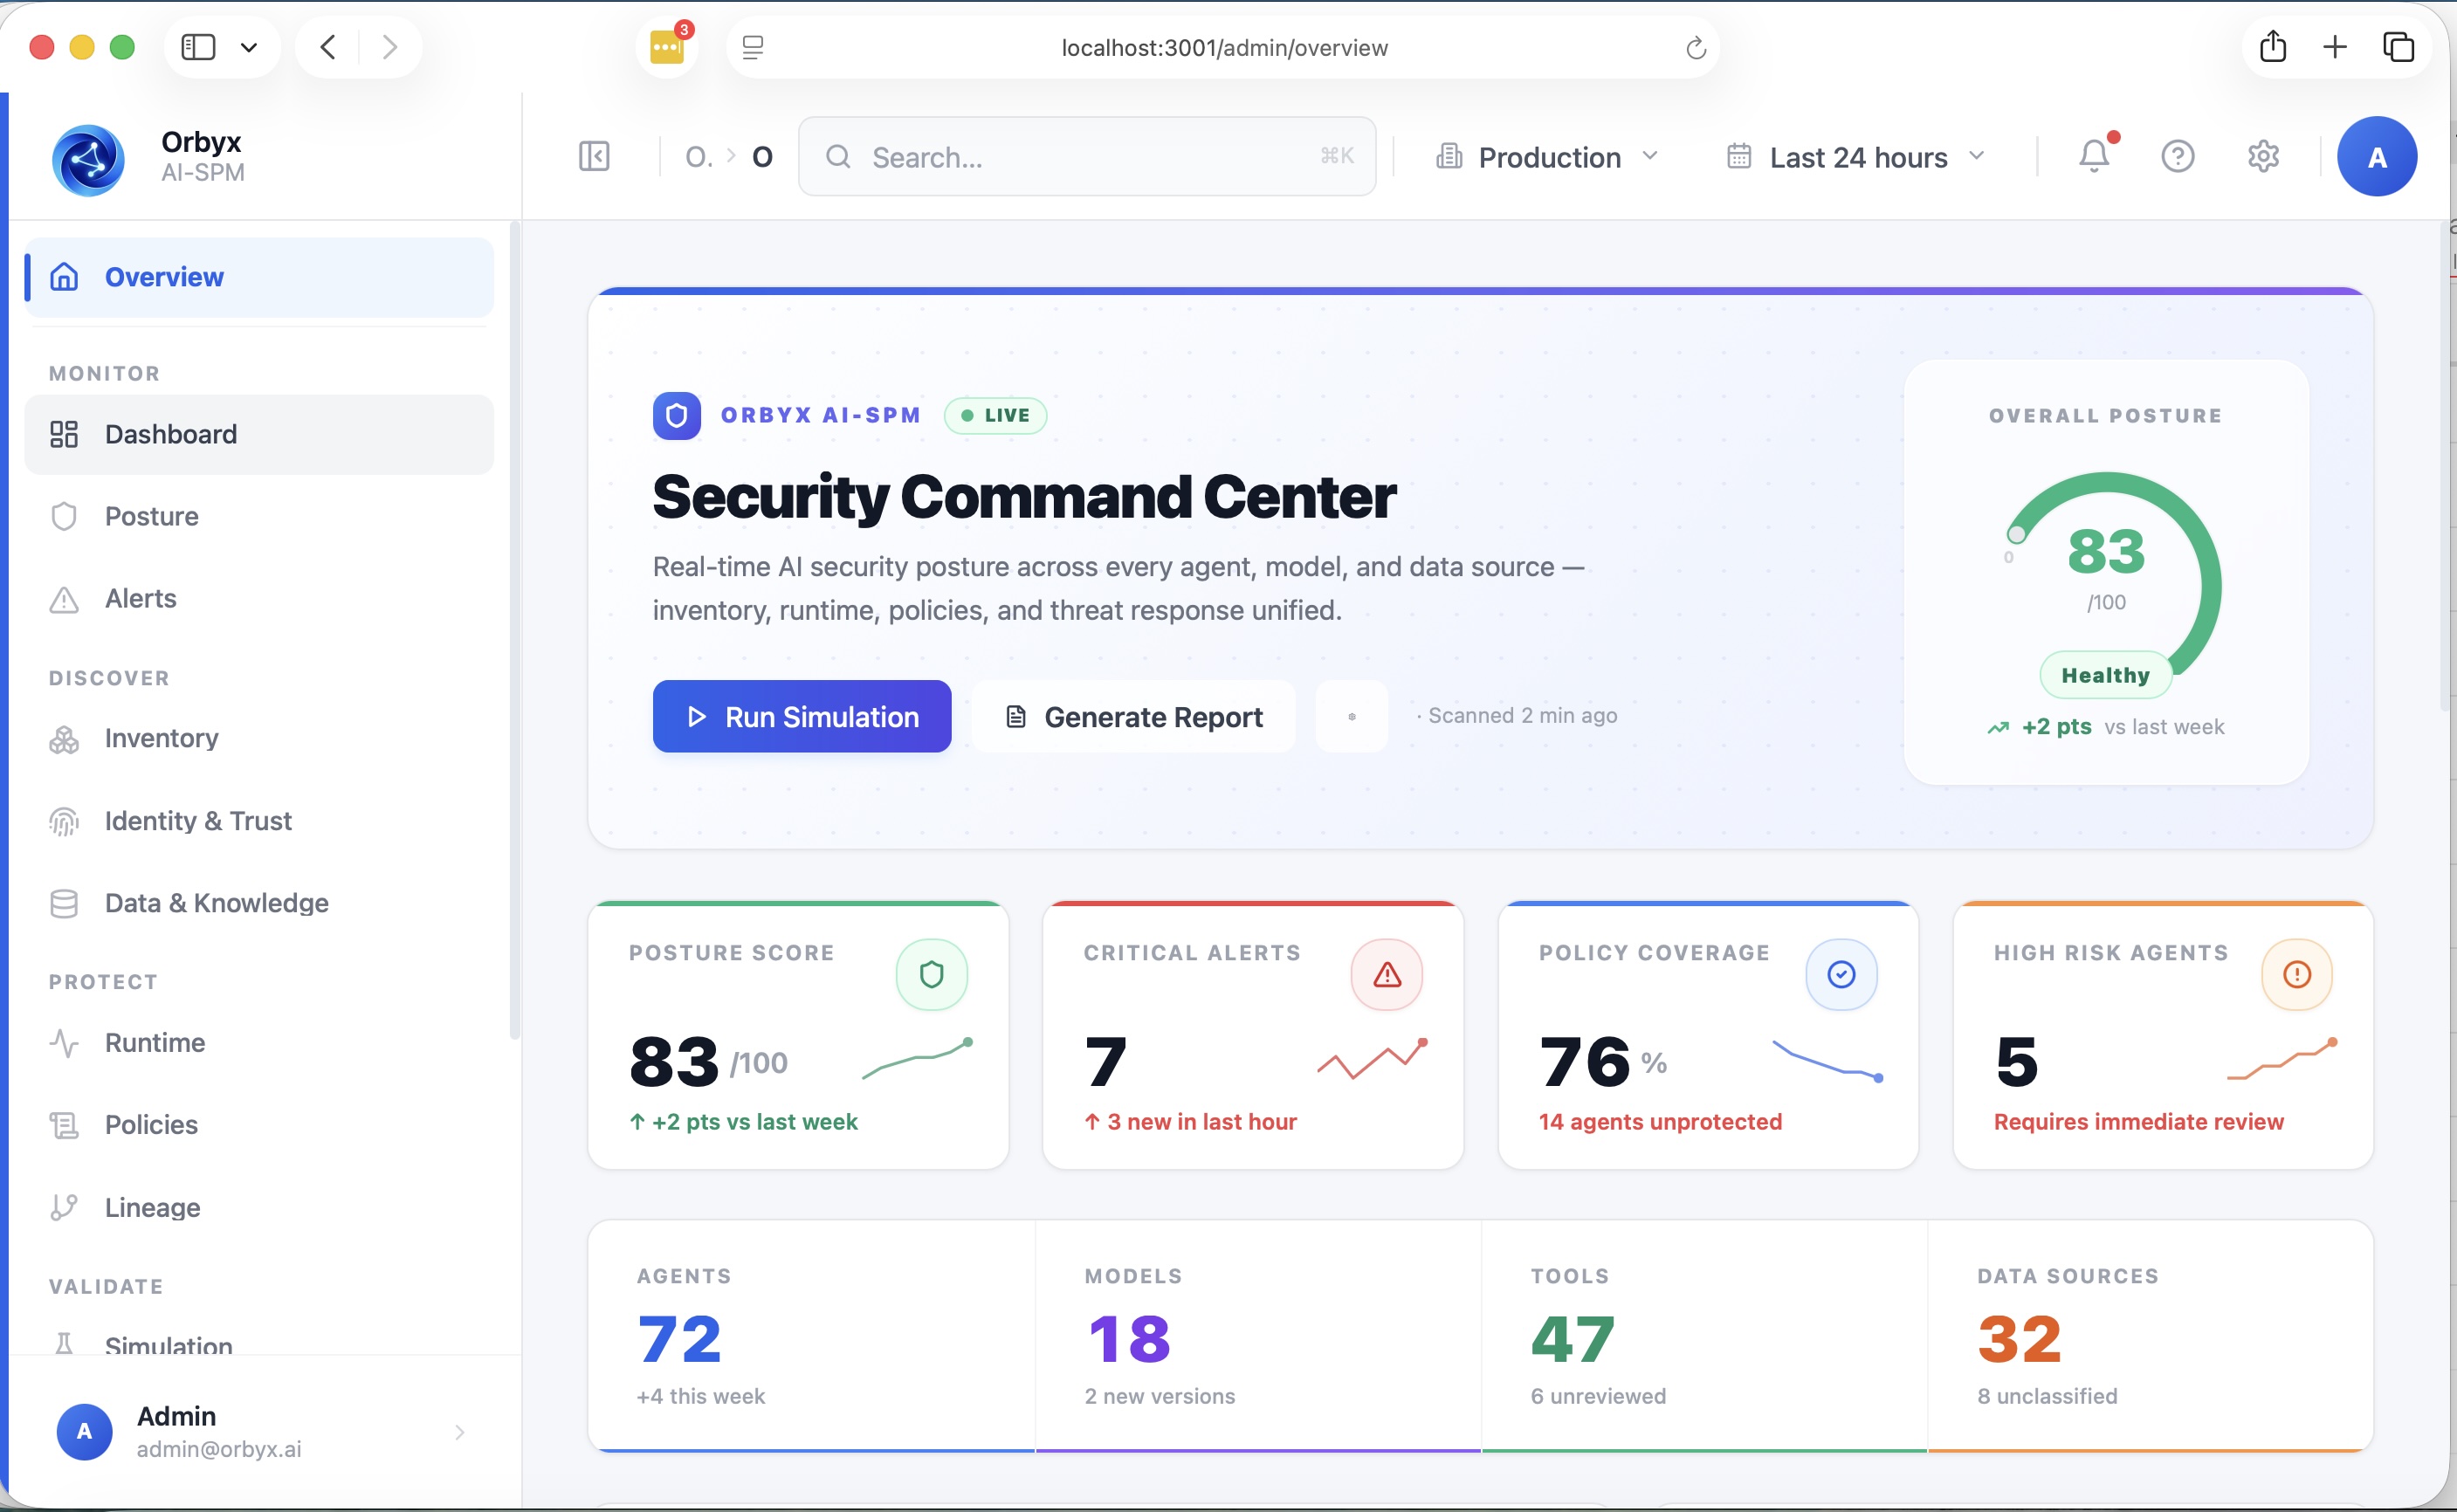 dshapi/ai-spm
This opensource project dedicated to implementing Enterprise level AI-SPM. By doing so organizations can proactively protect their AI systems from…
 sorami-consulting-au/ai-kubernetes-helm-chart-security
Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 sushank05/mcp-doorman
A lightweight mcp to prevent poisoning CVE (CVE-2025-54136), researchers hijacking Claude Code/Copilot/Gemini via prompt injection, and hundreds of…
 ololadeabiola03/aisecplus-week01-servicenow-ai-security-incident
Research and analysis of the ServiceNow Virtual Agent vulnerability (CVE-2025-12420), including attack flow, MITRE ATT&CK mapping, detection…
 db-ol/cuaharm
Benchmark for evaluating safety risks of computer-using agents, with 104 realistic misuse scenarios across seven malicious categories, supporting…
 comerc/cve-2025-68664
Detailed disclosure of CVE-2025-68664, a critical deserialization vulnerability in LangChain core allowing secret exfiltration and potential RCE via…