CTT-Serverless-RCE-v1.0---Convergent-Time-Theory-Enhanced-MCP-Exploit

Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…

Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…

Professional PoC for CVE-2025-59536 and related CVEs. Demonstrates an MCP Tool Confirmation Prompt Misrepresentation in Anthropic Claude_Code leading…

Detailed security advisory for CVE-2025-492025, documenting a UI misrepresentation vulnerability in Copilot AI that injects unintended hyperlinks…


Benign, self-contained reproduction of CVE-2026-61732 (Decepticon ChatML role-boundary forgery)

Knowns 0.30.0: Unauthenticated Header Injection Grants AI Agent Unrestricted Access to Host Filesystem

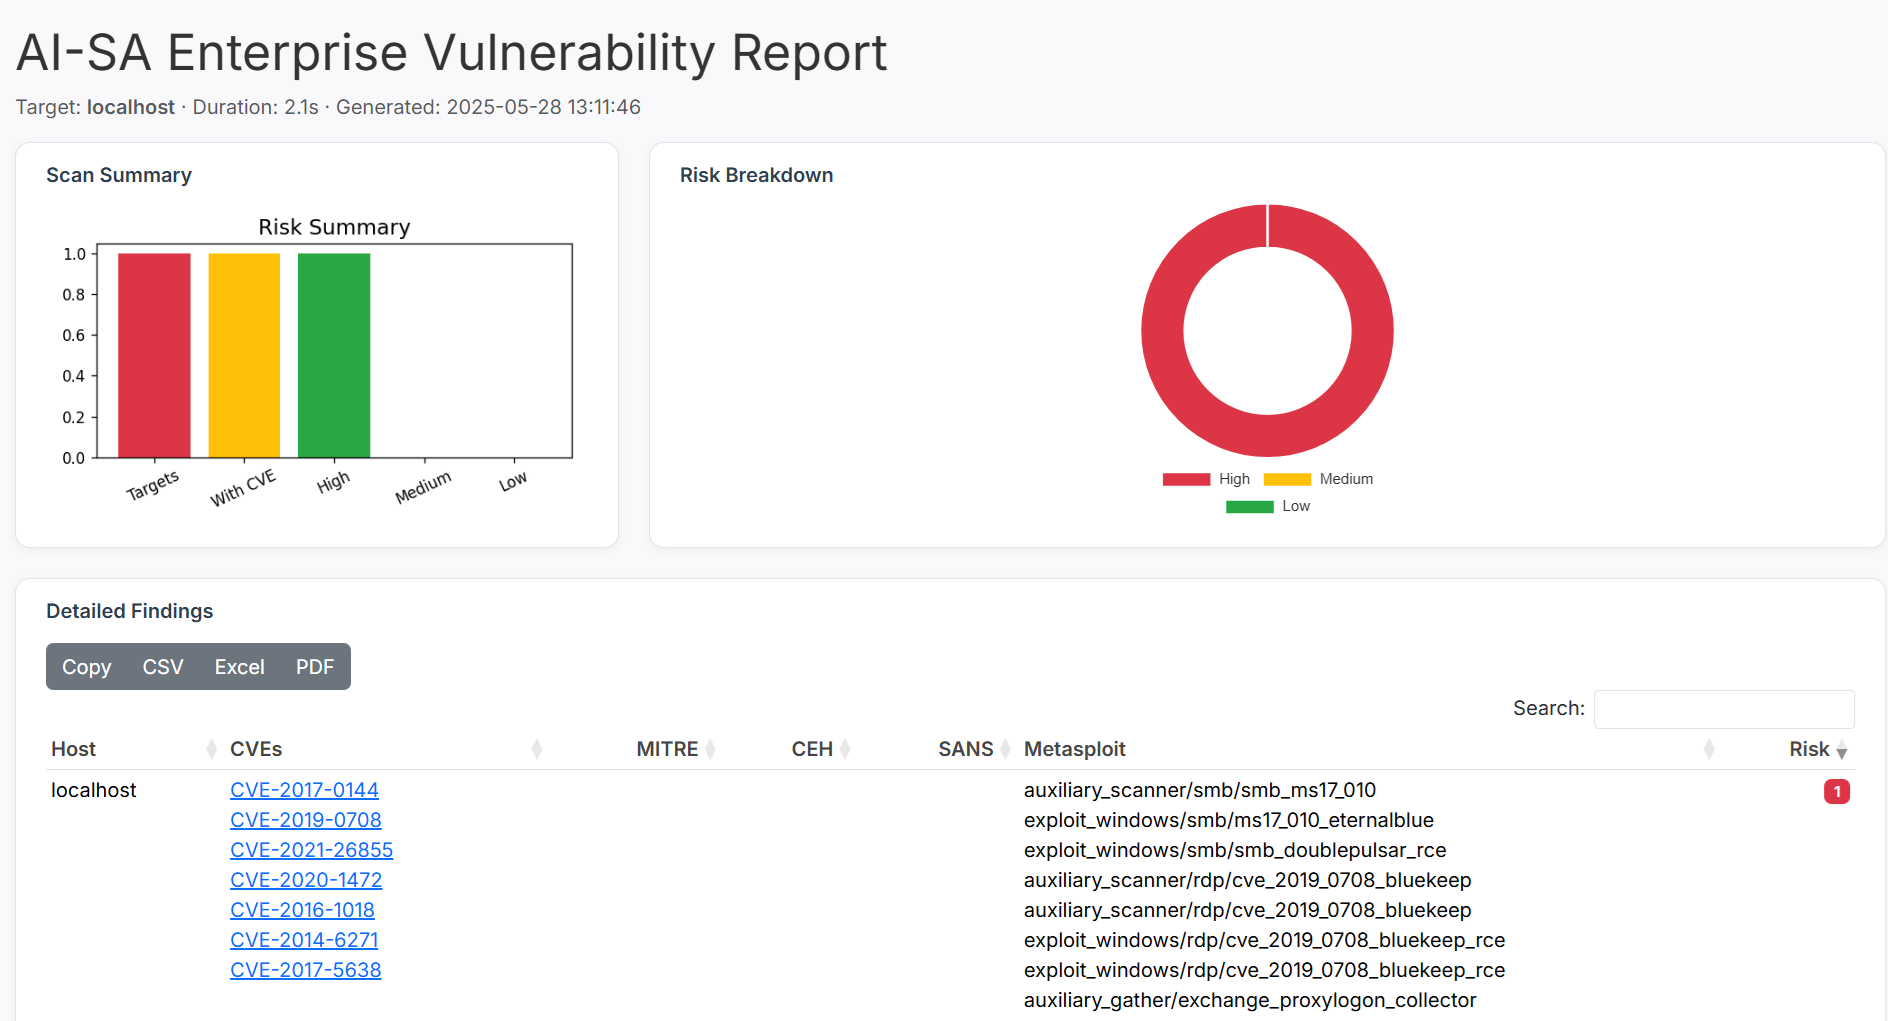
AISA-Scanner is an AI-powered autonomous vulnerability scanner that maps CVEs to metasploit exploits, MITRE, CEH, and SANS, delivering intelligent,…

Docker Container Escape POC via mlx-metal importlib

Collection of CVE(work) on tenserflow binary pwning it

Research and analysis of the ServiceNow Virtual Agent vulnerability (CVE-2025-12420), including attack flow, MITRE ATT&CK mapping, detection…

Black-box test whether an LLM chatbot is vulnerable to markdown/HTML exfil (CVE-2025-32711 class). Spins up a sink, sends payloads, renders in…


OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…

Locally-hosted, air-gapped VAPT platform that runs 8 parallel scanning modules, deterministically scores findings with CVSS v3.1, and generates PDF…

Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)

Proof-of-concept demonstrating CVE-2026-17351 SQL injection bypass in pgAdmin 4's AI Assistant via sqlparse/PostgreSQL lexer differential, including…

Security Advisory: Stored Cross-Site Scripting Via Agent Messages Leading To Session Token Theft (openclaw-dashboard)

A prompt injection in a code‑review bot that executes AI‑generated fixes in a sandbox. The sandbox uses a blacklist to prevent dangerous commands,…