
ironcurtain
 provos/ironcurtain
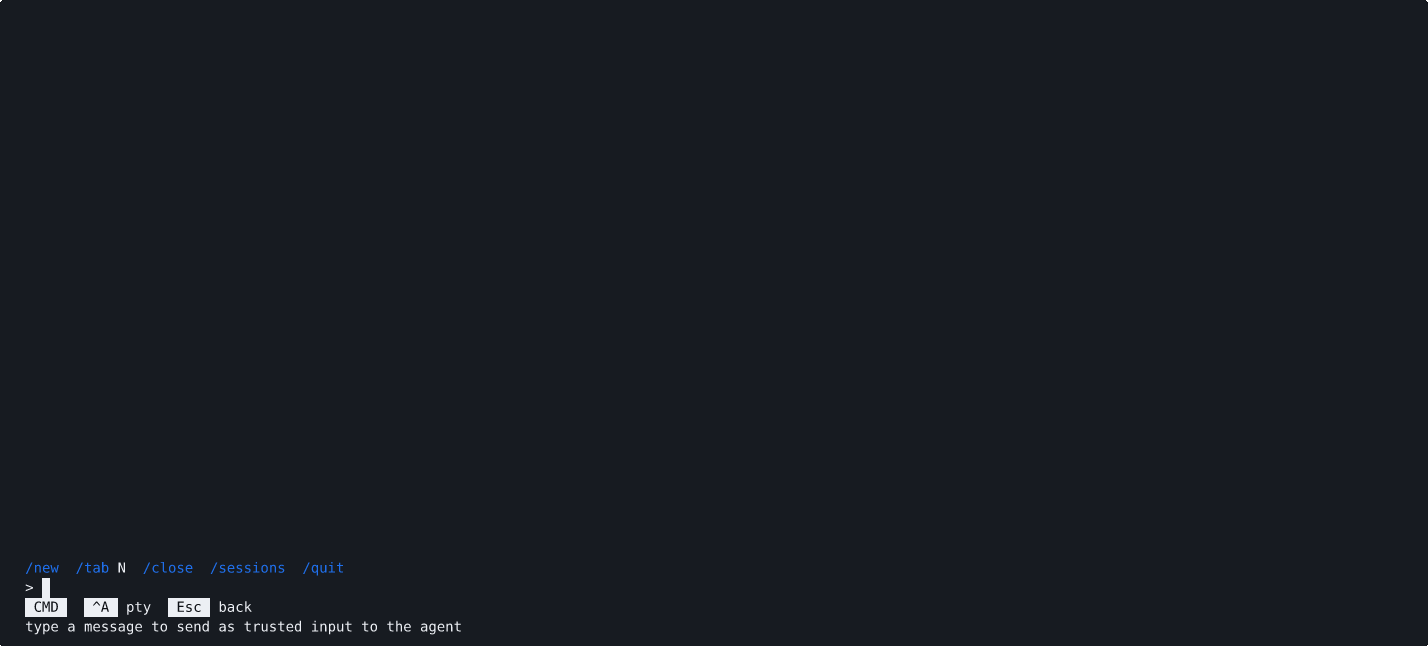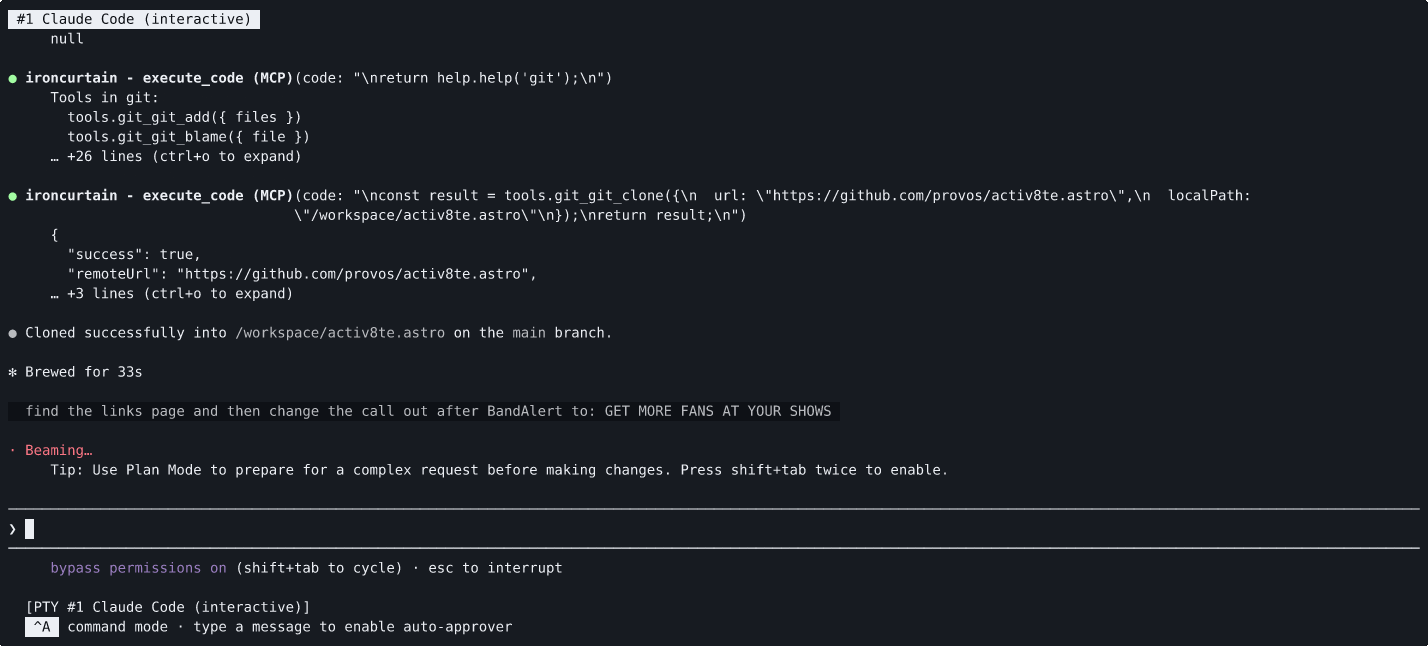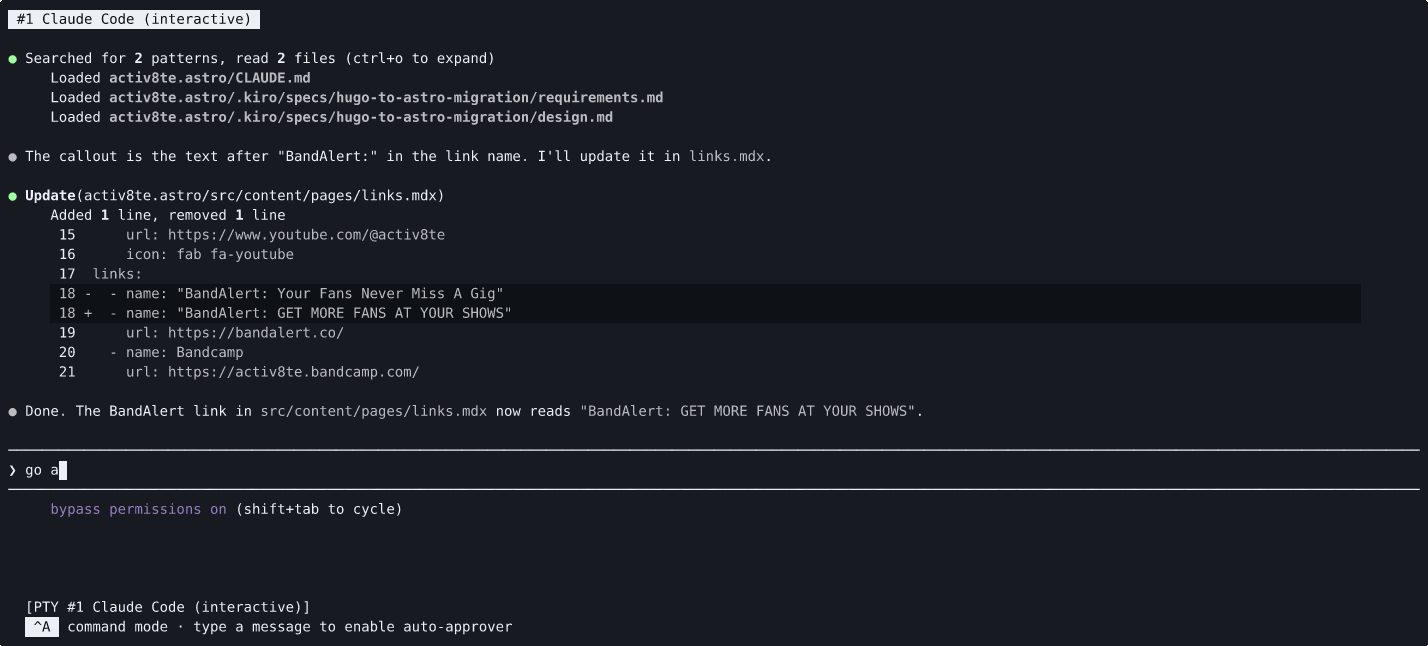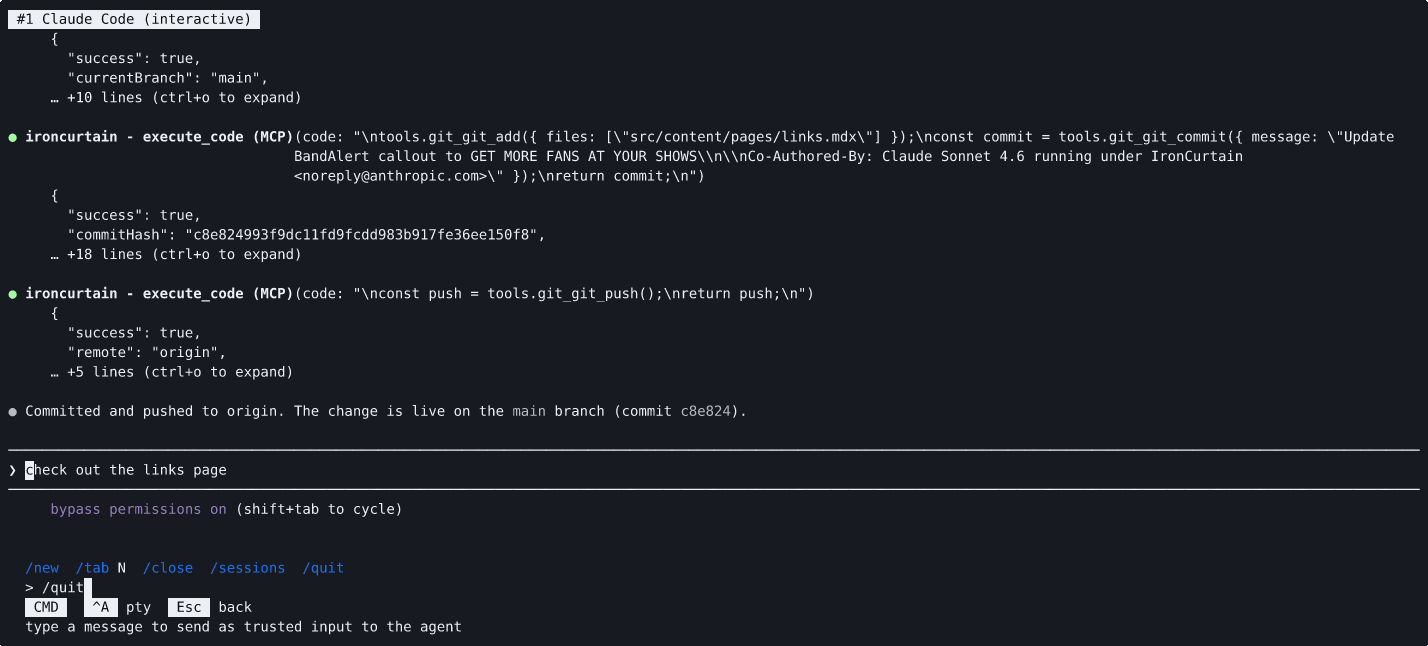
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)
ai-securitycontainer-securitydynamic-analysis-sandboxing+3
609
provos/ironcurtainA secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)
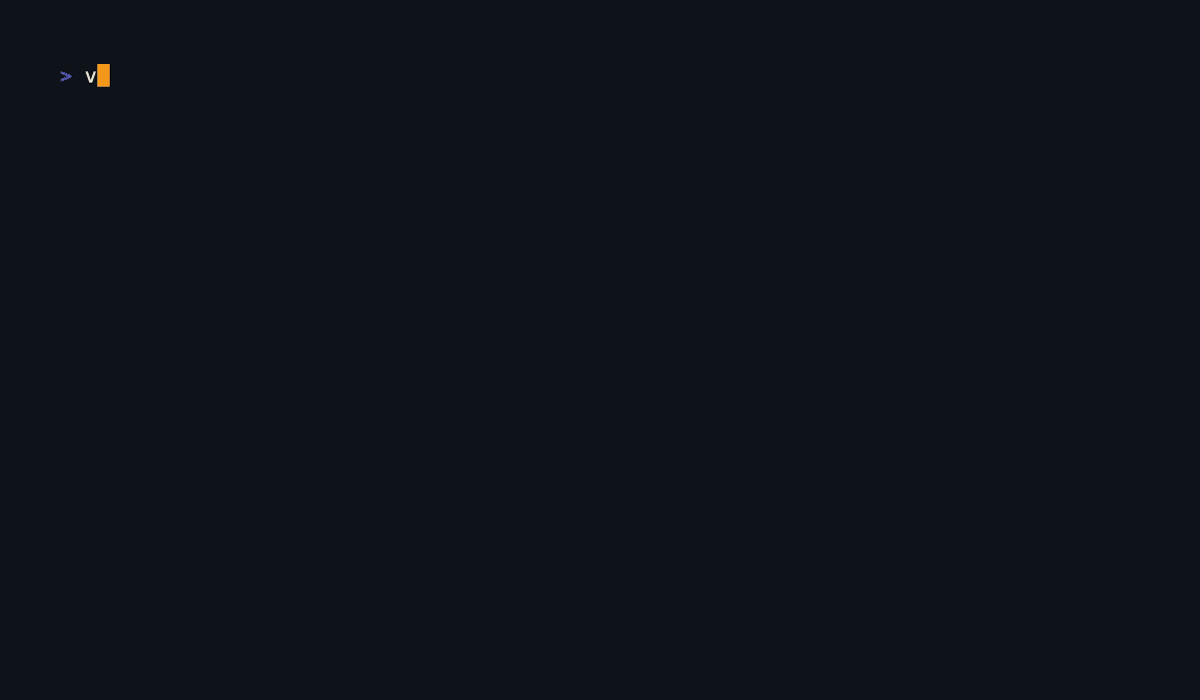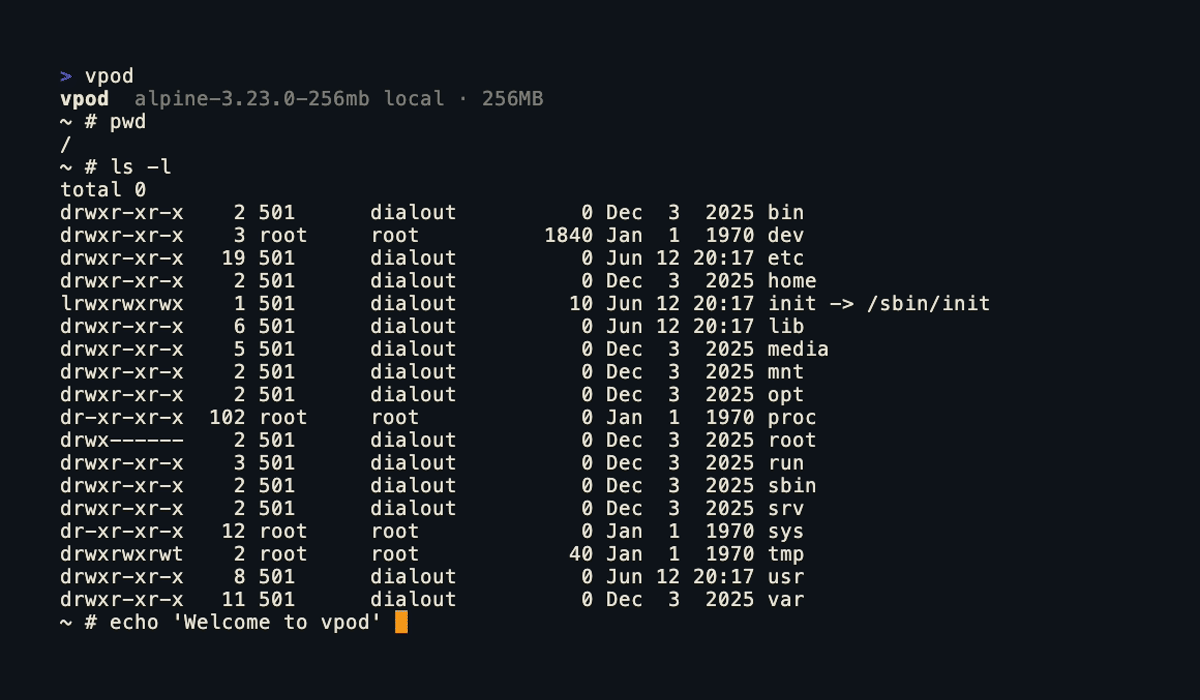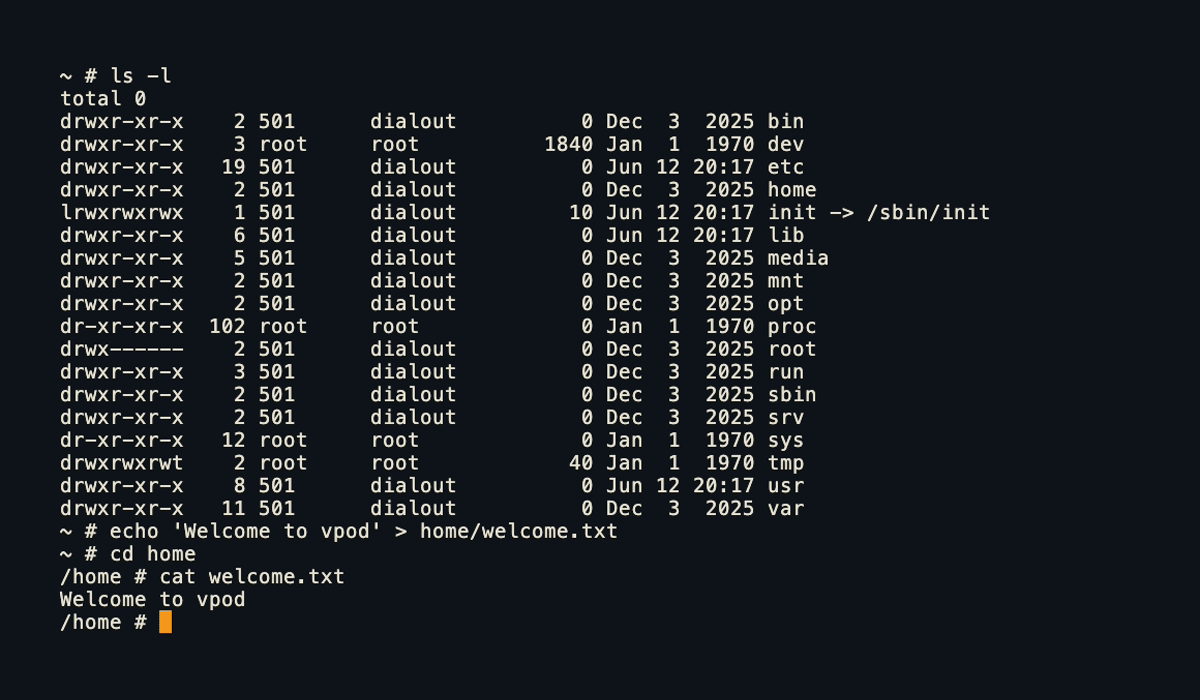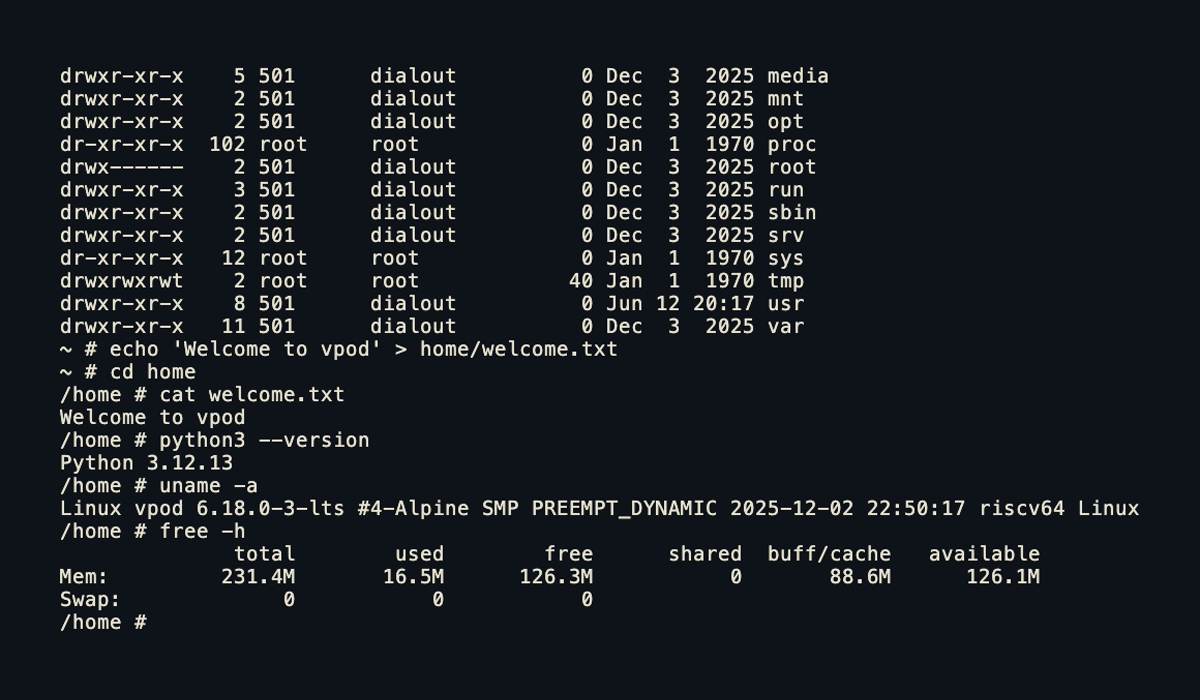 capsulerun/vpod
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 alixiacf/hpim-training-lab
Trained to Escalate: Forensic Analysis and Local Replication of RLHF-Induced Privilege Escalation in AI Agents (CVE-2026-65616)
 skorokithakis/stavrobot
An AI personal assistant with a focus on security.
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 iaga-team/iaga-sentinel
Cryptographically signed, replay-verifiable evidence layer for AI agents. Governs actions in the loop, produces Ed25519-signed receipts linked into a…
 xtuc/airgap
Security for the modern age of AI: defend against bad AI agents and malicious npm packages
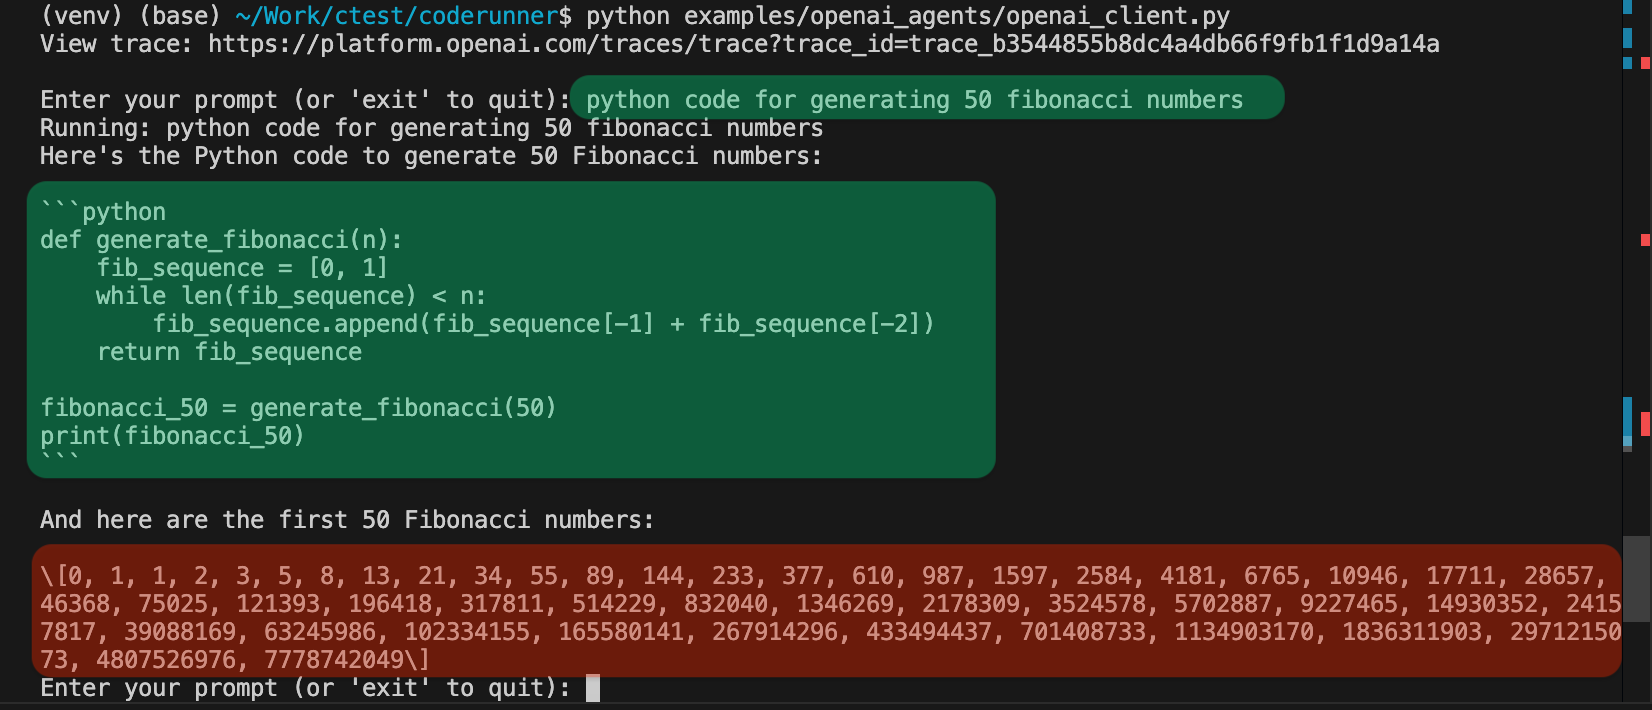 instavm/coderunner
A local sandbox for your AI agents
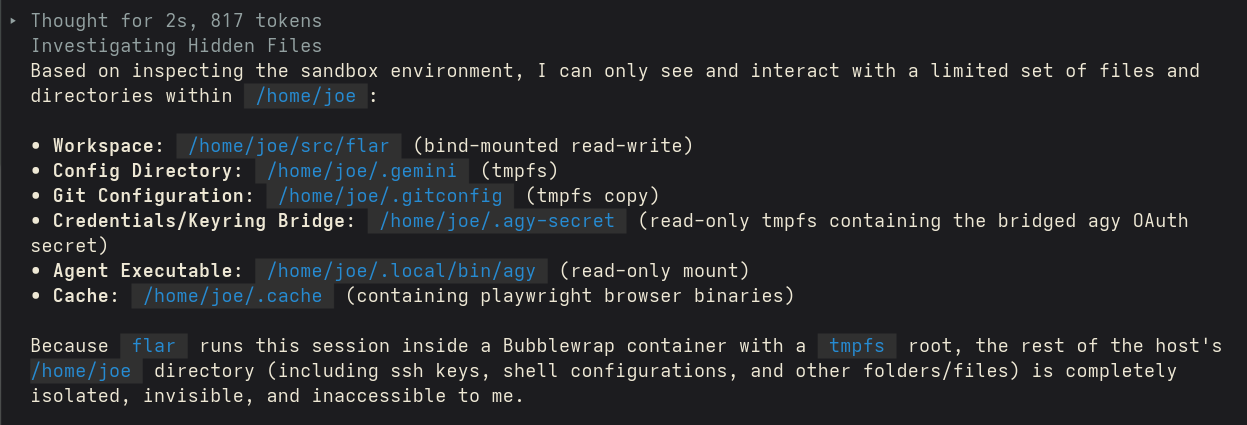 swelljoe/flar
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
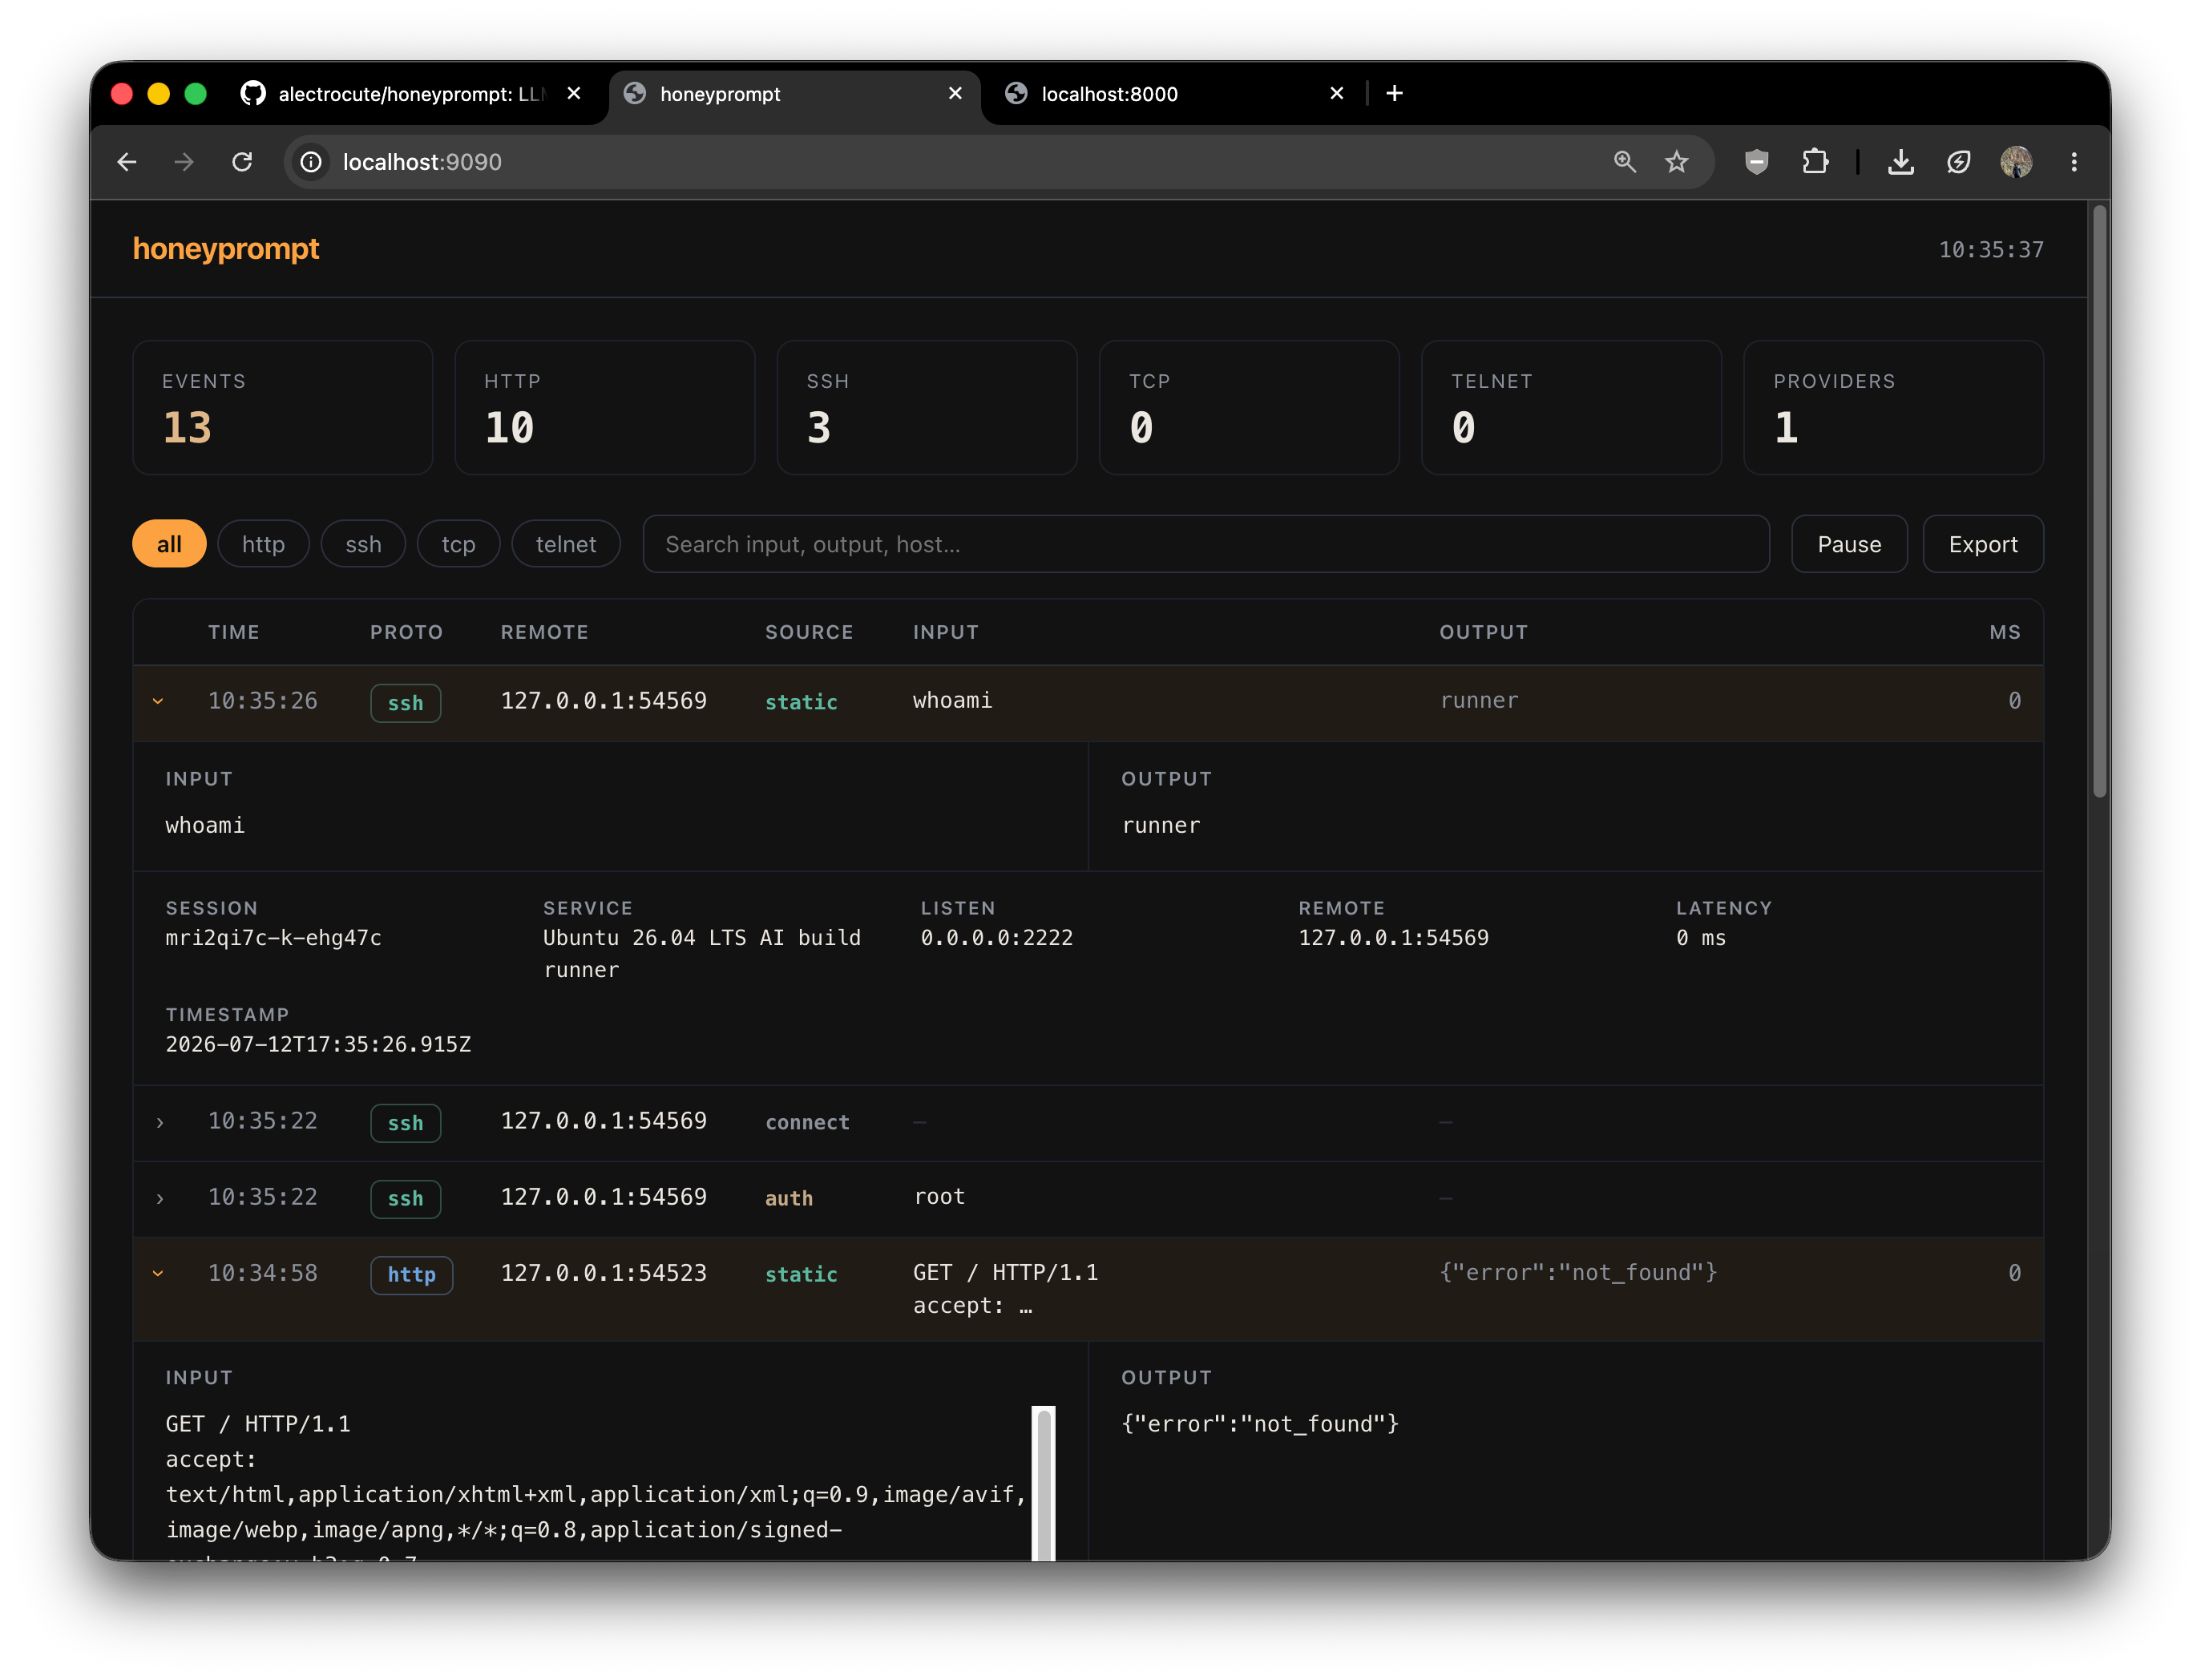 alectrocute/honeyprompt
LLM-first deception framework: "The honeypot that talks back!™"
 afshinm/zerobox
Lightweight, cross-platform process sandboxing powered by OpenAI Codex's runtime. Sandbox any command with file, network, and credential controls.
 amlalabs/amla-sandbox
WASM sandbox with capability enforcement for AI agent code. Agents can only call explicitly provided tools with defined constraints. Sandboxed…
 rootdirective-sec/cve-2026-33626-lab
Docker Compose lab reproducing CVE-2026-33626 SSRF in LMDeploy's vision-language image loader. Compares vulnerable (0.12.0) and patched (0.12.3)…
 thodoristsampouris/agentguard
Zero-trust sandbox for AI agents with kernel-level filesystem jail, transparent network proxy, and YAML-based policy engine to intercept and control…
 aradhyacp/secflow
AI-driven automated threat analysis pipeline that routes files, URLs, IPs, domains, or images through specialized security analyzers and generates…
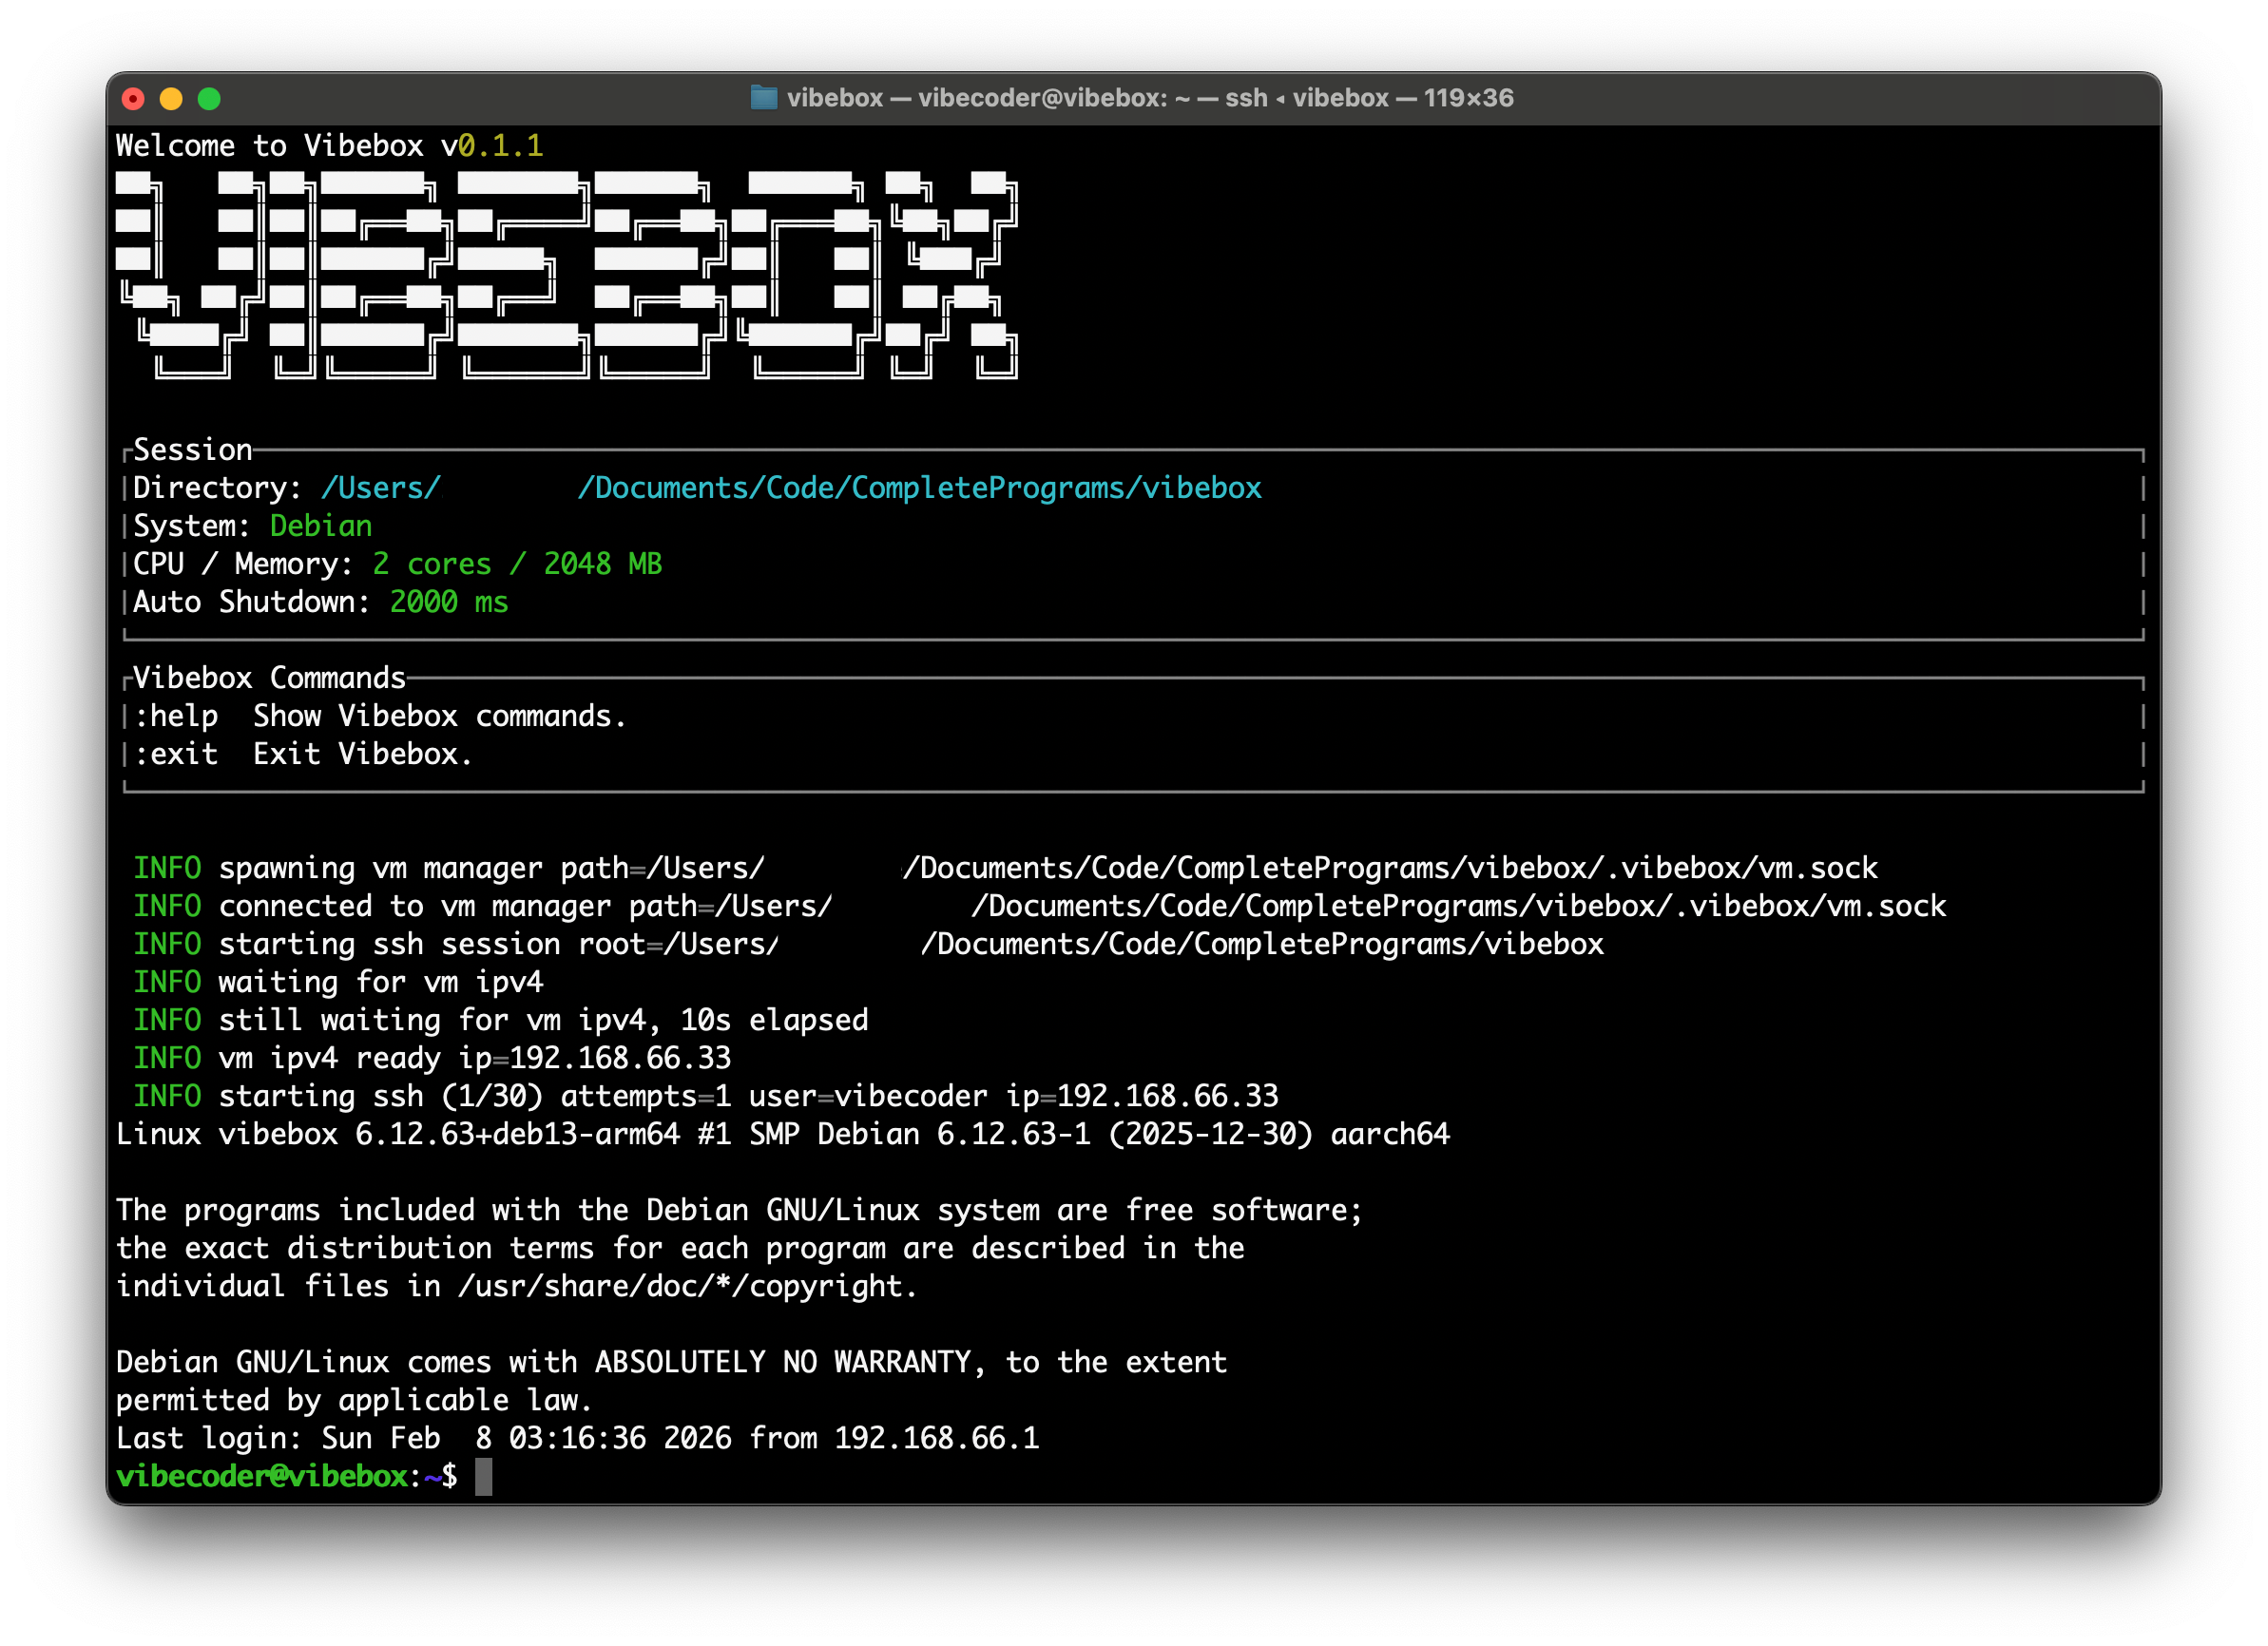 robcholz/vibebox
Ultrafast CLI on Apple Silicon macOS for fast, sandboxed development and LLM agents.