

Hexestra
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
ai-securitycommand-and-controlinformation-gathering+7
110
absllk/hexestraAI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
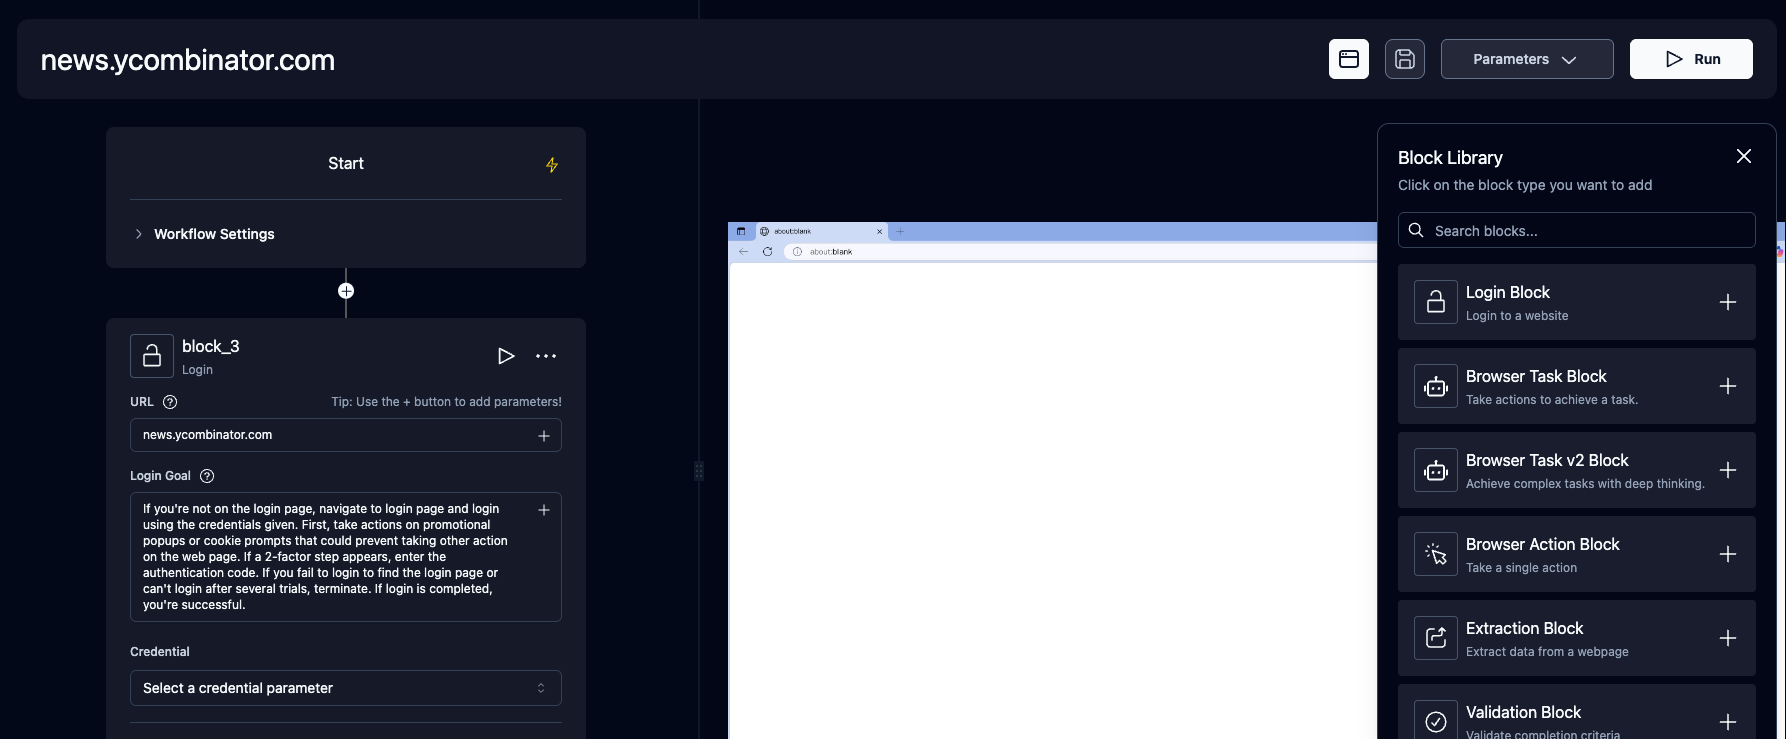 skyvern-ai/skyvern
Automate browser based workflows with AI
 0sec-labs/0
Open-source AI security harness. Includes a web UI for code analysis, pentesting, vulnerability research, reverse engineering, verification, and…
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
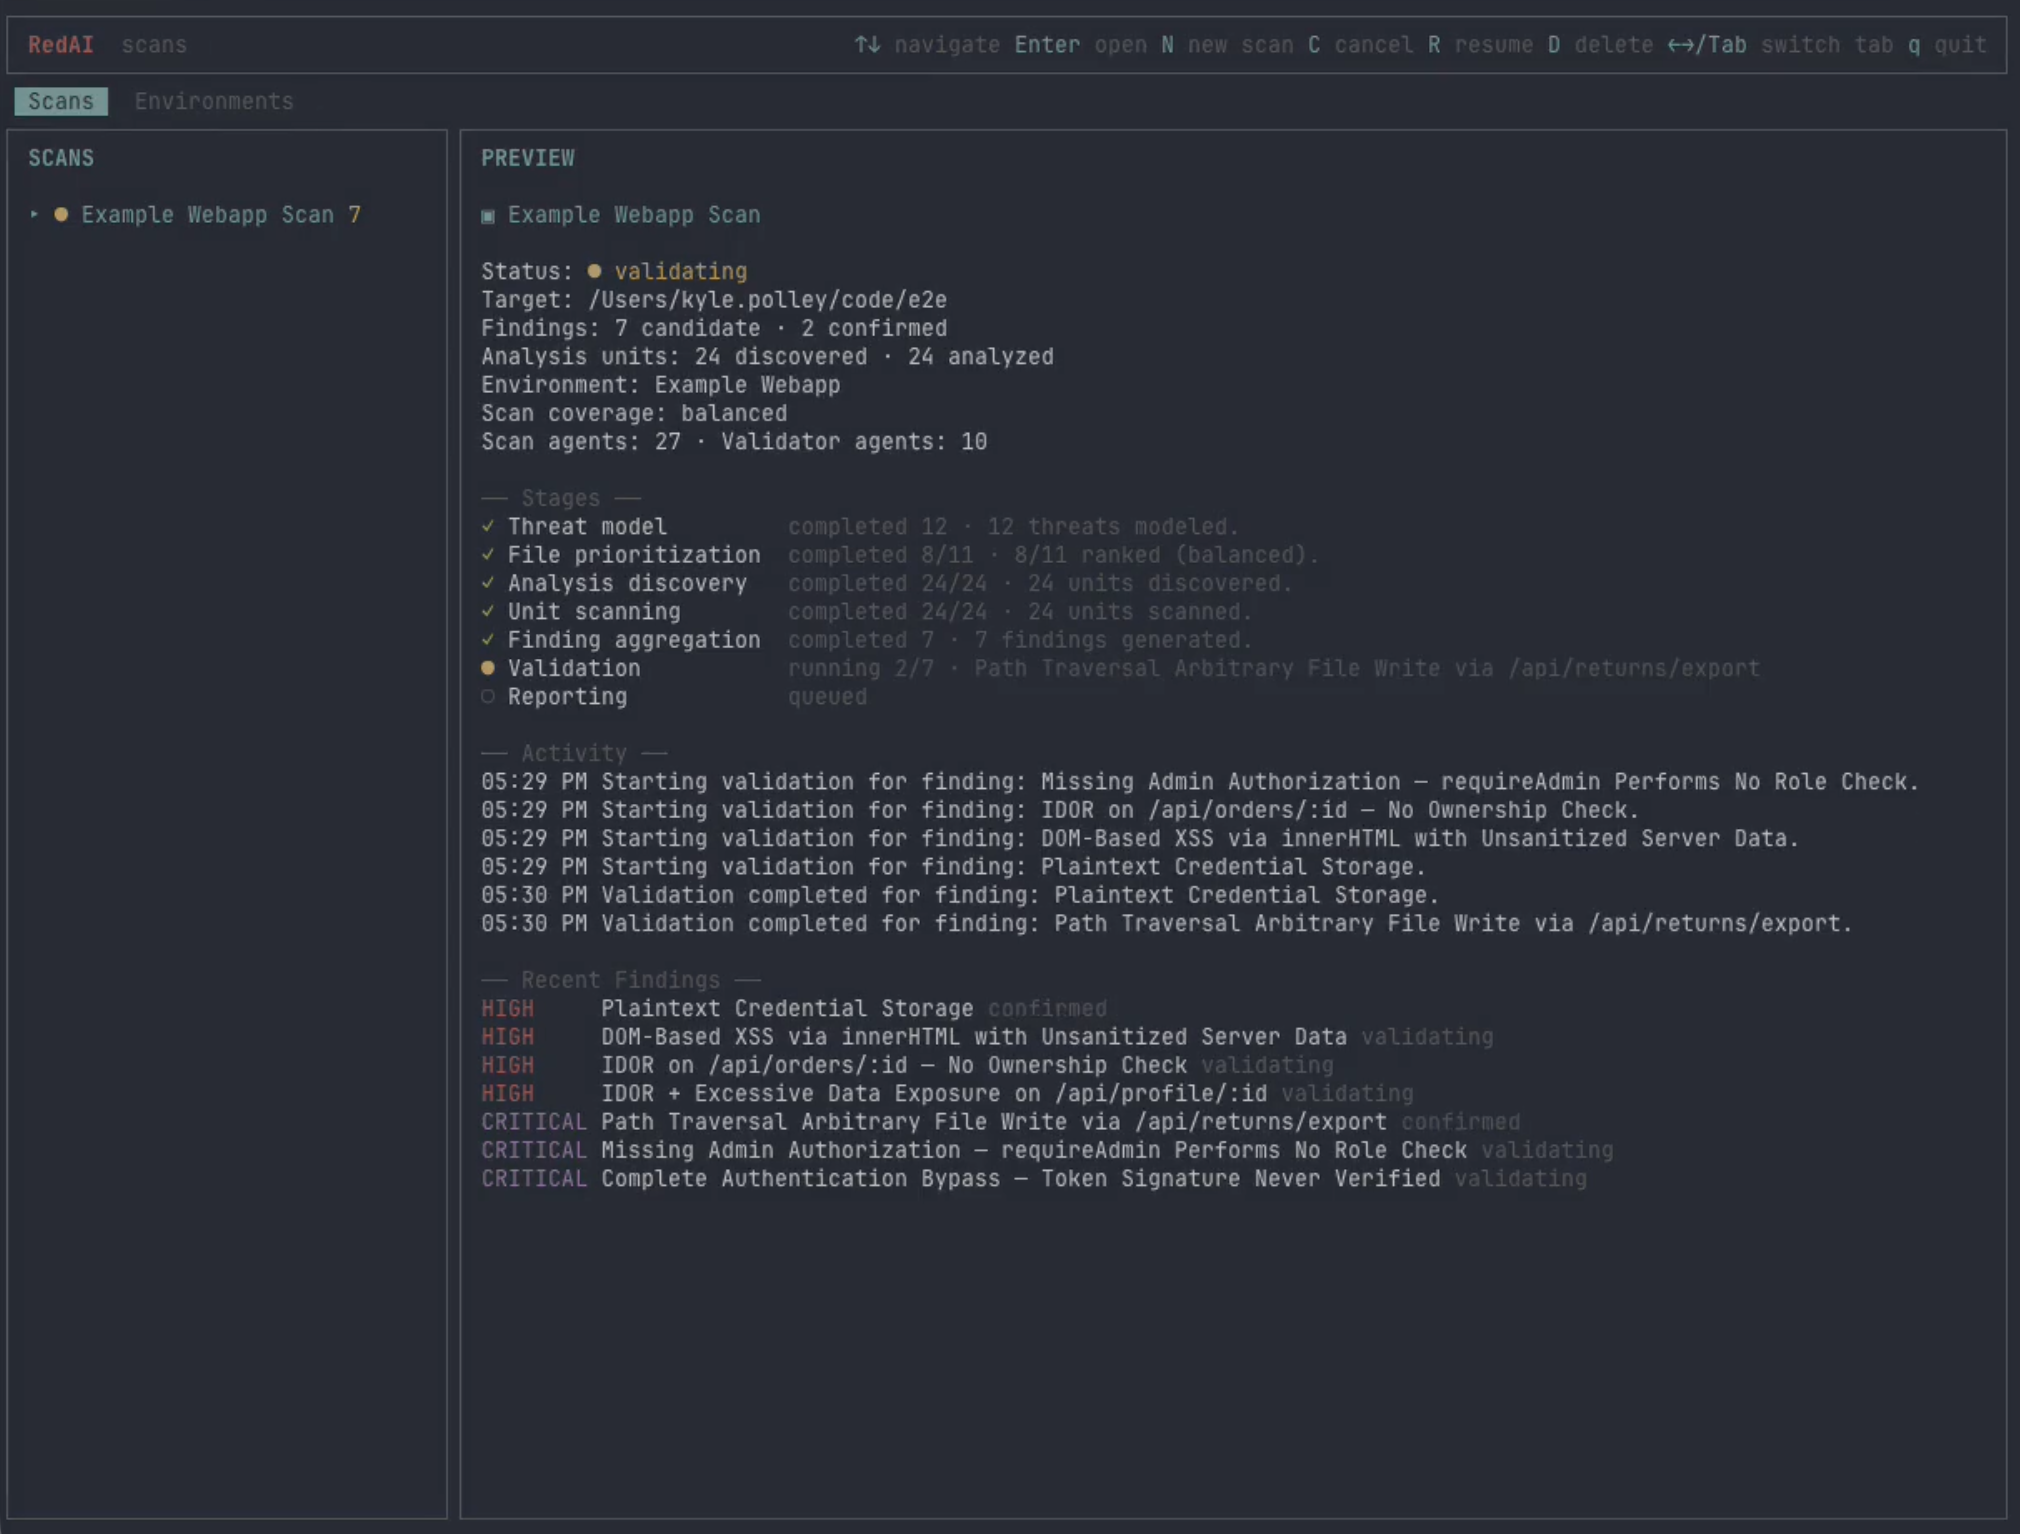 kpolley/redai
AI-driven vulnerability discovery and live validation
 qin2dim/hcaptcha-challenger
🥂 Gracefully face hCaptcha challenge with multimodal large language model.
 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
 moontea0416/webmirage
Adversarial image attacks on vision-language web agents, from visual grounding to browser execution
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 berylliumsec/nebula
AI-powered penetration testing assistant that automates reconnaissance, vulnerability analysis, and note-taking via integrated LLMs and CLI tool…
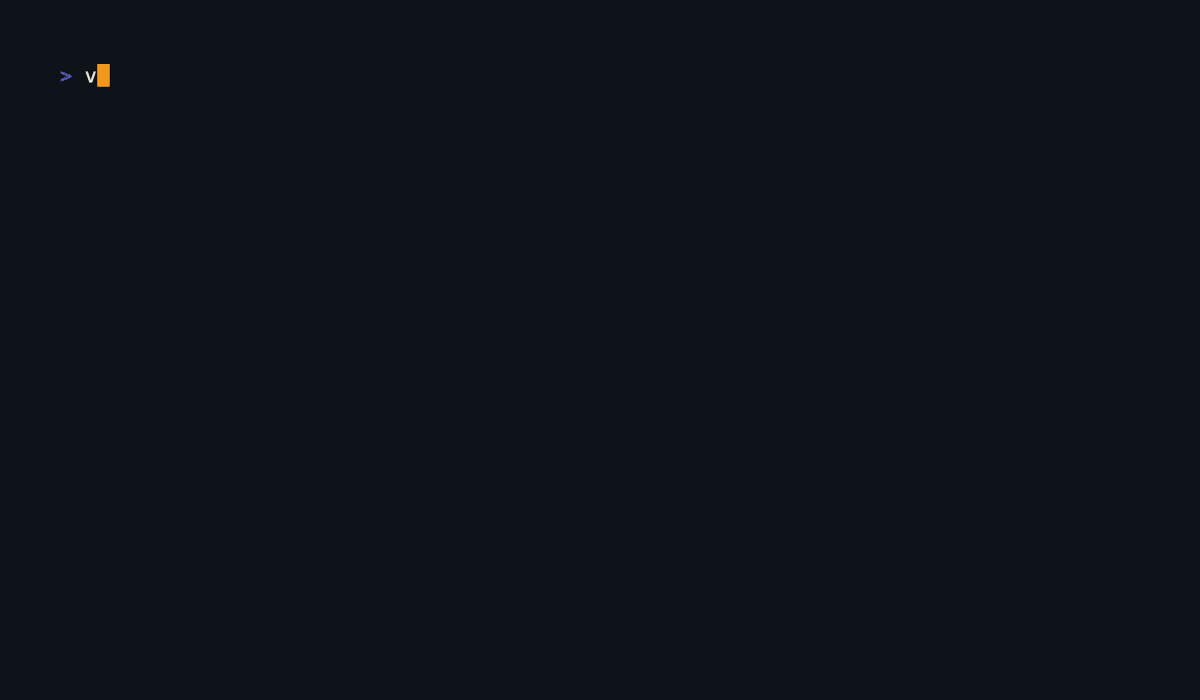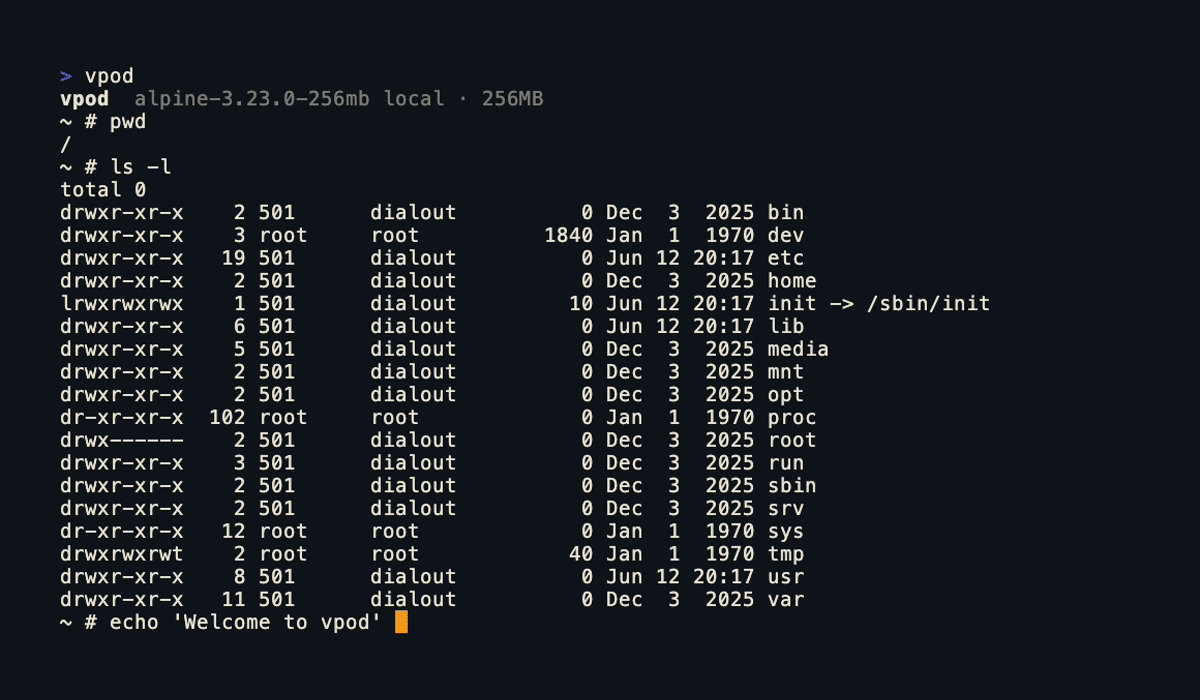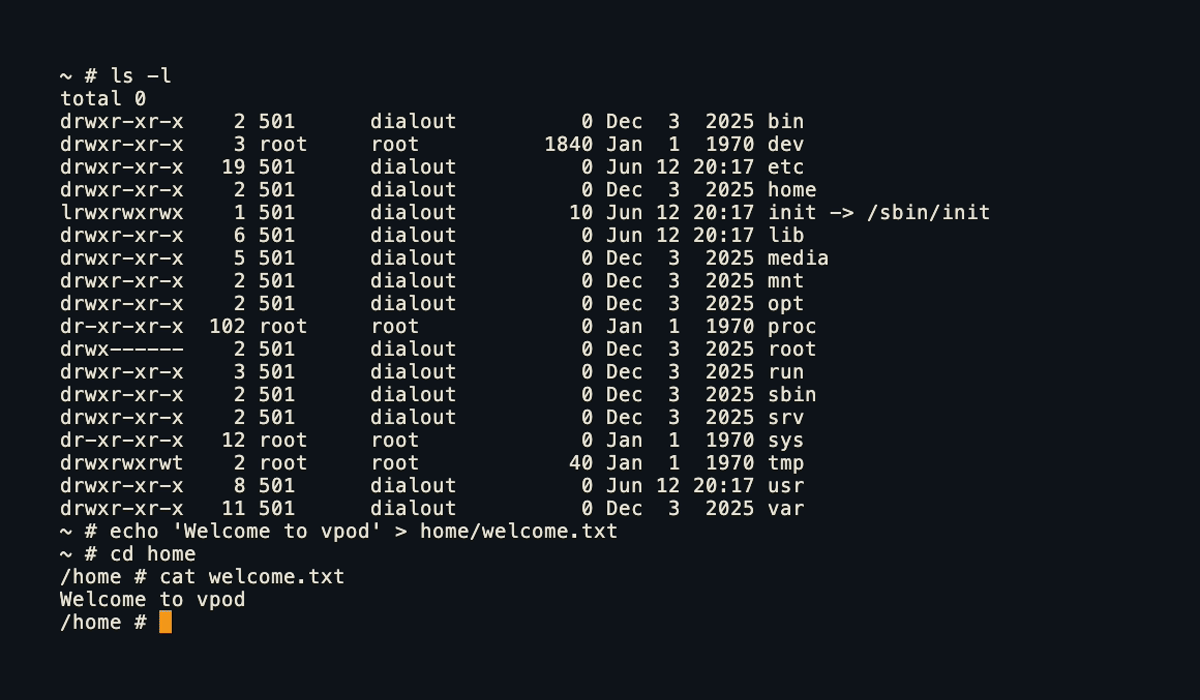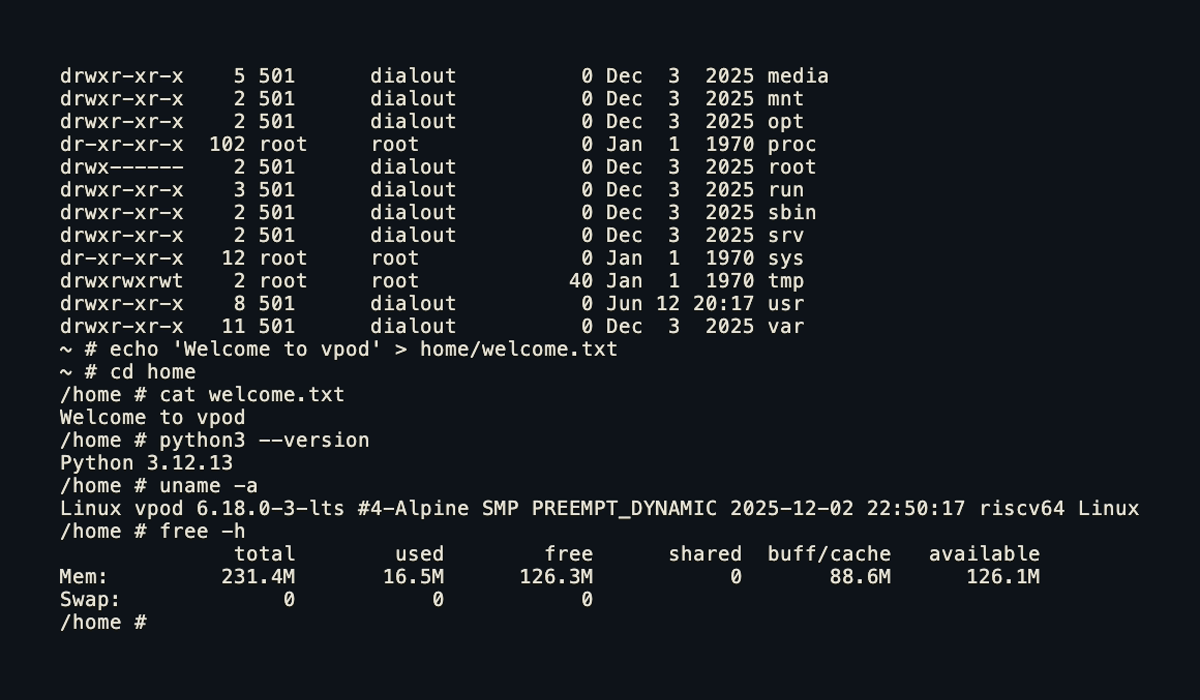 capsulerun/vpod
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
 osintnet/osintnet-public
OsintNET is a browser-based OSINT platform for domain intelligence, website risk scanning, SERP discovery, image intelligence and AI image detection.
 wantasticapp/wantasticcore
AIO Cloud Managment Server
 notasithlord/peerd
The first AI agent harness native to the browser. A browser extension that runs a full agent loop where you already work: it drives your tabs, spins…
 runanywhereai/on-device-browser-agent
On-device AI browser automation using WebLLM. No cloud, no API keys, fully private.
 mohamed--abdel-maksoud/pisiguard
Browser extension that detects PII and sensitive data in AI chats, masks it with placeholders before sending, and restores originals in replies—all…
 boreas37/cve-2025-62593-poc
PoC for CVE-2025-62593: unauthenticated RCE in Ray (CISA KEV). Stdlib-only Python.