

capa
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k
mandiant/capaRule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 mrexodia/ida-pro-mcp
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 lauriewired/ghidramcp
MCP Server for Ghidra
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 vulhunt-re/vulhunt
Vulnerability detection framework by Binarly's REsearch team
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
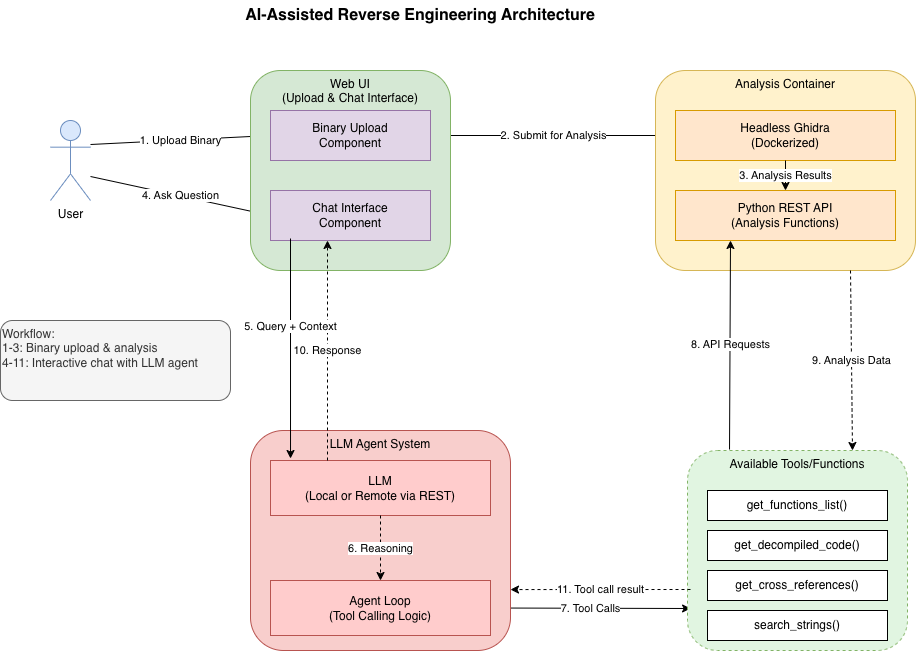 biniamf/ai-reverse-engineering
AI-Assisted Reverse Engineering with Ghidra
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
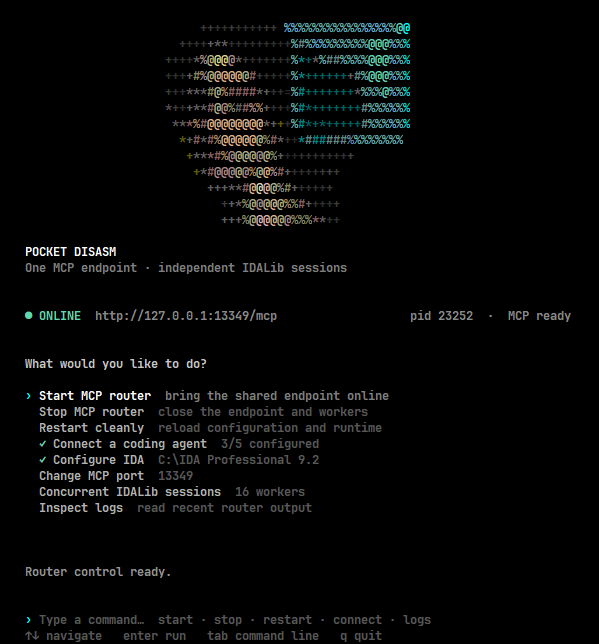 whoisqwerz/pocket_disasm
Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.
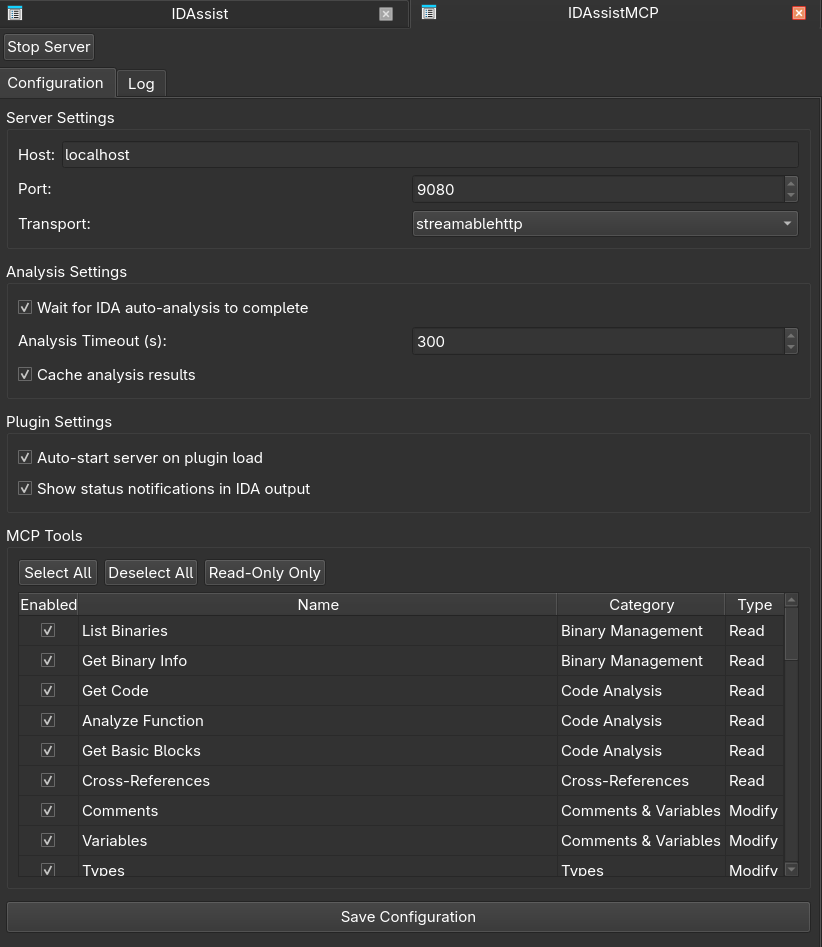 symgraph/idassistmcp
Standalone MCP server plugin for IDA Pro.
 ddudle/ctxdebug
MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…