
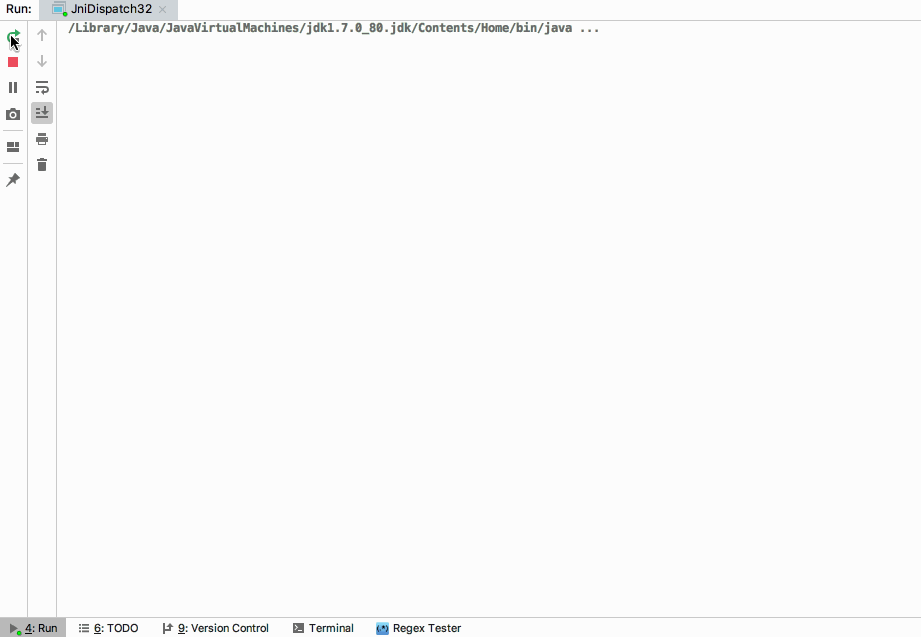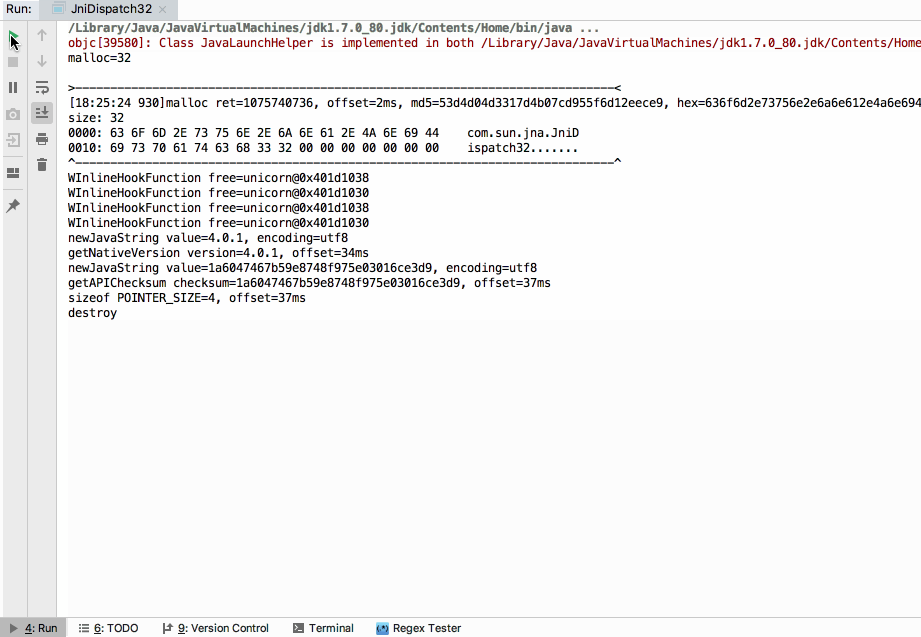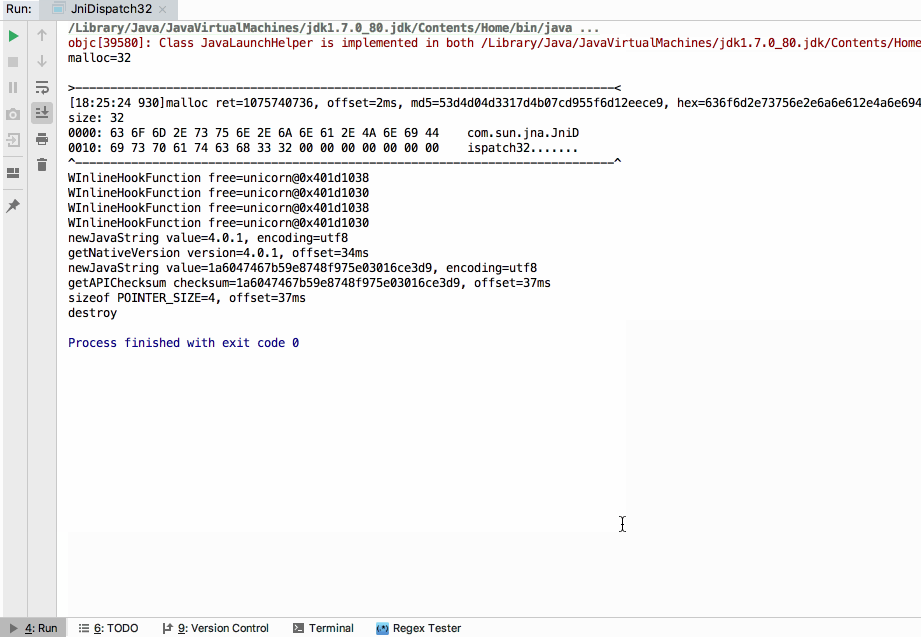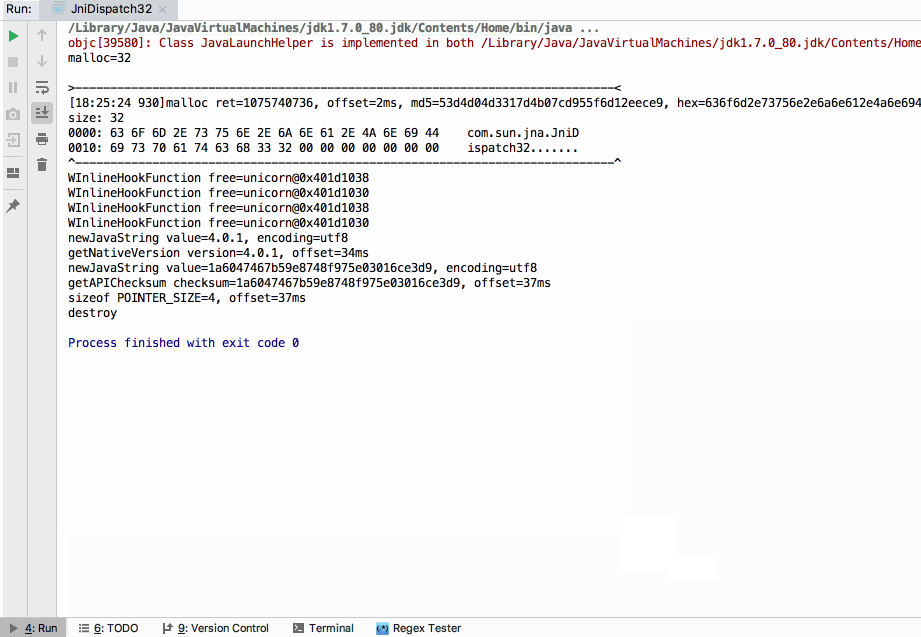
unidbg
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
ai-assisted-reversingandroid-securitybinary-analysis+5
5.2k16 days ago
zhkl0228/unidbgAllows you to emulate an Android native library, and an experimental iOS emulation
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
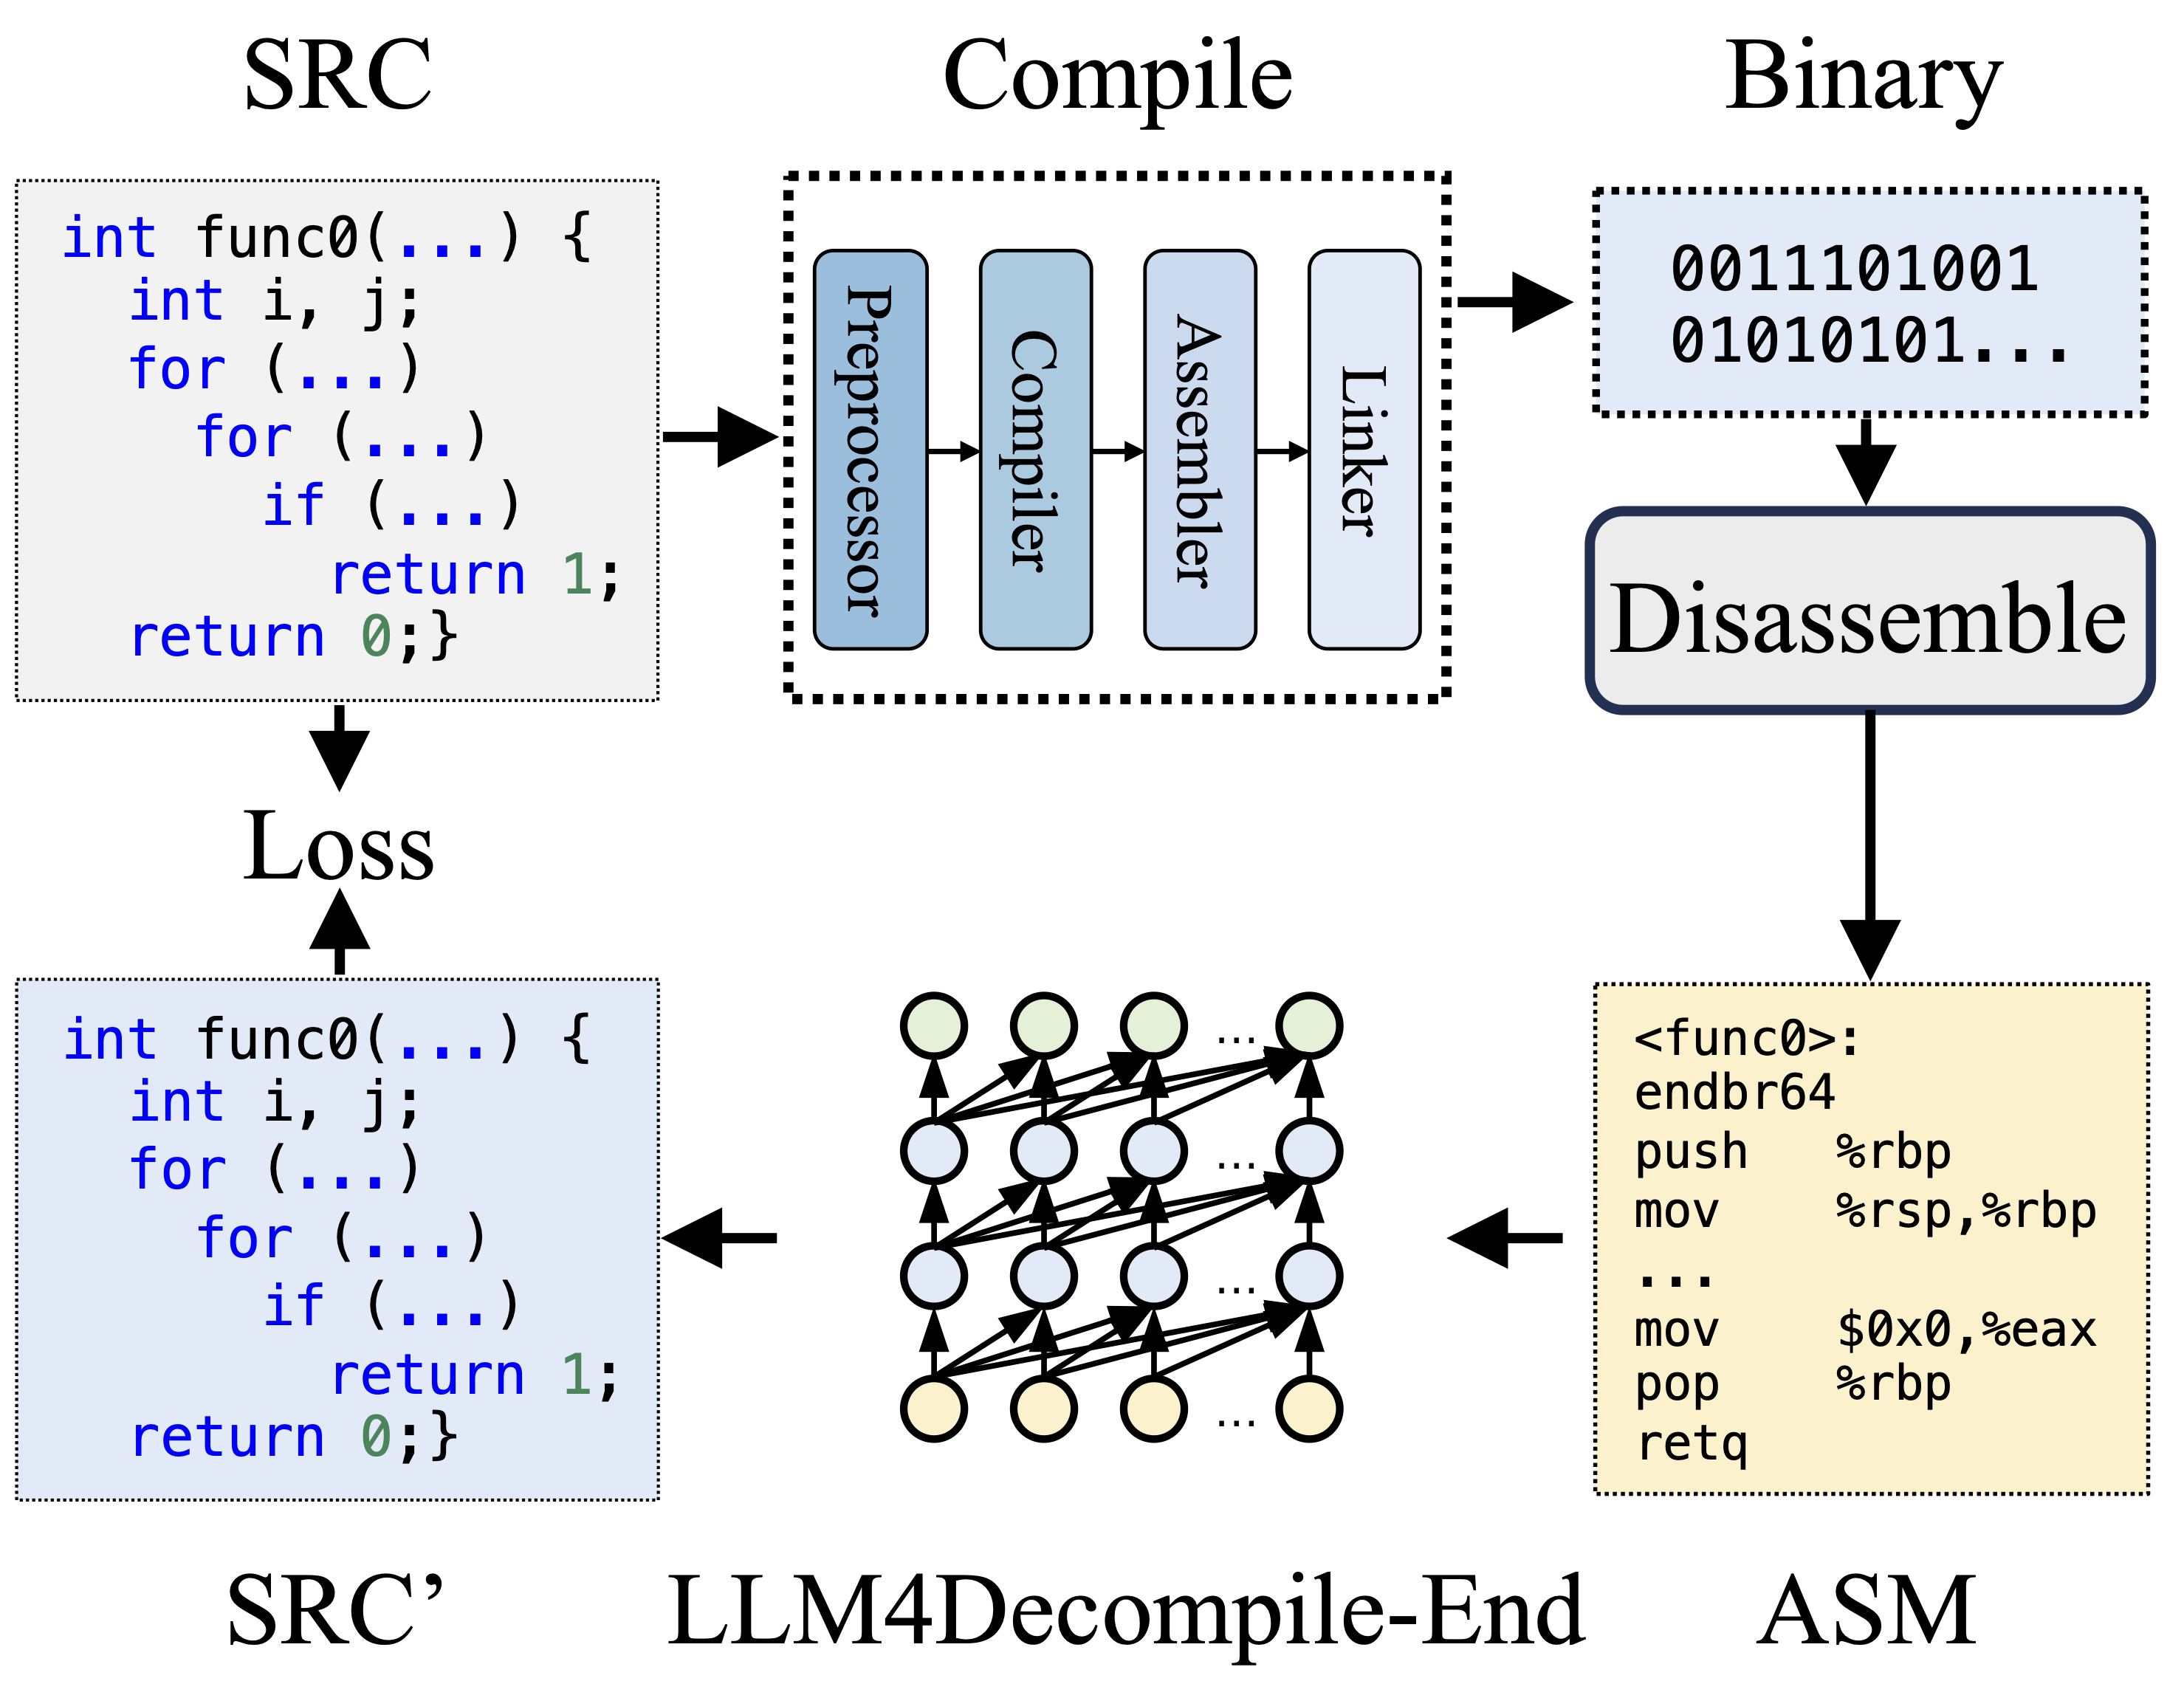 albertan017/llm4decompile
Reverse Engineering: Decompiling Binary Code with Large Language Models
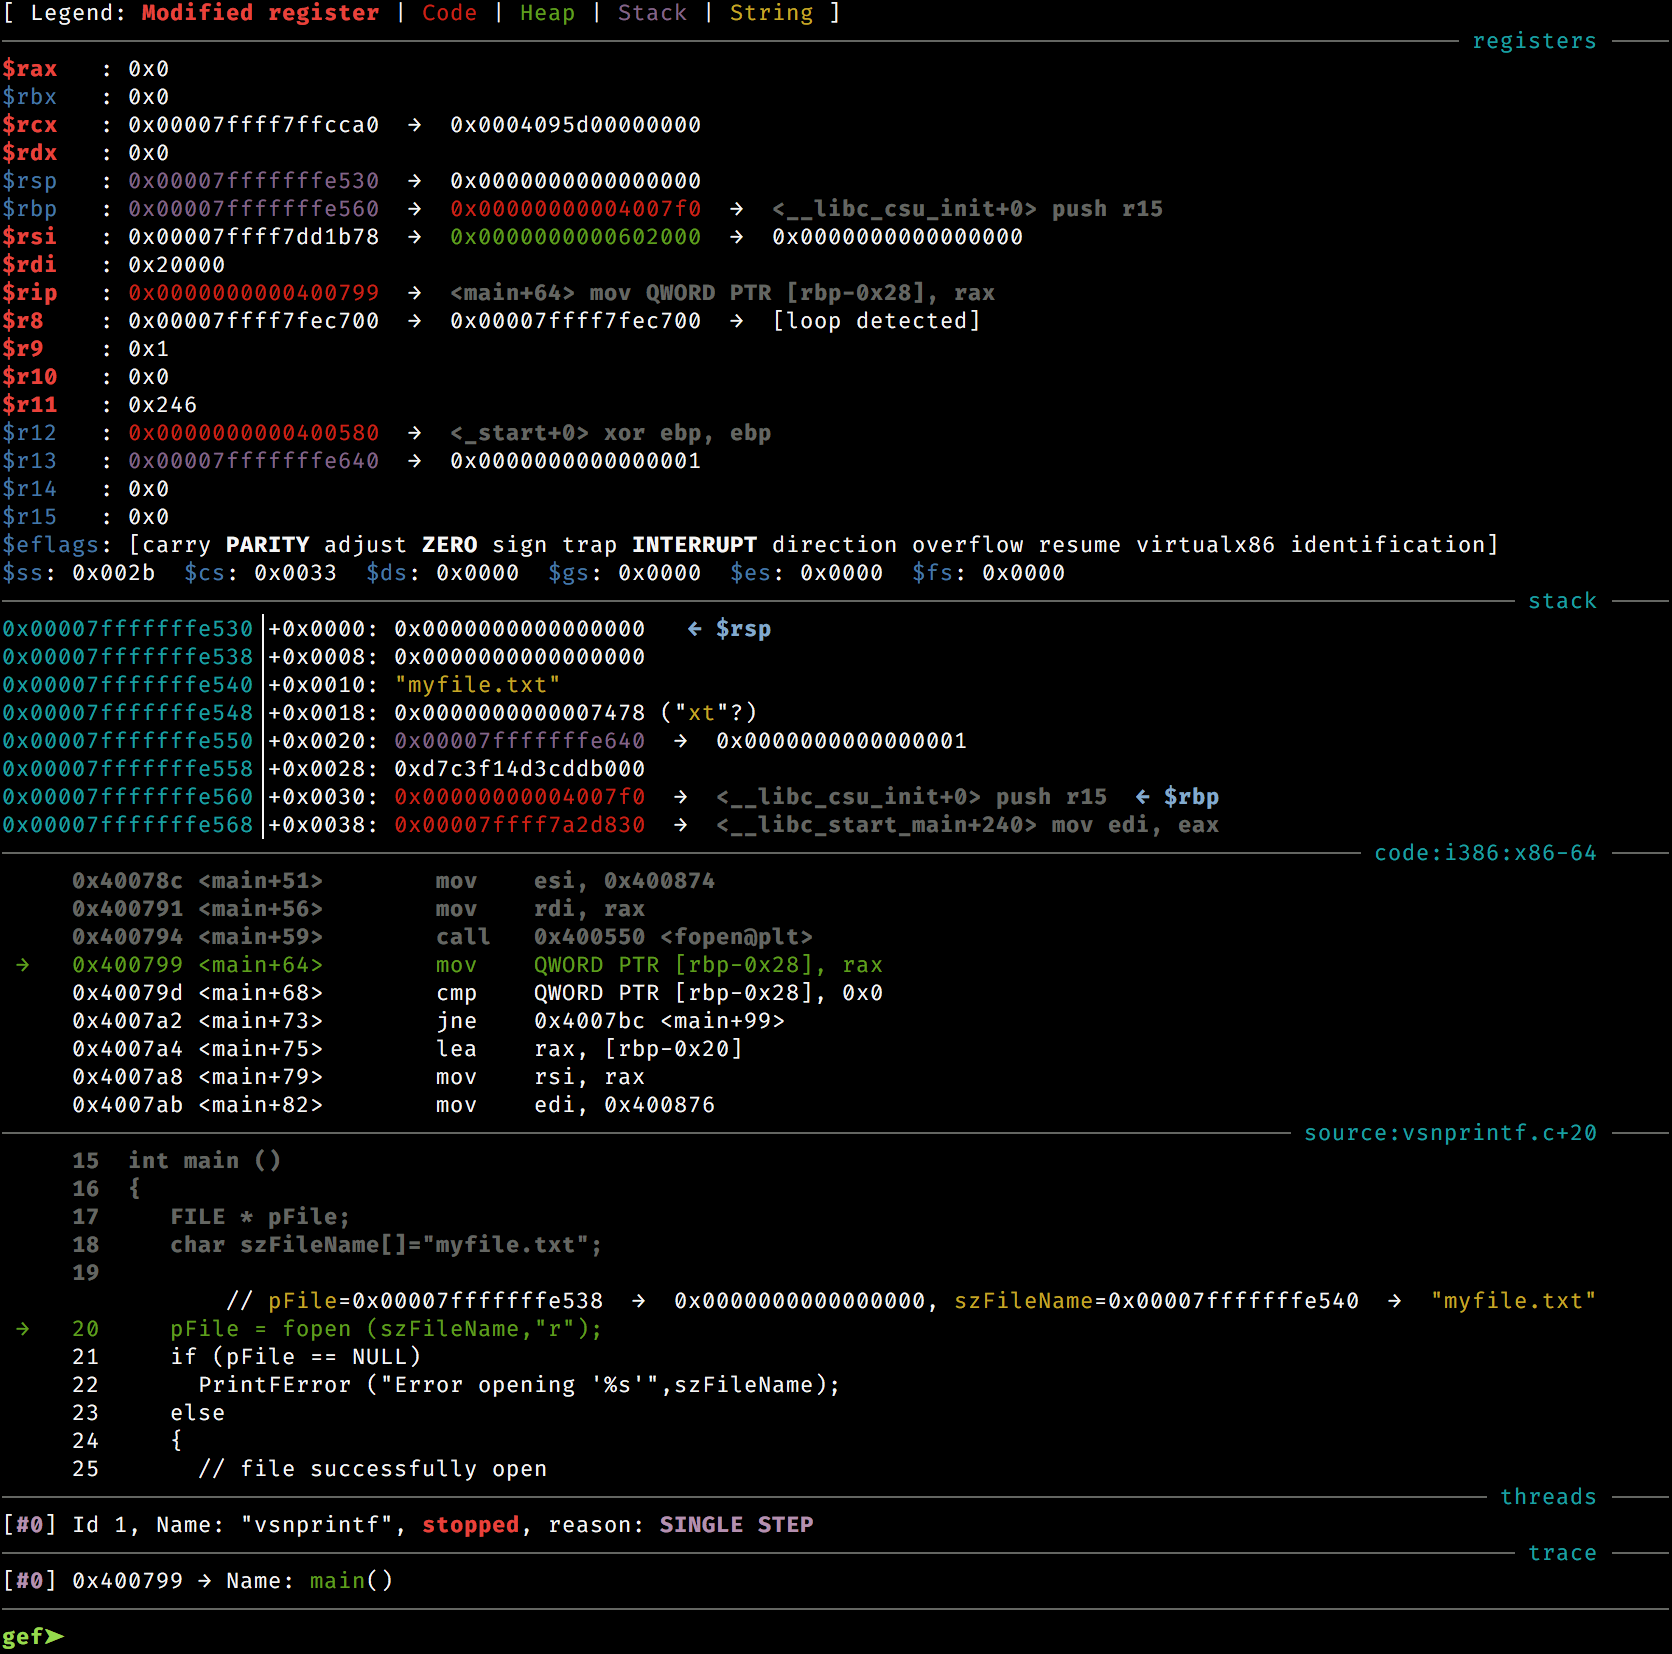 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 lauriewired/ghidramcp
MCP Server for Ghidra

 dryxio/auto-re-agent
Reconstruct and validate C/C++ code from compiled programs with AI.
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
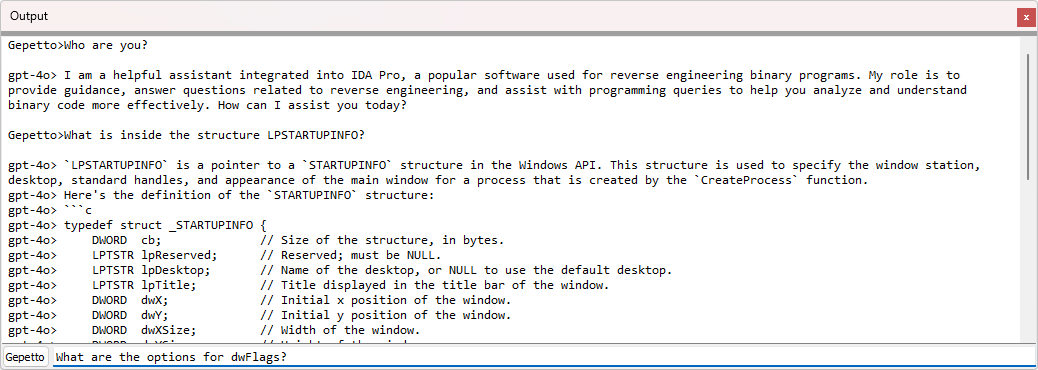 justicerage/gepetto
IDA plugin which queries language models to speed up reverse-engineering
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 lauriewired/malimite
iOS and macOS Decompiler
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 symgraph/ghidrassist
An LLM extension for Ghidra to enable AI assistance in RE.
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…