
brawl-public-game-001
 mitre/brawl-public-game-001
Data from a BRAWL Automated Adversary Emulation Exercise
adversarial-attackcloud-securitydigital-forensics+7
215
mitre/brawl-public-game-001Data from a BRAWL Automated Adversary Emulation Exercise
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 barre/privaxy
Privaxy is the next generation tracker and advertisement blocker. It blocks ads and trackers by MITMing HTTP(s) traffic. Also check out my new…
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
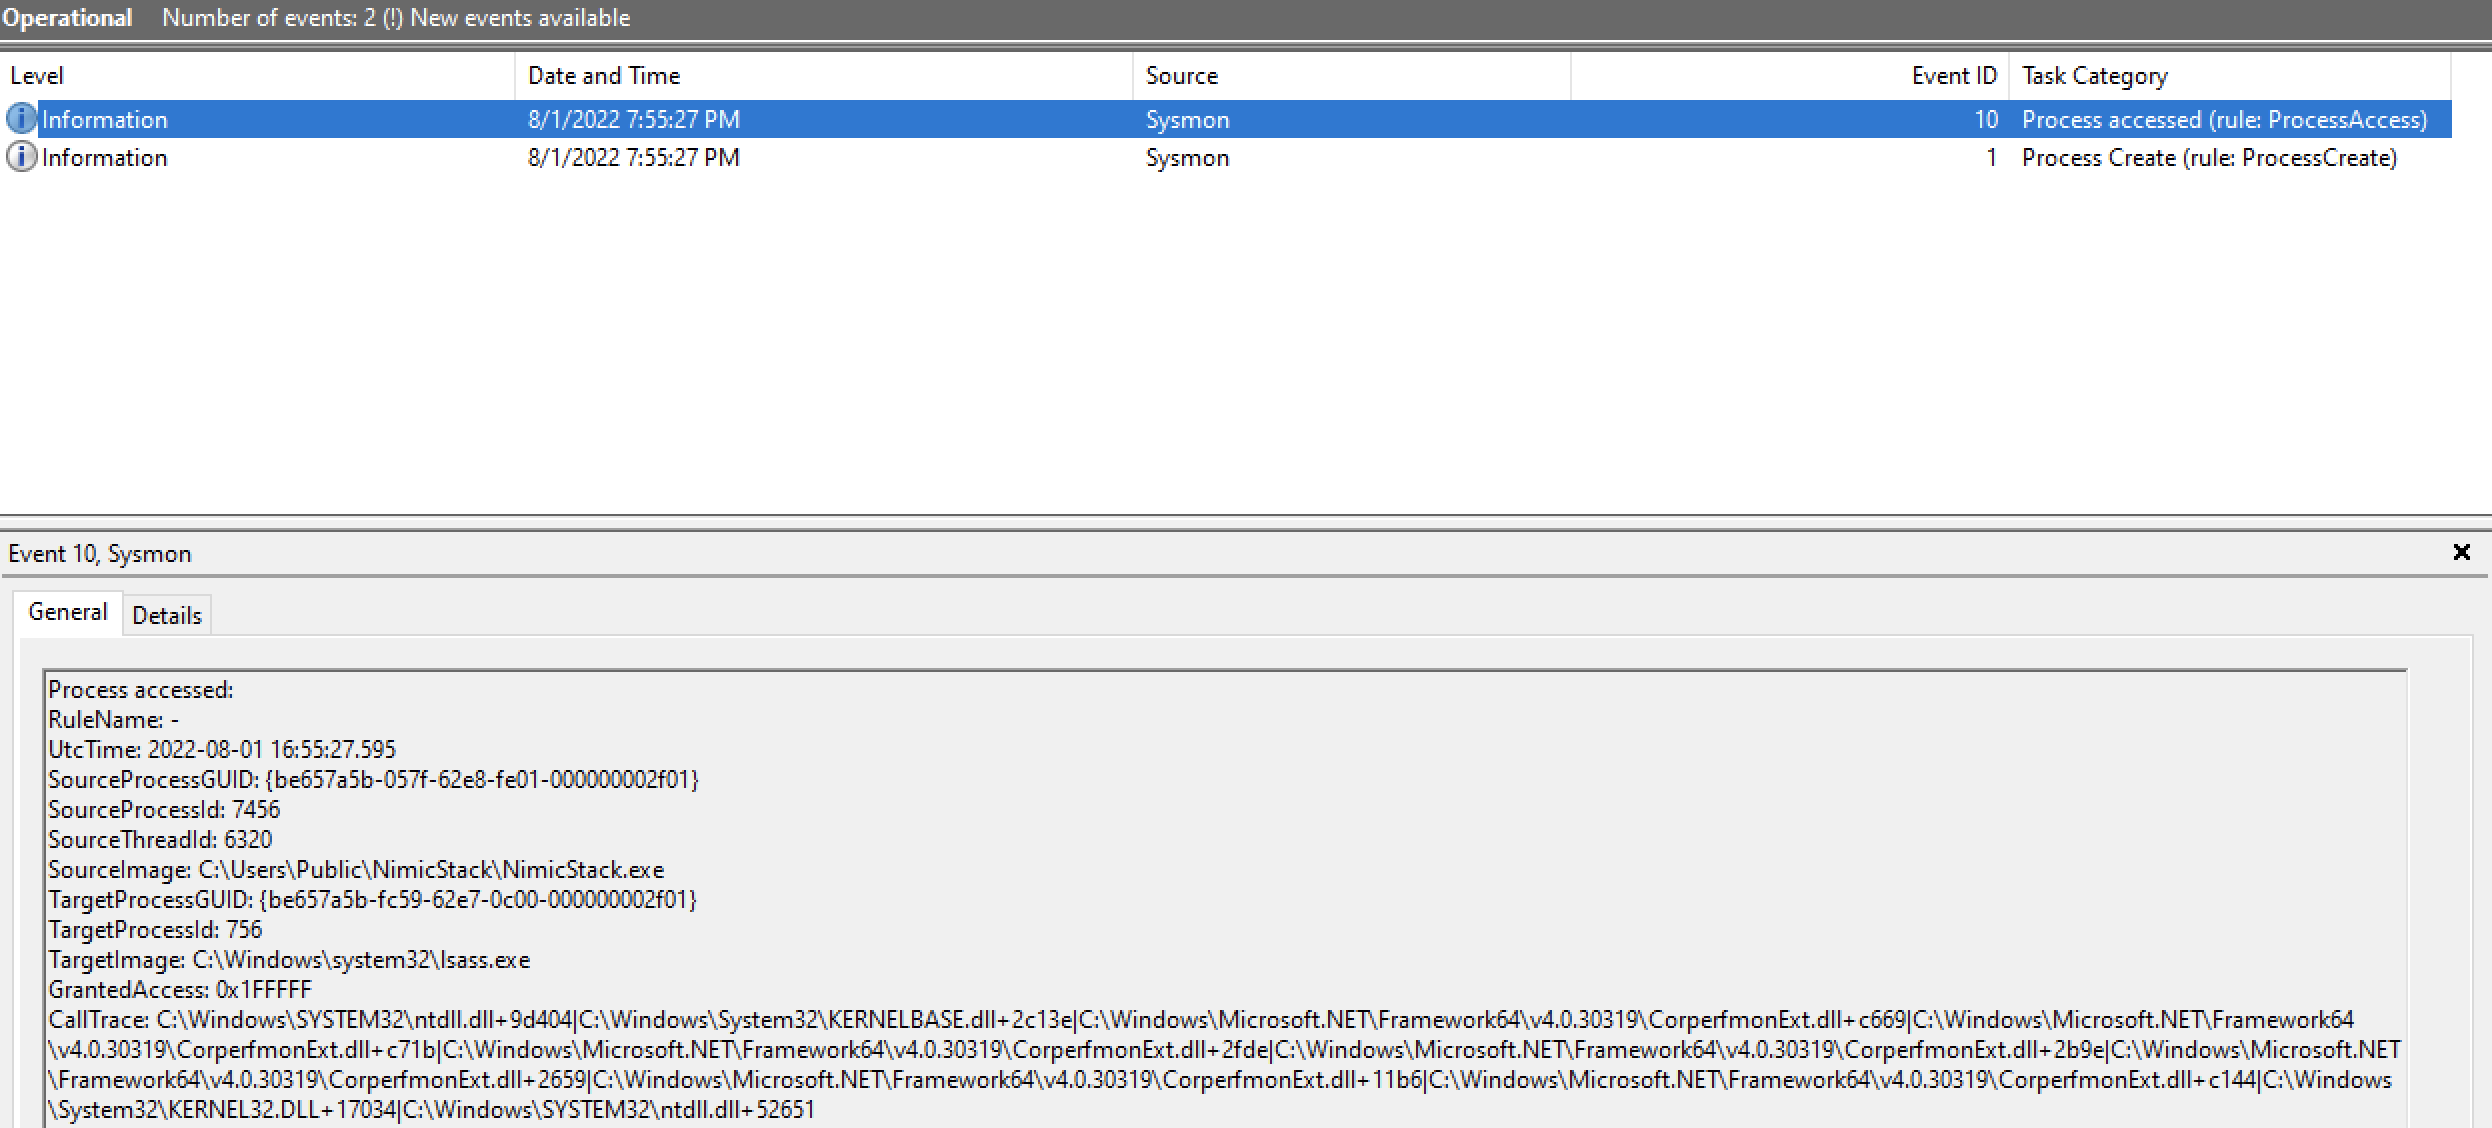 frkngksl/nimicstack
NimicStack is the pure Nim implementation of Call Stack Spoofing technique to mimic legitimate programs
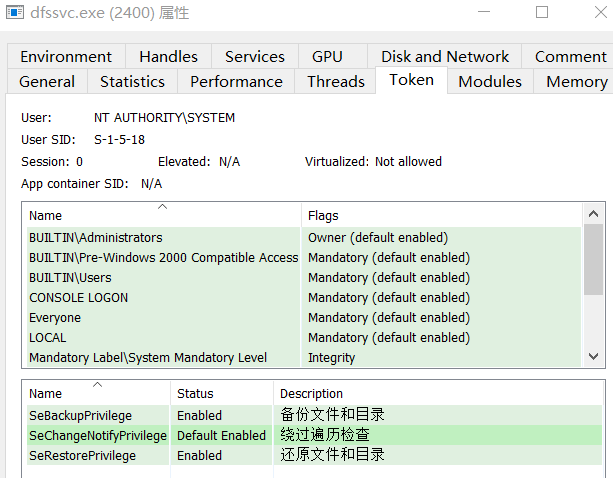 crisprss/magicnetdefs
Similar to Petitpotam, the netdfs service is enabled in Windows Server and AD environments, and the abused RPC method allows privileged processes to…
 bishopfox/sliver
Adversary Emulation Framework
 apache/caldera
Automated Adversary Emulation Platform
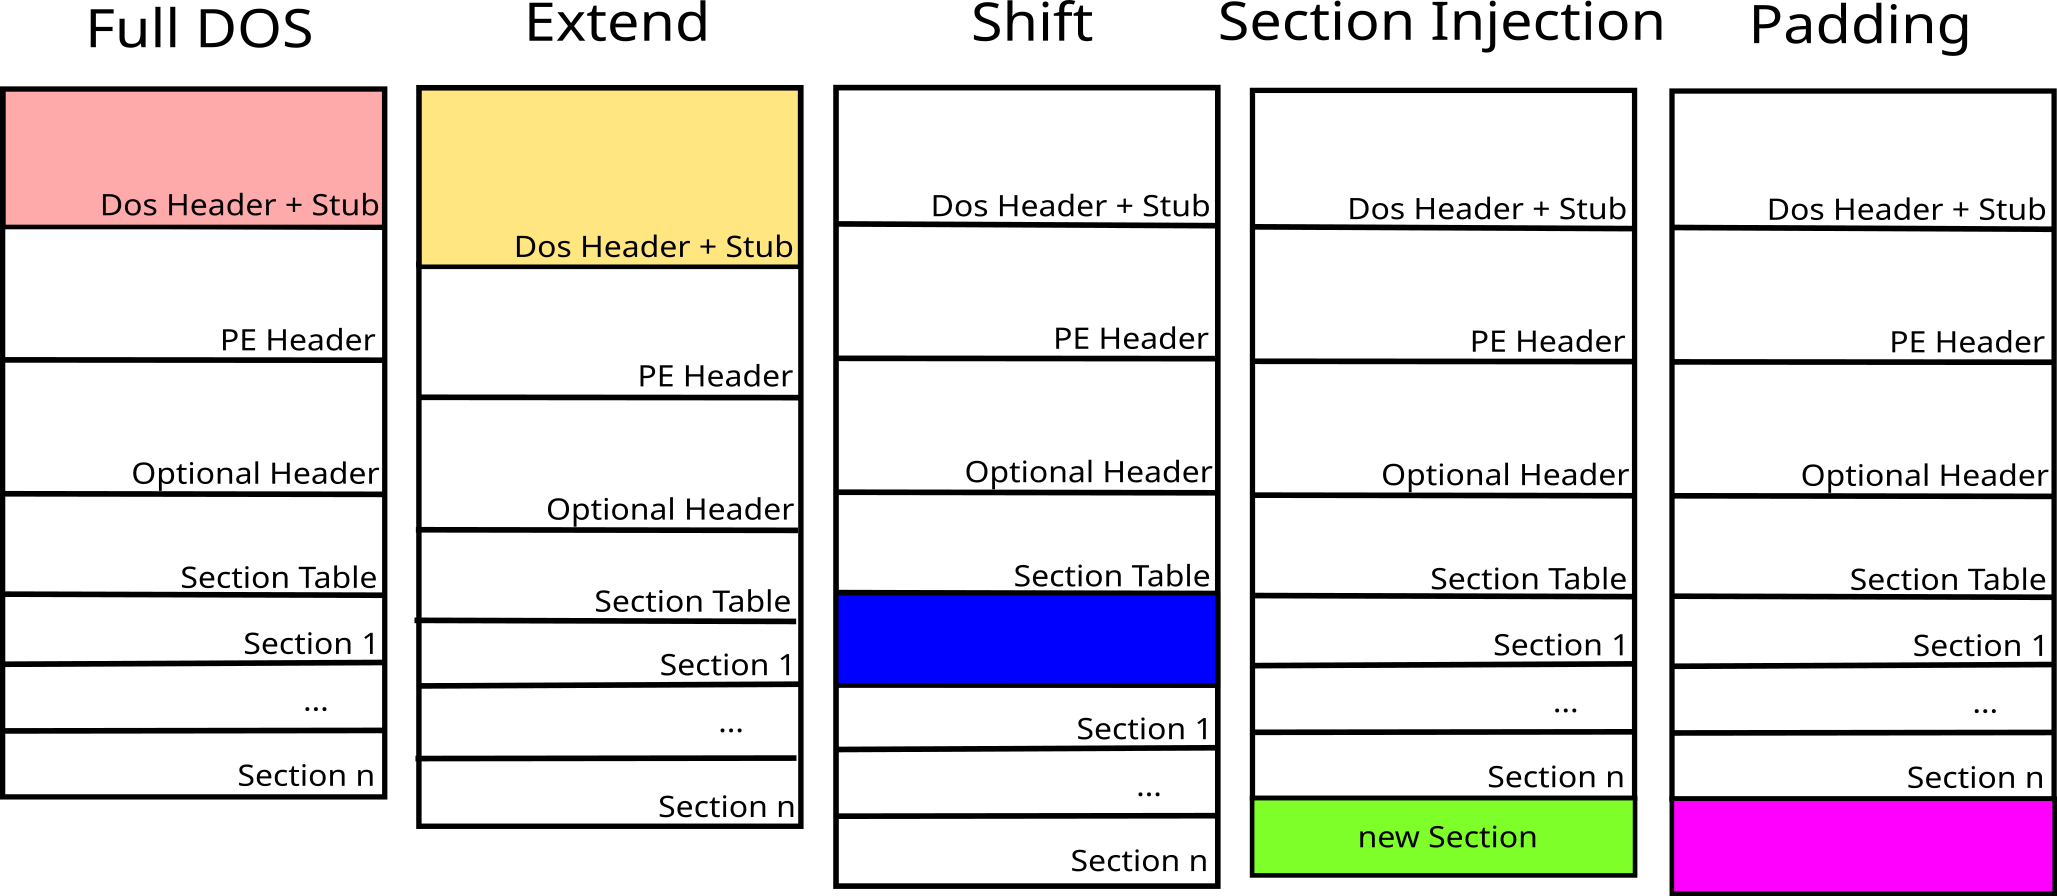
 scythe-io/purple-team-exercise-framework
Purple Team Exercise Framework
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
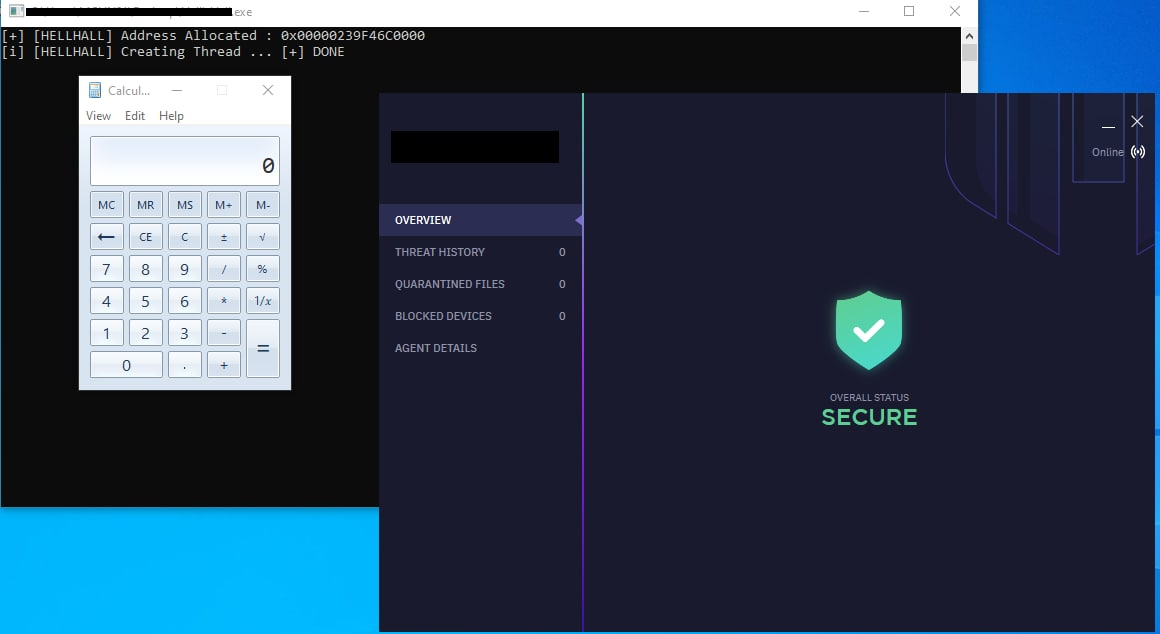 maldev-academy/hellhall
Performing Indirect Clean Syscalls
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
 rasta-mouse/crystal-kit
Evasion kit for Cobalt Strike
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 redcanaryco/chain-reactor
Generate Linux executables that simulate adversary behaviors and techniques for testing detection and response coverage. Consumes JSON for easy…