
CobaltWhispers
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
adversarial-attackcommand-and-controlids-ips-evasion+4
243
nvisosecurity/cobaltwhispersCobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
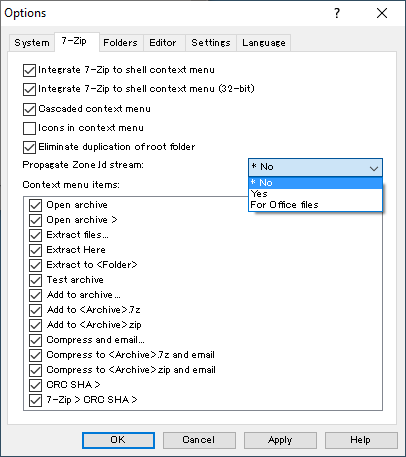 nmantani/archiver-motw-support-comparison
Compares Windows archiver support for Mark of the Web propagation, helping teams assess which tools preserve MOTW and mitigate macro-based malware…
 sej2020/manipulating-web-agents
Research demonstration of indirect prompt injection attacks to control autonomous LLM-based web agents, with tools for trigger optimization and…
 nextronsystems/aptsimulator
A toolset to make a system look as if it was the victim of an APT attack
 thuyimingli/backdoor-learning-resources
Curated list of backdoor learning papers, surveys, and toolboxes, organizing poisoning-based attacks and defenses in deep learning for researchers…
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 redteamoperations/redcloud-os
RedCloudOS is a Cloud Adversary Simulation Operating System for Red Teams to assess the Cloud Security of Leading Cloud Service Providers (CSPs)
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
 gmh5225/awesome-ai-security
A curated list of AI Security materials and resources for Pentesters, Bug Hunters, and Security Researchers.
 rasta-mouse/process-inject-kit
Port of Cobalt Strike's Process Inject Kit
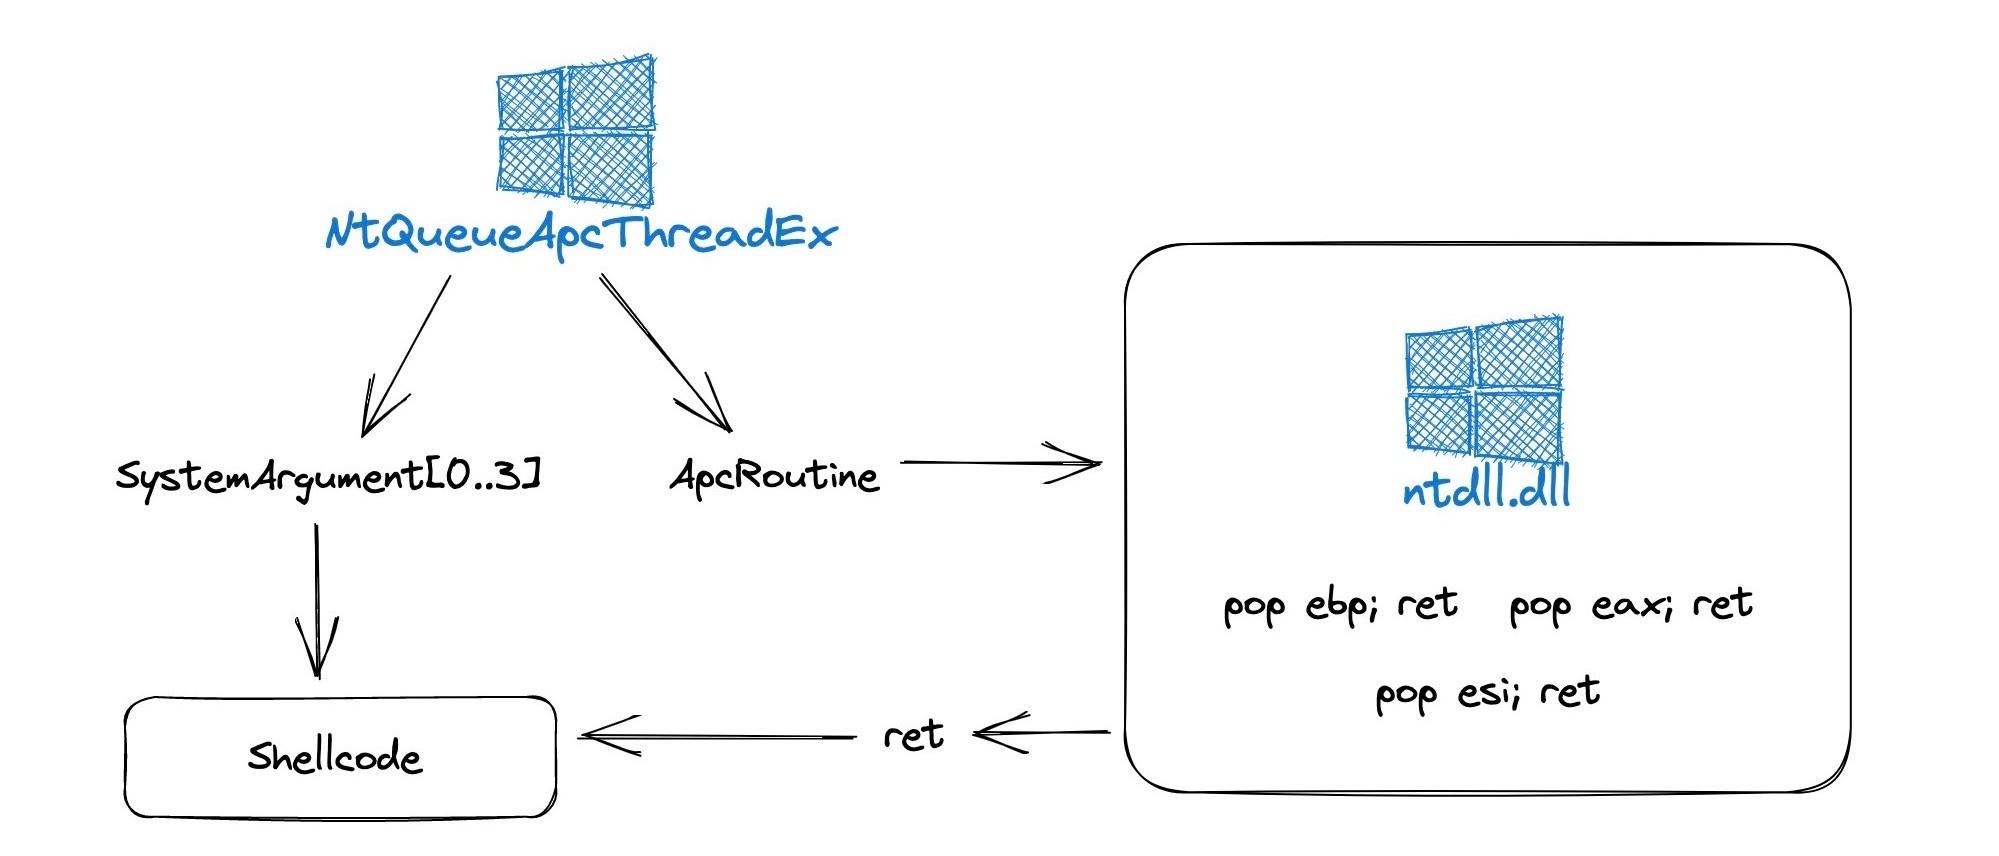 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
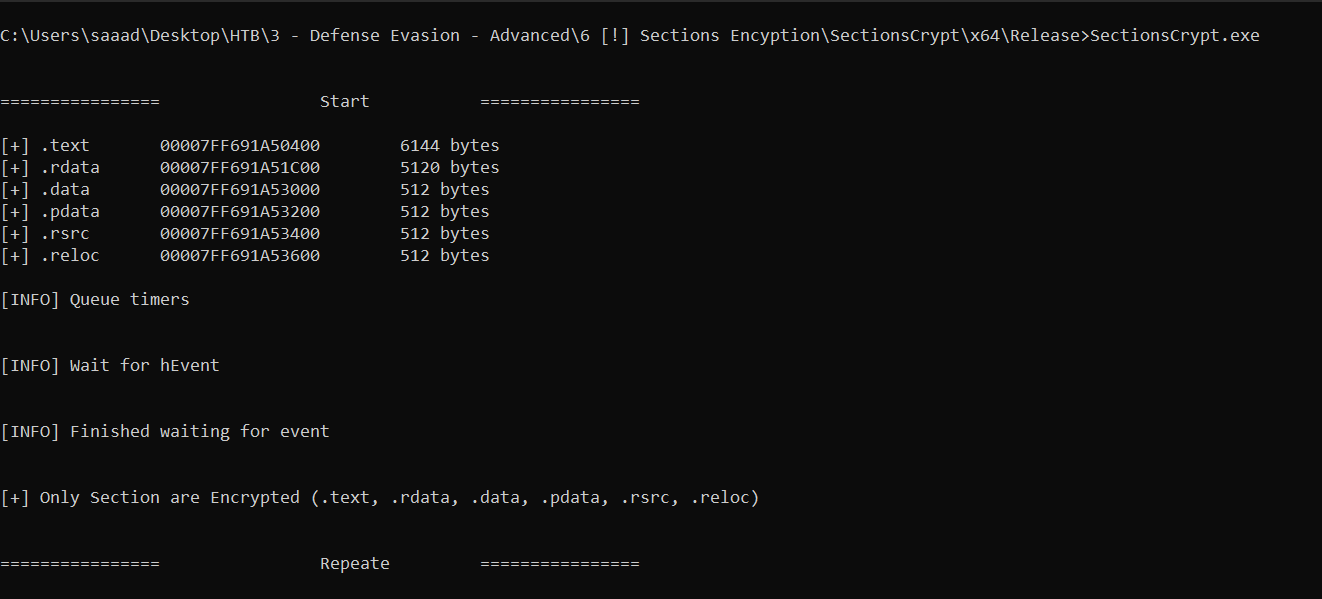 saadahla/d1rksleep
Improved version of EKKO by @5pider that Encrypts only Image Sections
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
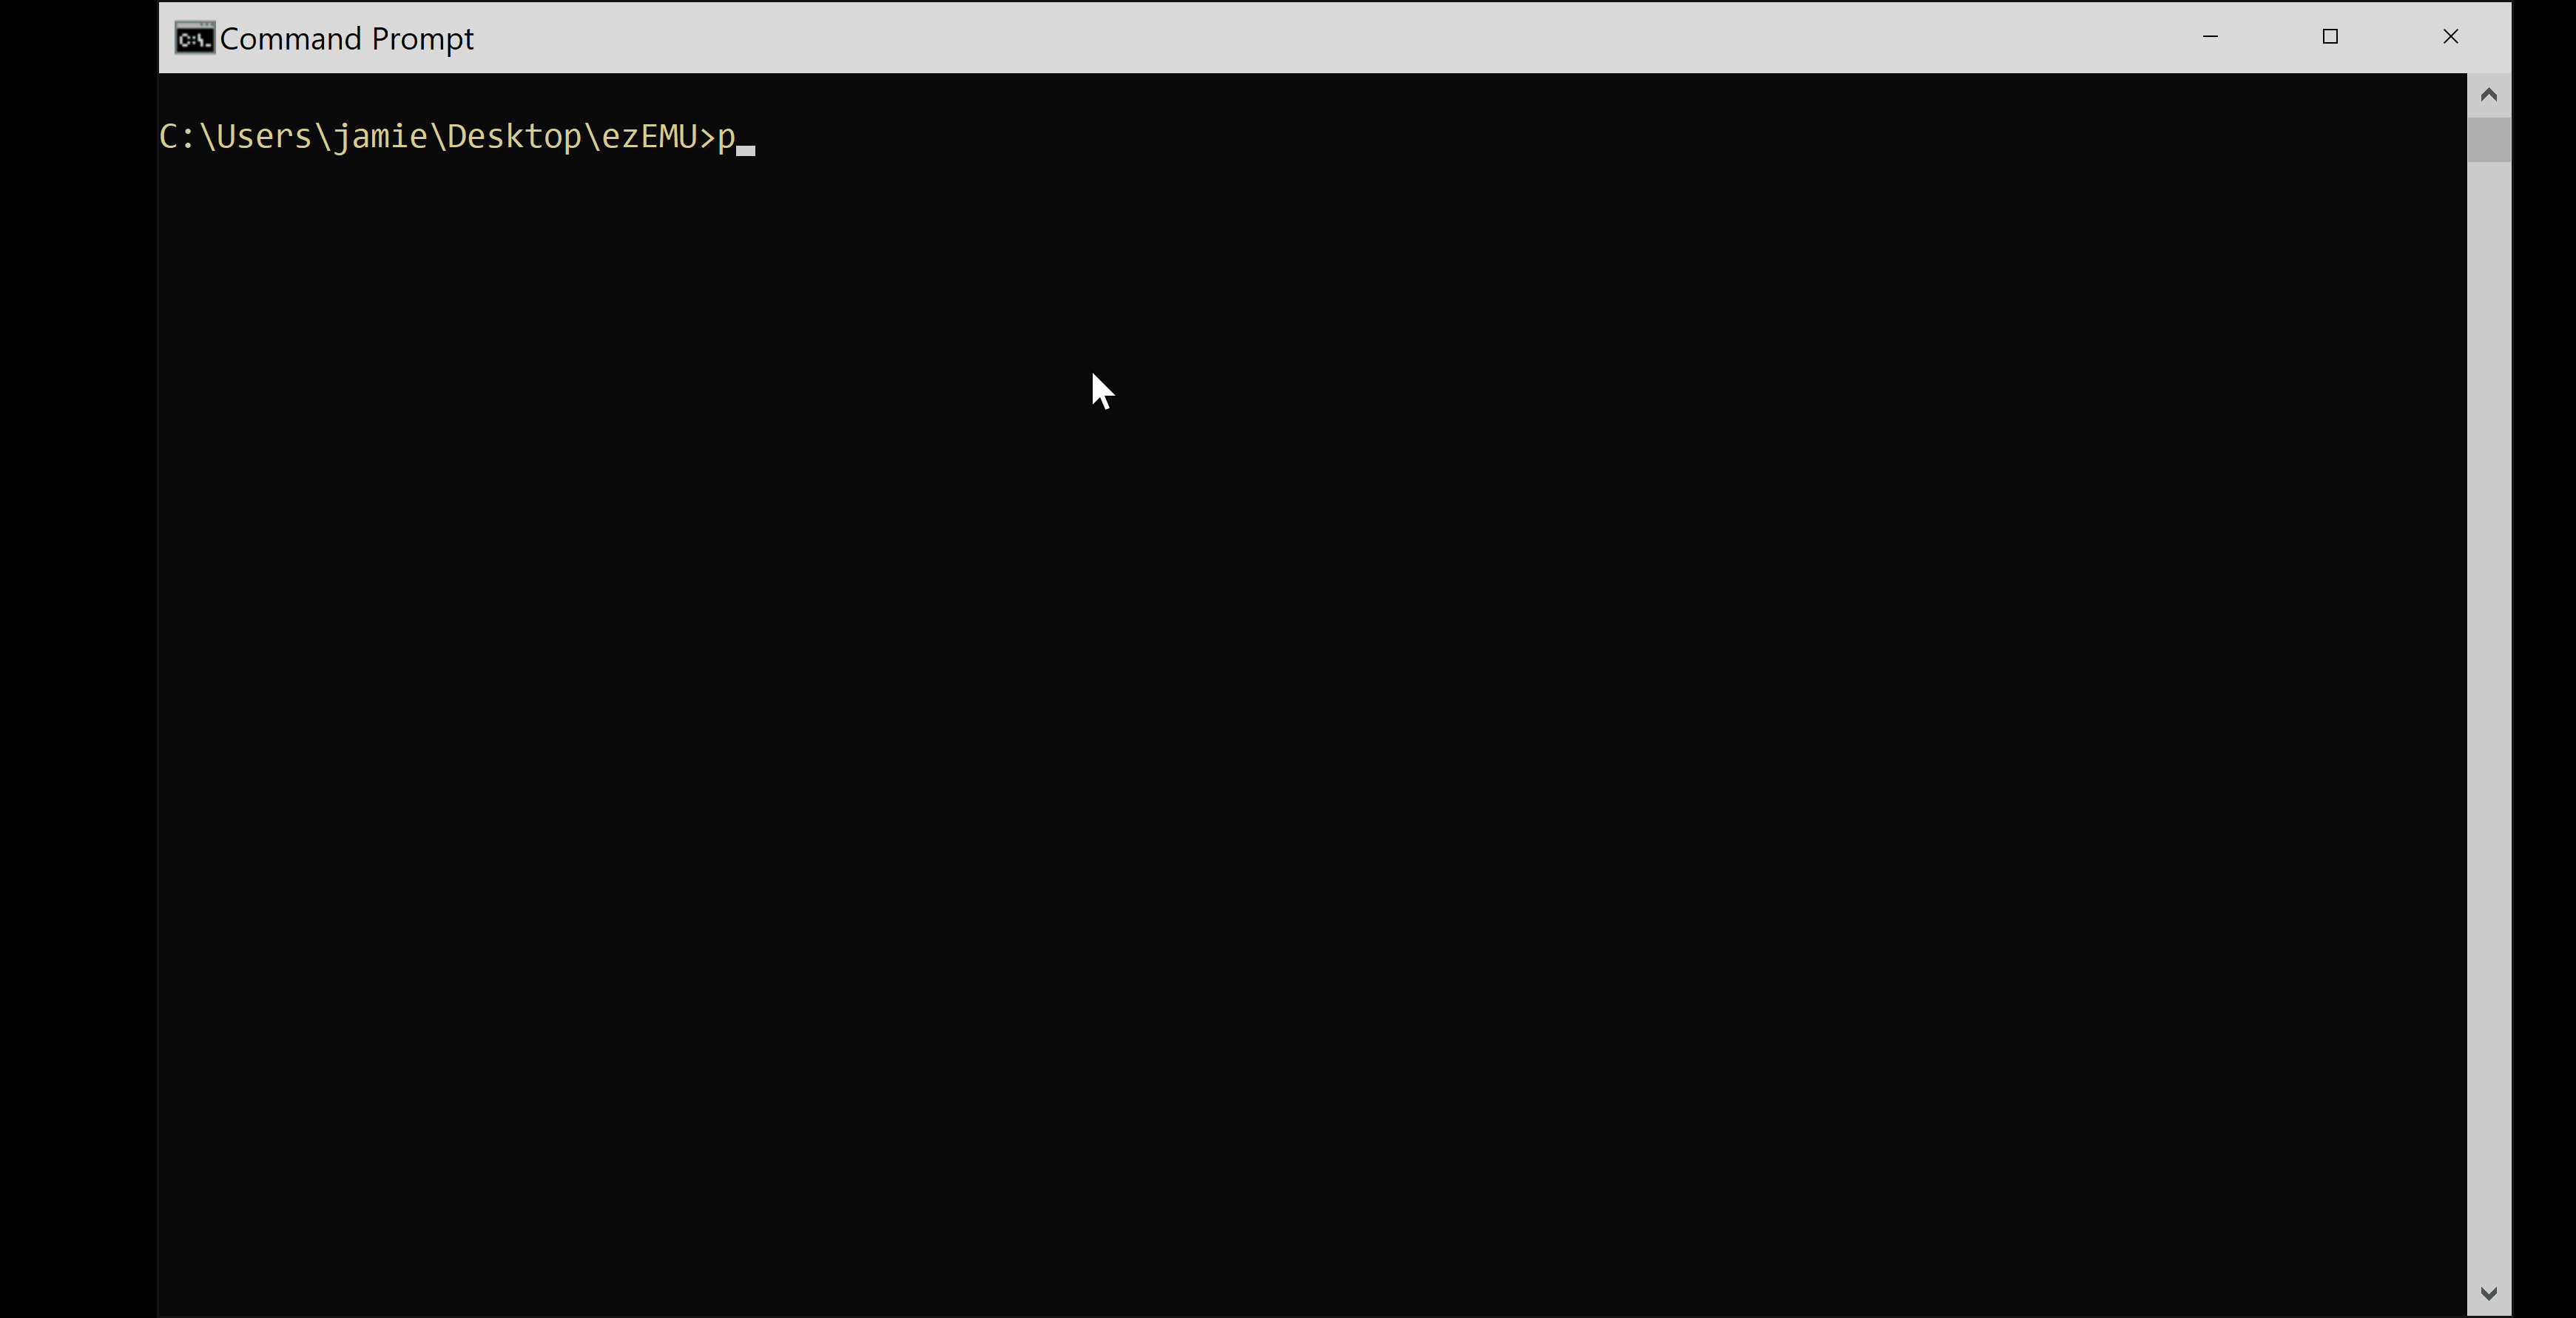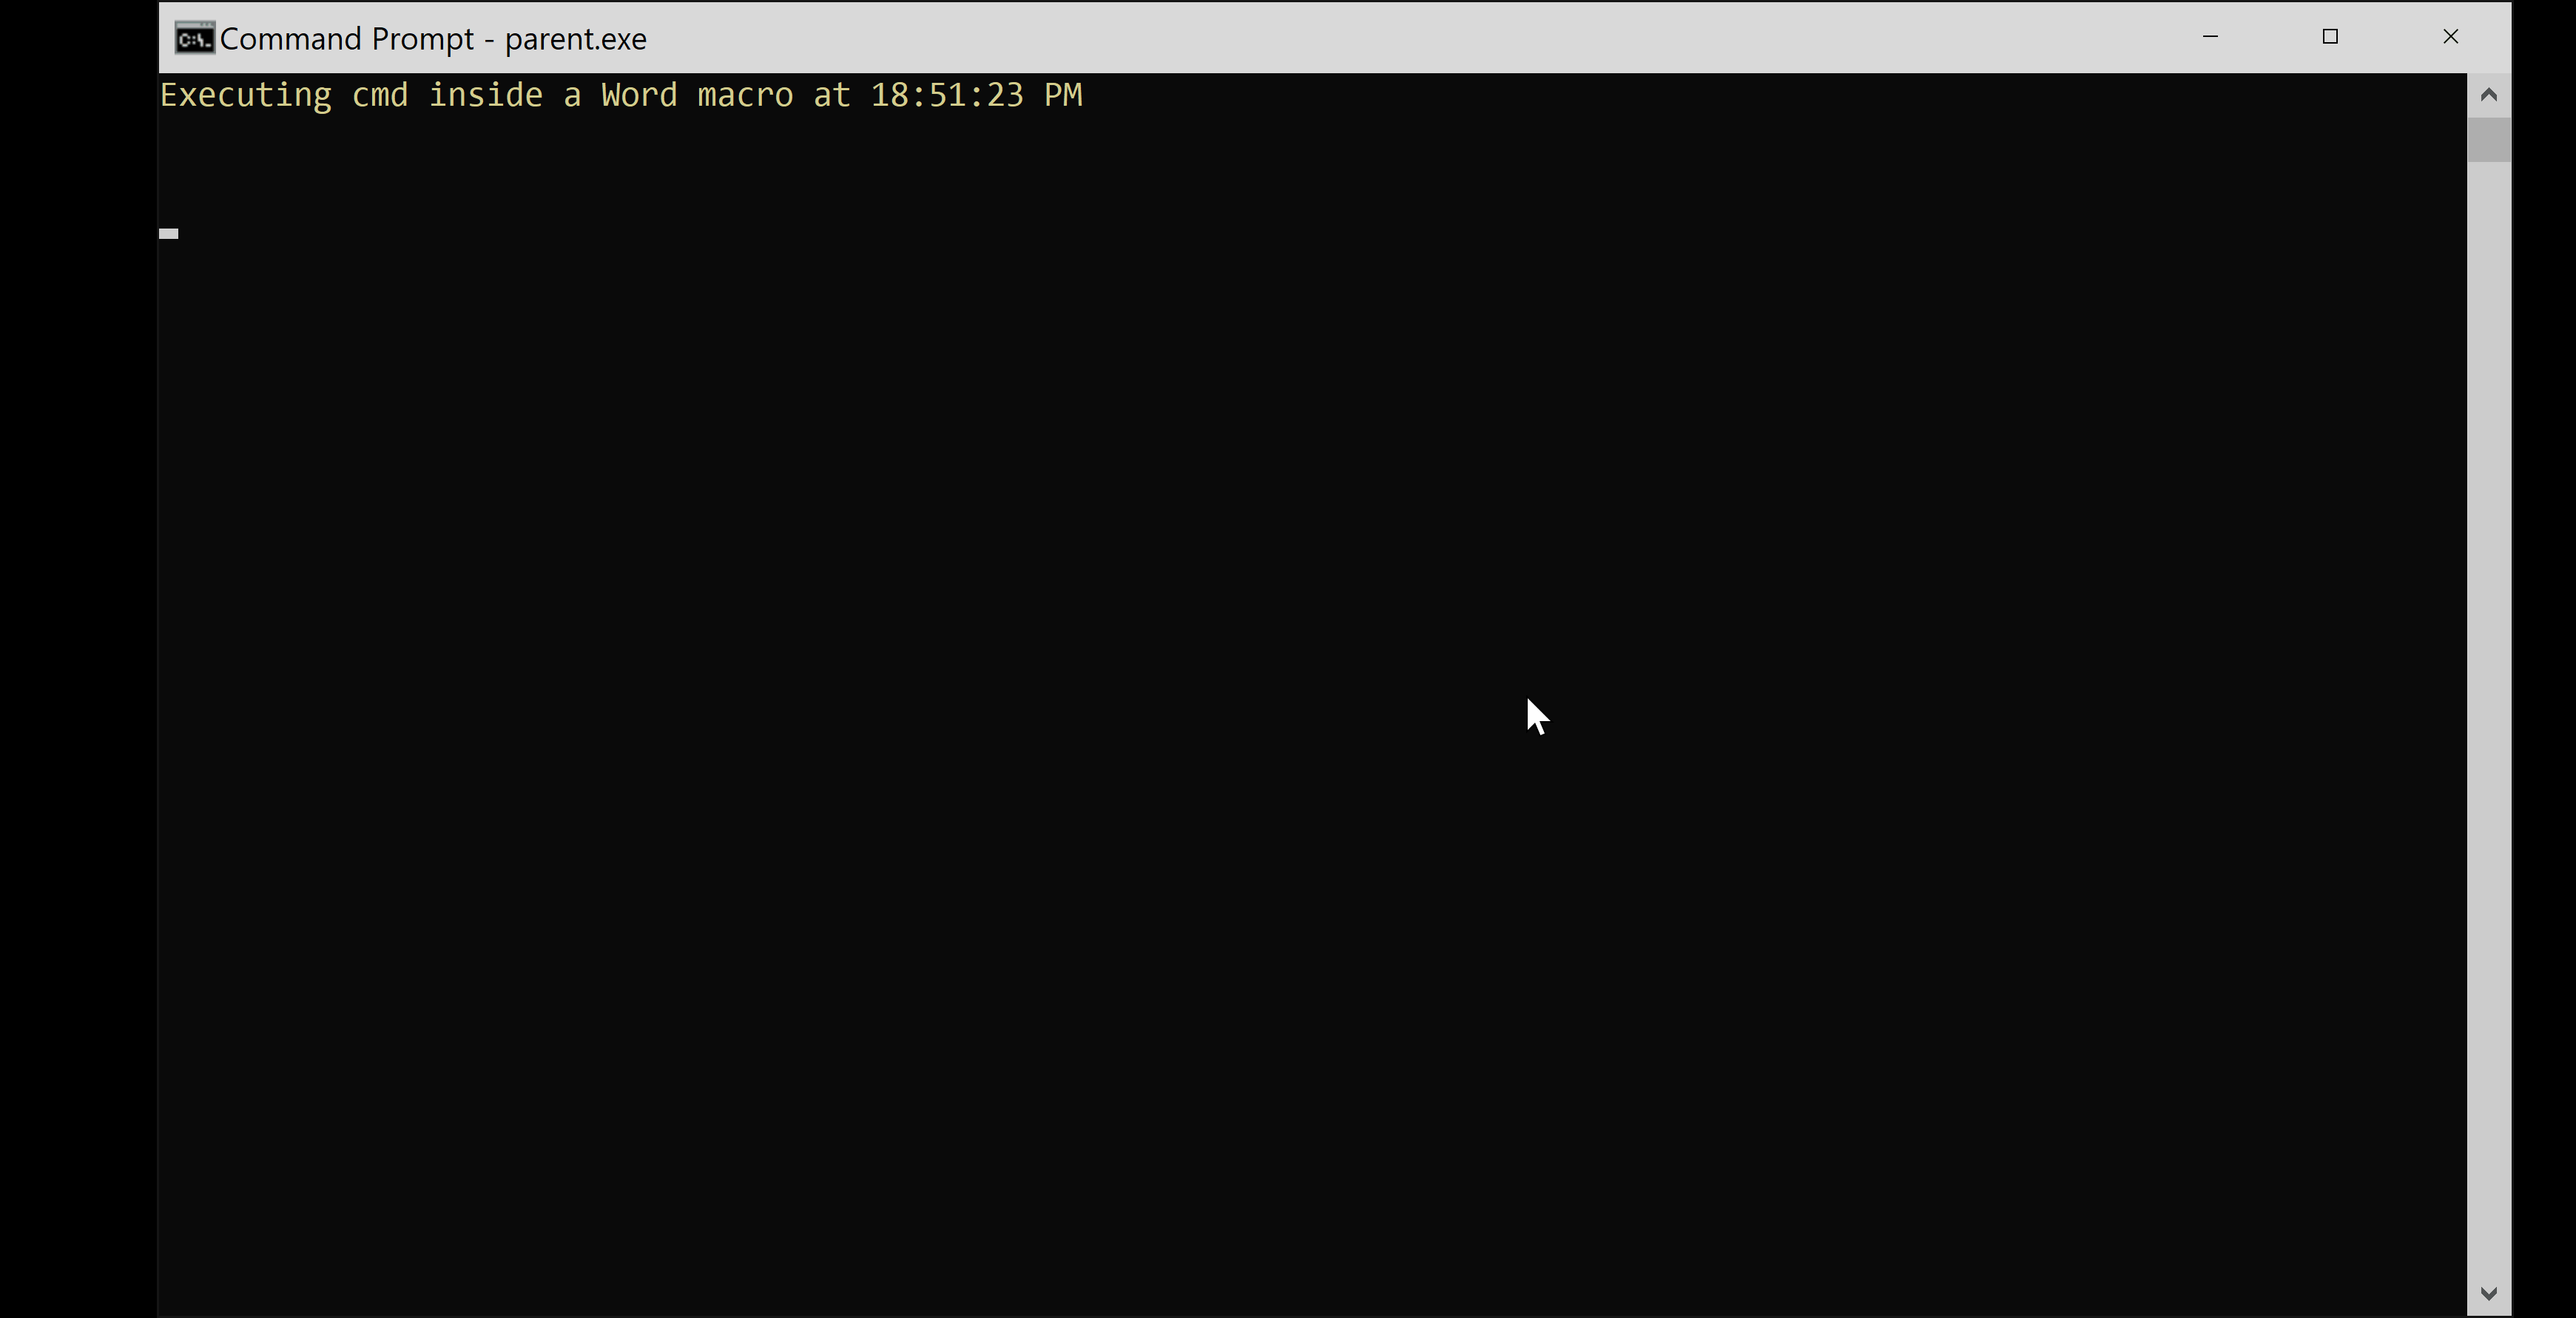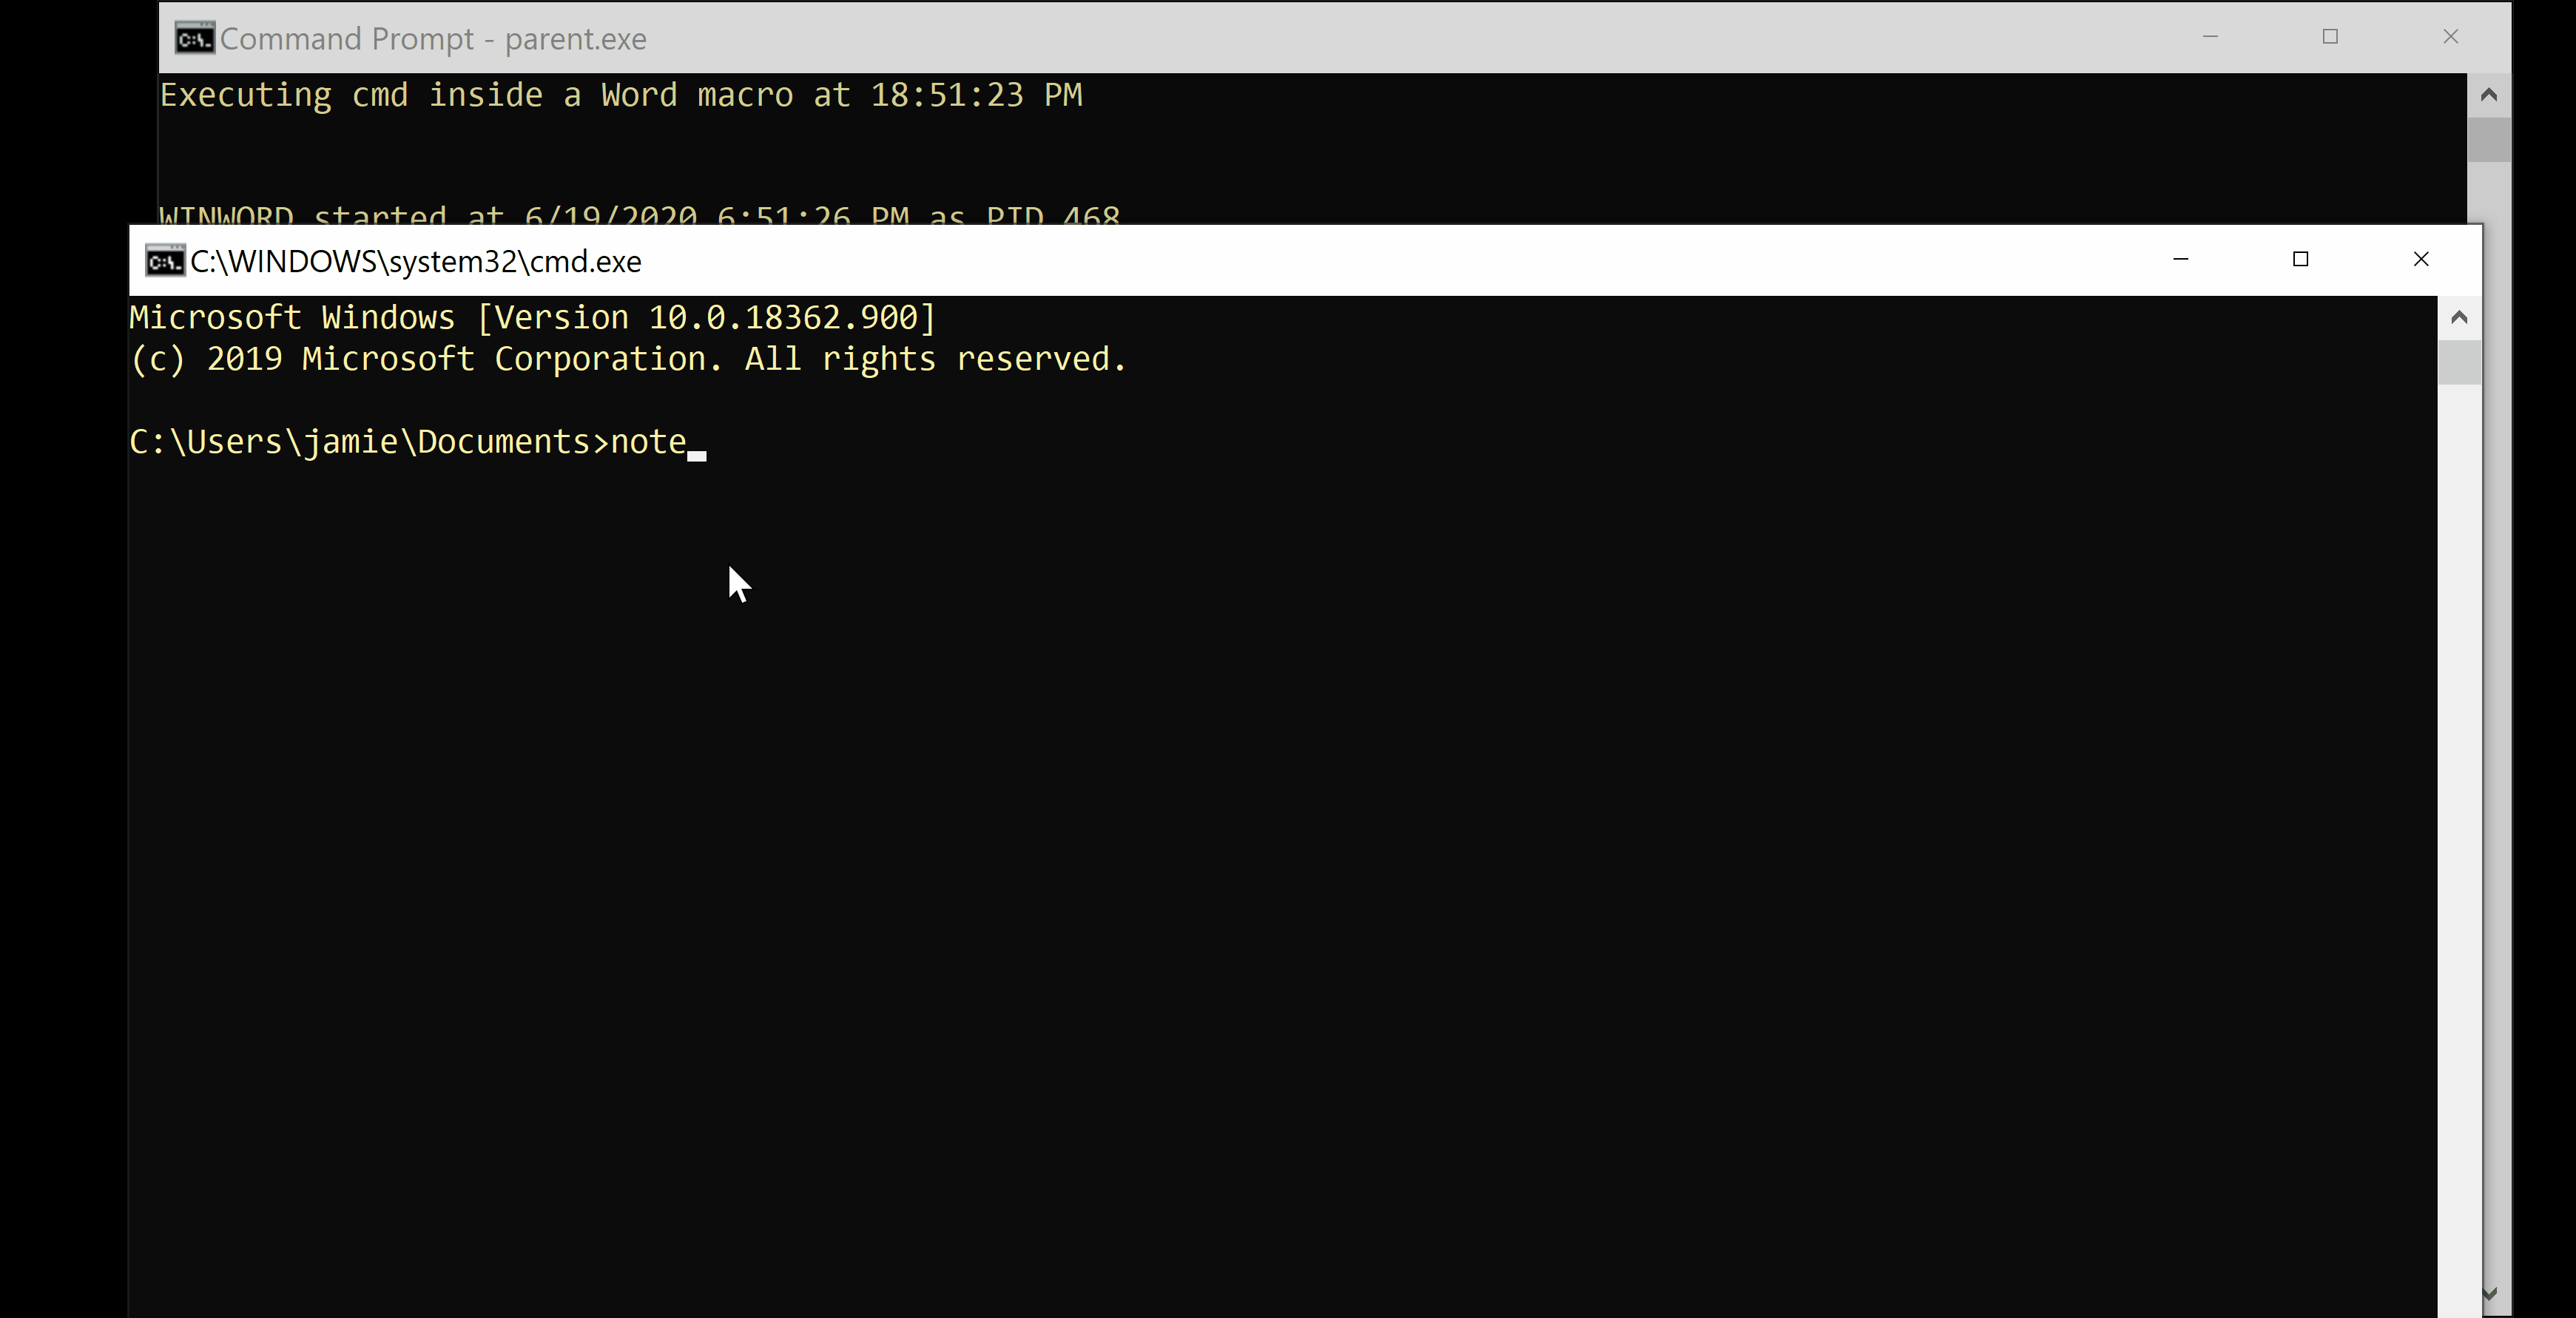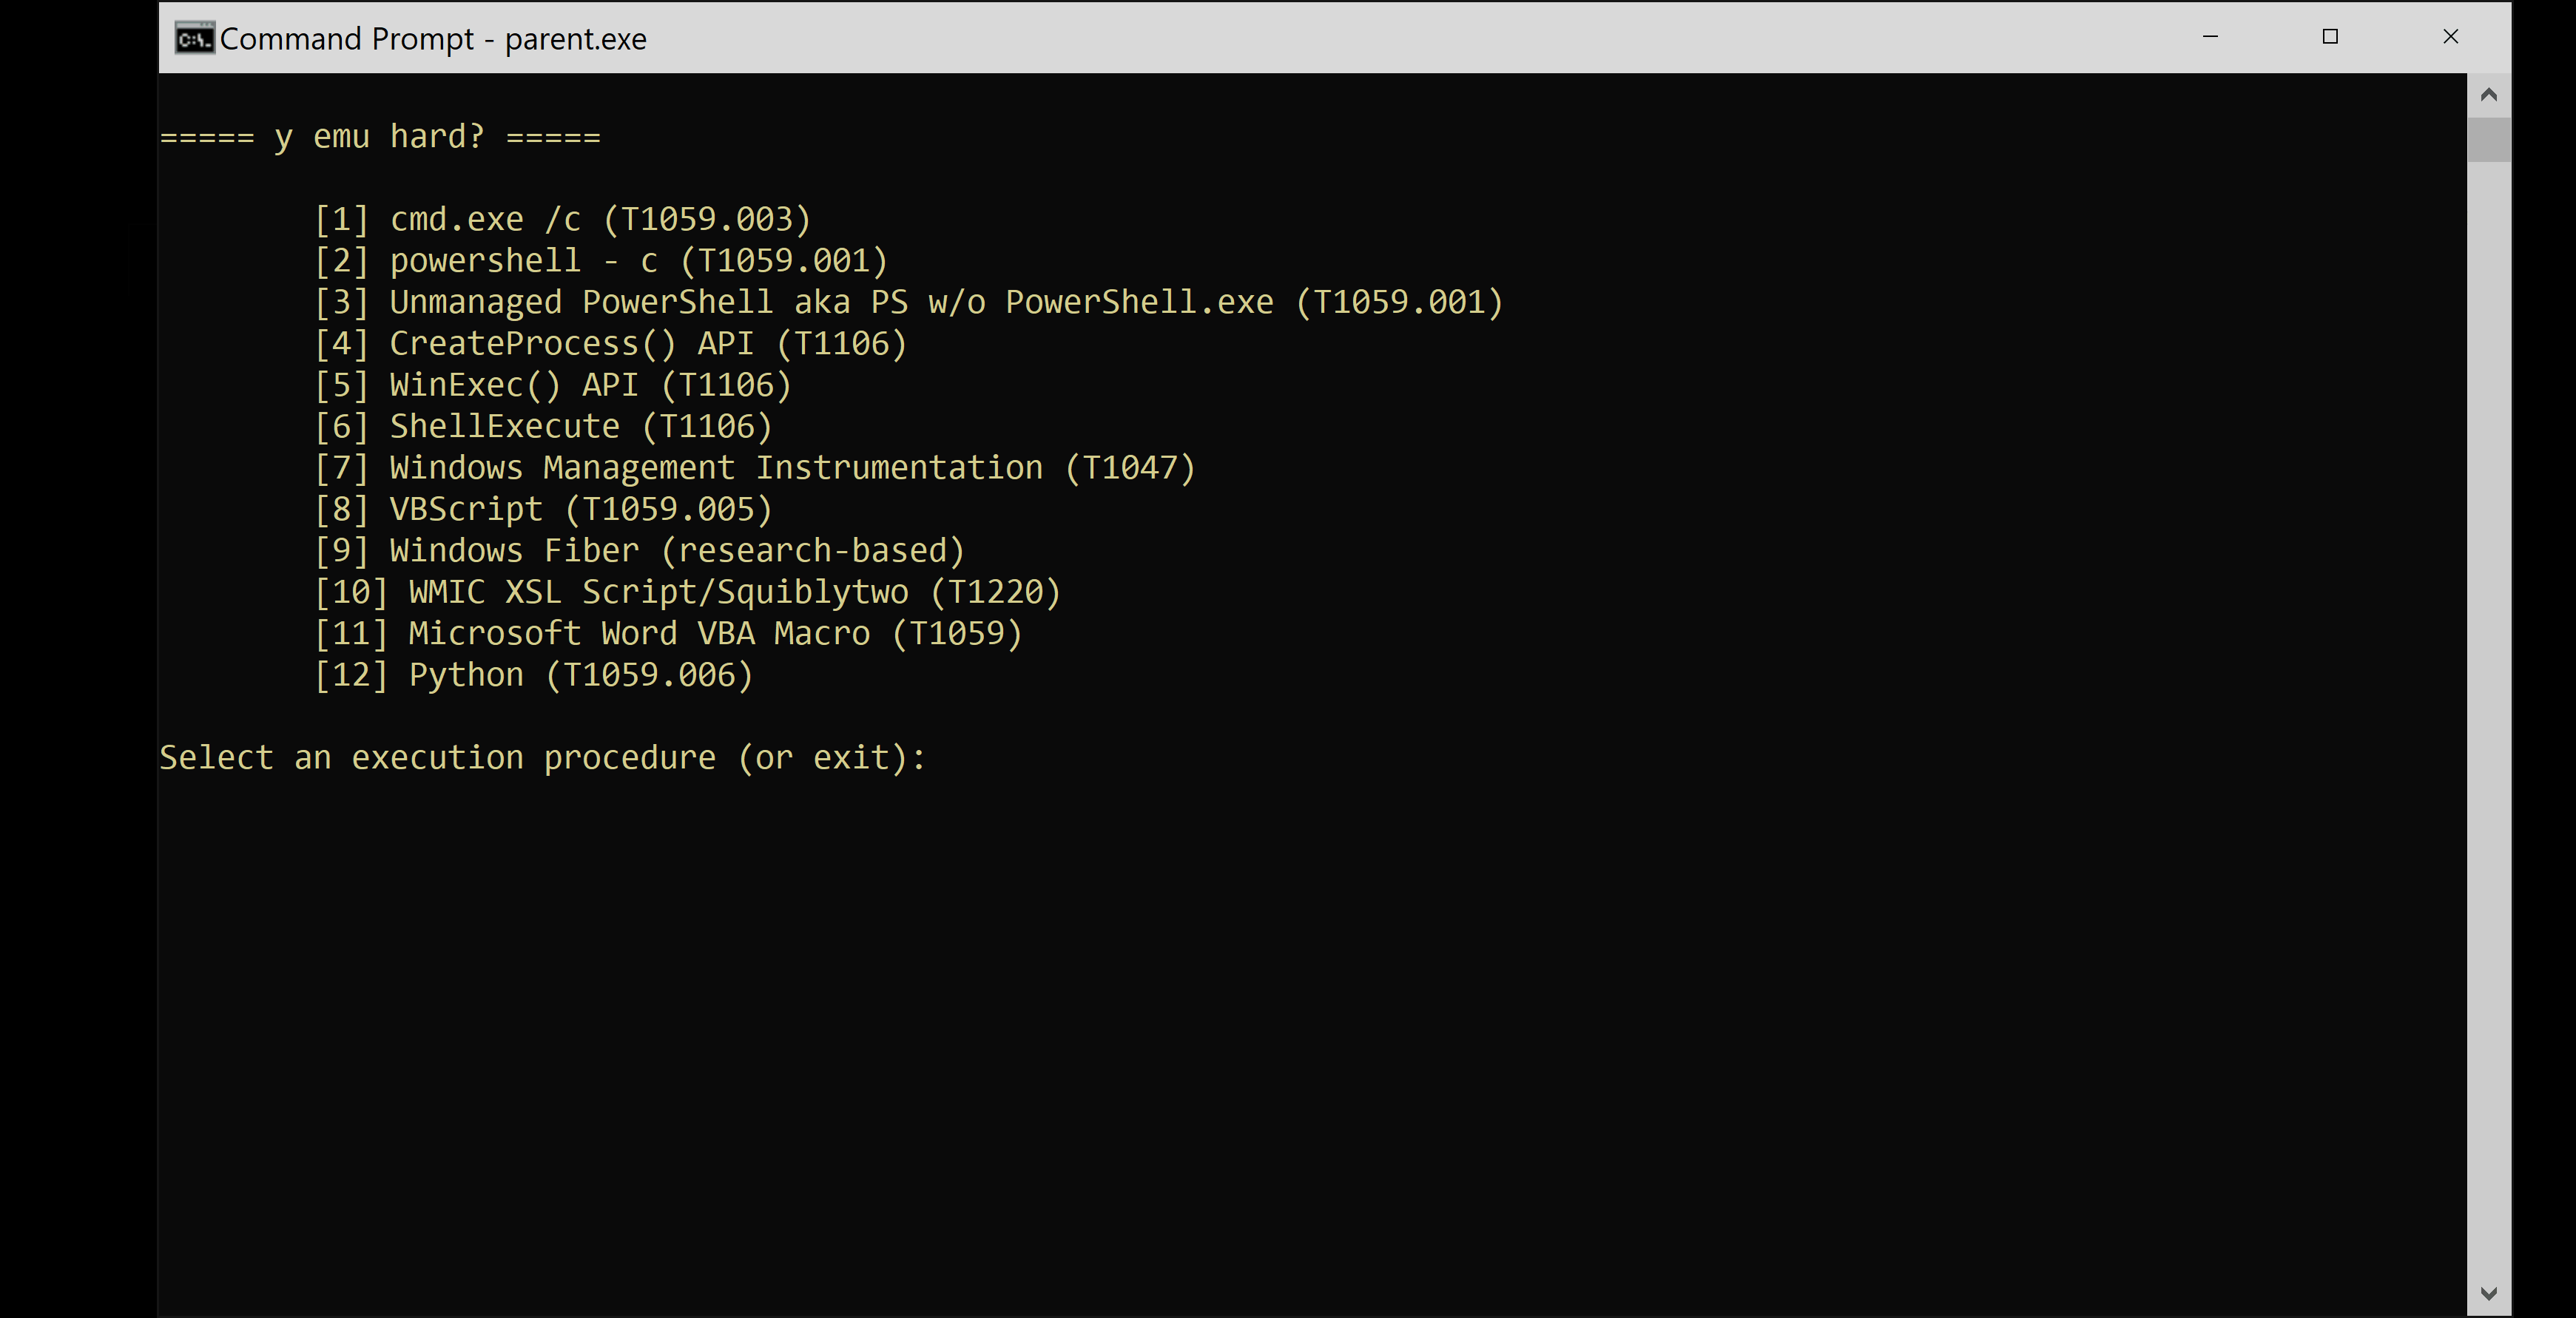 jwillyamz/ezemu
See adversary, do adversary: Simple execution of commands for defensive tuning/research (now with more ELF on the shelf)
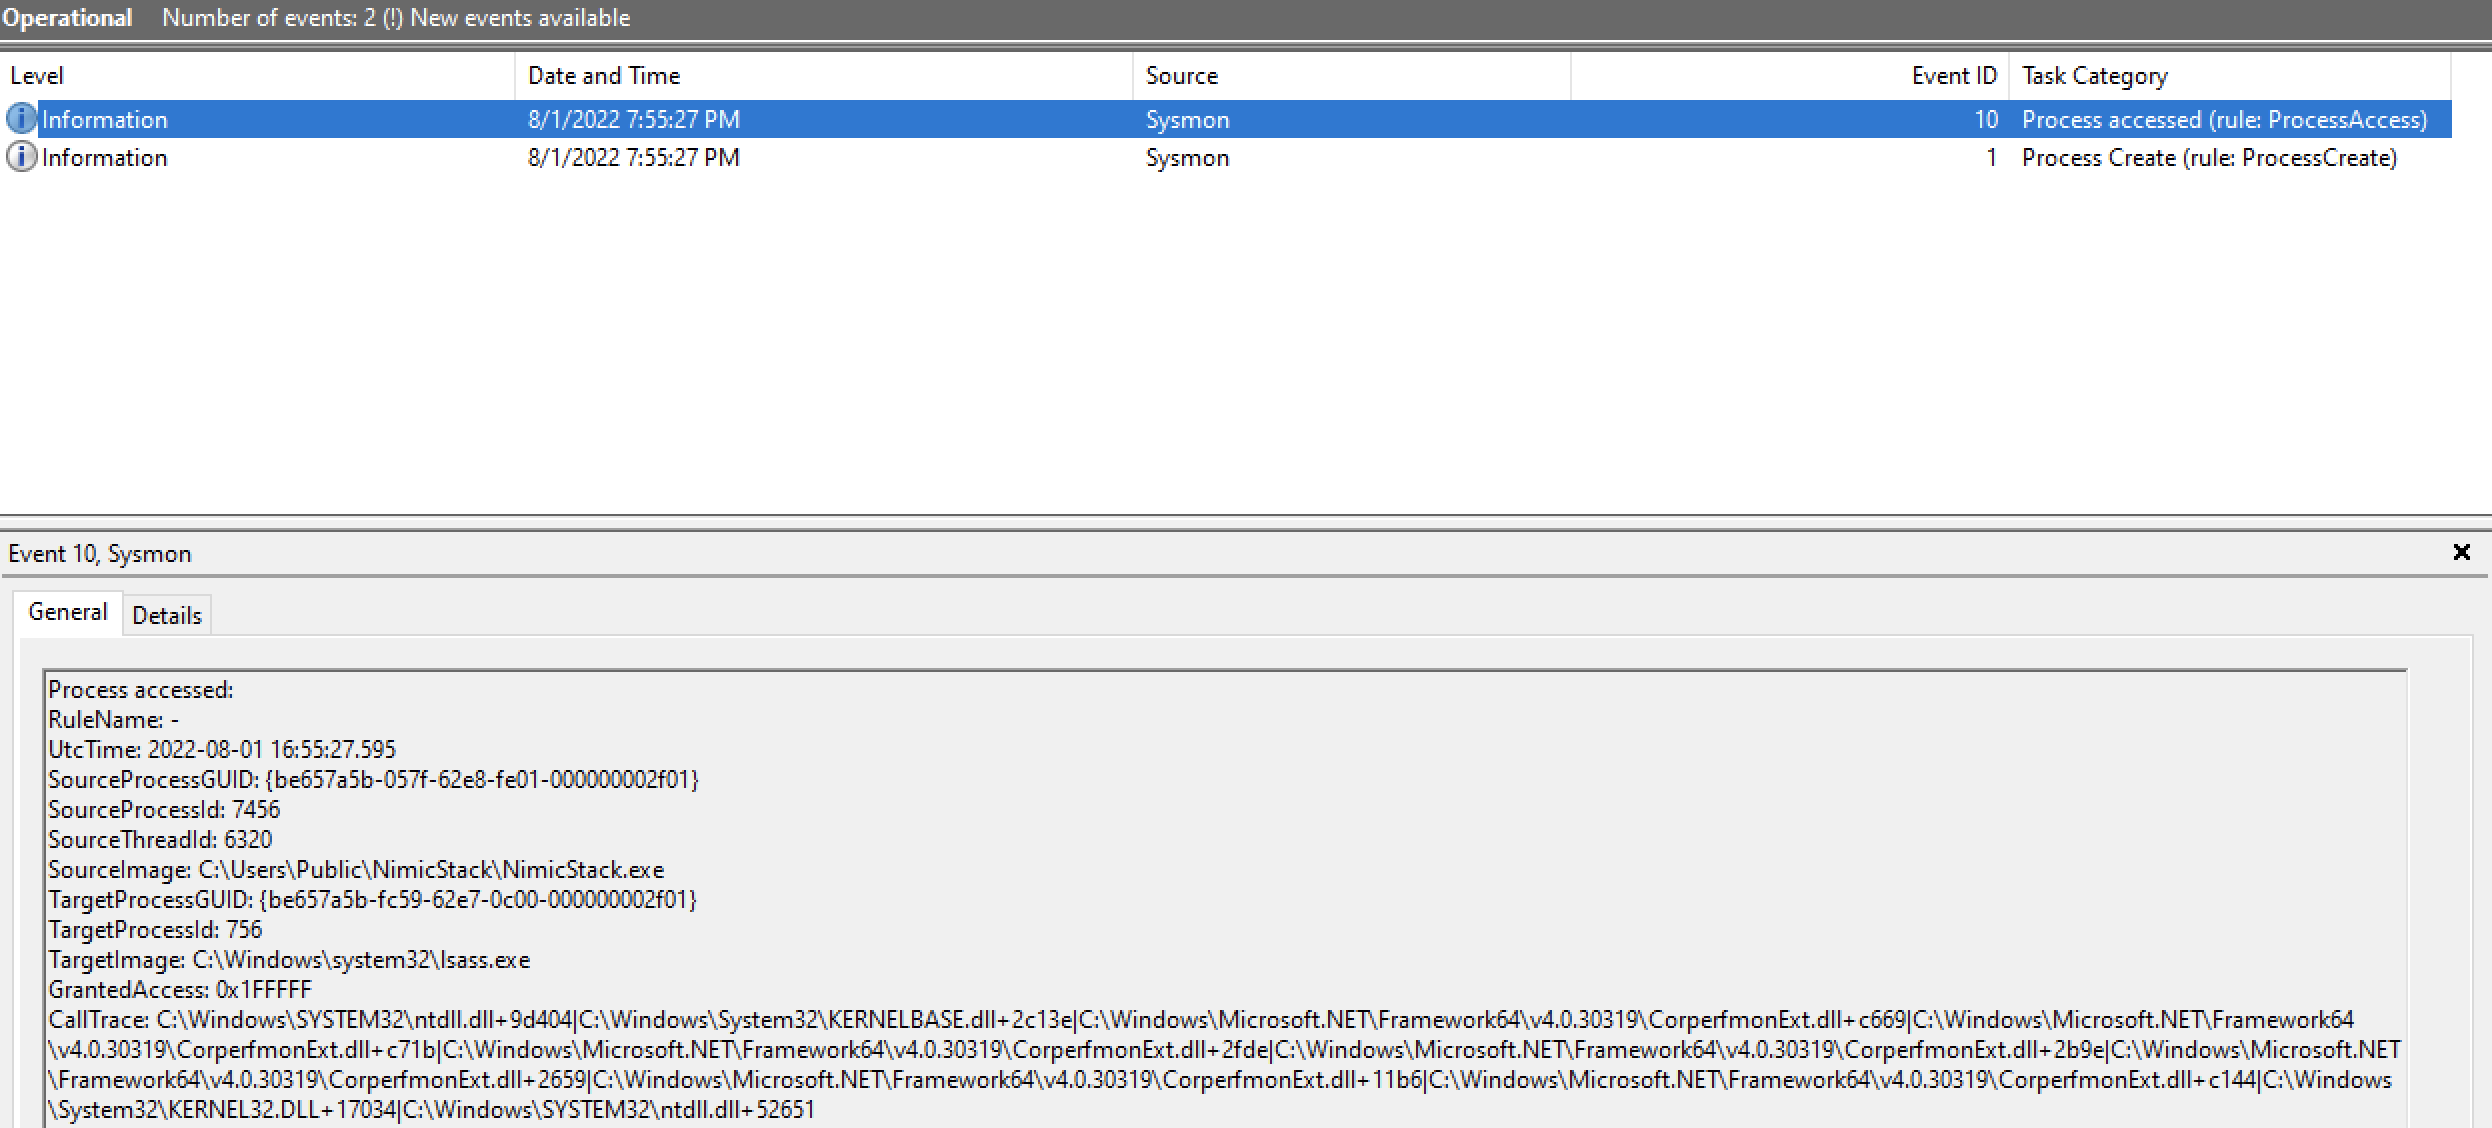 frkngksl/nimicstack
NimicStack is the pure Nim implementation of Call Stack Spoofing technique to mimic legitimate programs