
PE-Obfuscator
 saadahla/pe-obfuscator
PE obfuscator with Evasion in mind
adversarial-attackexploitationpayload-development+2
saadahla/pe-obfuscatorPE obfuscator with Evasion in mind
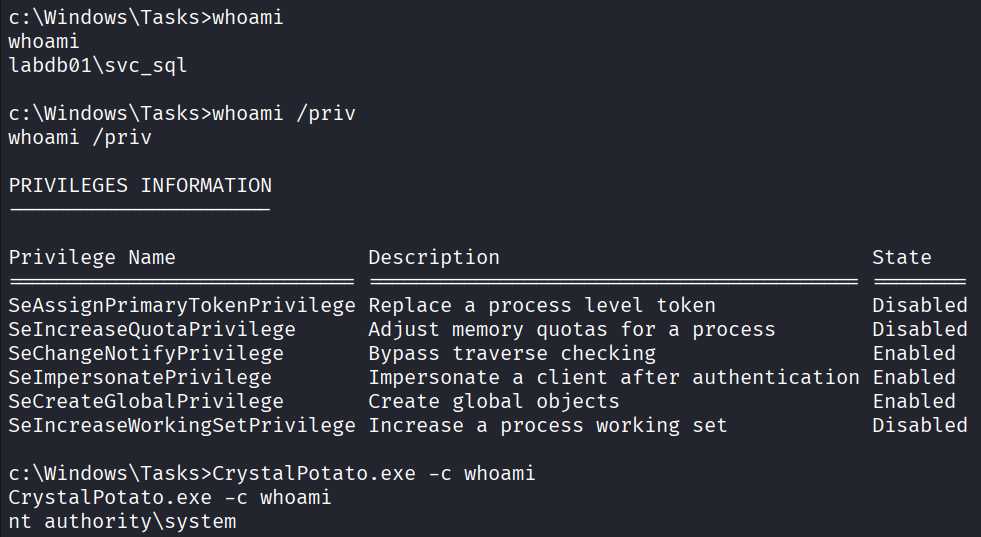 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 rad9800/vehapiresolve
Resolves Windows APIs at runtime using vectored exception handlers and hashed lookups to hide imports and slow reverse engineering of offensive…
 dosx-dev/dotnet_xorcryptor
A new simple and powerfull packer for malware
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
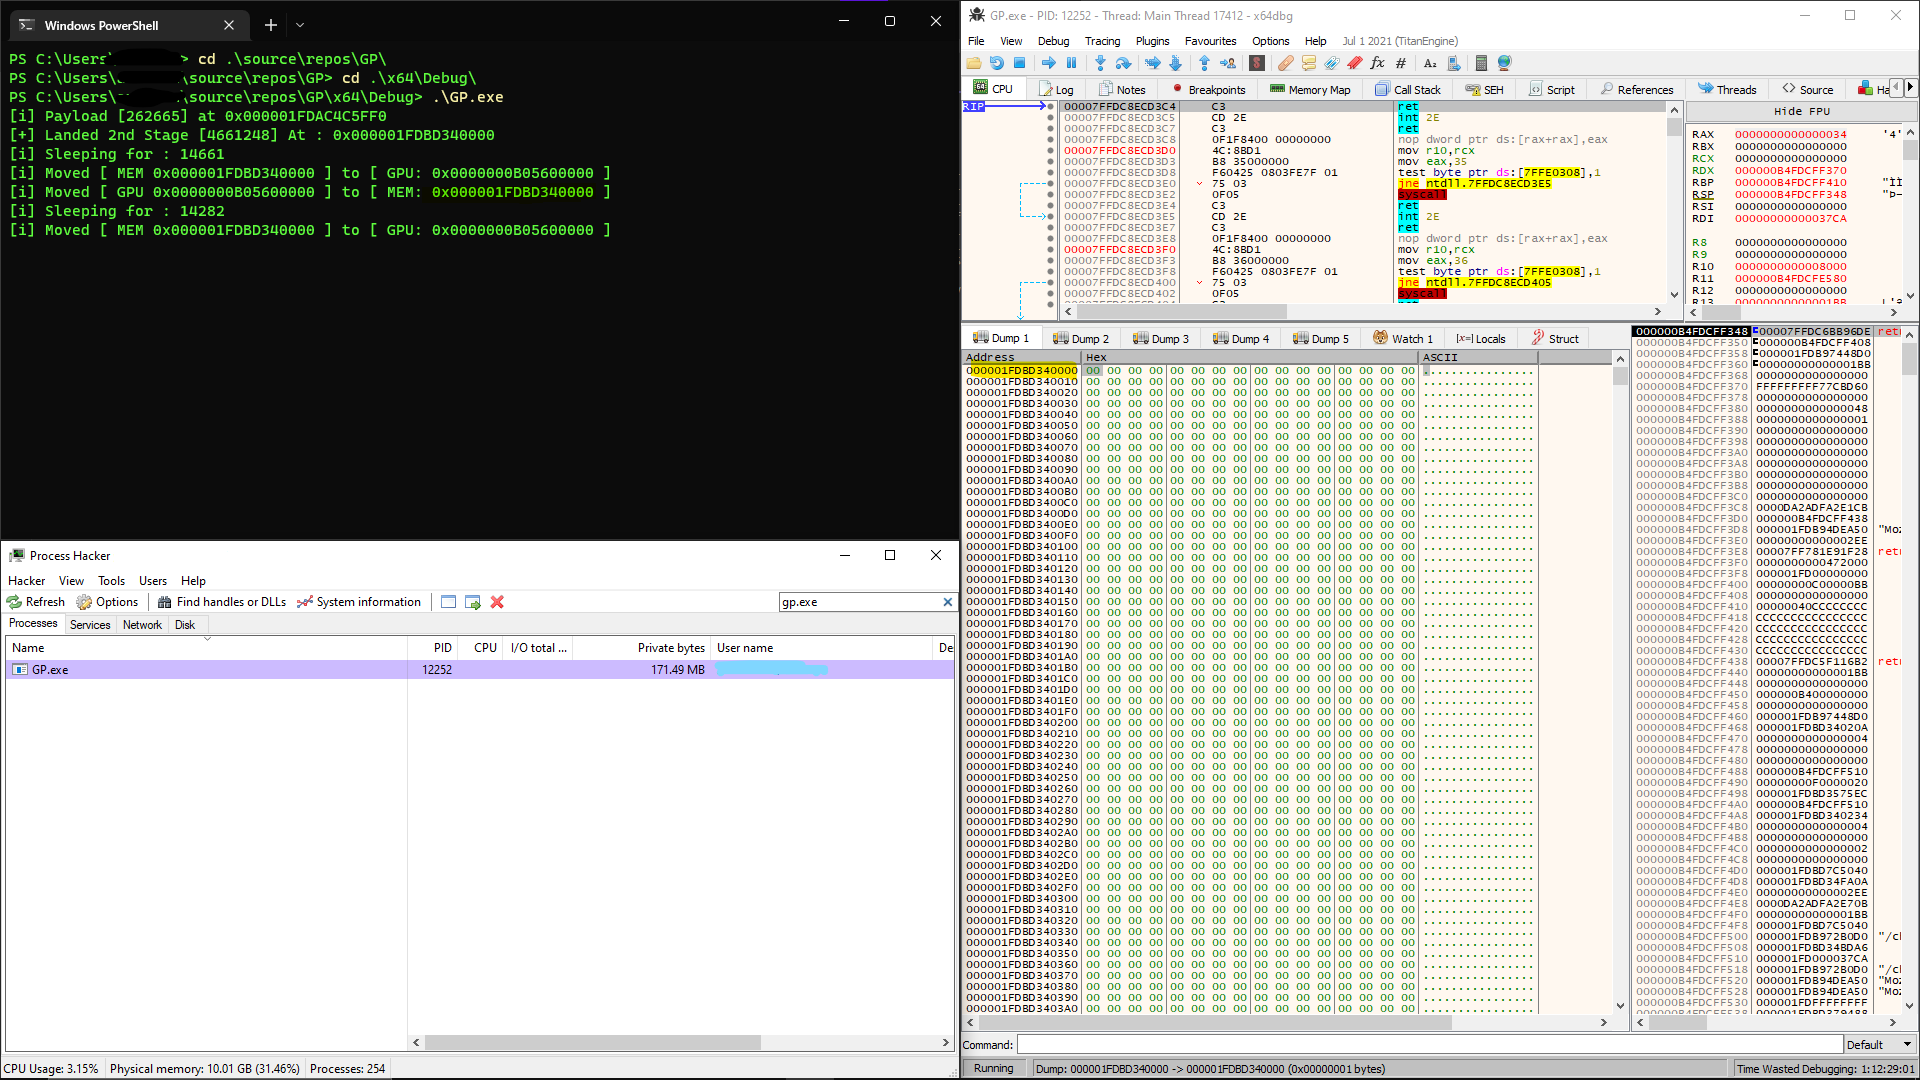 h1d3r/gpu_shellcode
Hides reflective payloads in GPU memory via CUDA APIs, wiping host memory during sleep and using a VEH handler to restore executable memory, evading…
 idov31/jormungandr
Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.
 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
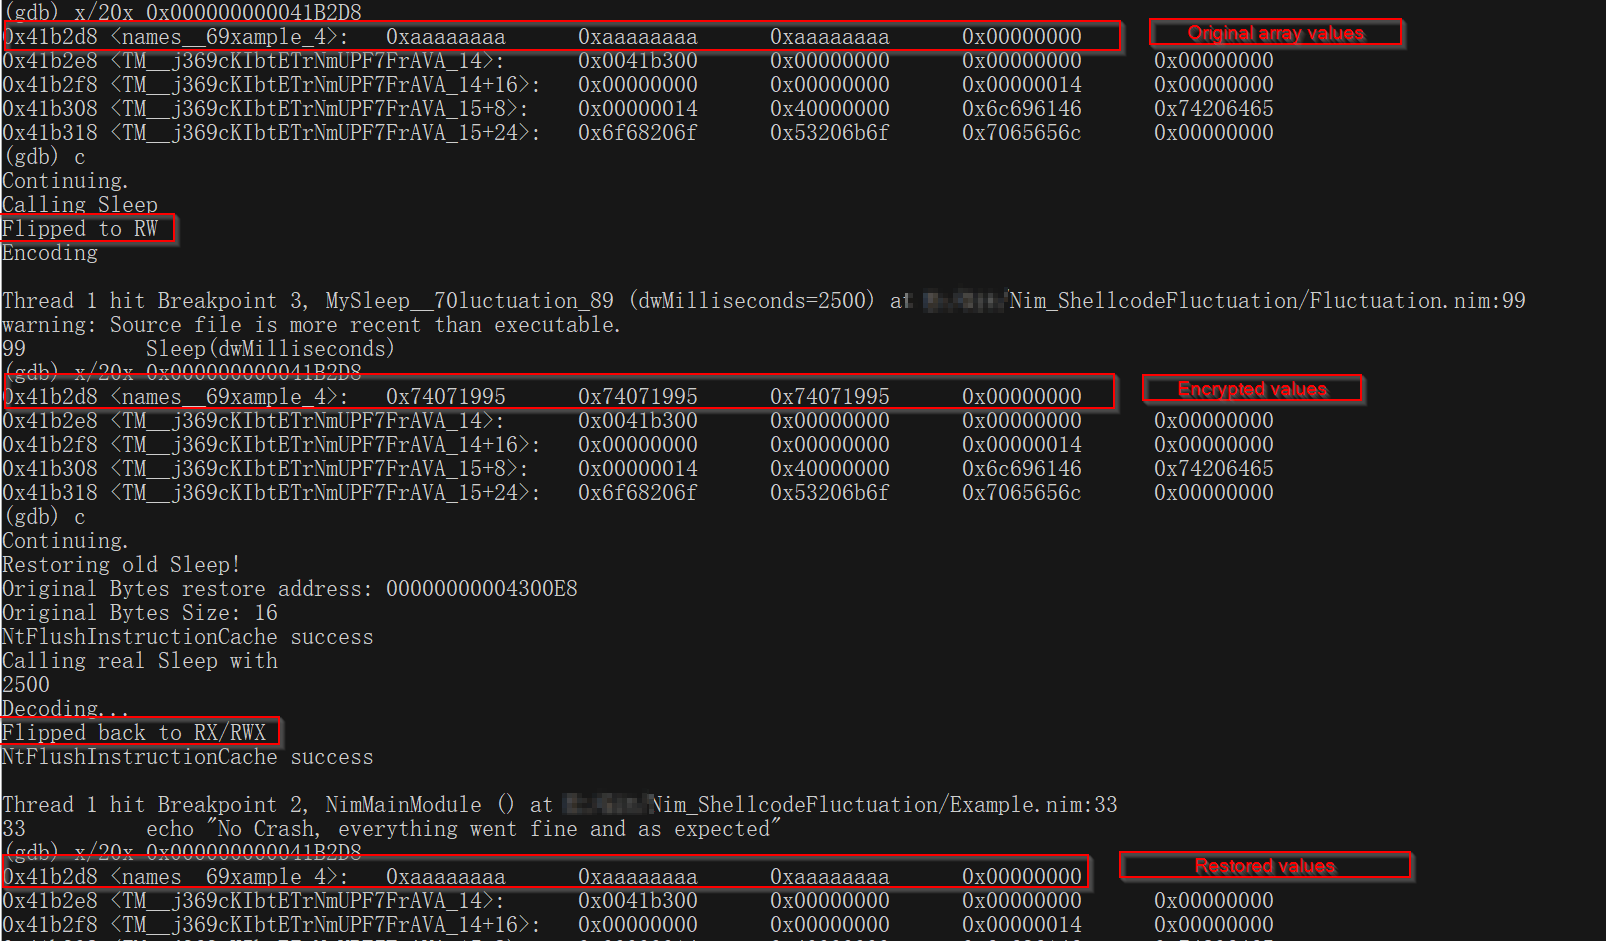 s3cur3th1ssh1t/nimshellcodefluctuation
ShellcodeFluctuation PoC ported to Nim
 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 thewover/dinvoke
Dynamically invoke arbitrary unmanaged code from managed code without PInvoke.
 d00mfist/mystikal
macOS Initial Access Payload Generator
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 thiagopeixoto/winsos-poc
A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
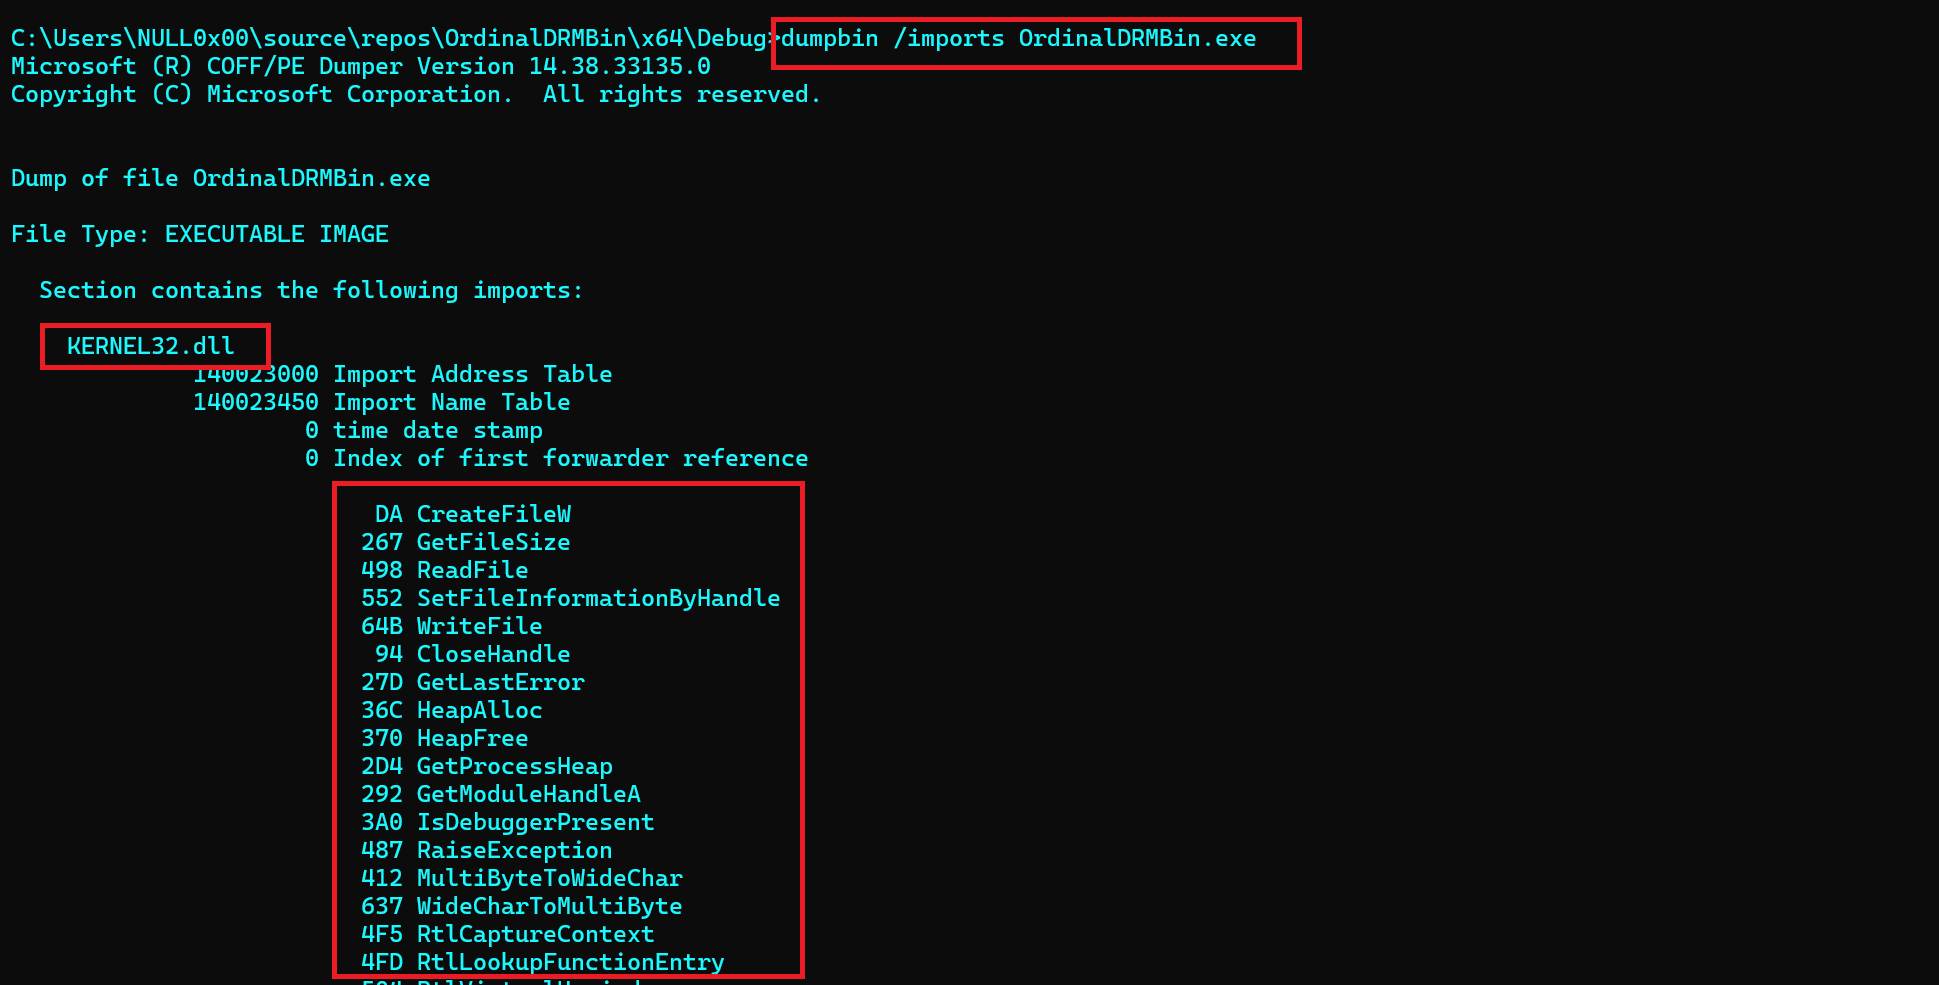 maldev-academy/drmbinviaordinalimports
Create Anti-Copy DRM Malware
 frank2/blenny
A payload delivery system which embeds payloads in an executable's icon file!