

RTA
 endgameinc/rta
Scripted framework for simulating over 50 MITRE ATT&CK techniques to test blue team detection capabilities. Includes Python scripts and a compiled…
adversarial-attackeducationlabs-practice+2
1.1k
endgameinc/rtaScripted framework for simulating over 50 MITRE ATT&CK techniques to test blue team detection capabilities. Includes Python scripts and a compiled…
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 s12cybersecurity/windefenderkiller
Windows Defender Killer | Registry-Based Disablement + BYOVD Process Termination (C++)
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
 d419h/iconjector
Inject DLLs into the explorer process using icons
 rsmudge/unhook-bof
Remove API hooks from a Beacon process.
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 rasta-mouse/process-inject-kit
Port of Cobalt Strike's Process Inject Kit
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 saadahla/pspersist
Dropping a powershell script at %HOMEPATH%\Documents\WindowsPowershell\ , that contains the implant's path , and whenever powershell process is…
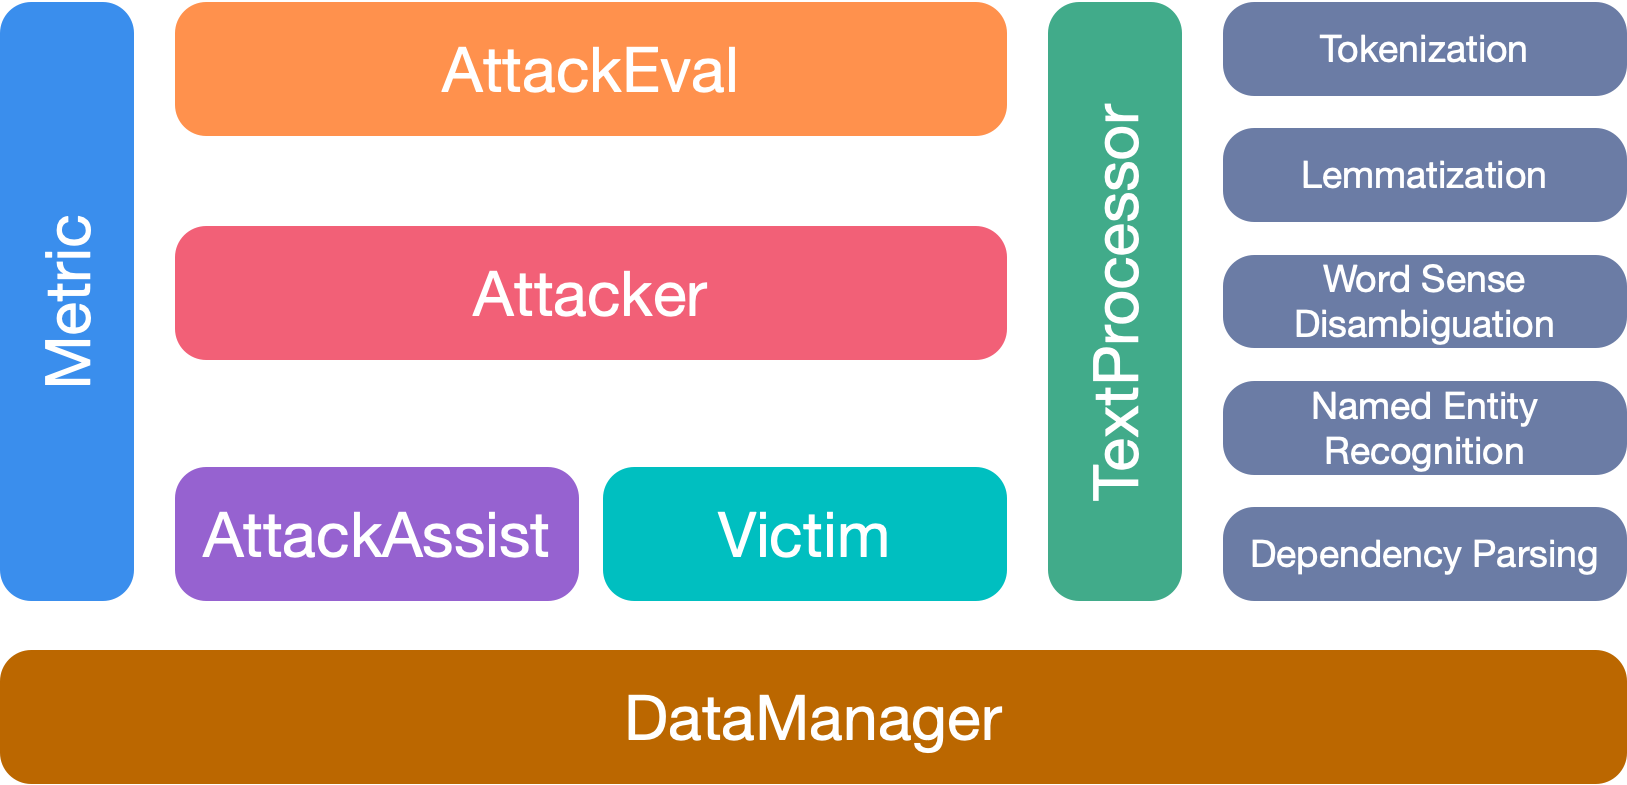 thunlp/openattack
An Open-Source Package for Textual Adversarial Attack.
 dis0rder0x00/obex
Obex – Blocking unwanted DLLs in user mode

 soufianetahiri/teamsntlmleak
Leak NTLM via Website tab in teams via MS Office
 alwashali/detection-validation
Detection rule validation