

MAAD-AF
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
adversarial-attackcloud-securitydata-exfiltration+6
429
vectra-ai-research/maad-afMAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 bishopfox/sliver
Adversary Emulation Framework
 mitre/brawl-public-game-001
Data from a BRAWL Automated Adversary Emulation Exercise
 soufianetahiri/teamsntlmleak
Leak NTLM via Website tab in teams via MS Office
 ioactive/i-know-where-your-page-lives
I Know Where Your Page Lives: Derandomizing the latest Windows 10 Kernel - ZeroNights 2016
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
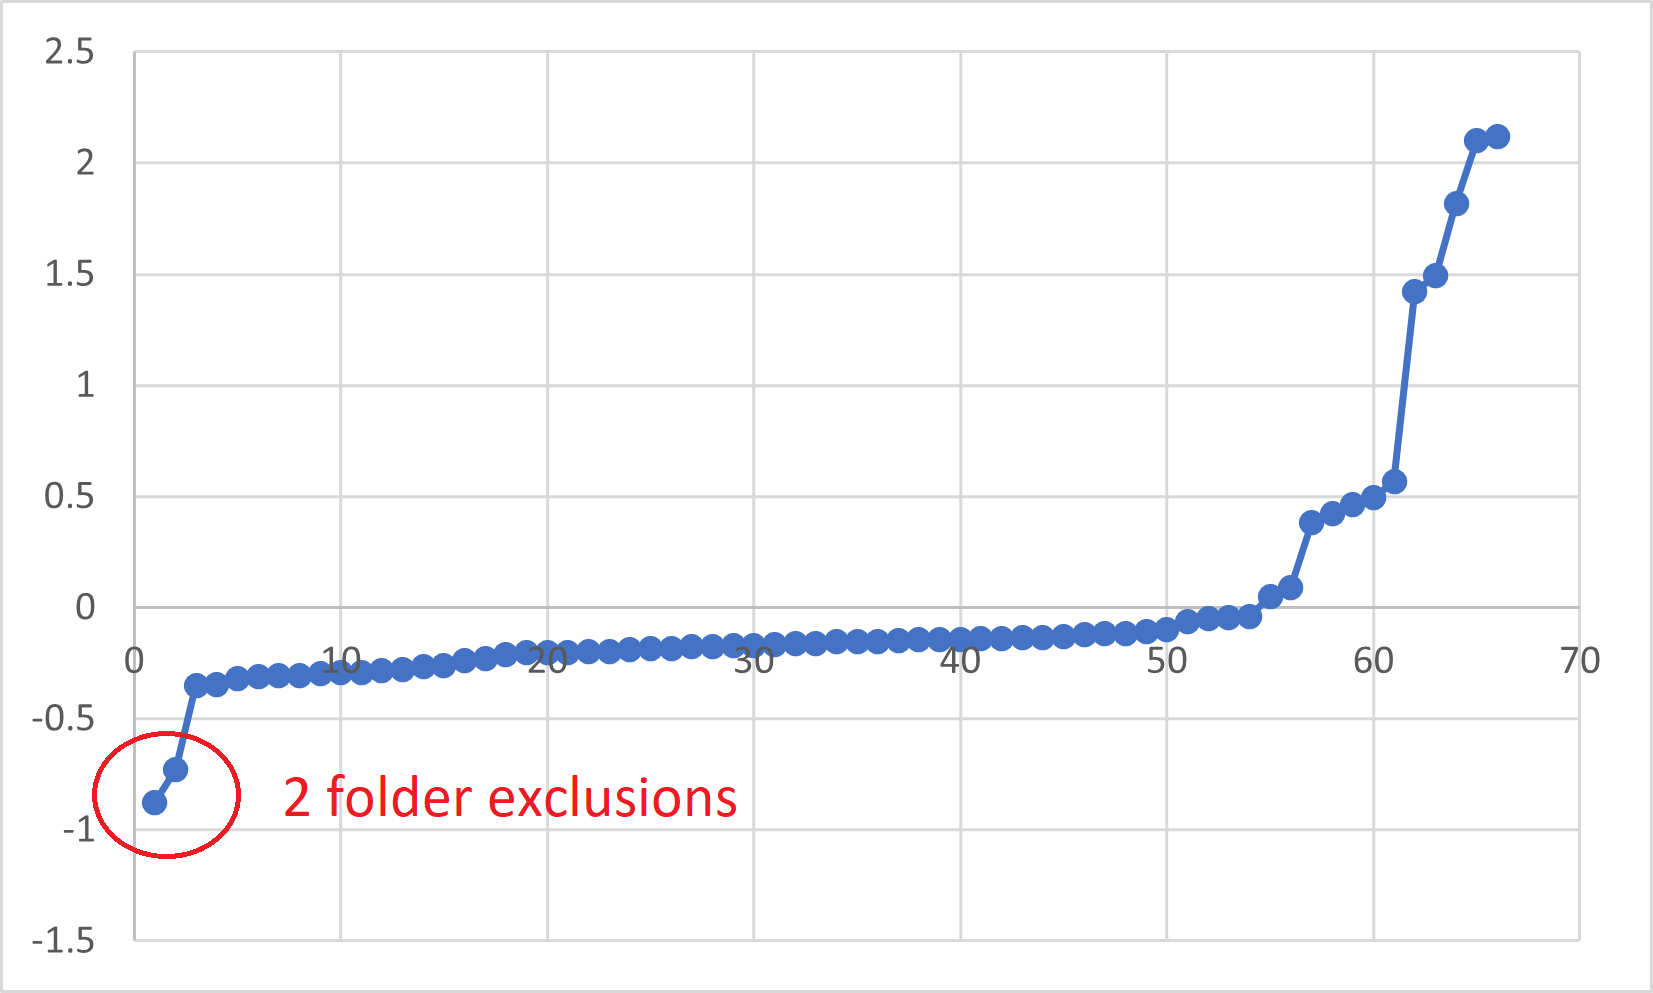 bananabr/timeexception
A tool to find folders excluded from AV real-time scanning using a time oracle
 r3drun3/magnet
Purple-team telemetry & simulation toolkit.
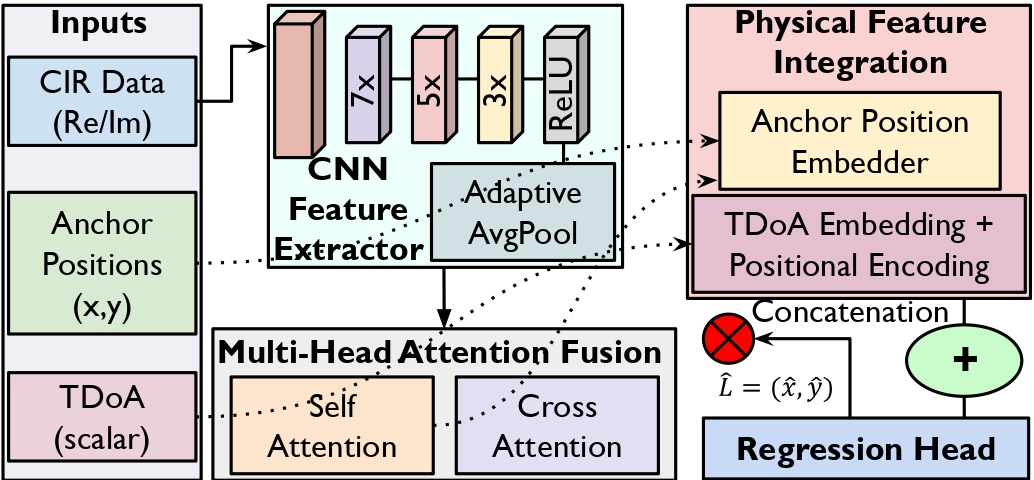 sec5gloc/sec5gloc
Adversary-resilient deep learning architecture for secure 5G indoor localization, combining CNN and multi-head attention to defend against signal…
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
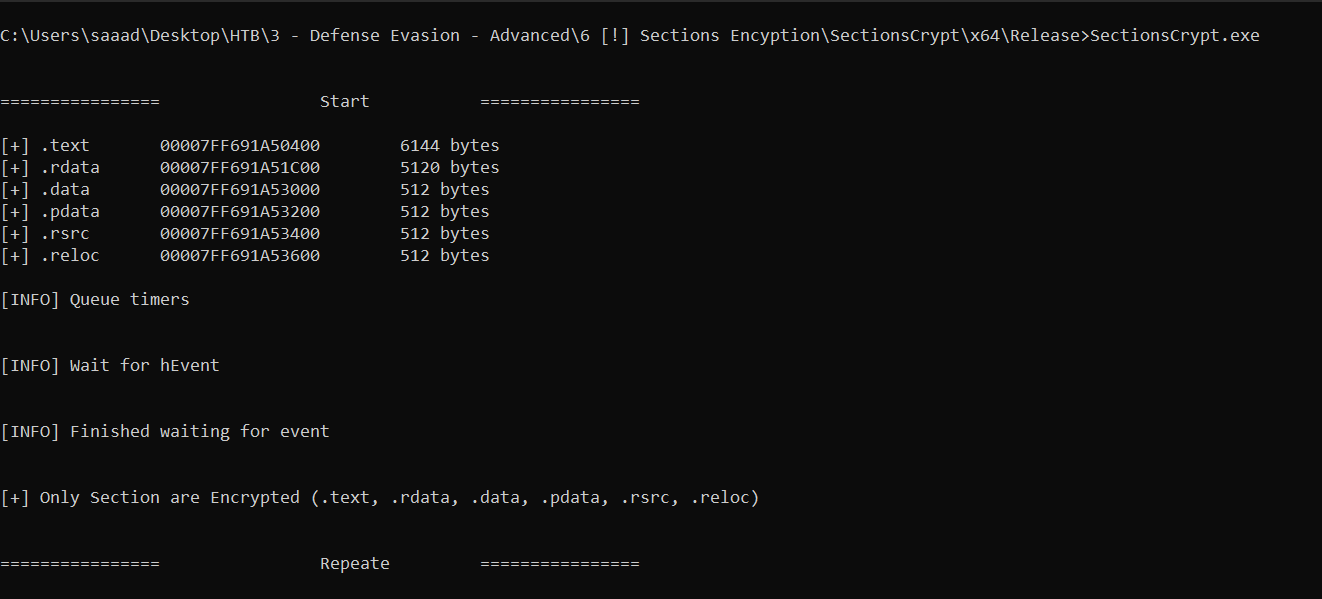 saadahla/d1rksleep
Improved version of EKKO by @5pider that Encrypts only Image Sections
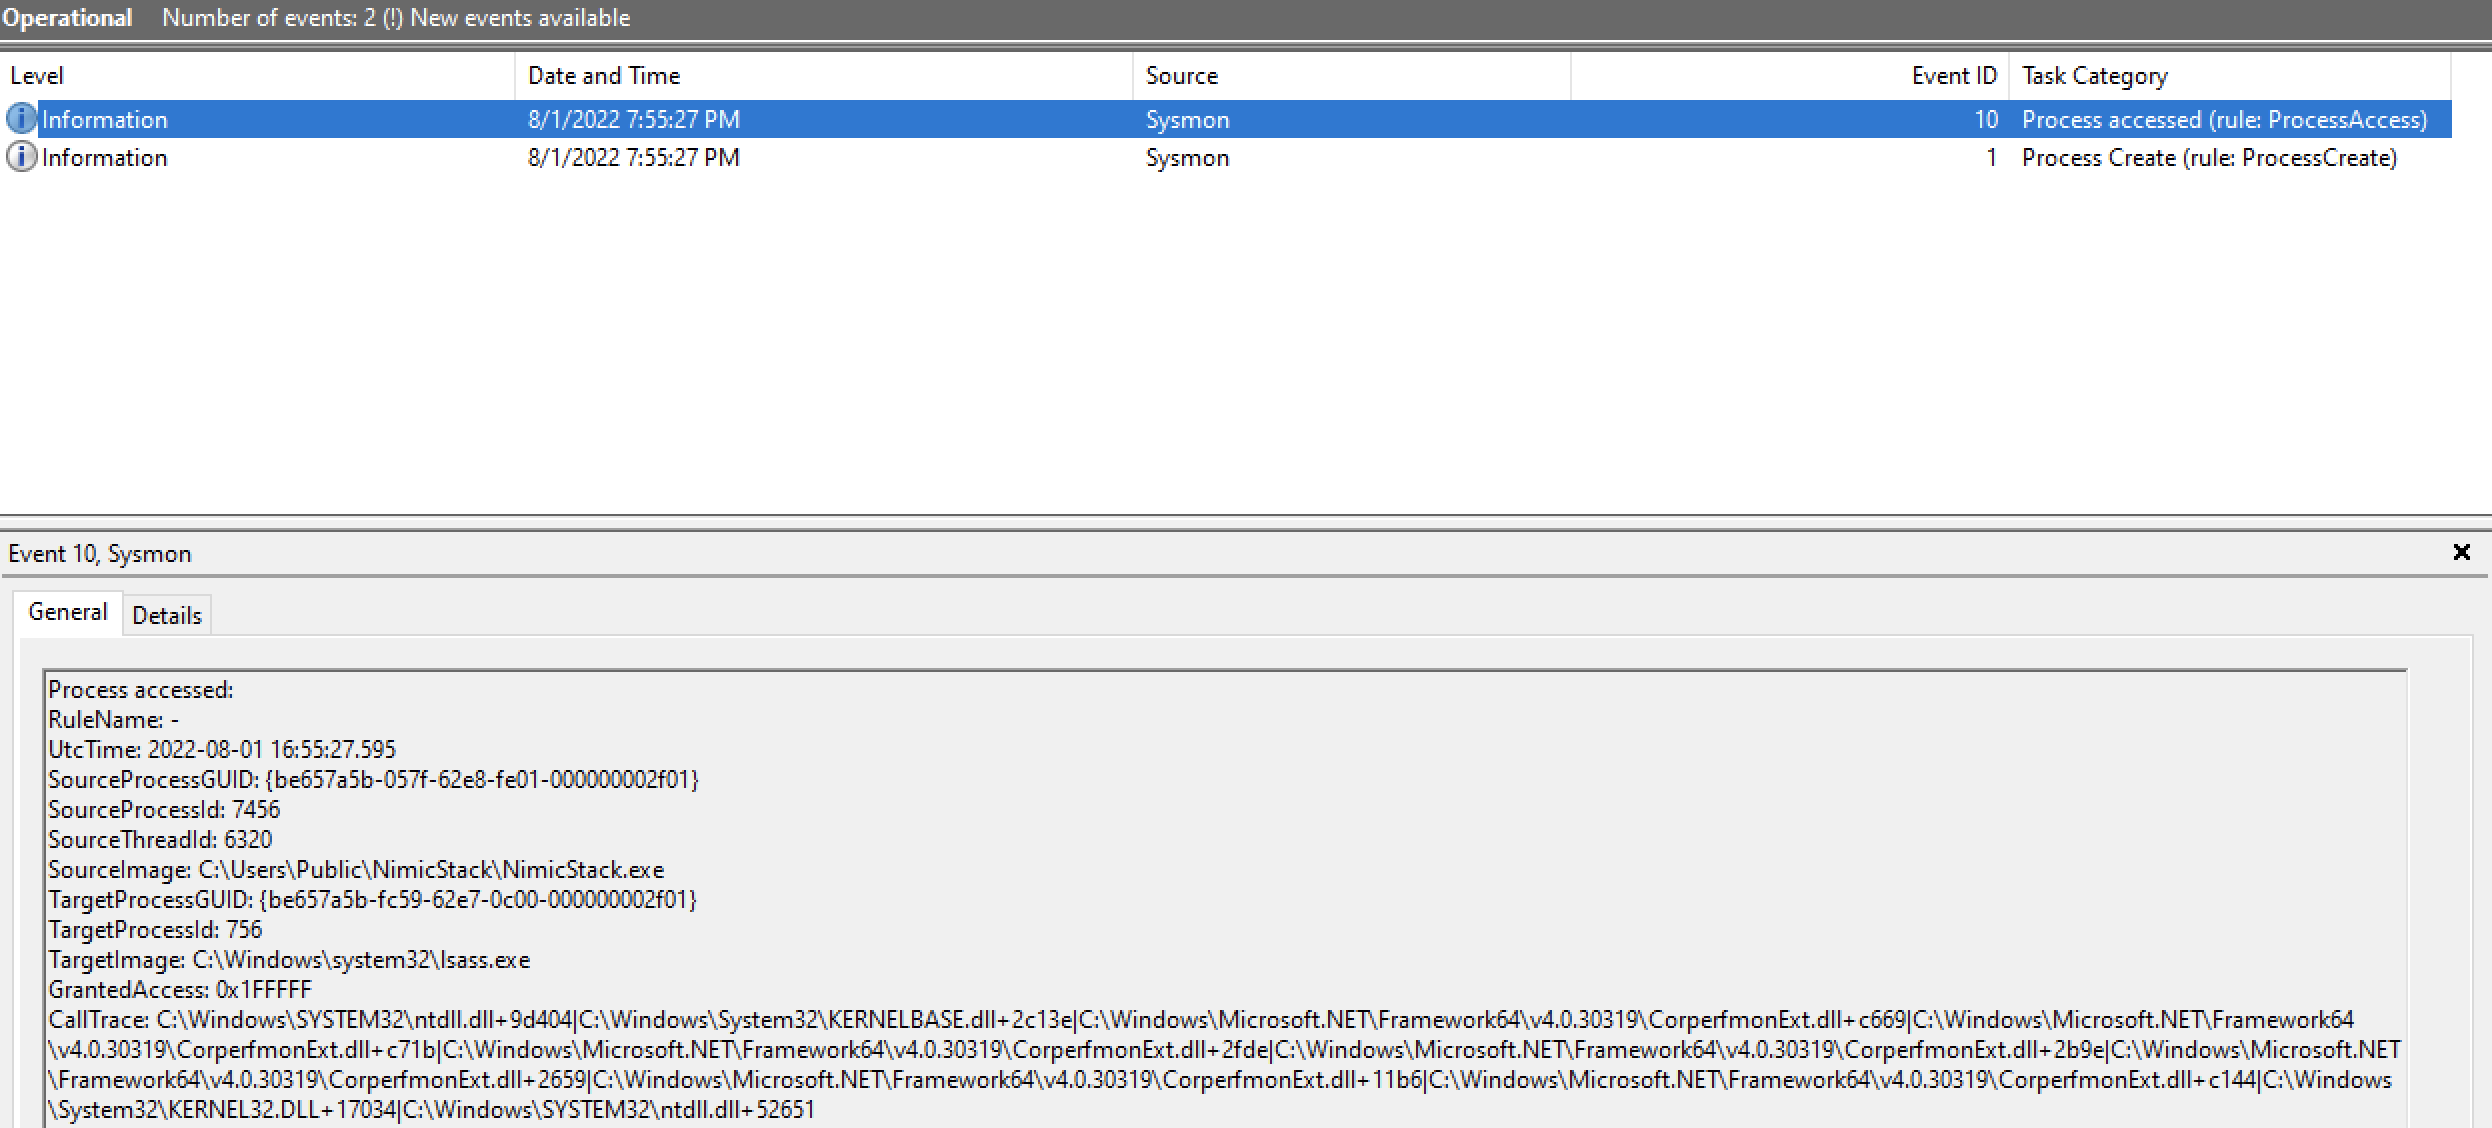 frkngksl/nimicstack
NimicStack is the pure Nim implementation of Call Stack Spoofing technique to mimic legitimate programs
 adityabhatt3010/cve-2025-54794-hijacking-claude-ai-with-a-prompt-injection-the-jailbreak-that-talked-back
A high-severity prompt injection flaw in Claude AI proves that even the smartest language models can be turned into weapons — all with a few lines of…