
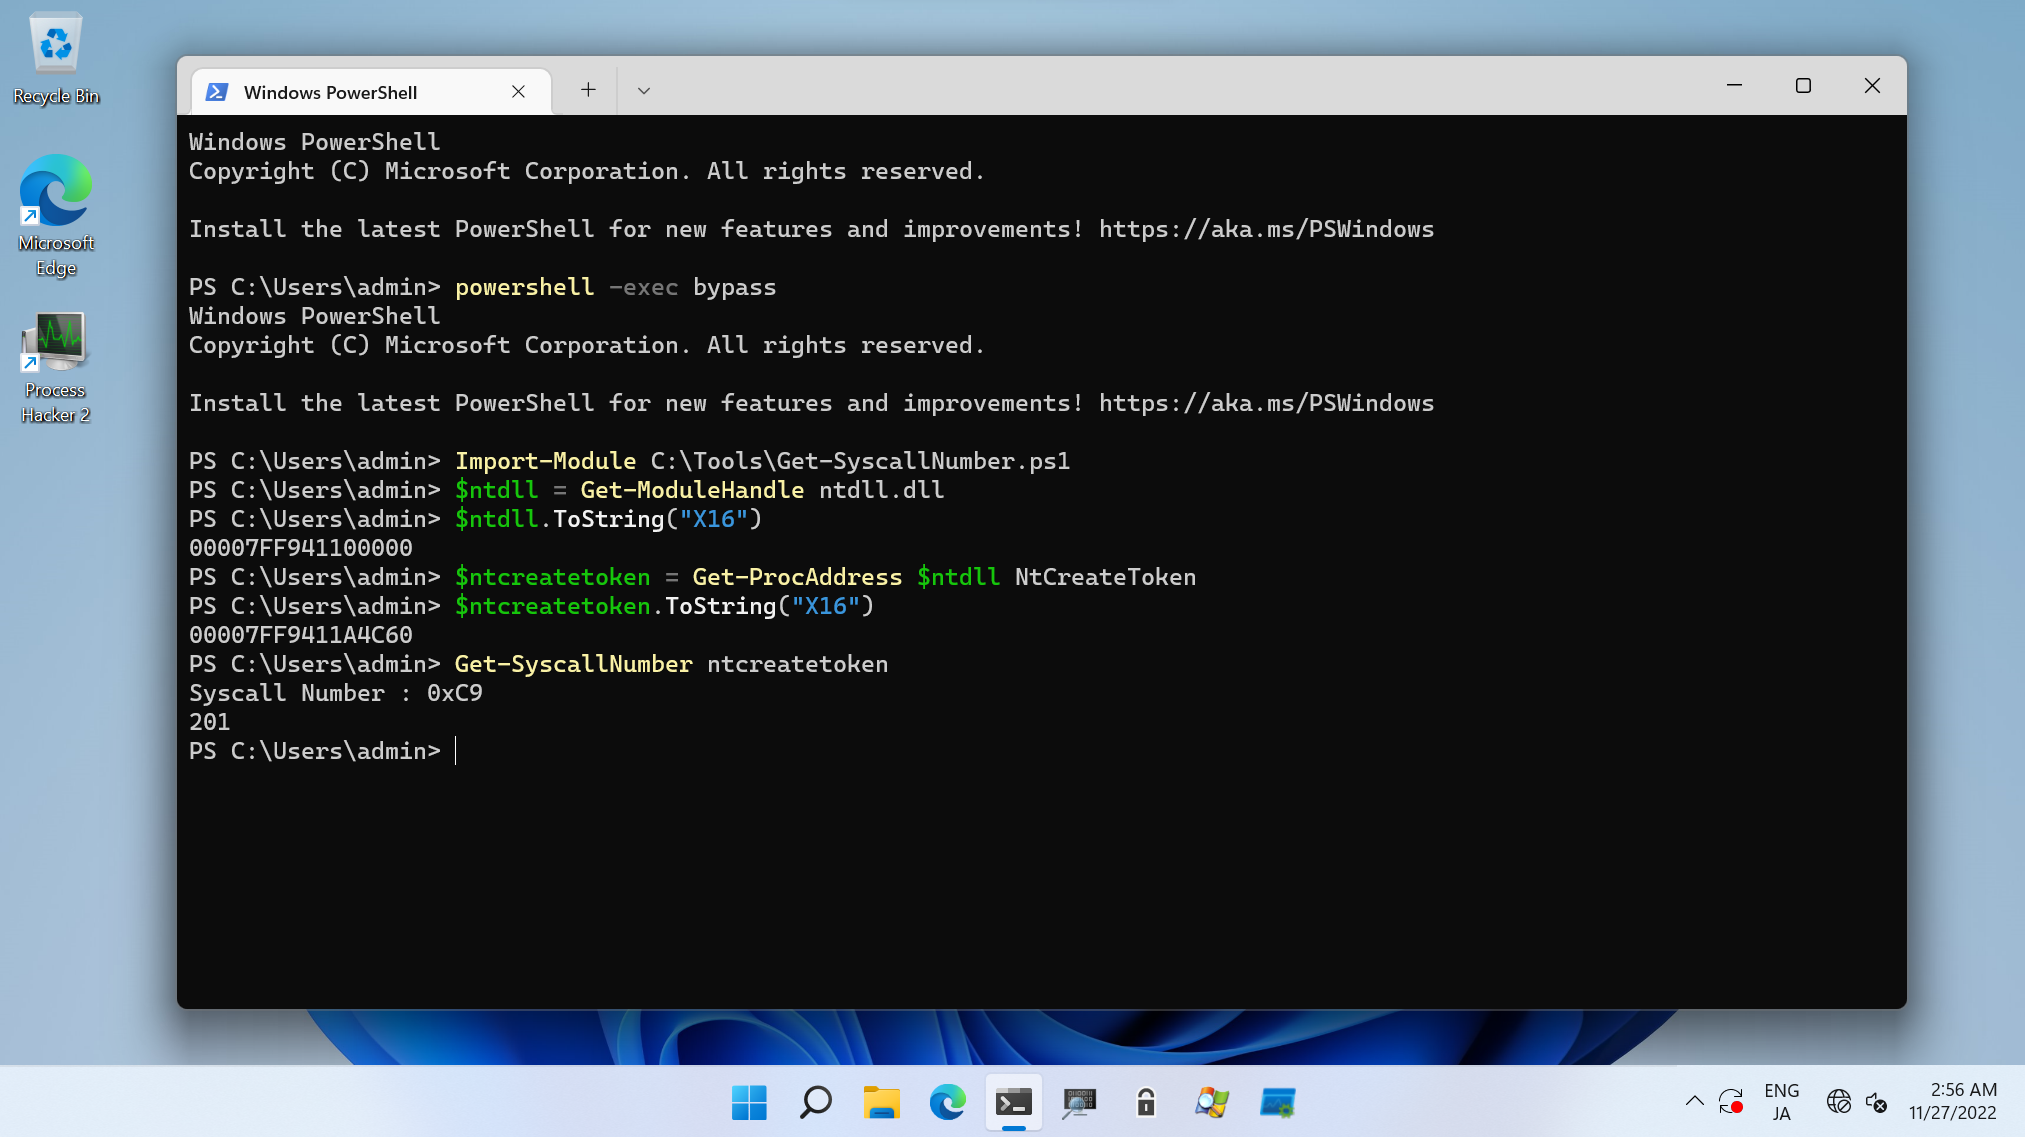
AtomicSyscall
 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
adversarial-attackbinary-analysiseducation+3
36410 months ago
daem0nc0re/atomicsyscallTools and PoCs for Windows syscall investigation.
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
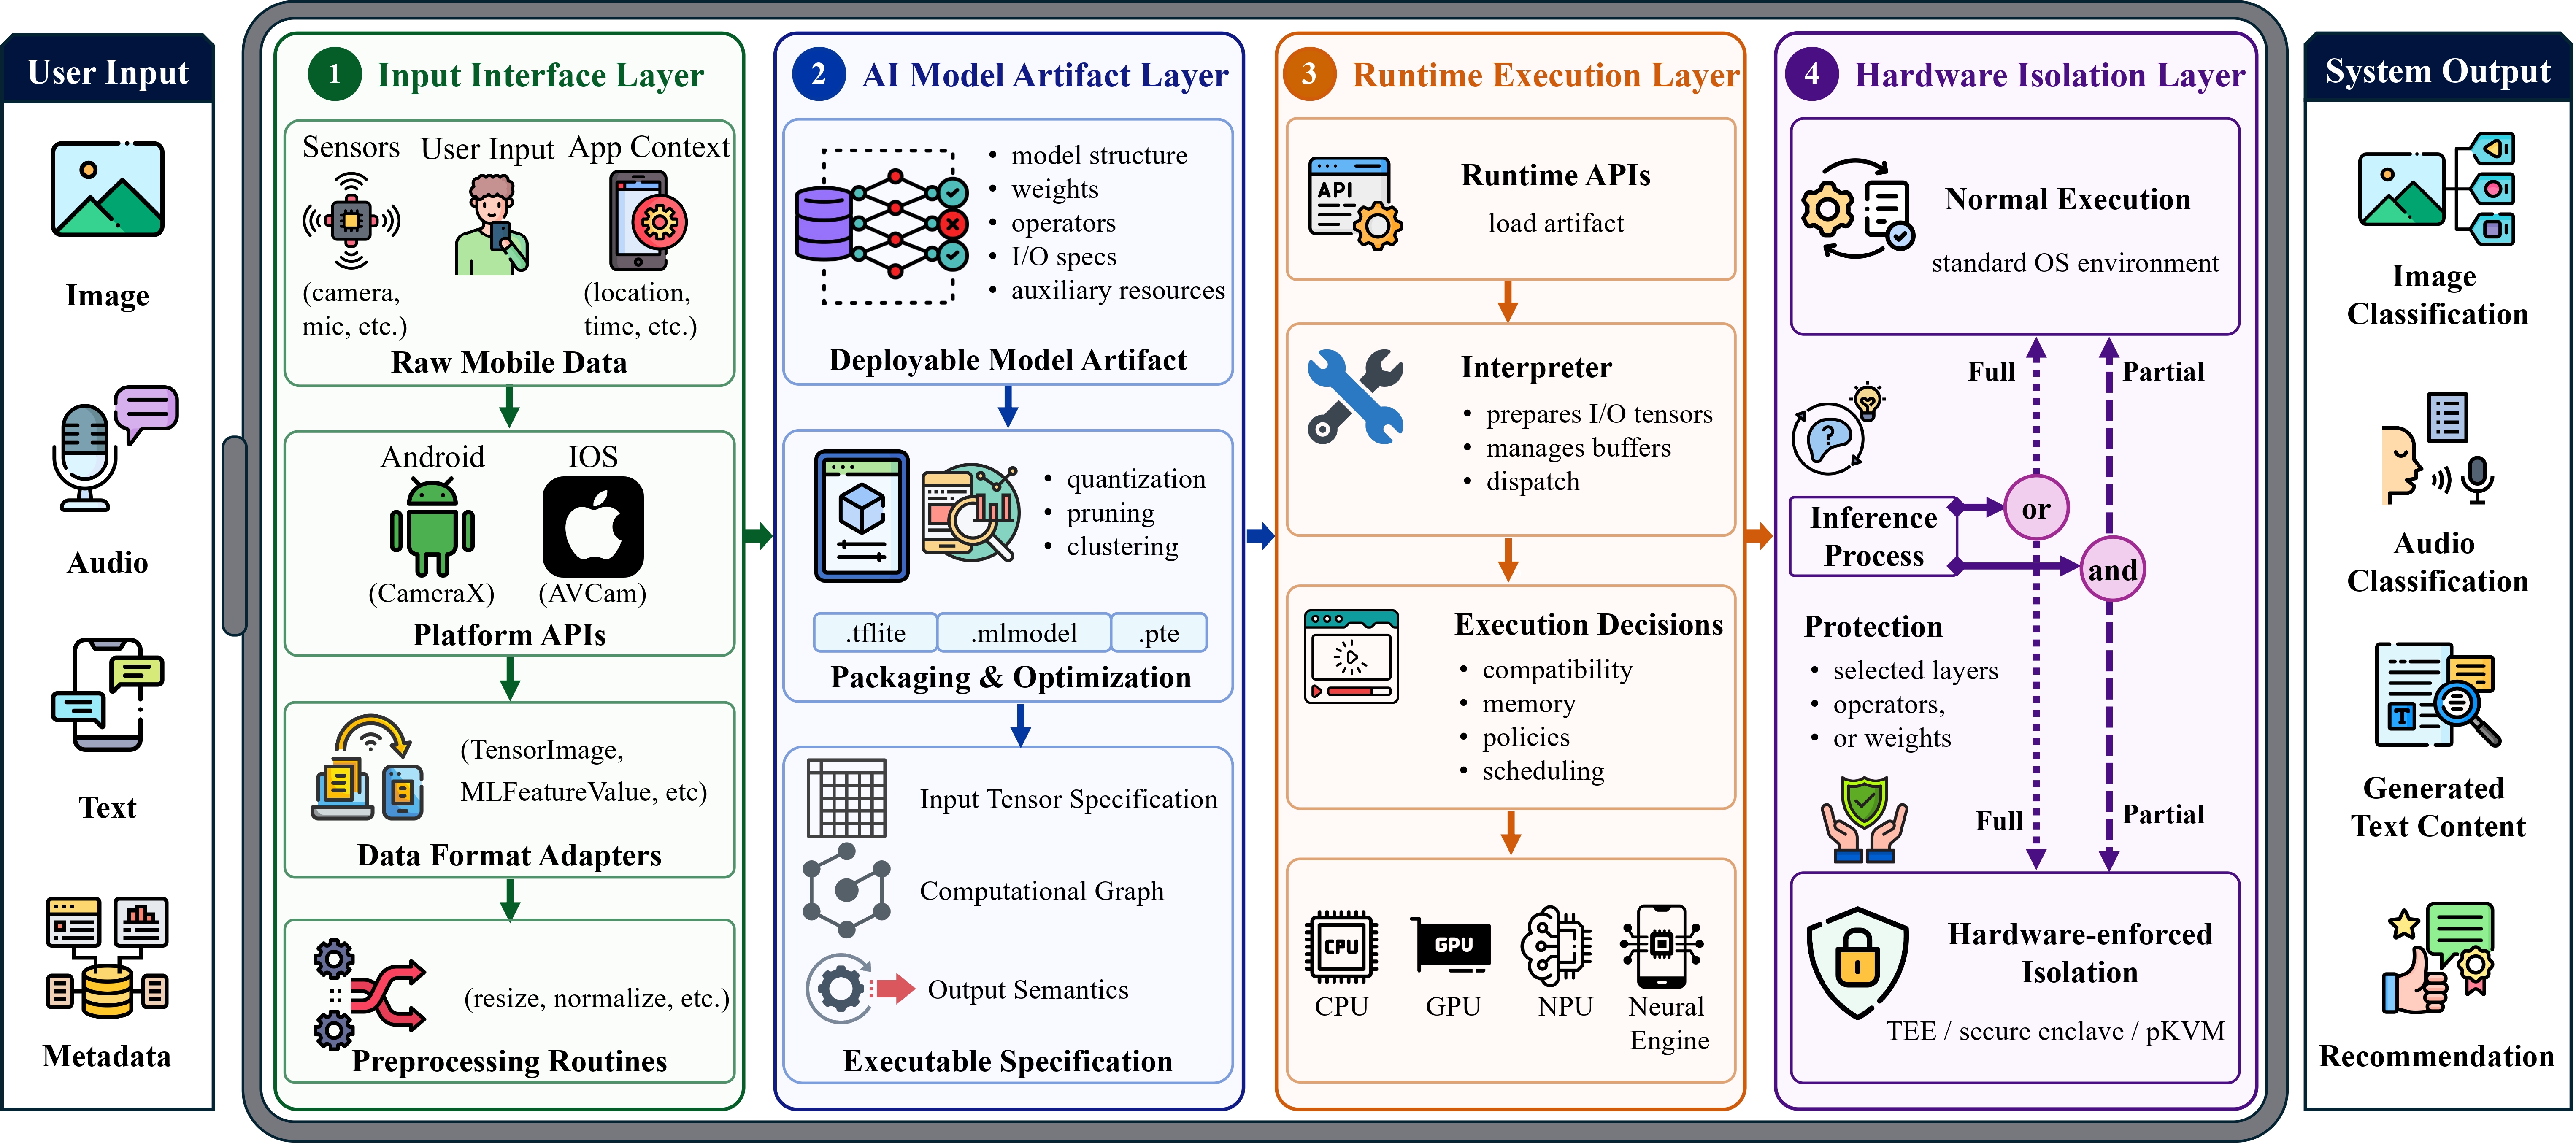 jinxhy/awesome-moai-security
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…
 aloshdenny/reverse-synthid
reverse engineering Gemini's SynthID detection
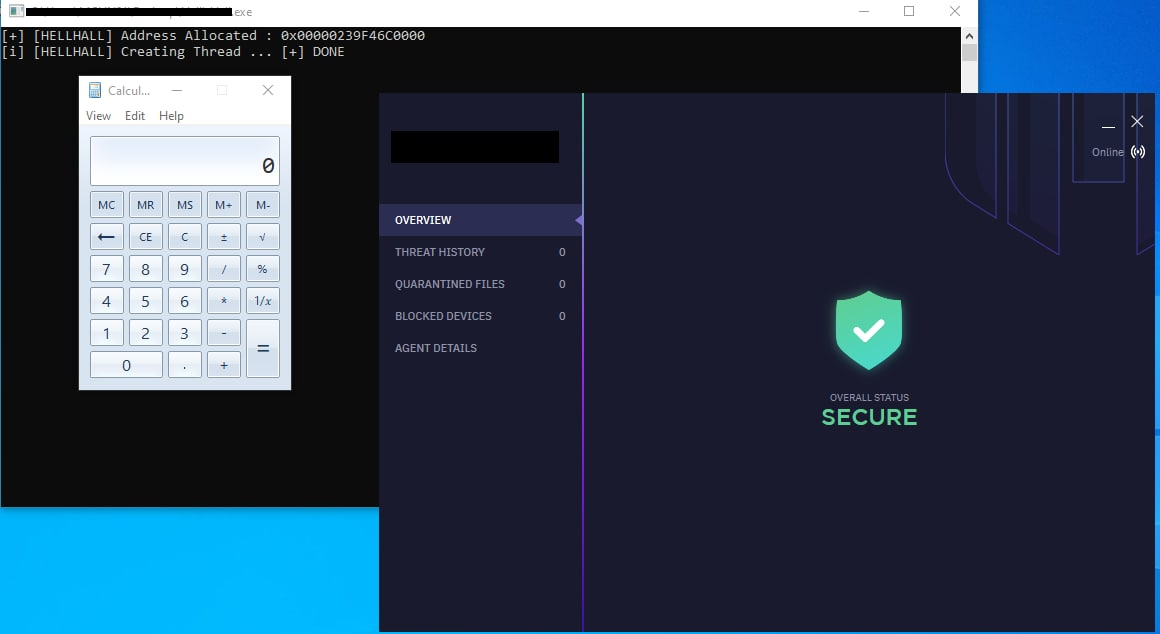 maldev-academy/hellhall
Performing Indirect Clean Syscalls
 aloshdenny/reverse-synthid-text
reverse engineering SynthID for text
 splx-ai/agentic-radar
A security scanner for your LLM agentic workflows
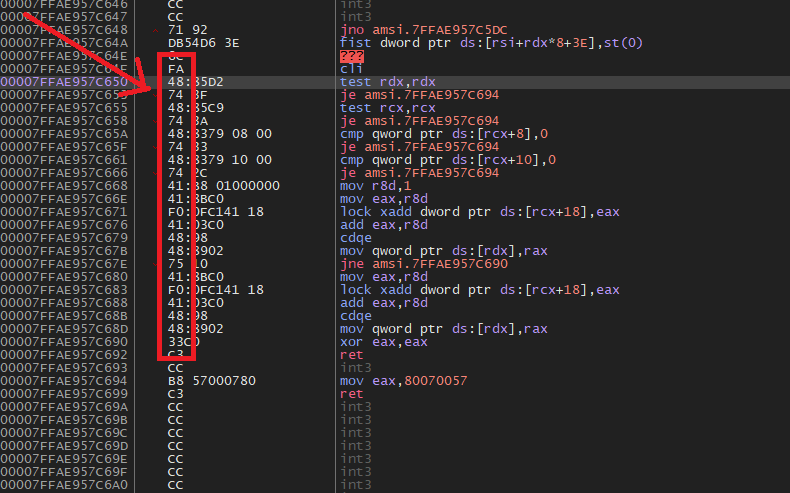 zeromemoryex/amsi-killer
Lifetime AMSI bypass
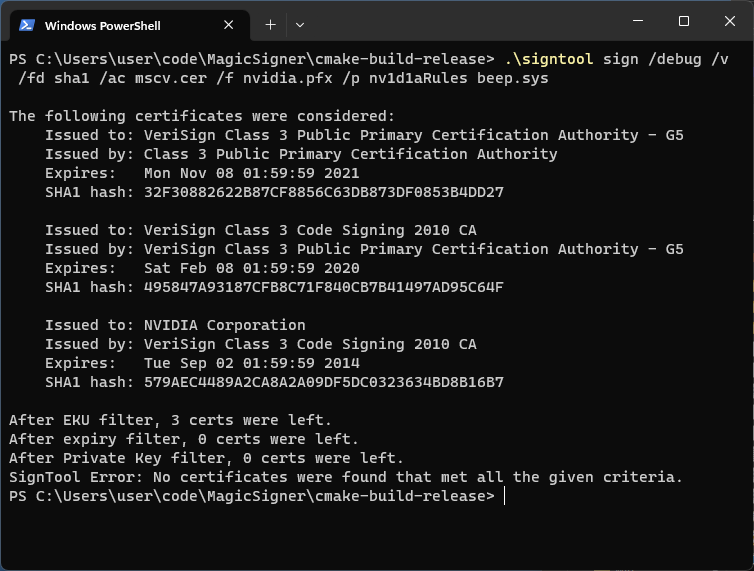 namazso/magicsigner
Signtool for expired certificates
 neomaster831/kurasagi
Windows 11 24H2-25H2 Runtime PatchGuard Bypass
 thebabush/llvm-jutsu
Anti-LLM obfuscation via finger counting
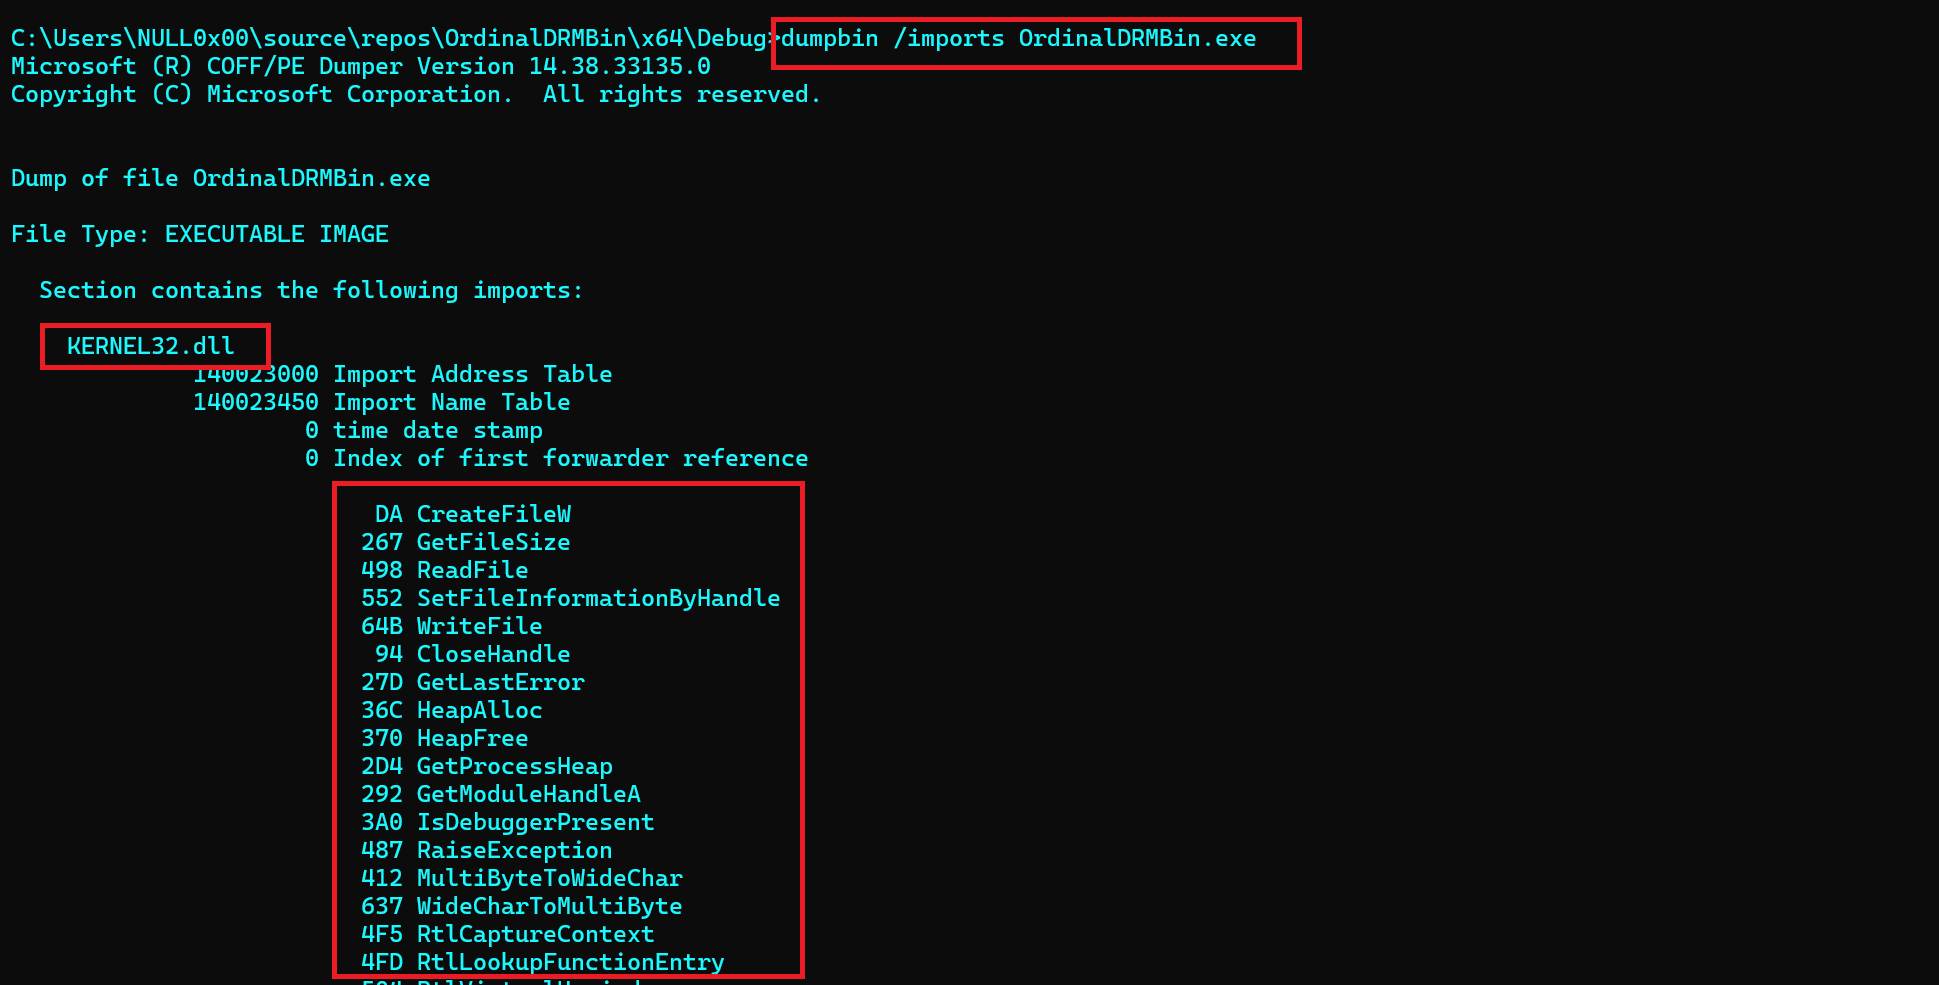 maldev-academy/drmbinviaordinalimports
Create Anti-Copy DRM Malware
 gmh5225/antidebug-antivm
Different methods to detect a virtualized environment or potential debugging