
xspawn
 cenobyte-vincit/xspawn
Spawns macOS programs through launchd's private XPC interface without execing them, making EDR record launchd as parent. Supports one-shot,…
adversarial-attackids-ips-evasionpersistence-mechanisms+2
cenobyte-vincit/xspawnSpawns macOS programs through launchd's private XPC interface without execing them, making EDR record launchd as parent. Supports one-shot,…
 george0papasotiriou/cve-2026-22003-redis-lua-sandbox-escape-via-debug.sethook-
Proof-of-concept exploit for CVE-2026-22003 demonstrating Redis Lua sandbox escape via debug.sethook to execute arbitrary system commands.
 ottosulin/awesome-ai-security
A collection of awesome resources related AI security
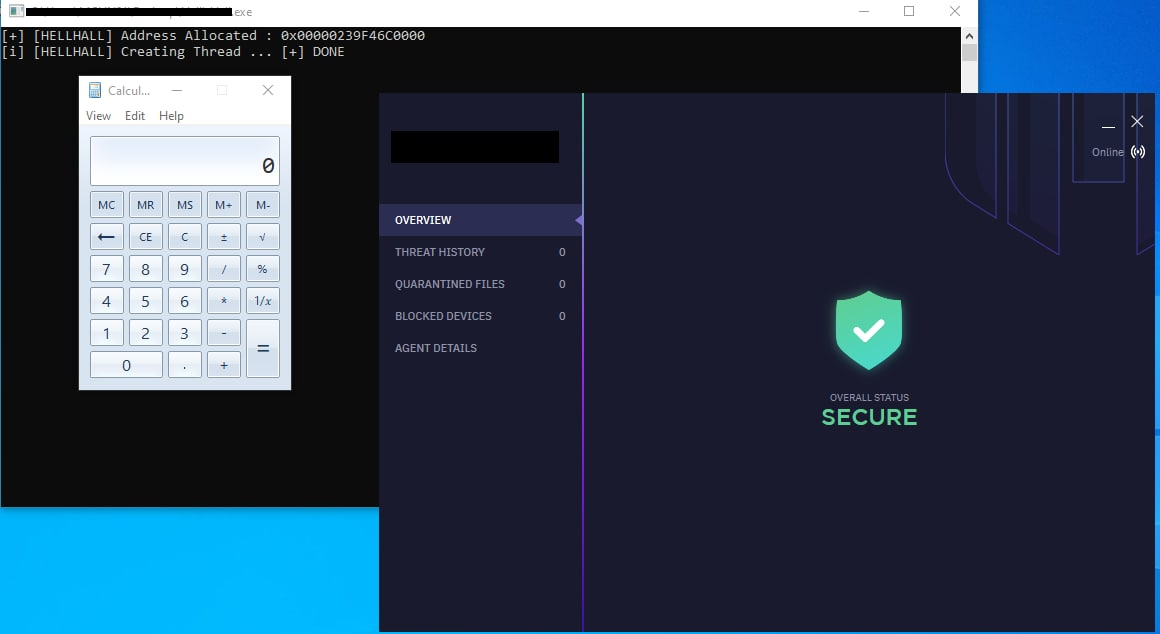 maldev-academy/hellhall
Performing Indirect Clean Syscalls
 helviojunior/hookchain
HookChain: A new perspective for Bypassing EDR Solutions
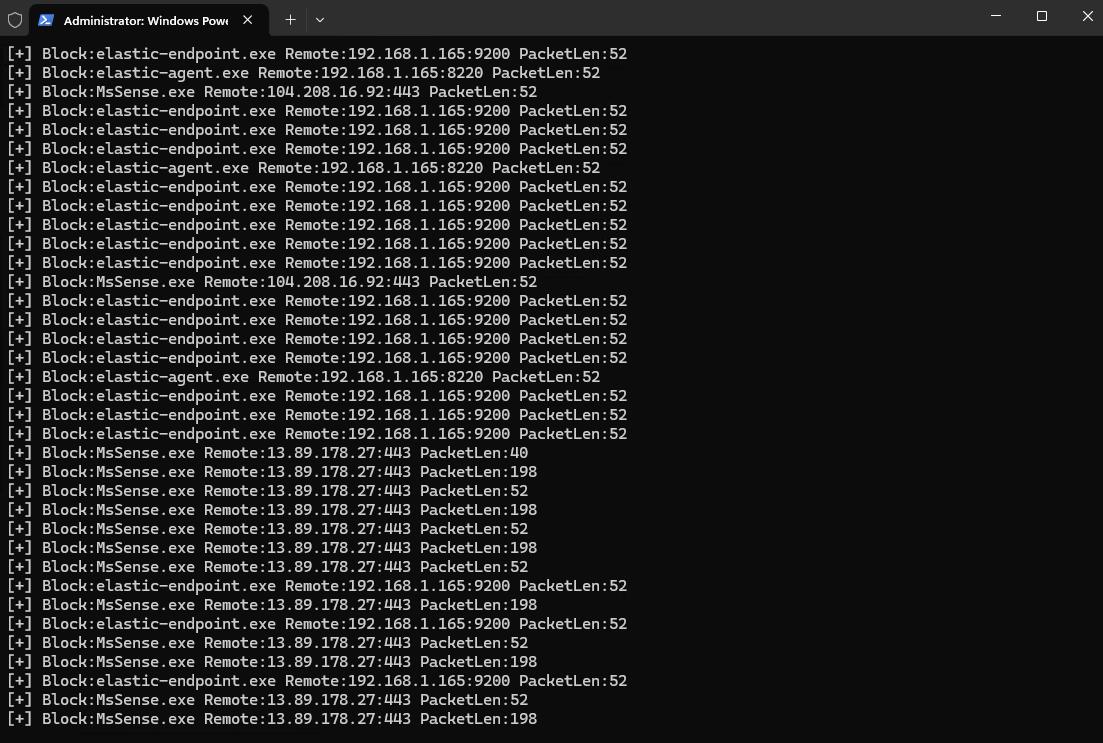 senzee1984/edrprison
Leverage a legitimate WFP callout driver to prevent EDR agents from sending telemetry
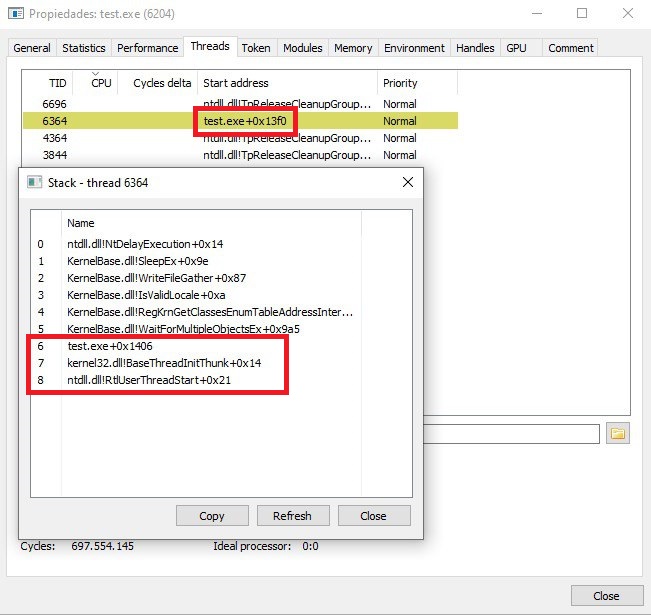 kudaes/unwinder
Call stack spoofing for Rust
 rsmudge/unhook-bof
Remove API hooks from a Beacon process.
 george0papasotiriou/cve-2026-22020-weak-seed-in-quantum-key-distribution-error-correction
Python PoC demonstrating CVE-2026-22020: exploitable weak seed in quantum key distribution privacy amplification, reducing final key entropy.
 es3n1n/no-defender
A slightly more fun way to disable windows defender + firewall. (through the WSC api)
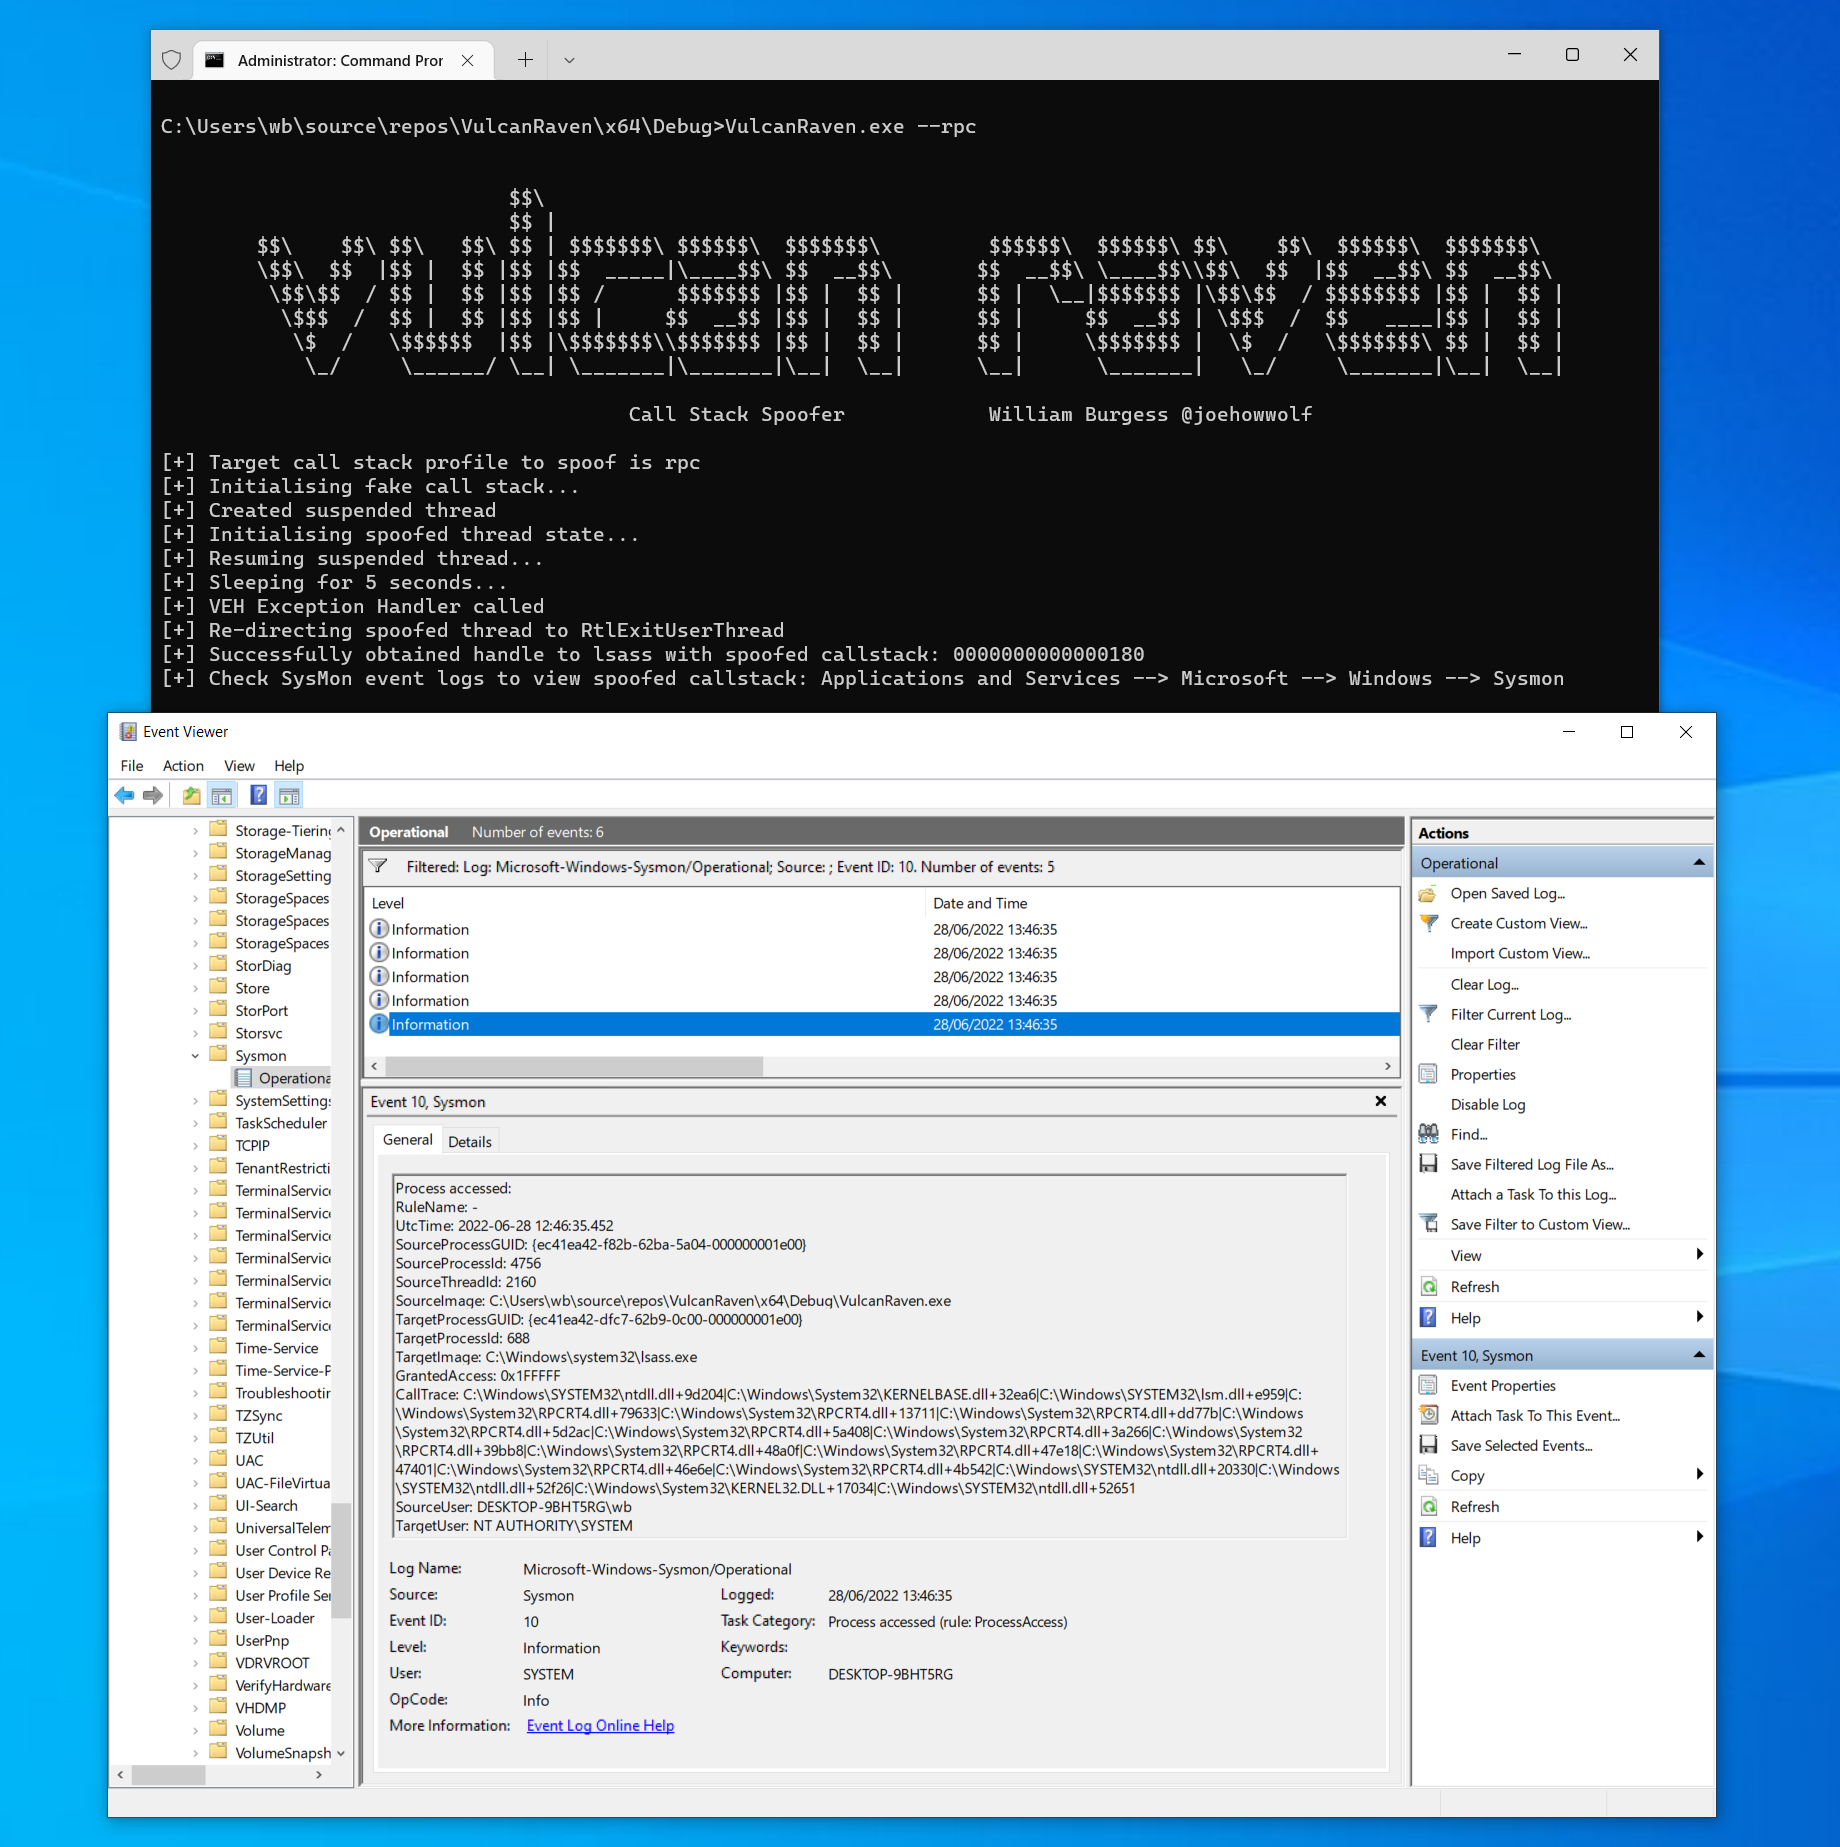 withsecurelabs/callstackspoofer
A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
 gmh5225/callmewin32kdriver
Load your driver like win32k.sys
 dis0rder0x00/obex
Obex – Blocking unwanted DLLs in user mode
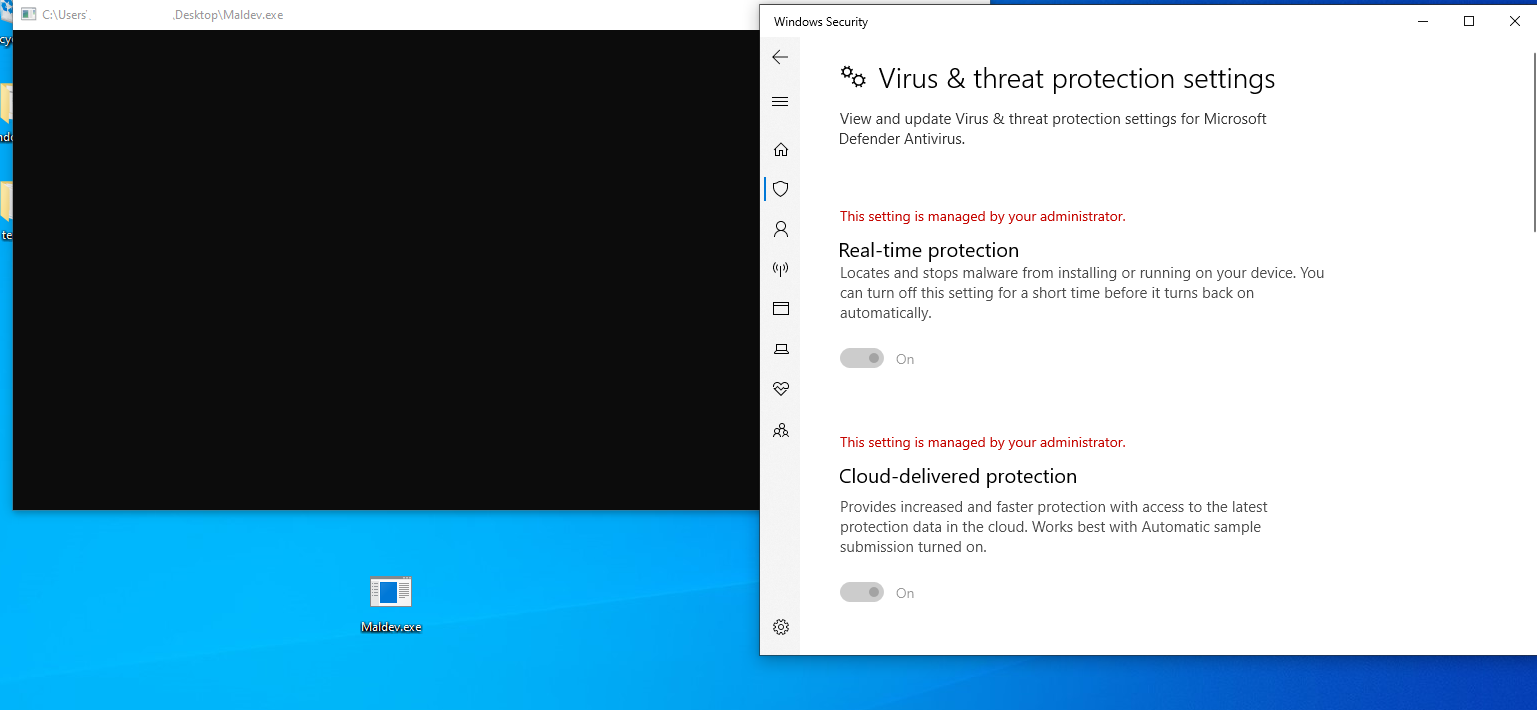 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
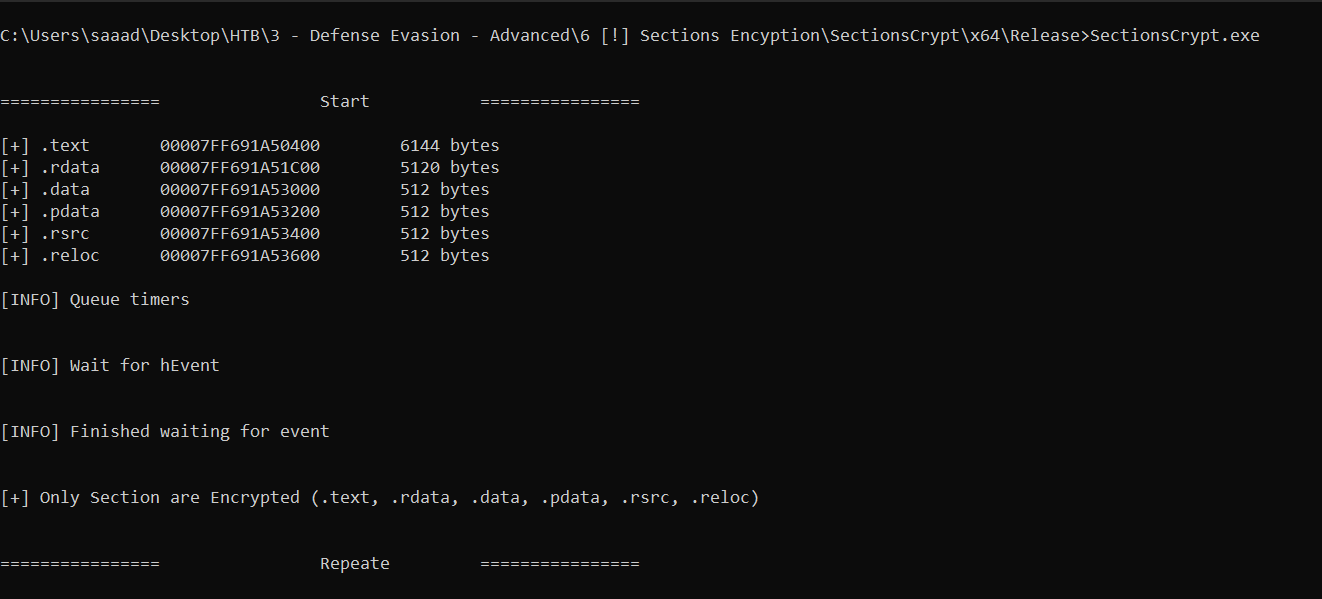 saadahla/d1rksleep
Improved version of EKKO by @5pider that Encrypts only Image Sections
 nul0x4c/etwsessionhijacking
A Poc on blocking Procmon from monitoring network events
 rasta-mouse/libtp
Crystal Palace library for proxying Nt API calls via the Threadpool