

CallMeWin32kDriver
 gmh5225/callmewin32kdriver
Load your driver like win32k.sys
adversarial-attackids-ips-evasionpost-exploitation+1
2584 years ago
gmh5225/callmewin32kdriverLoad your driver like win32k.sys
 xforcered/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 dis0rder0x00/obex
Obex – Blocking unwanted DLLs in user mode
 kudaes/split
Apply a divide and conquer approach to bypass EDRs
 mr-un1k0d3r/amsi-etw-patch
Patch AMSI and ETW
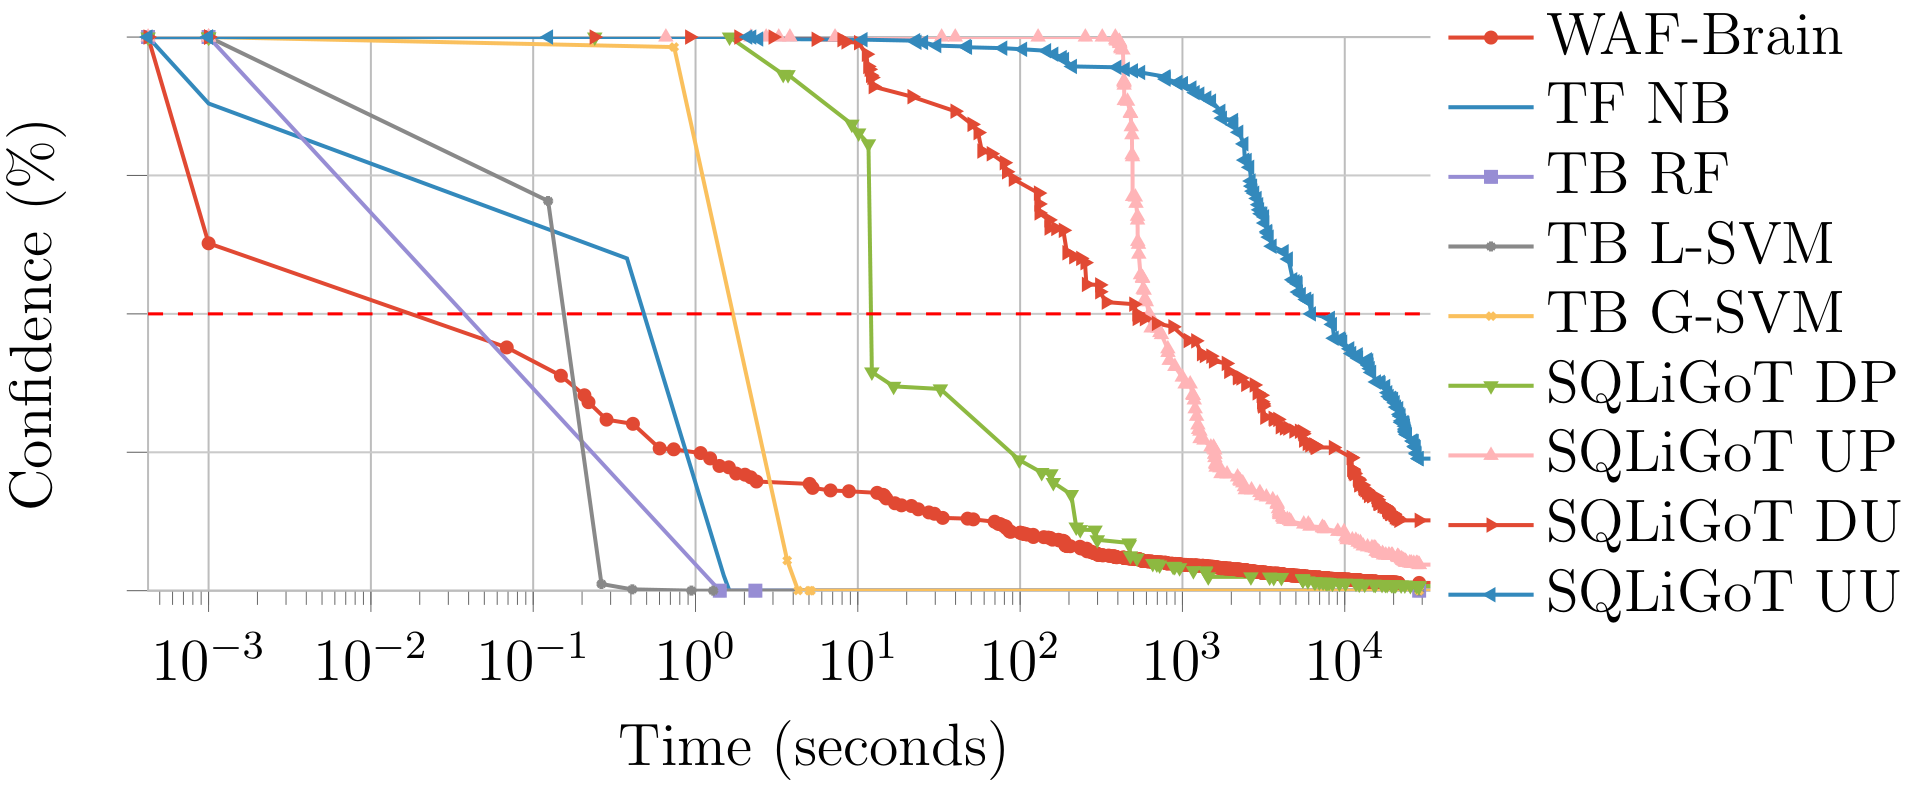 avalz/waf-a-mole
A guided mutation-based fuzzer for ML-based Web Application Firewalls
 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 nul0x4c/etwsessionhijacking
A Poc on blocking Procmon from monitoring network events

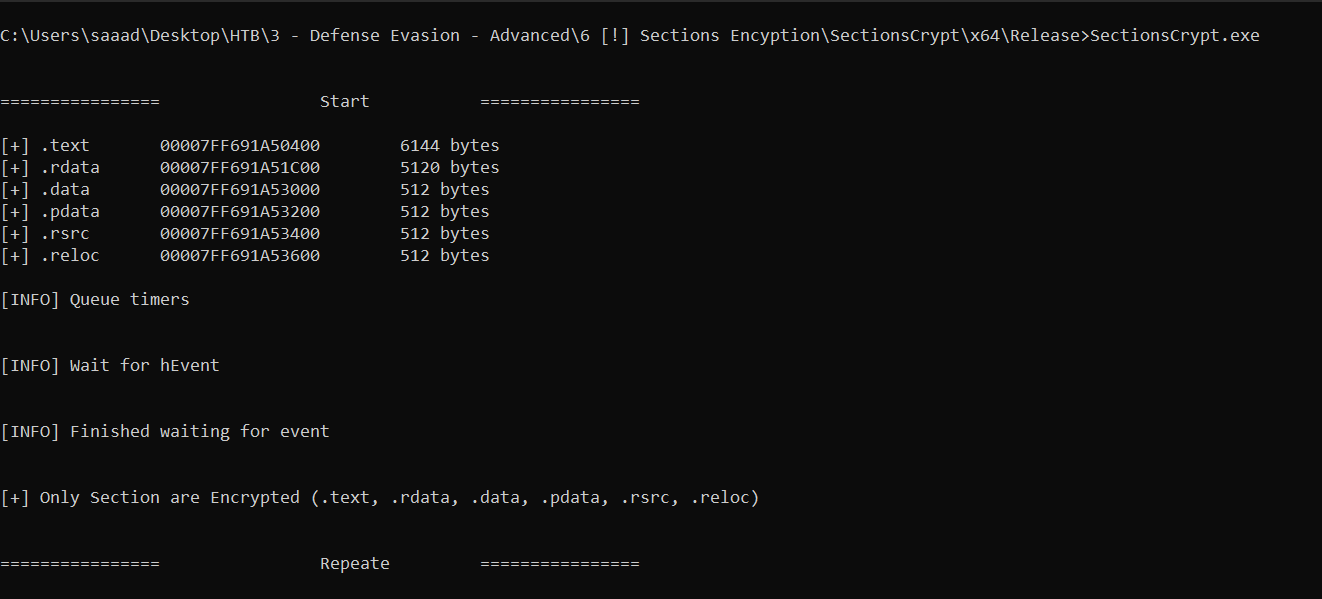 saadahla/d1rksleep
Improved version of EKKO by @5pider that Encrypts only Image Sections
 unkvolism/fuck-etw
Bypass the Event Trace Windows(ETW) and unhook ntdll.
 rasta-mouse/libtp
Crystal Palace library for proxying Nt API calls via the Threadpool
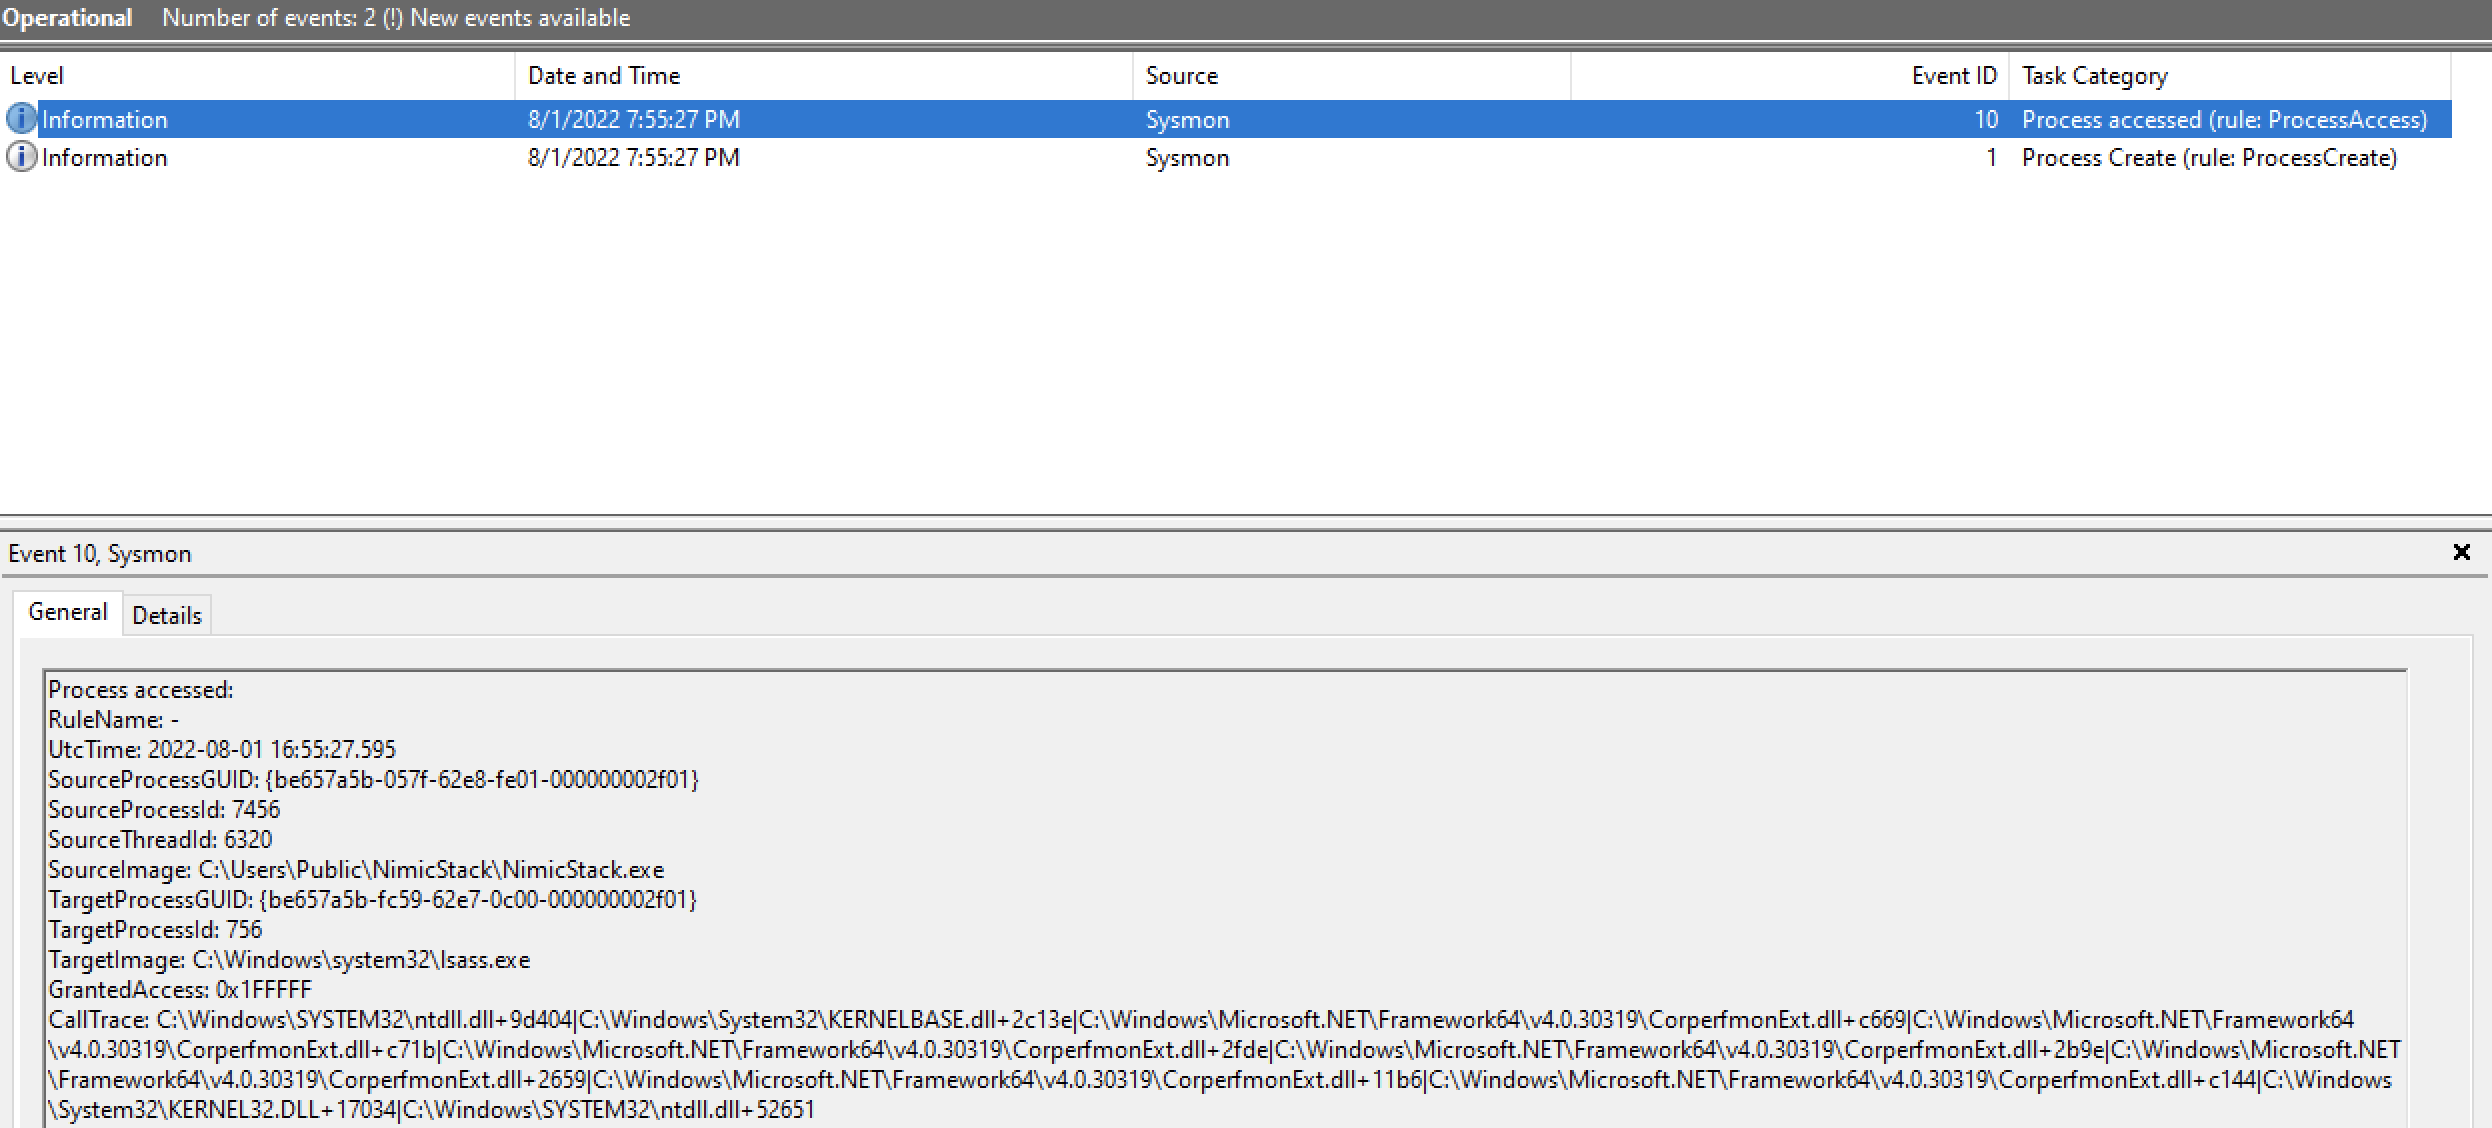 frkngksl/nimicstack
NimicStack is the pure Nim implementation of Call Stack Spoofing technique to mimic legitimate programs
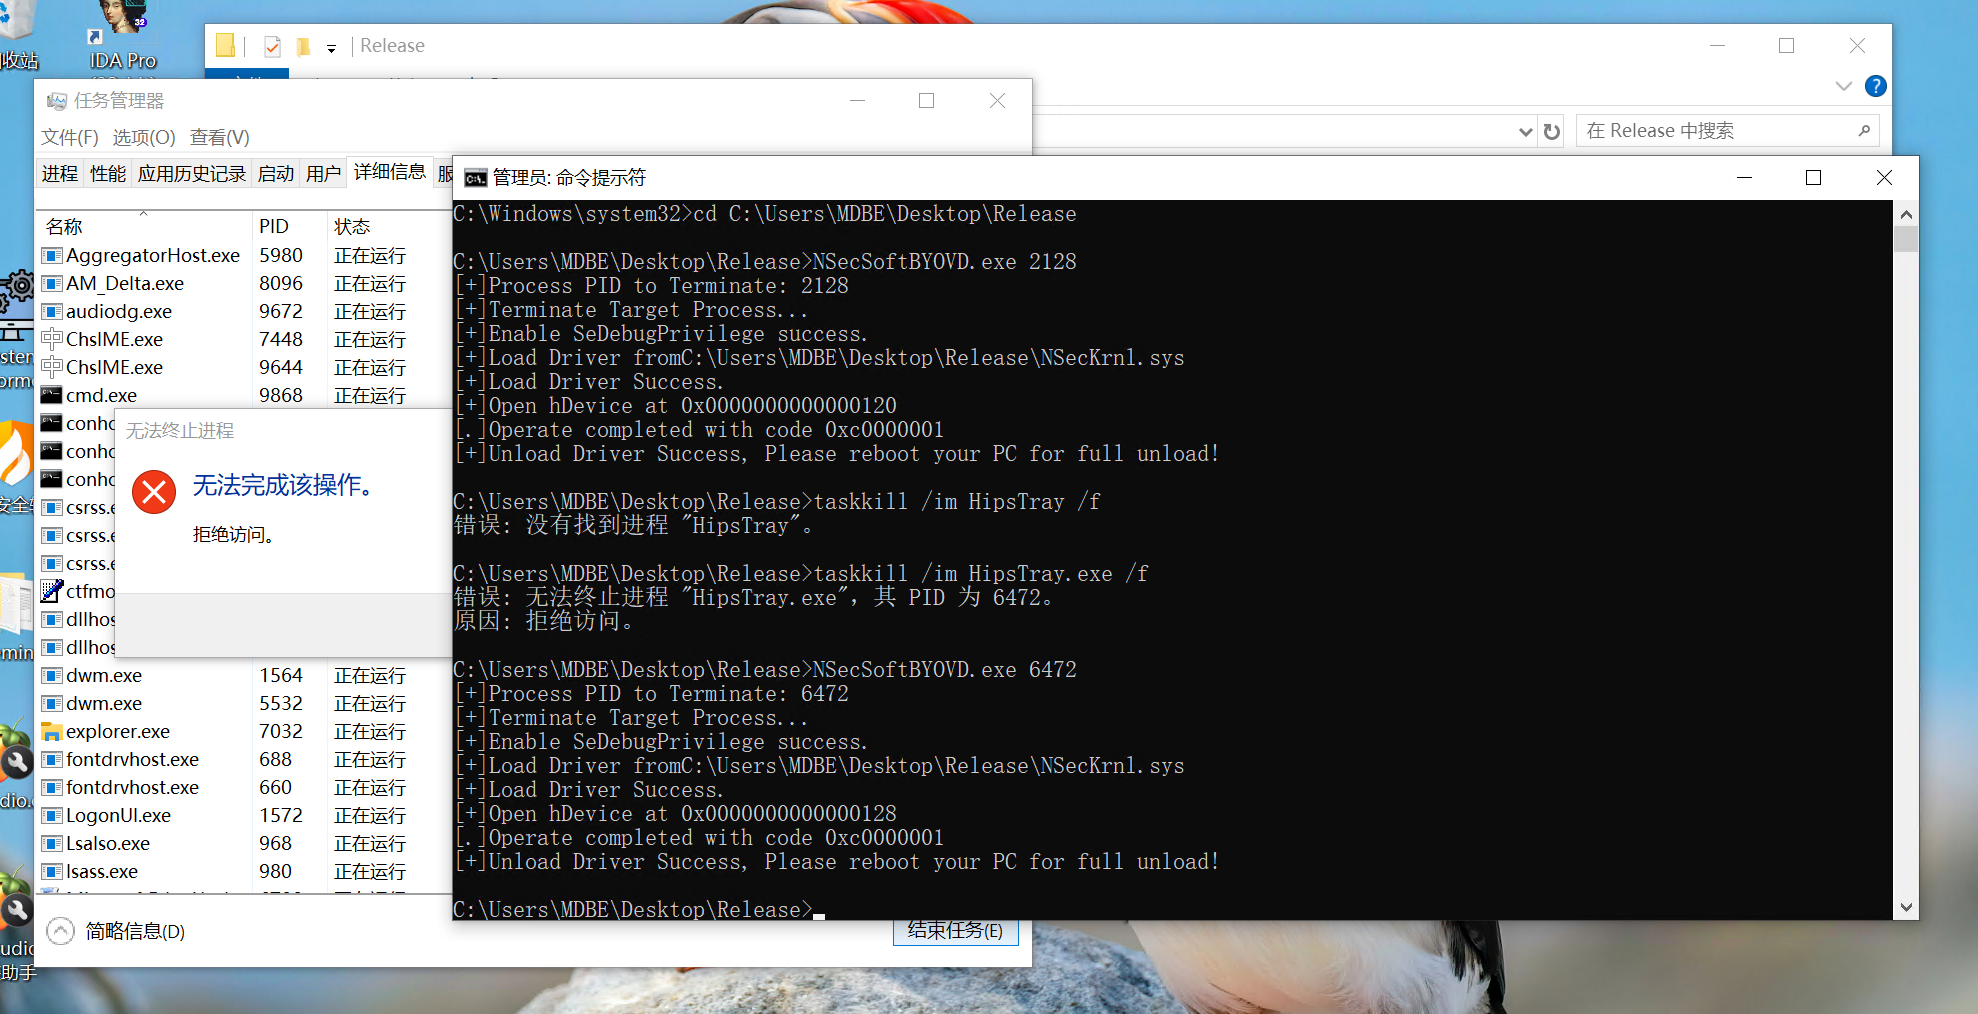
 didierstevens/falsepositives
Tools that trigger False Positive AV alerts
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver