
DutchOven
 loosehose/dutchoven
Application-scoped Windows network brownouts in native C and BOF form
adversarial-attackchaos-engineeringnetwork-security+2
231 month ago
loosehose/dutchovenApplication-scoped Windows network brownouts in native C and BOF form
 cenobyte-vincit/xspawn
Spawns macOS programs through launchd's private XPC interface without execing them, making EDR record launchd as parent. Supports one-shot,…
 maldev-academy/hellhall
Performing Indirect Clean Syscalls
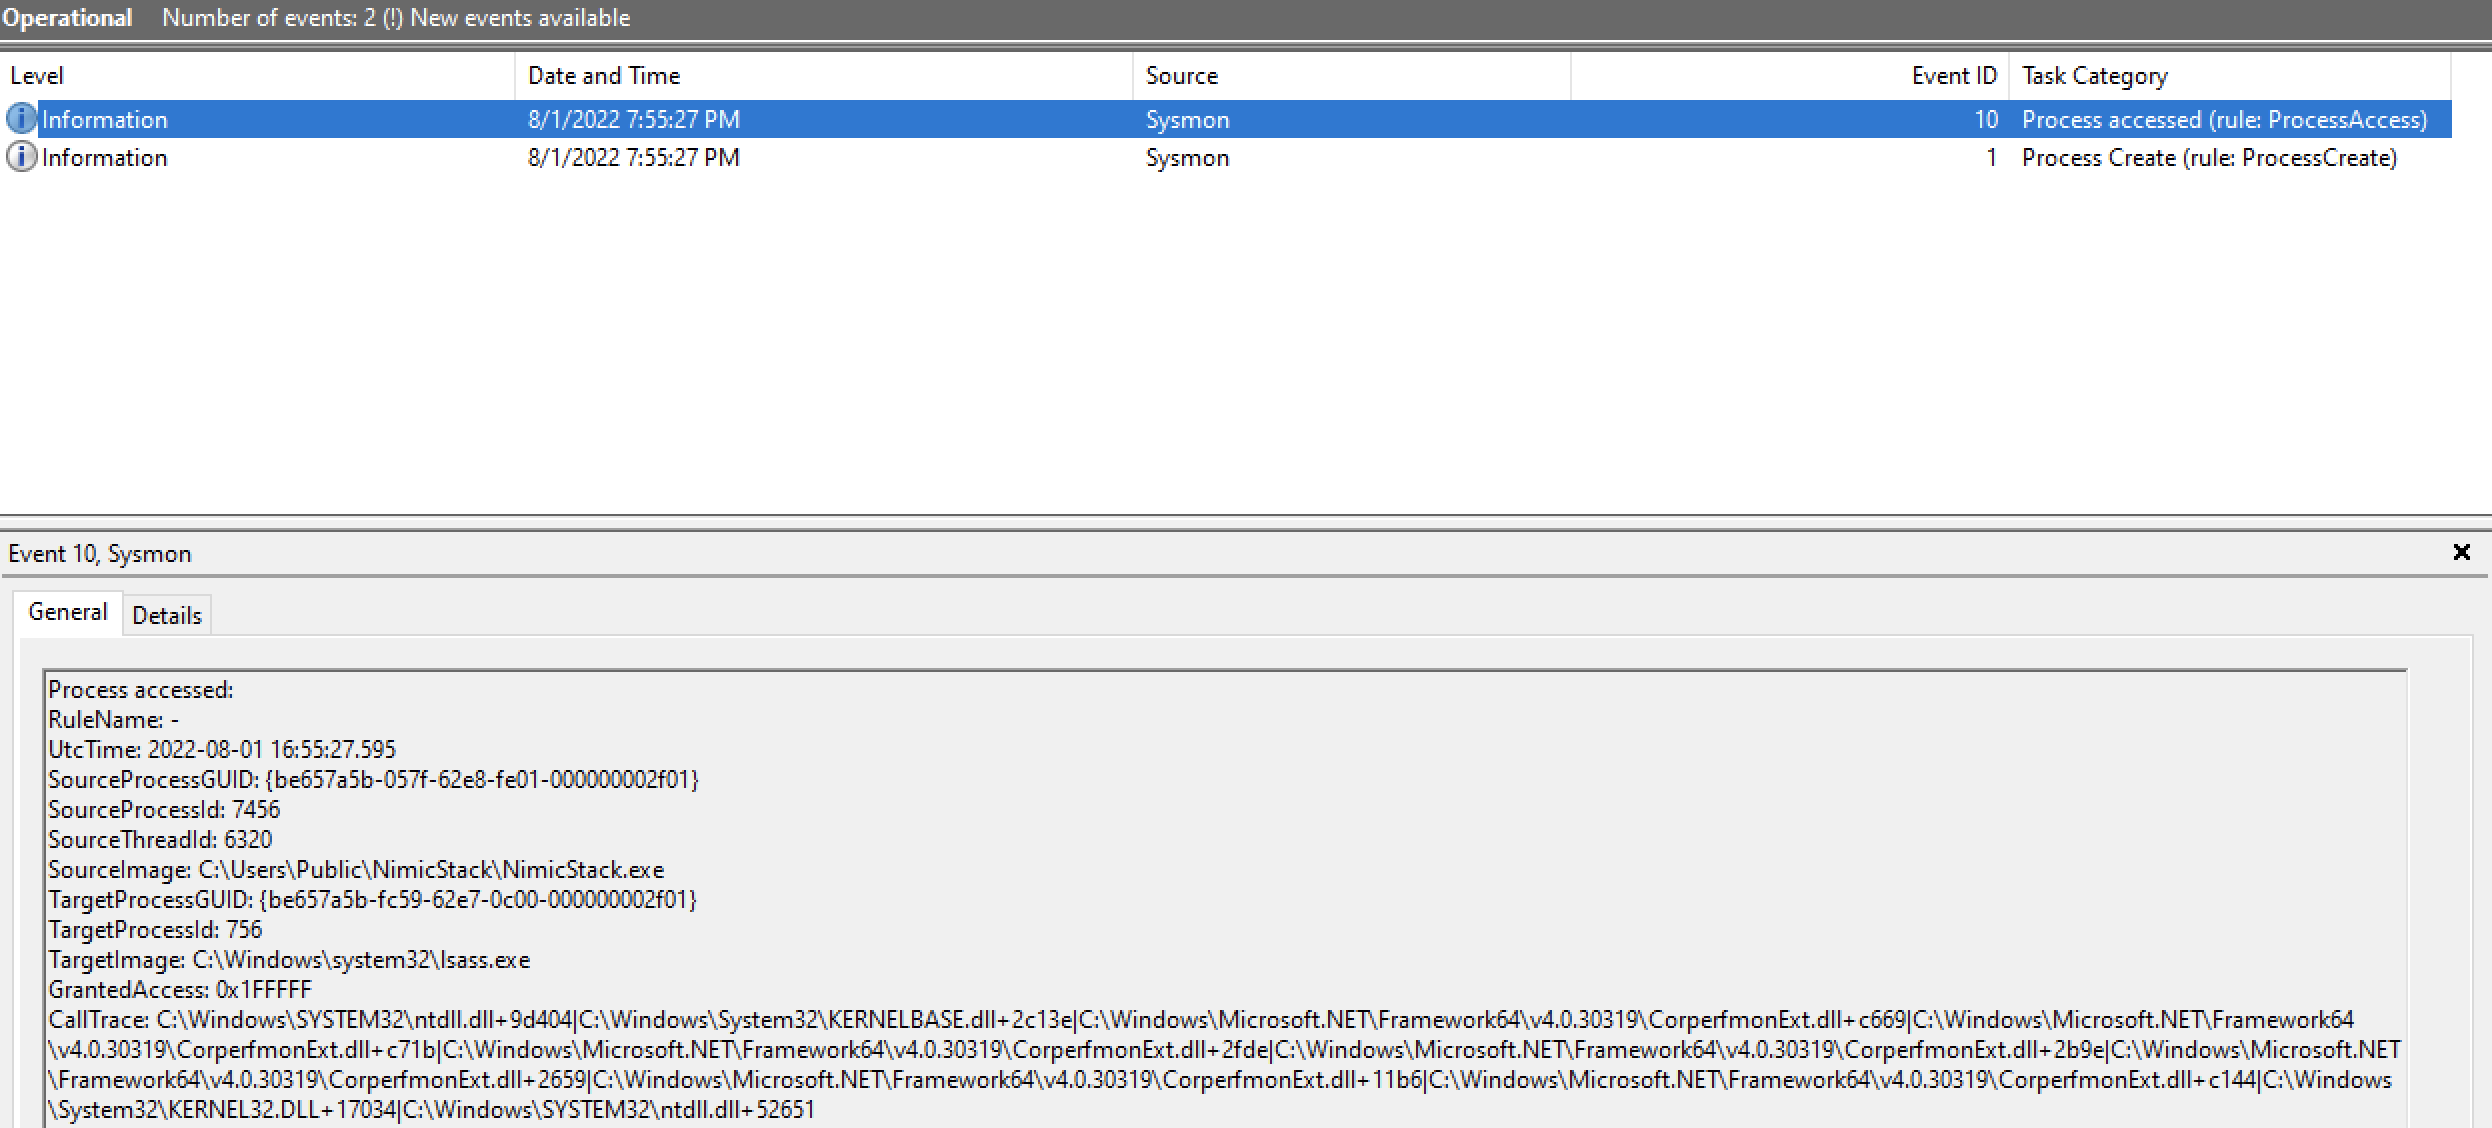 frkngksl/nimicstack
NimicStack is the pure Nim implementation of Call Stack Spoofing technique to mimic legitimate programs
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.
 rasta-mouse/libtp
Crystal Palace library for proxying Nt API calls via the Threadpool
 dis0rder0x00/obex
Obex – Blocking unwanted DLLs in user mode
 nul0x4c/etwsessionhijacking
A Poc on blocking Procmon from monitoring network events
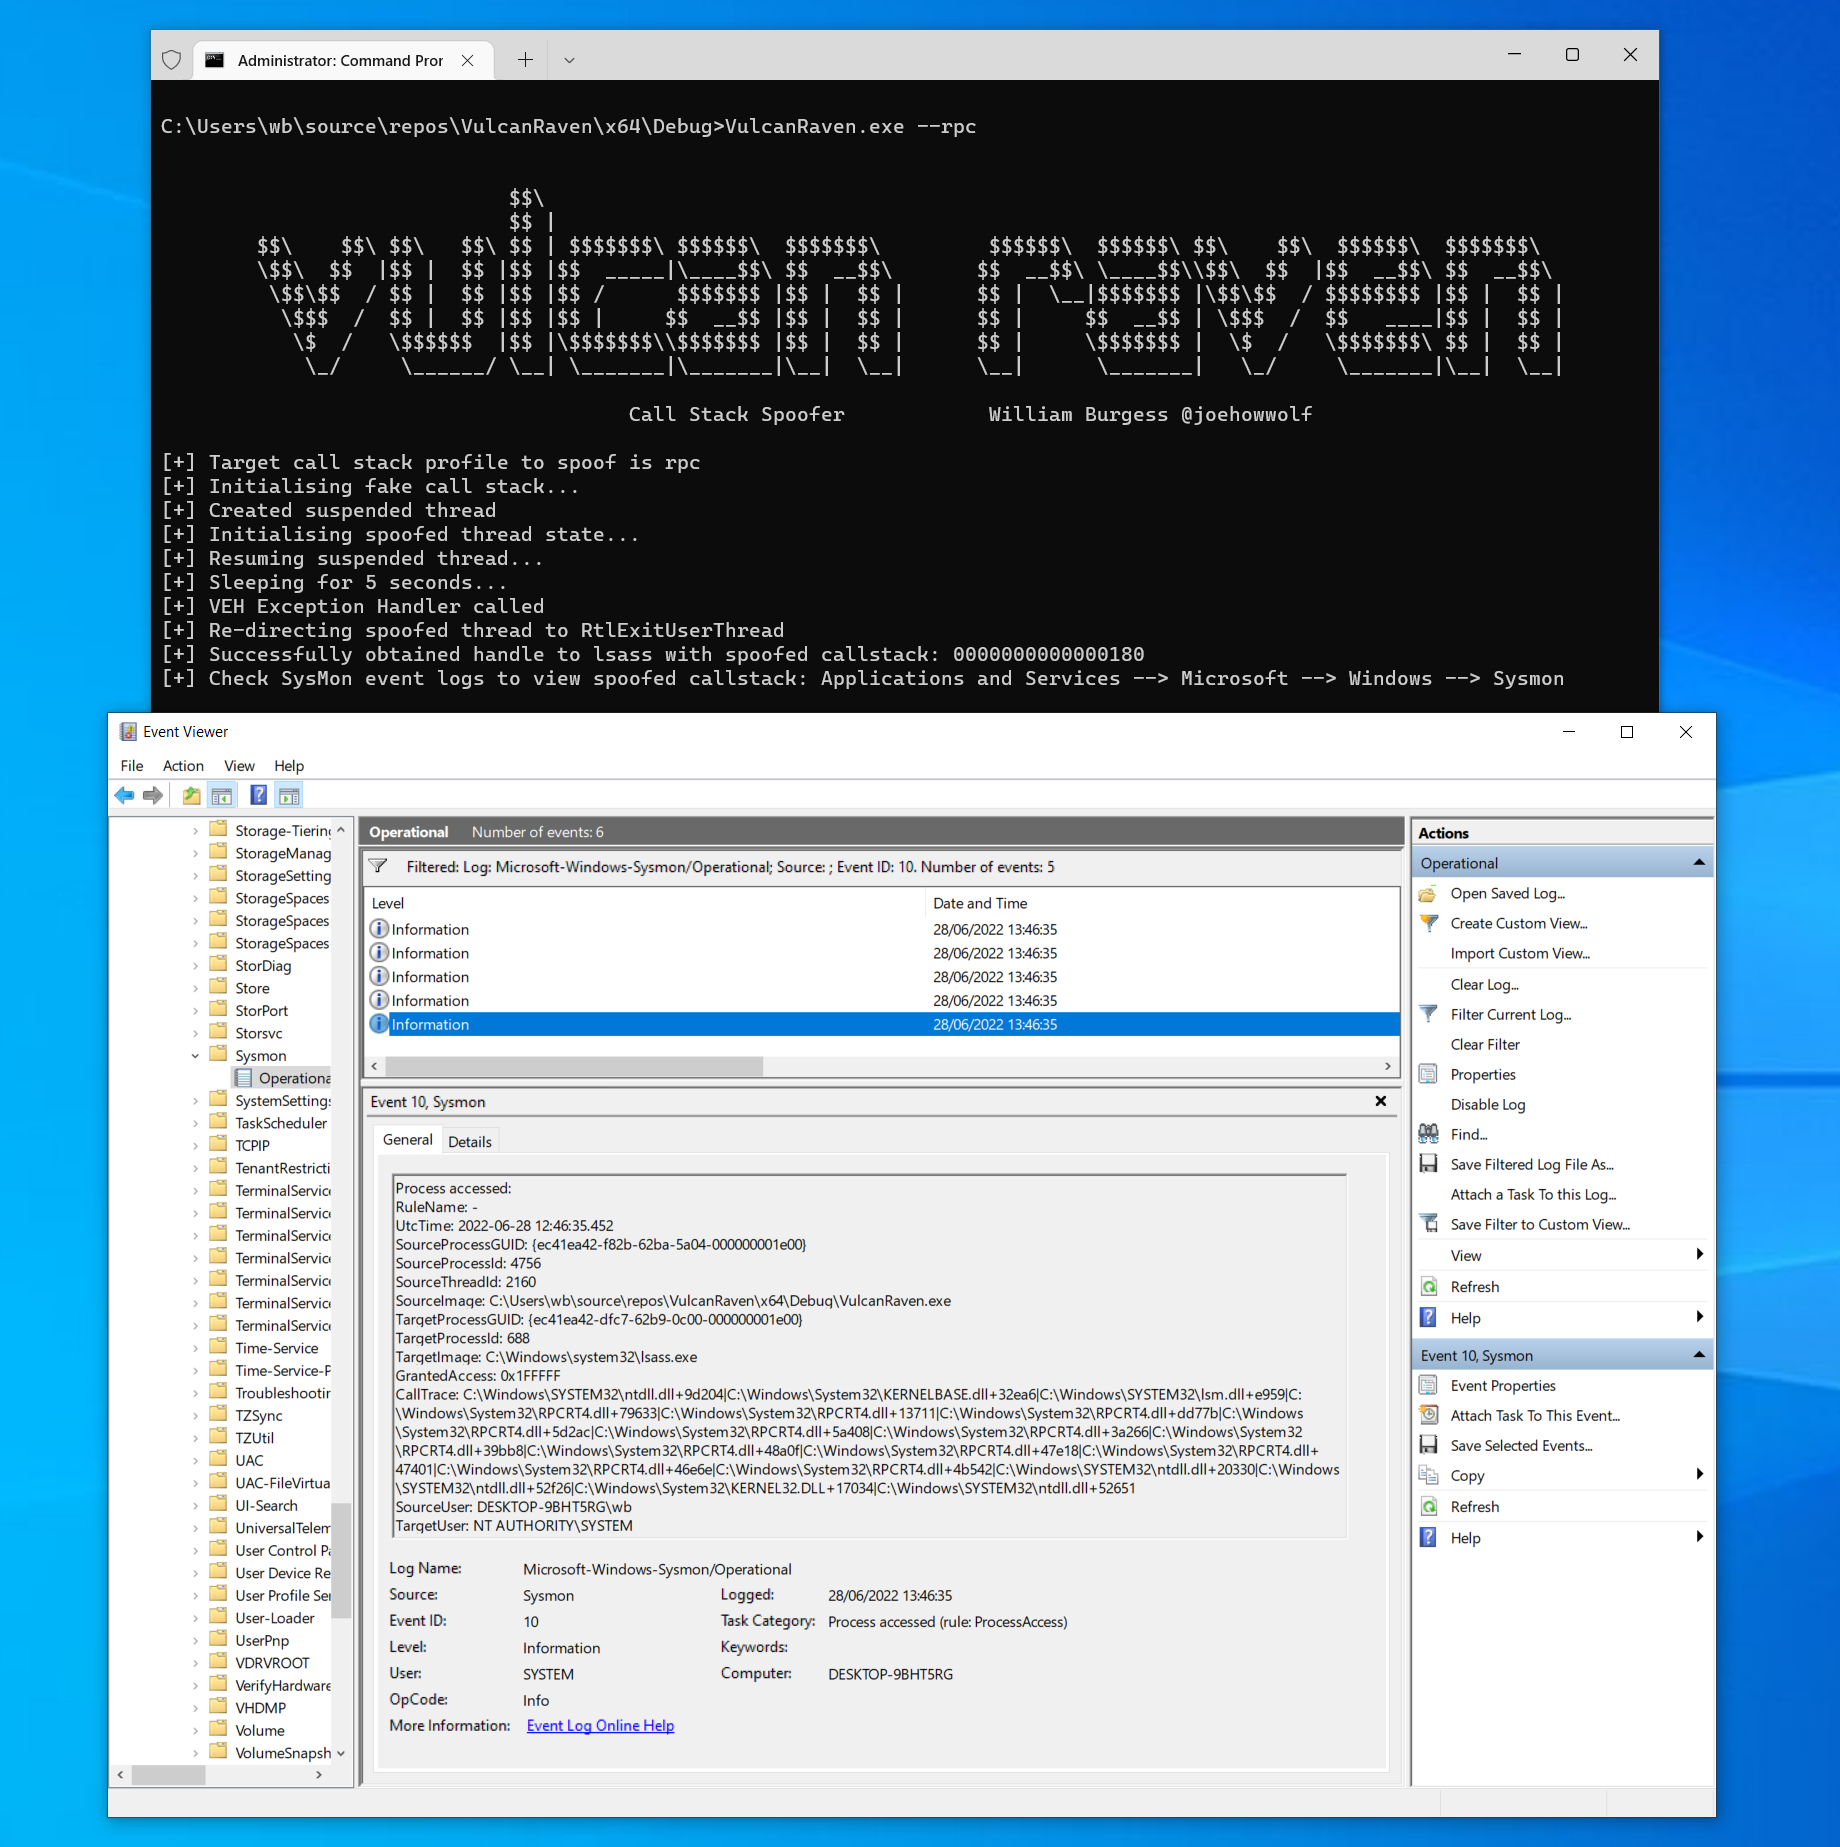 withsecurelabs/callstackspoofer
A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
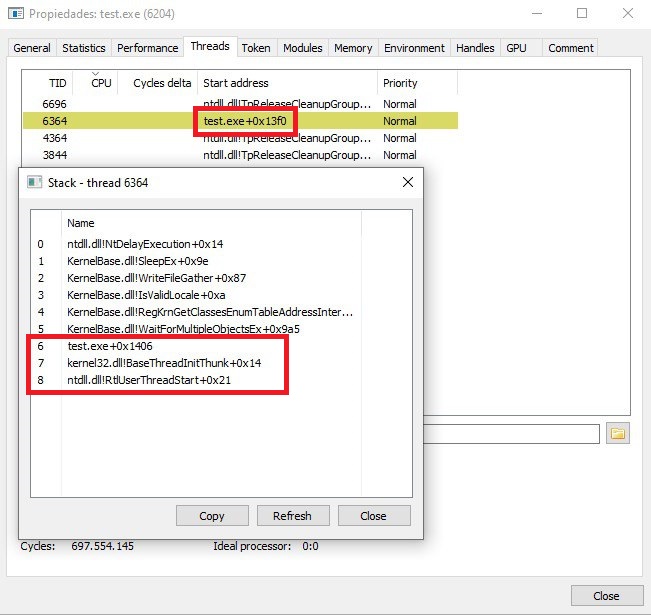 kudaes/unwinder
Call stack spoofing for Rust
 helviojunior/hookchain
HookChain: A new perspective for Bypassing EDR Solutions
 netero1010/edrsilencer
A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
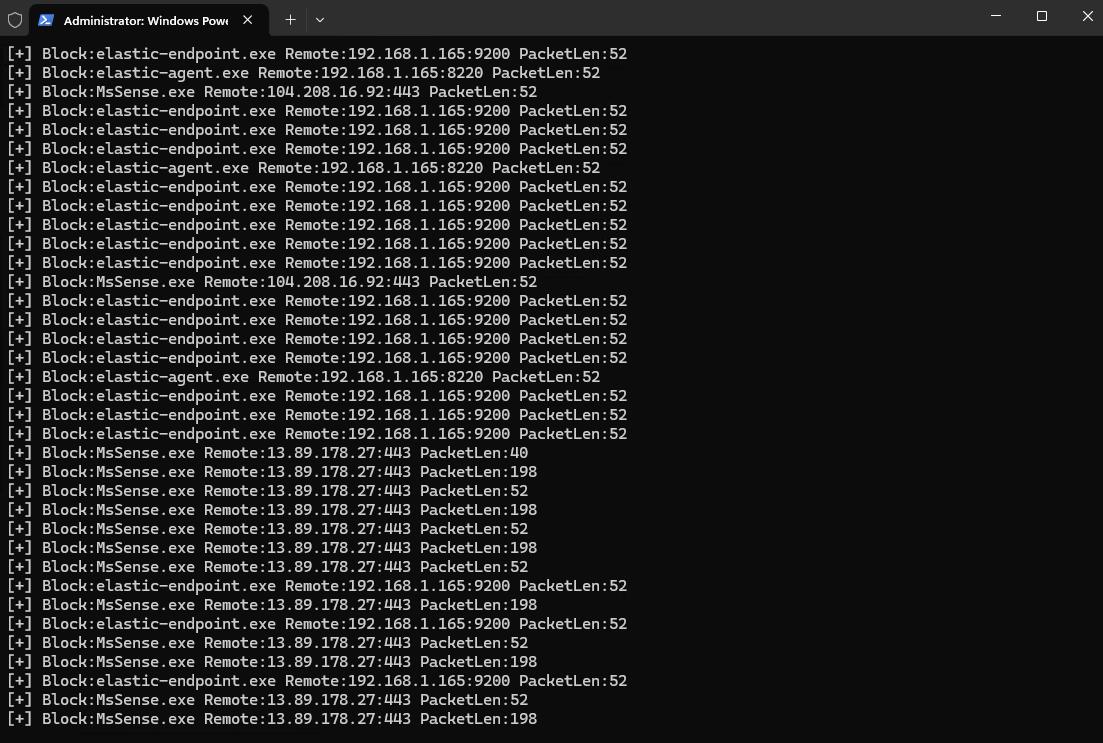 senzee1984/edrprison
Leverage a legitimate WFP callout driver to prevent EDR agents from sending telemetry
 es3n1n/no-defender
A slightly more fun way to disable windows defender + firewall. (through the WSC api)
 mr-un1k0d3r/amsi-etw-patch
Patch AMSI and ETW
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 gmh5225/bedaisy-bypass
Kernel-mode hook that intercepts, decrypts, and nullifies BEDaisy-to-service report traffic to suppress anti-cheat detection on UEFI and non-UEFI…