

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 marcgoam/cve-2026-54121-certighost
CVE-2026-54121 (Certighost) AD CS DC-impersonation PoC. Patched SAN handling + MAQ-safe account reuse.
 pasquini-dario/project_mantis
Project Mantis: Hacking Back the AI-Hacker; Prompt Injection as a Defense Against LLM-driven Cyberattacks
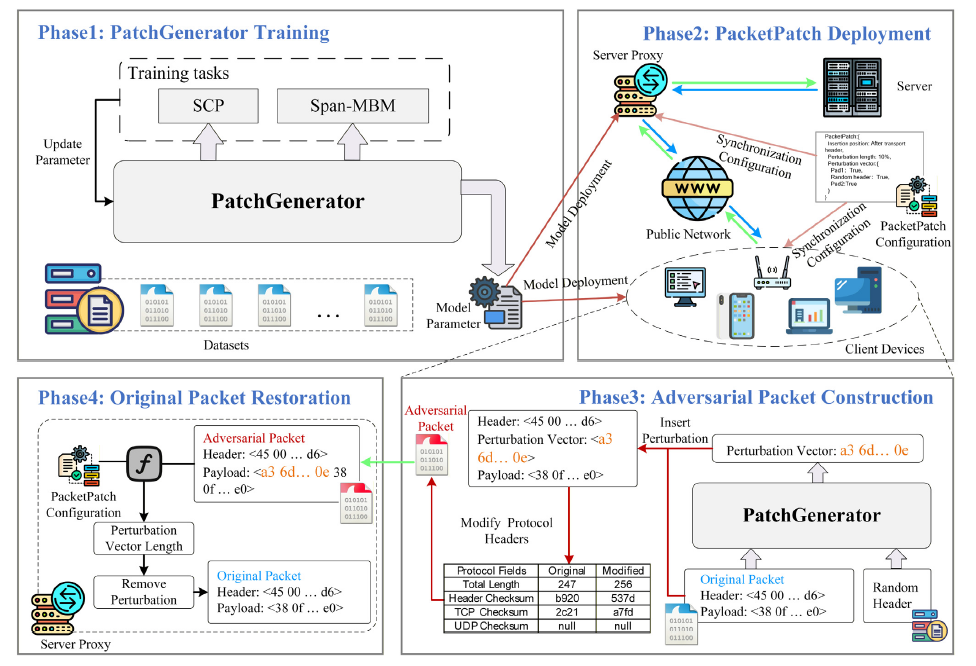 xuyw-seu/packetpatch
Practical black-box adversarial packet generation against encrypted traffic classification with minimal overhead and full packet recoverability.
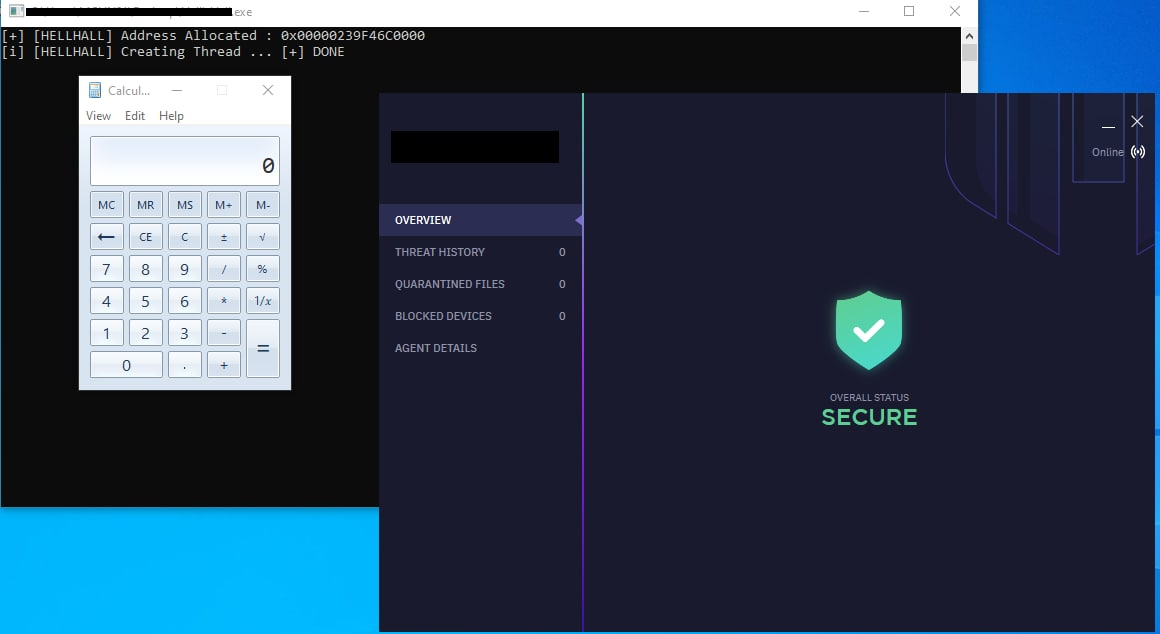 maldev-academy/hellhall
Performing Indirect Clean Syscalls
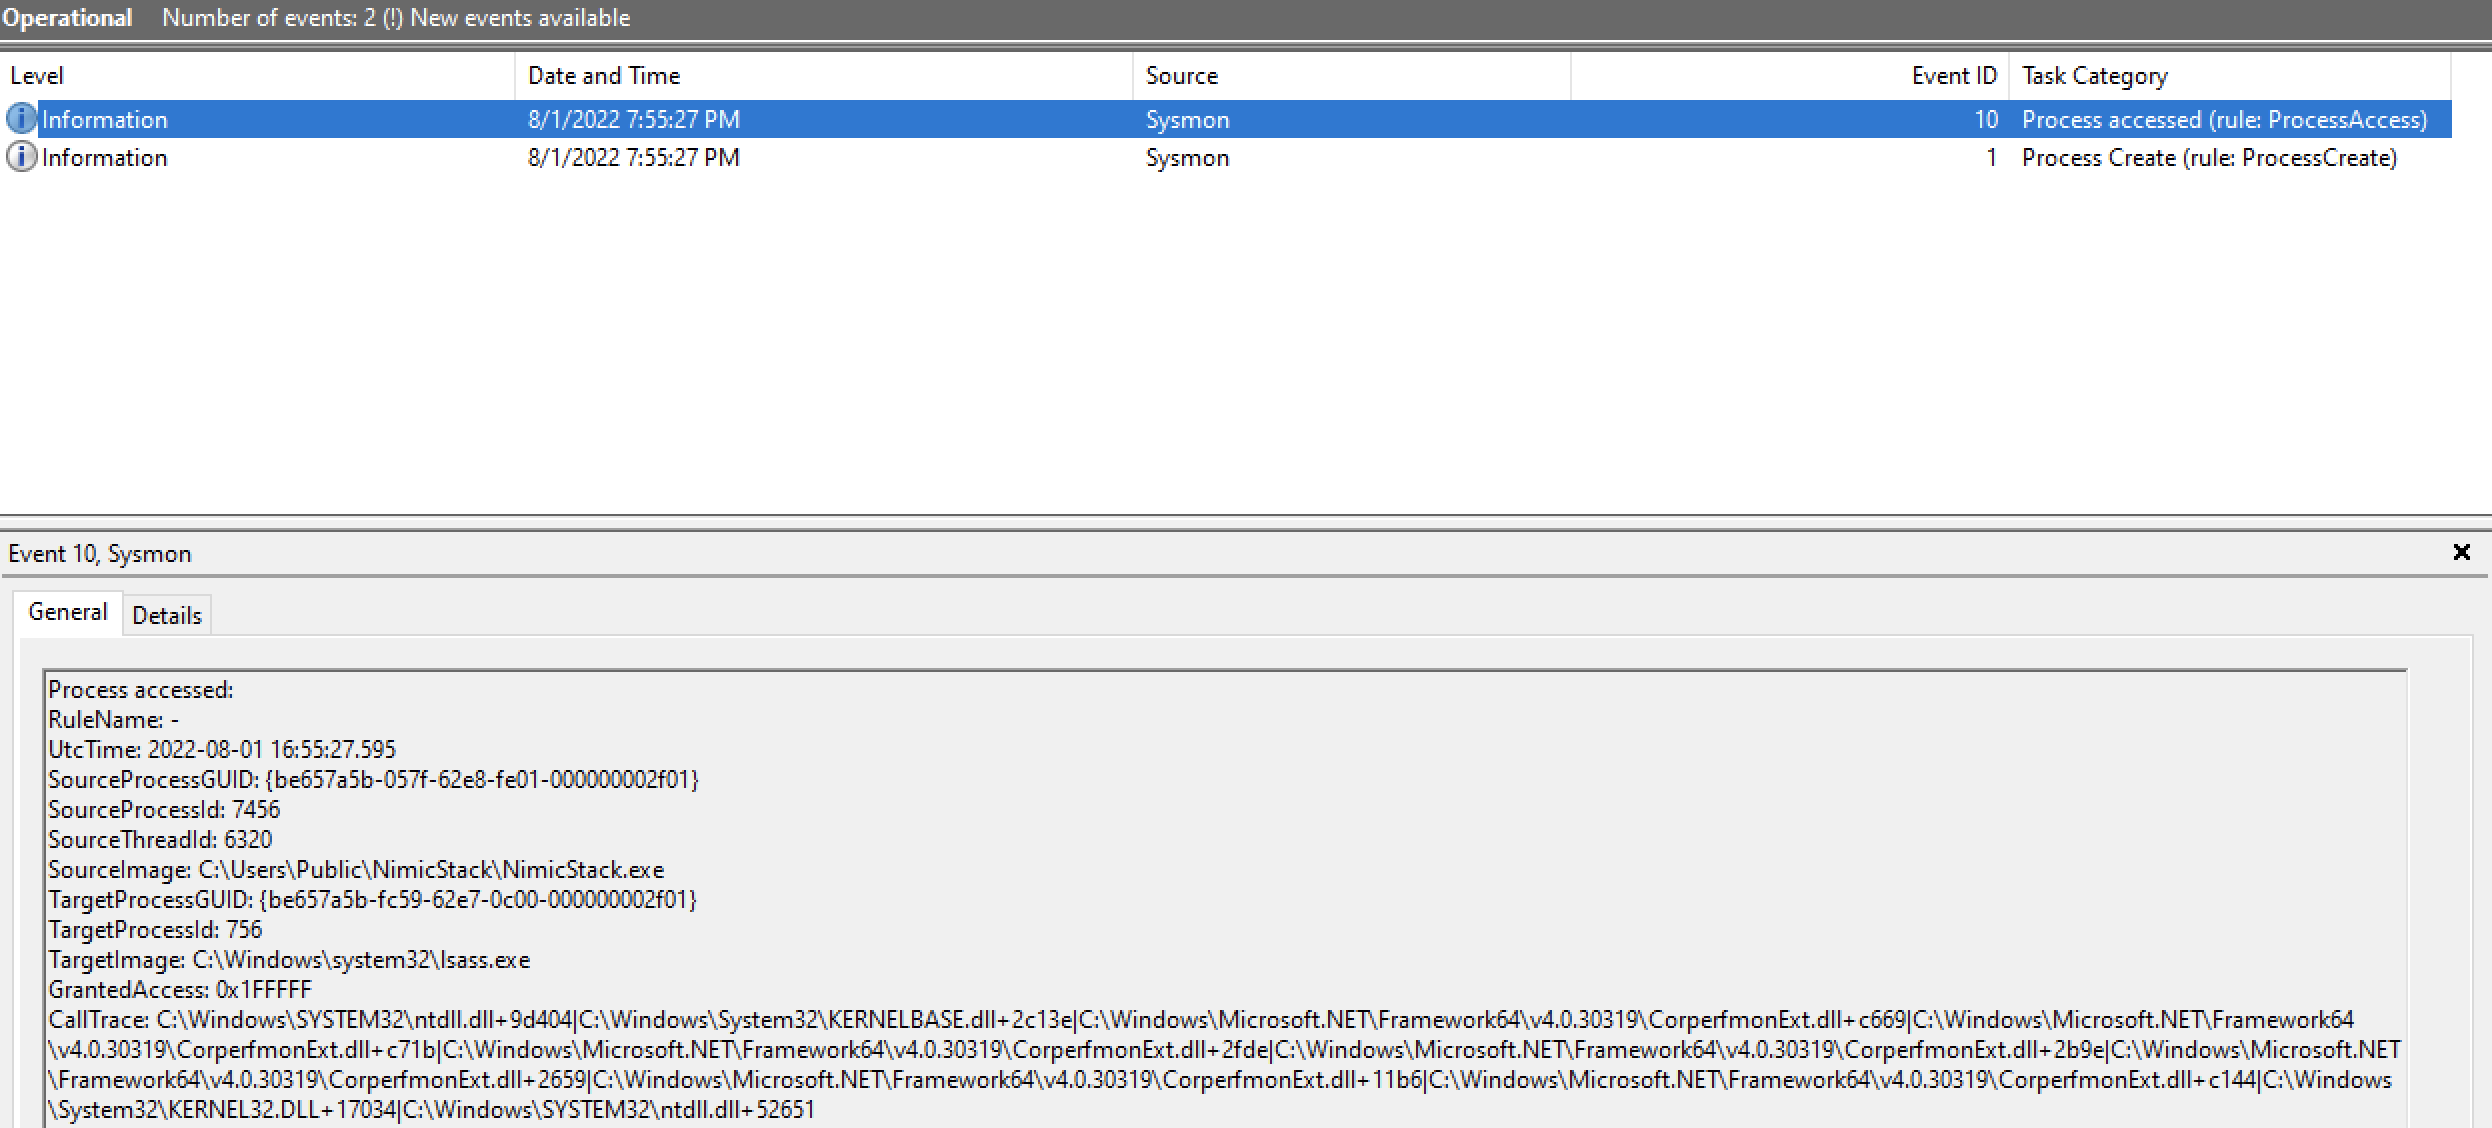 frkngksl/nimicstack
NimicStack is the pure Nim implementation of Call Stack Spoofing technique to mimic legitimate programs
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 r3drun3/magnet
Purple-team telemetry & simulation toolkit.
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.
 adityabhatt3010/cve-2025-54794-hijacking-claude-ai-with-a-prompt-injection-the-jailbreak-that-talked-back
A high-severity prompt injection flaw in Claude AI proves that even the smartest language models can be turned into weapons — all with a few lines of…
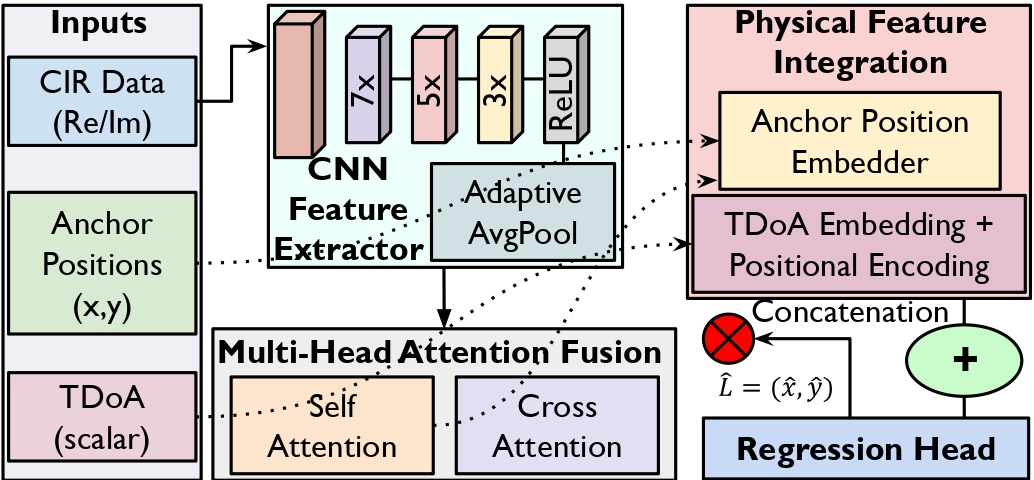 sec5gloc/sec5gloc
Adversary-resilient deep learning architecture for secure 5G indoor localization, combining CNN and multi-head attention to defend against signal…
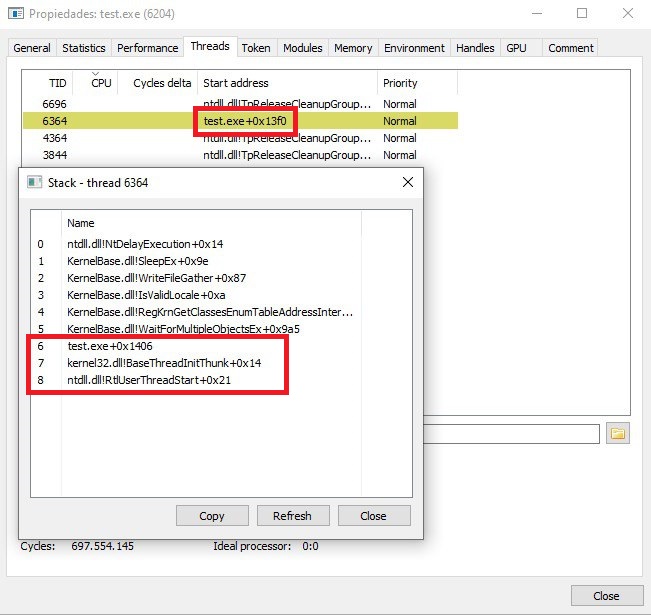 kudaes/unwinder
Call stack spoofing for Rust
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.