Awesome-MoAI-Security

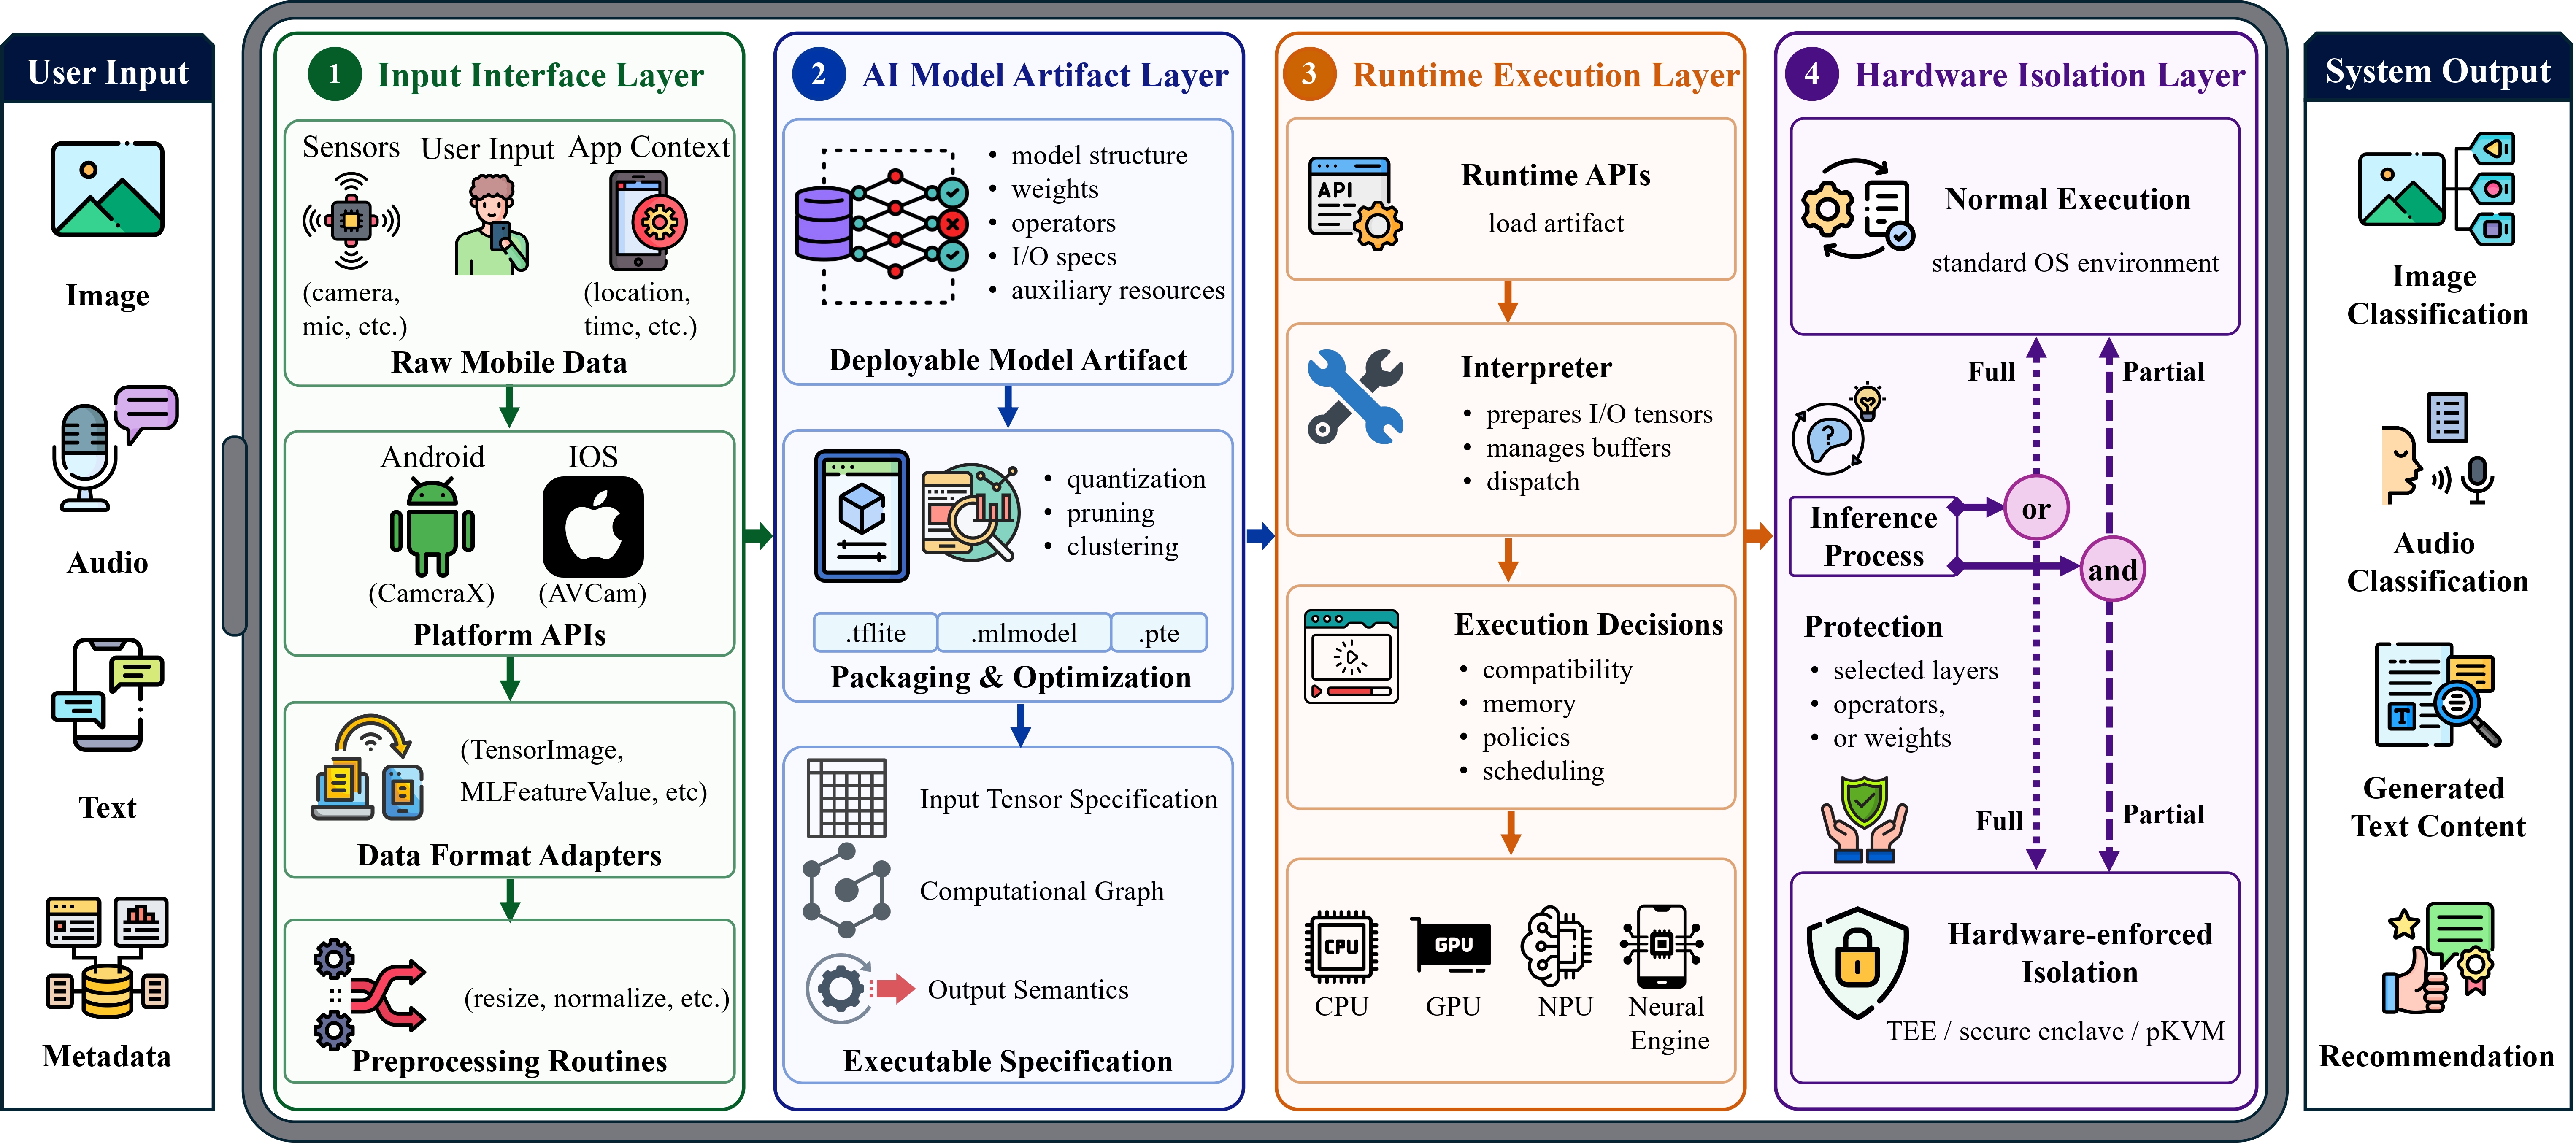
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…

Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…

reverse engineering Gemini's SynthID detection

Performing Indirect Clean Syscalls

PoCs and tools for investigation of Windows process execution techniques

reverse engineering SynthID for text

Anti-LLM obfuscation via finger counting

Tools and PoCs for Windows syscall investigation.

A security scanner for your LLM agentic workflows

Windows 11 24H2-25H2 Runtime PatchGuard Bypass

Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.

Create Anti-Copy DRM Malware

Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…

Lifetime AMSI bypass

Signtool for expired certificates

HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…

Different methods to detect a virtualized environment or potential debugging

Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…