

offensive-ai-compilation
 jiep/offensive-ai-compilation
A curated list of useful resources that cover Offensive AI.
adversarial-attackai-securitycurated-resources+5
1.4k
jiep/offensive-ai-compilationA curated list of useful resources that cover Offensive AI.
 giskard-ai/giskard-oss
🐢 Open-Source Evaluation & Testing library for LLM Agents
 ottosulin/awesome-ai-security
A collection of awesome resources related AI security
 togg53192-cmd/jailbreaks
Curated collection of LLM jailbreak prompts and bypass techniques, documenting adversarial inputs that circumvent AI model safety guardrails.
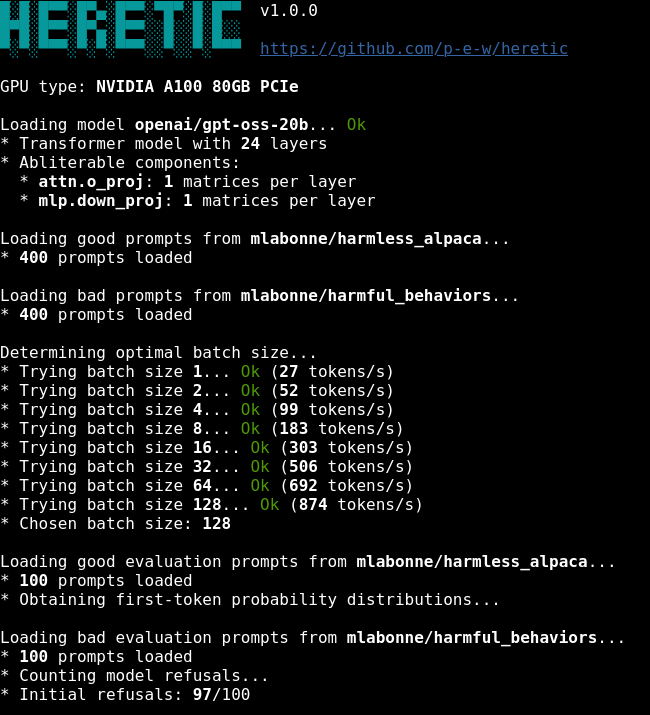 p-e-w/heretic
Training-free language model modification: Remove censorship, suppress slop, reduce sycophancy, and more
 promptfoo/promptfoo
Test your prompts, agents, and RAGs. Red teaming/pentesting/vulnerability scanning for AI. Compare performance of GPT, Claude, Gemini, DeepSeek, and…
 hectorm/hblock
Improve your security and privacy by blocking ads, tracking and malware domains.
 meta-llama/purplellama
Set of tools to assess and improve LLM security.
 datadog/stratus-red-team
:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
 requie/ai-red-teaming-guide
A comprehensive guide to adversarial testing and security evaluation of AI systems, helping organizations identify vulnerabilities before attackers…
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
 bishopfox/sliver
Adversary Emulation Framework
 gmh5225/awesome-ai-security
A curated list of AI Security materials and resources for Pentesters, Bug Hunters, and Security Researchers.
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 meridianlabs-ai/inspect_petri
An alignment auditing agent capable of quickly exploring alignment hypothesis
 suels-group/beyond_asr
Research code for measuring jailbreak attack success rates (ASR and stepwise ASR) against LLMs, with implementations of attacks such as GCG and…
 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 ye-ze-yu/epireal-bench
Red-teaming benchmark and black-box attack framework for evaluating visual misinformation risks in commercial image generators, with 10k false-claim…