APTs-Adversary-Simulation

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…

PoC demonstrating quadratic DoS in Elixir html_sanitize_ex via crafted HTML; includes timing benchmarks, remote exploitation curl, and verification…

XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE PoC mirror — WordSec, MIT; for authorized security testing

A simple PoC on the Remote Code Execution (RCE) Vulnerability of CraftCMS designated as CVE-2025-32432 written in Go

Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…

Proof-of-concept exploit for CVE-2026-21003 demonstrating JWT authentication bypass by omitting the kid header and using the 'none' algorithm to…

A delicious, but malicious SSL-VPN server 🌮

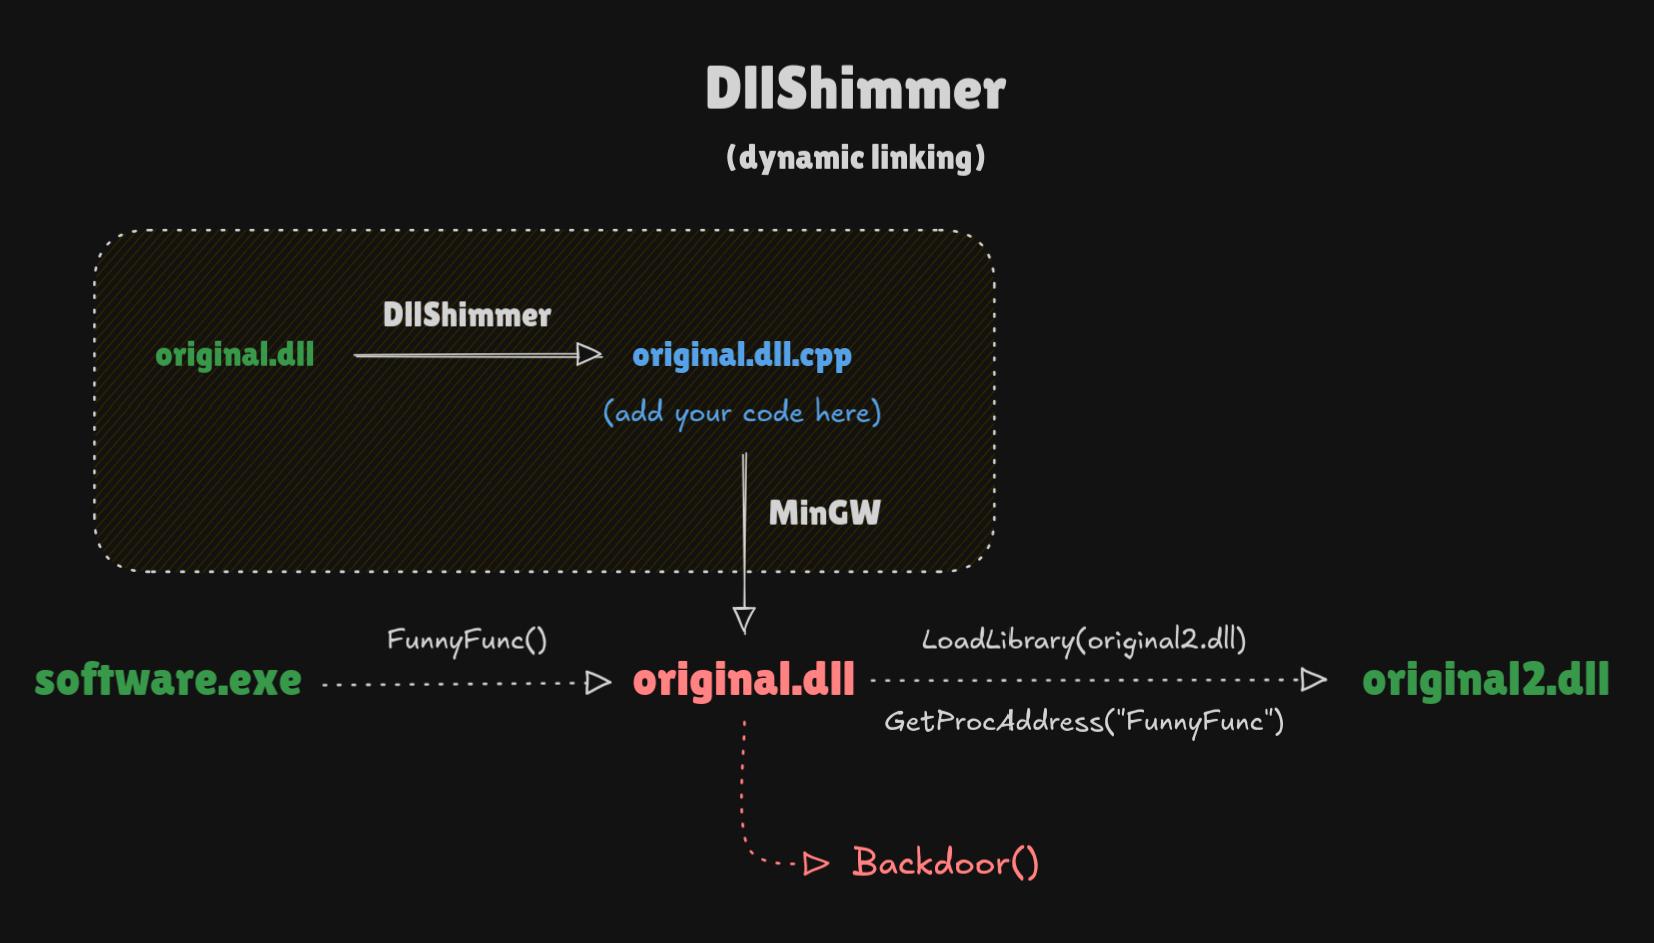
Weaponize DLL hijacking easily. Backdoor any function in any DLL.

Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.

Modern PIC implant for Windows (64 & 32 bit)

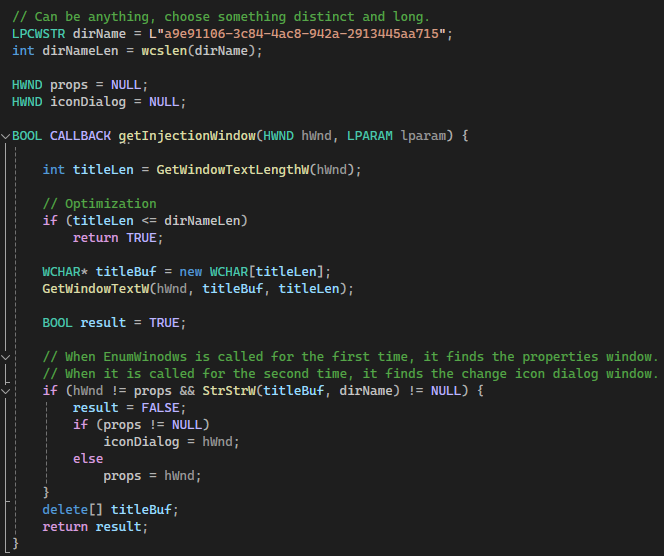
Inject DLLs into the explorer process using icons

Threadless Process Injection using remote function hooking.

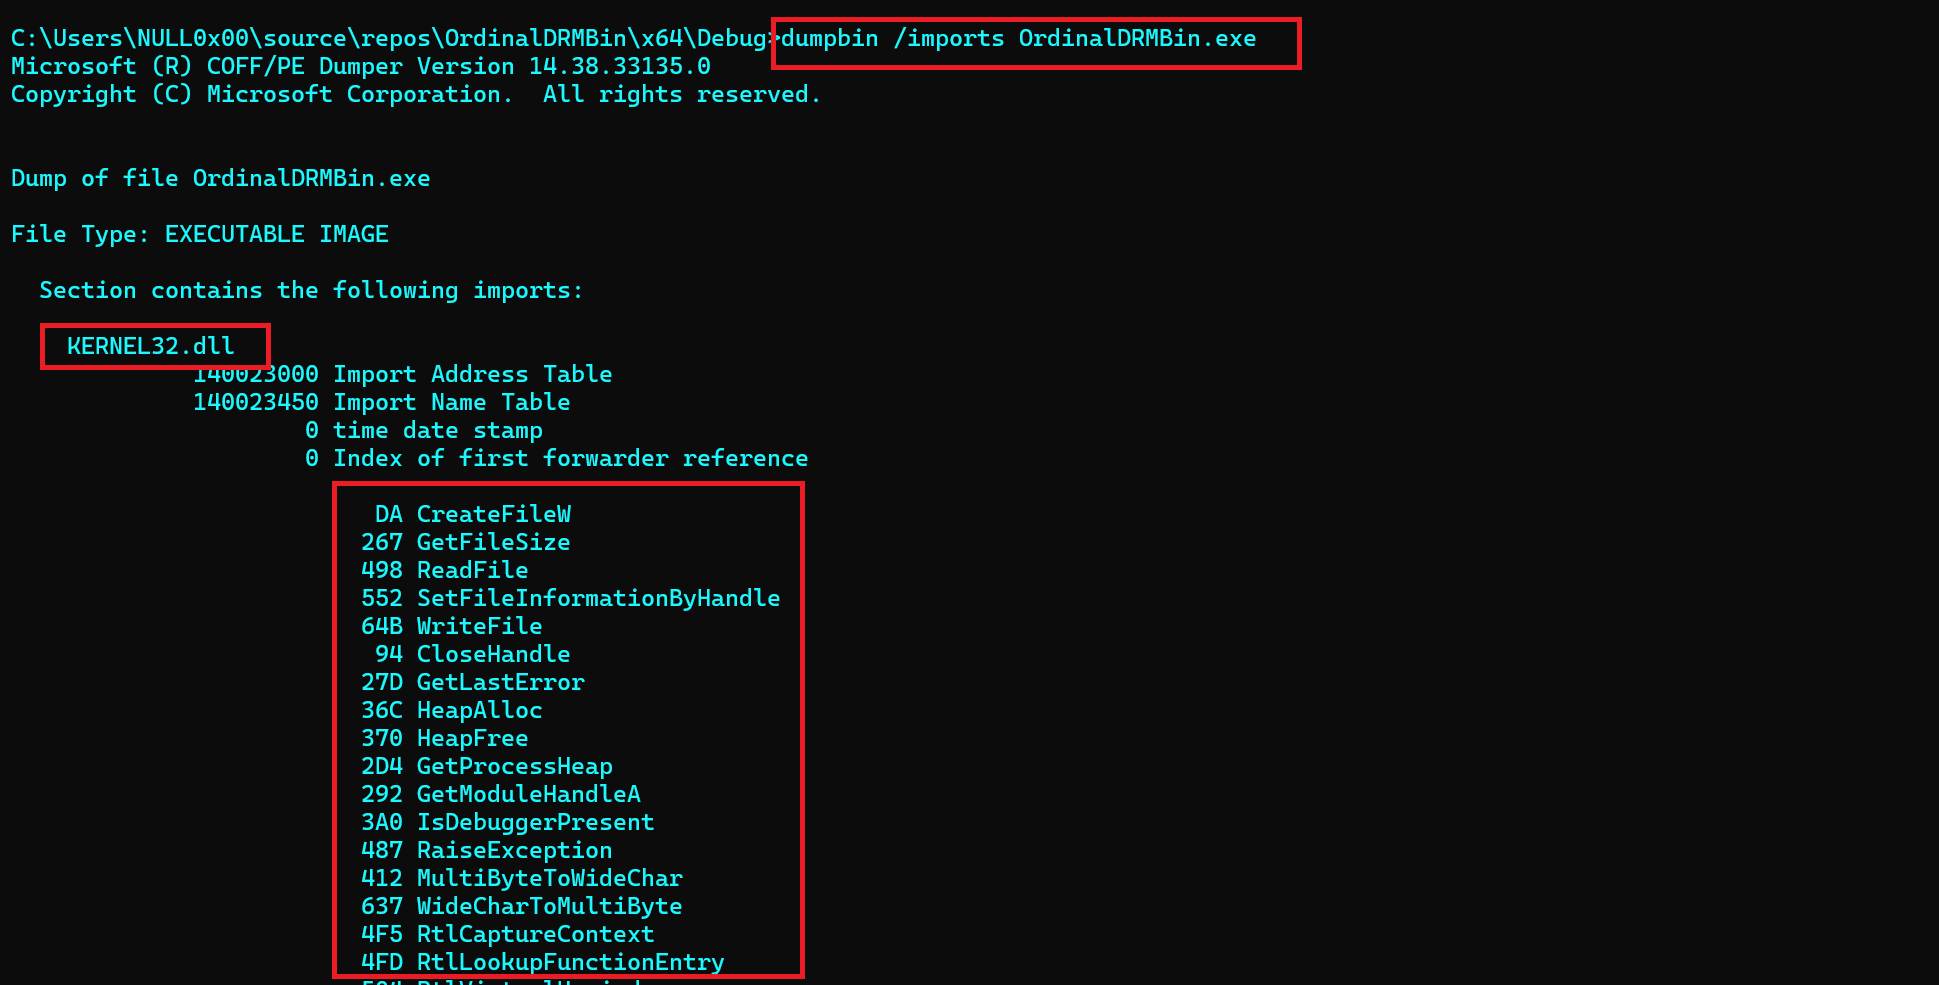
Create Anti-Copy DRM Malware

A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.

A new simple and powerfull packer for malware

A payload delivery system which embeds payloads in an executable's icon file!

macOS Initial Access Payload Generator

Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.