

mora-hwbp
 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
adversarial-attackdebuggersdefensive-tools+3
22
dovughs/mora-hwbpHardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
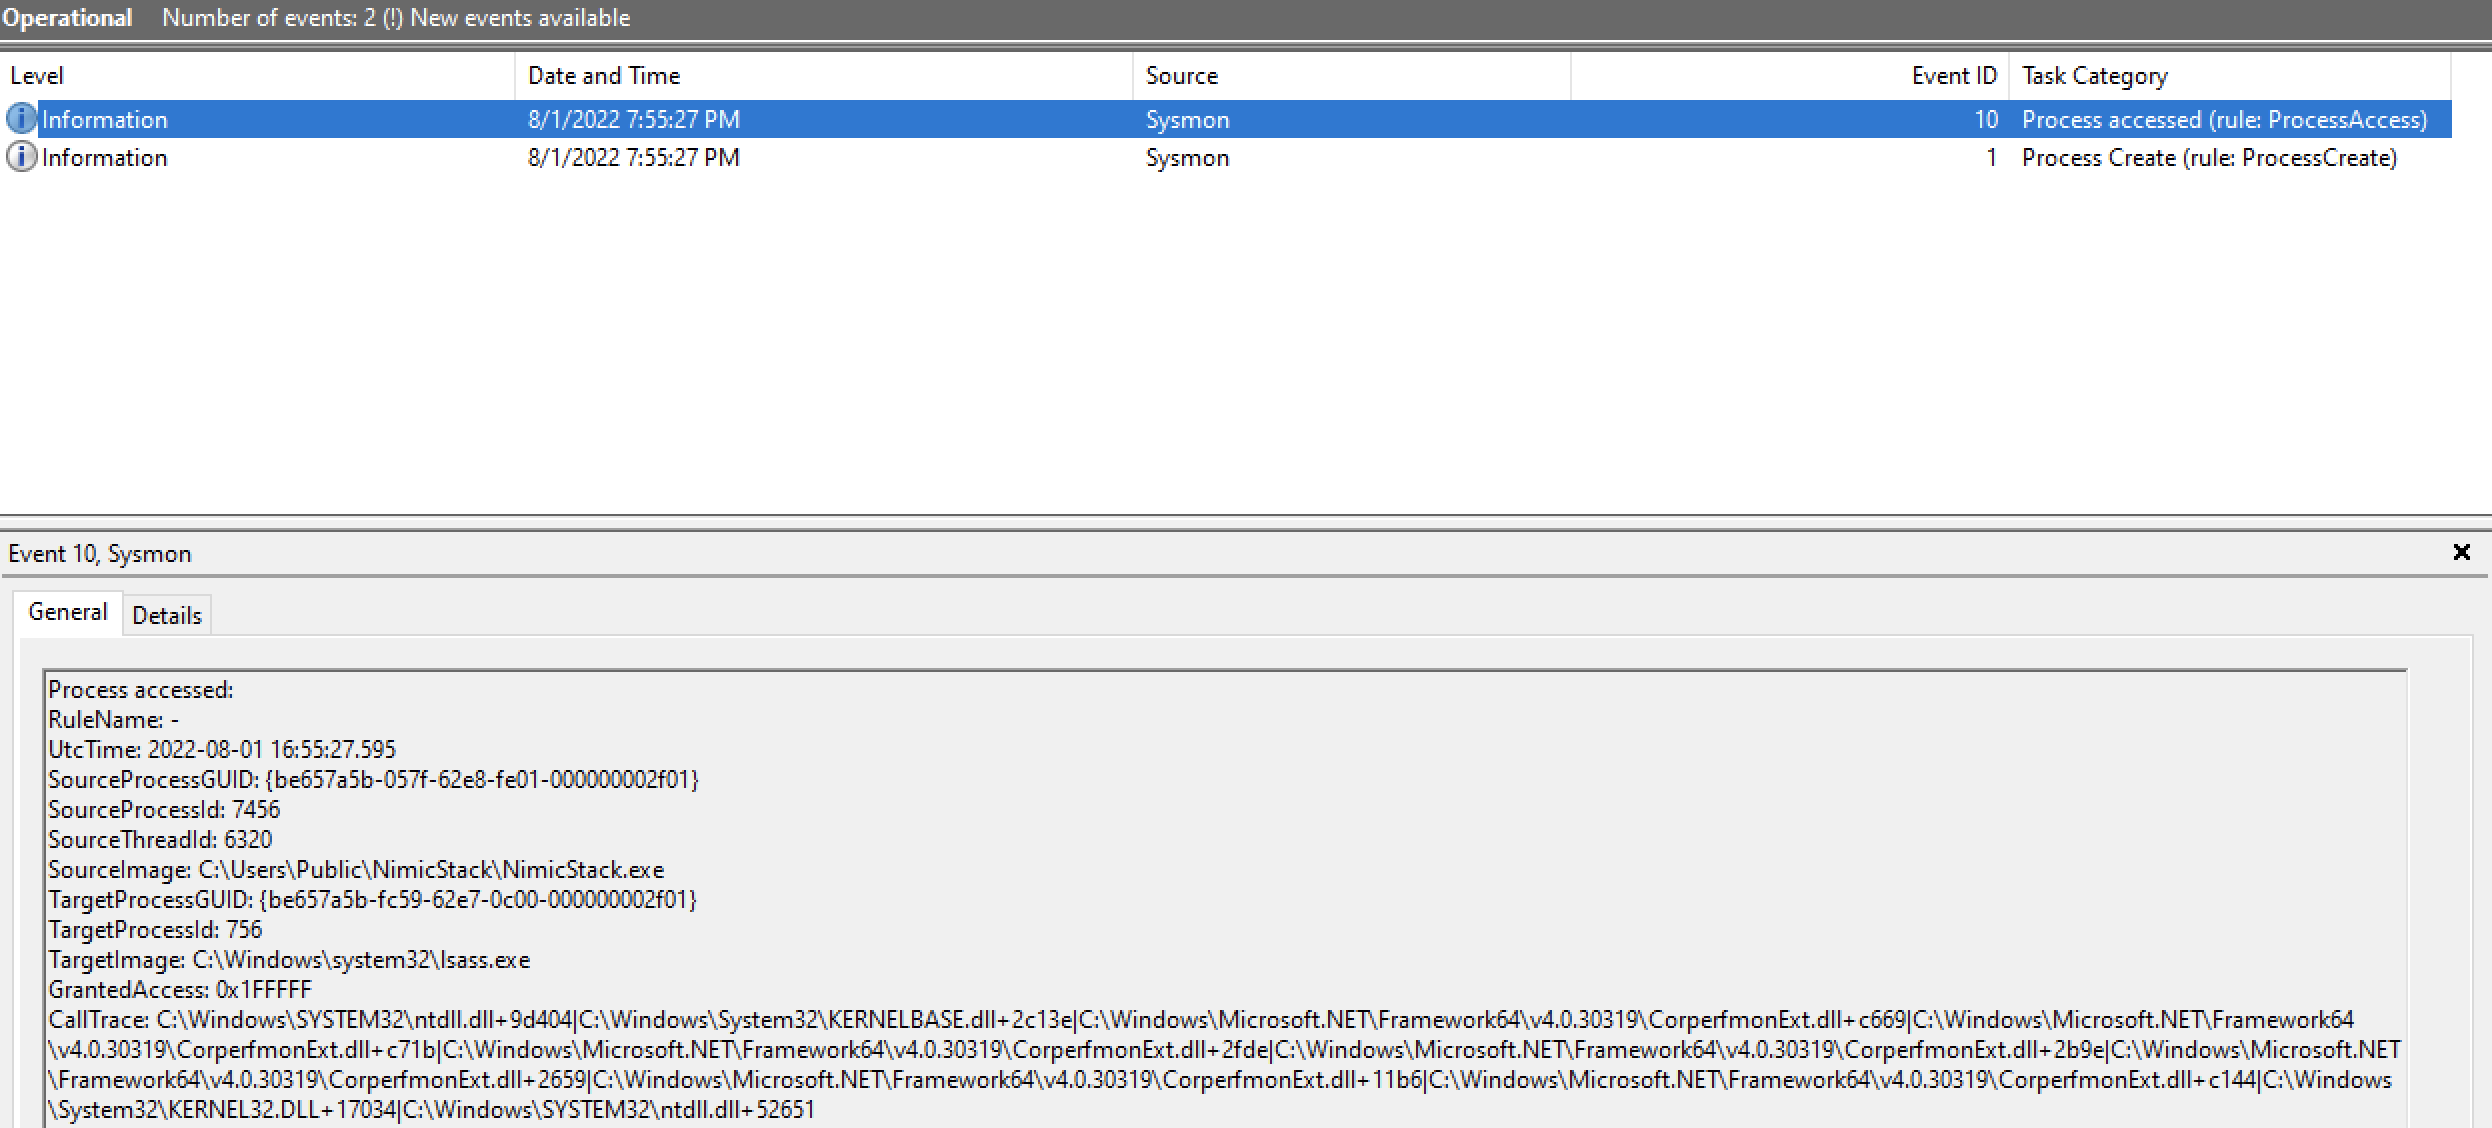 frkngksl/nimicstack
NimicStack is the pure Nim implementation of Call Stack Spoofing technique to mimic legitimate programs
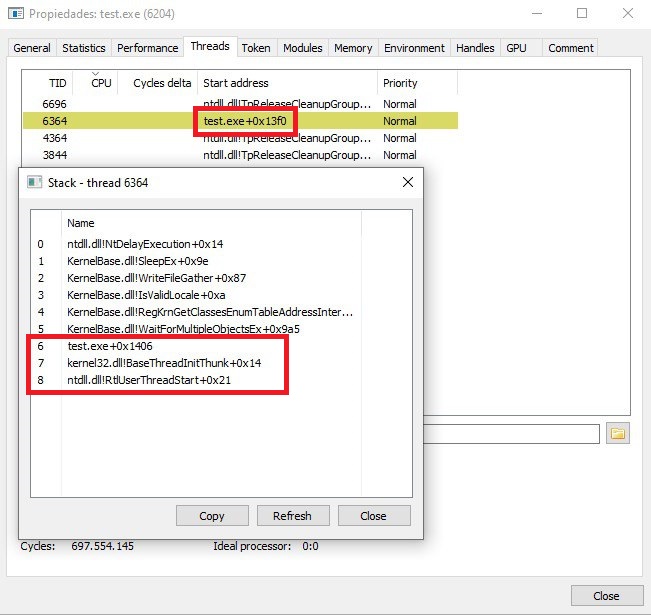 kudaes/unwinder
Call stack spoofing for Rust
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
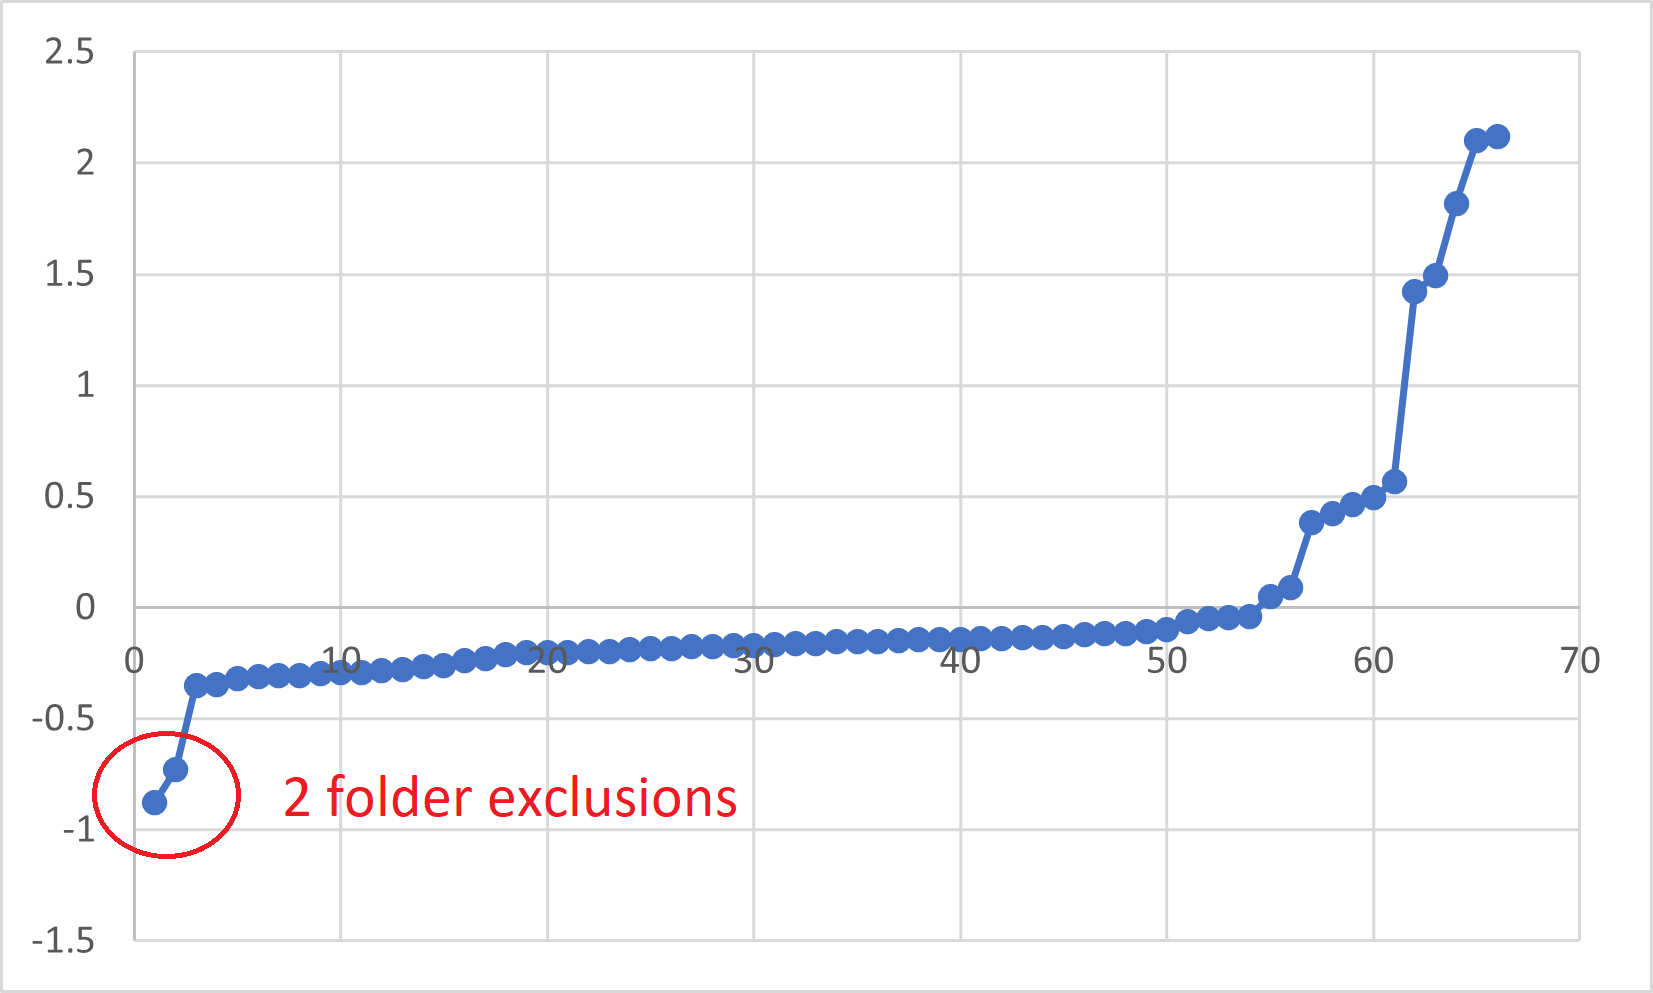 bananabr/timeexception
A tool to find folders excluded from AV real-time scanning using a time oracle
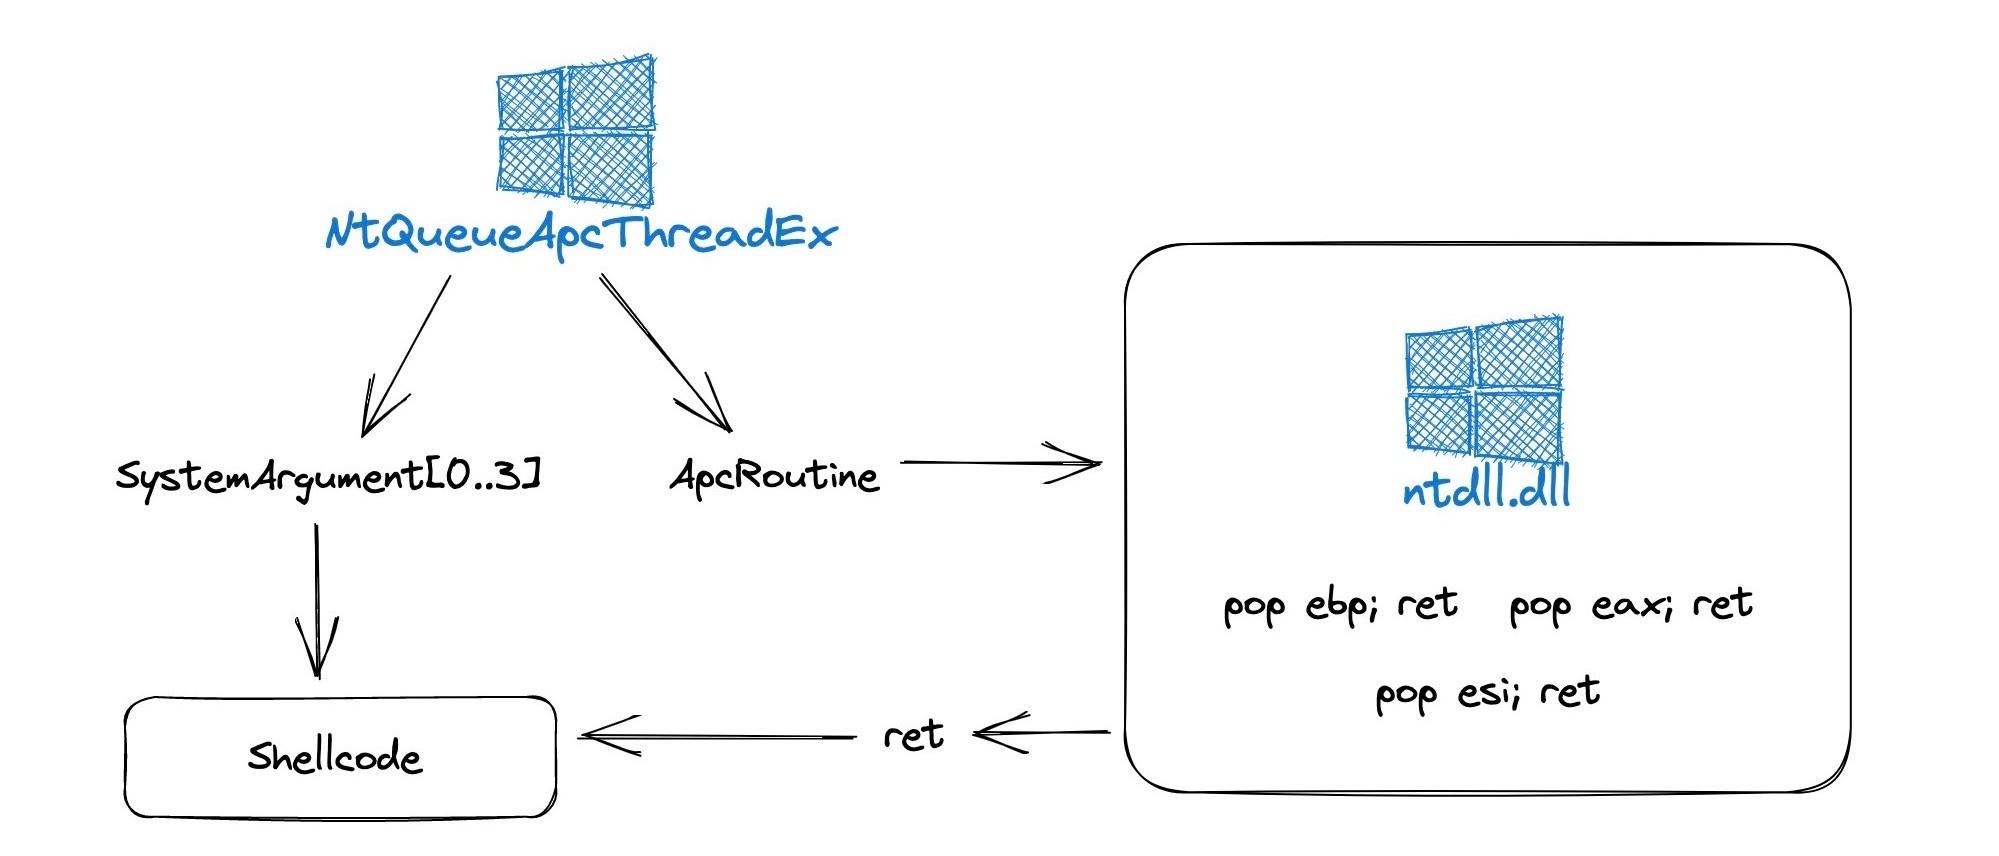 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
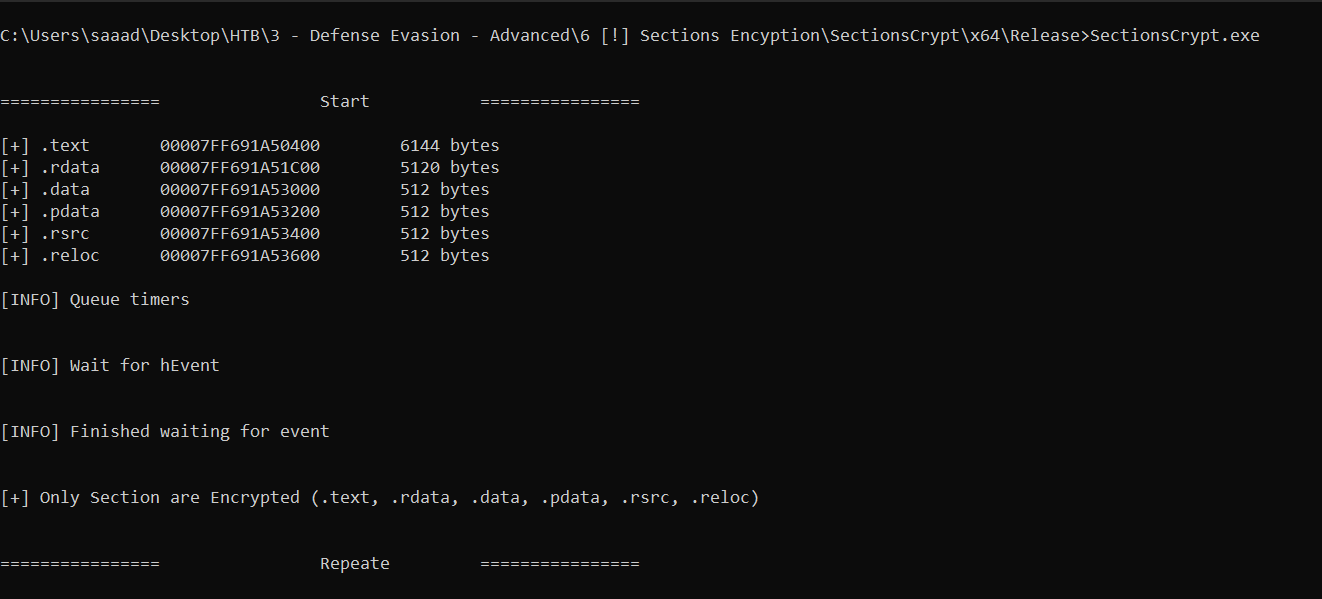 saadahla/d1rksleep
Improved version of EKKO by @5pider that Encrypts only Image Sections
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
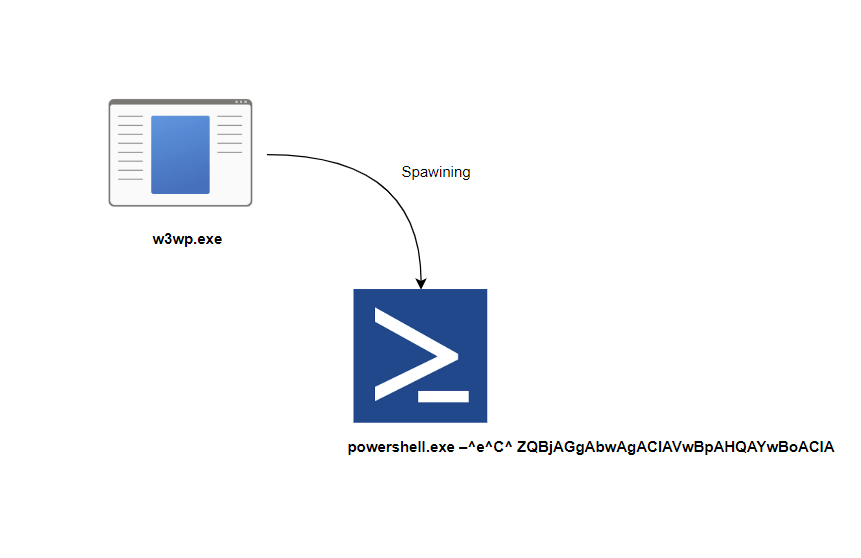 alwashali/detection-validation
Detection rule validation
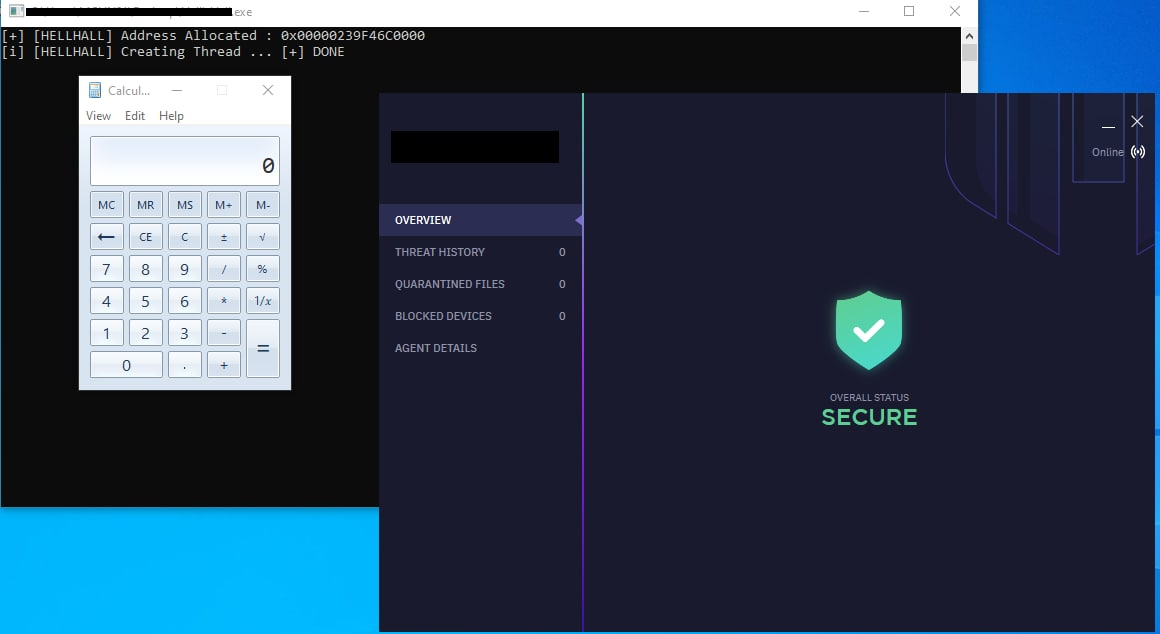 maldev-academy/hellhall
Performing Indirect Clean Syscalls
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 netero1010/edrsilencer
A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
 soufianetahiri/teamsntlmleak
Leak NTLM via Website tab in teams via MS Office