Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Open-Source SOC — Open-source SOC lab that collects and normalizes logs with Fluent Bit and Vector, detects anomalies via Suricata and OpenSearch, and auto-creates ITSM incident tickets in Znuny. | Kitploit
Tools/GitLabGitLab/pet-projects2845224/open-souce-soc
Defensive ToolsWeb SecurityNetwork SecurityIntrusion DetectionLearning & EducationIncident ResponseDNS AnalysisAnomaly DetectionLog Analysis
Share
Labs & Practice
GitLabpet-projects2845224/open-souce-soc

Open-Source SOC

Open-source SOC lab that collects and normalizes logs with Fluent Bit and Vector, detects anomalies via Suricata and OpenSearch, and auto-creates ITSM incident tickets in Znuny.

View Repository
1 day agoNot yet reviewed

🛡️ Pet-Project: Open-Source SIEM & ITSM Lab (Part 1)

📝 Project Description

This project is a laboratory setup demonstrating the full lifecycle of security event processing: from collecting logs from endpoint devices to creating incidents in a Service Management (ITSM) system.

The architecture is built exclusively on Open-Source solutions and simulates the operation of a Security Operations Center (SOC) capable of detecting anomalies, generating alerts, and automatically creating tickets for analysts.

This part covers: collection, normalization, storage, basic correlation, and incident management.
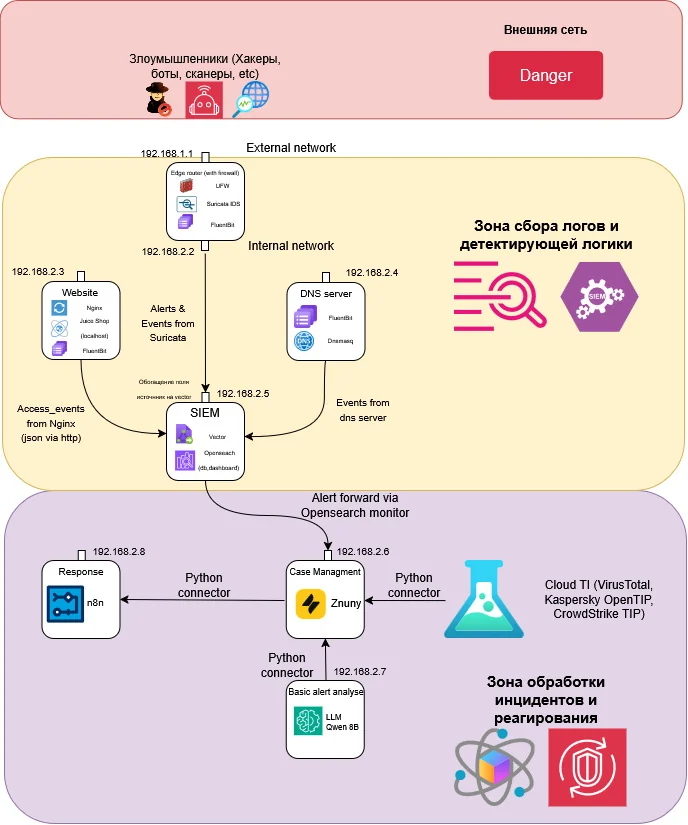

🏗️ Architecture (Diagram)

Project architecture diagram

Components and their roles:

ComponentRoleIP address
Nginx + JuiceShopWeb server (Reverse Proxy) with a vulnerable application.192.168.25.3
dnsmasqLocal DNS server for generating DNS logs.192.168.25.4
SuricataIDS/IPS for traffic analysis and alert generation.192.168.25.2
Fluent BitLightweight log collection and initial forwarding agent.On sources
VectorLog aggregator, normalizer, and router (VRL).192.168.25.5
OpenSearchData storage (SIEM) and correlation engine.192.168.25.5
Znuny (OTRS)ITSM system for incident management.192.168.25.6

⚙️ Implementation

Receiving normalized events in OpenSearch:
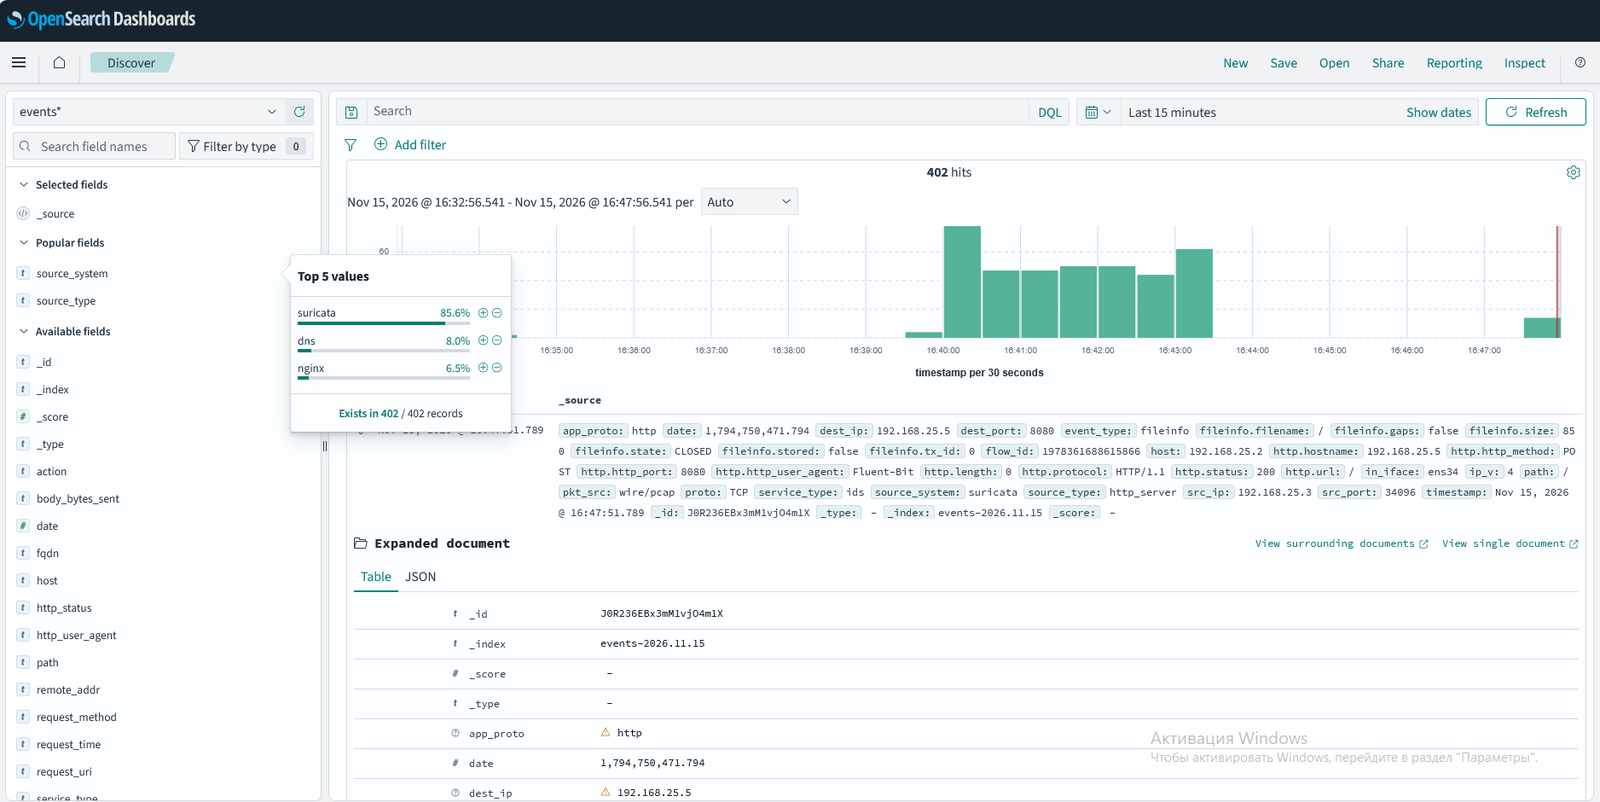
Events

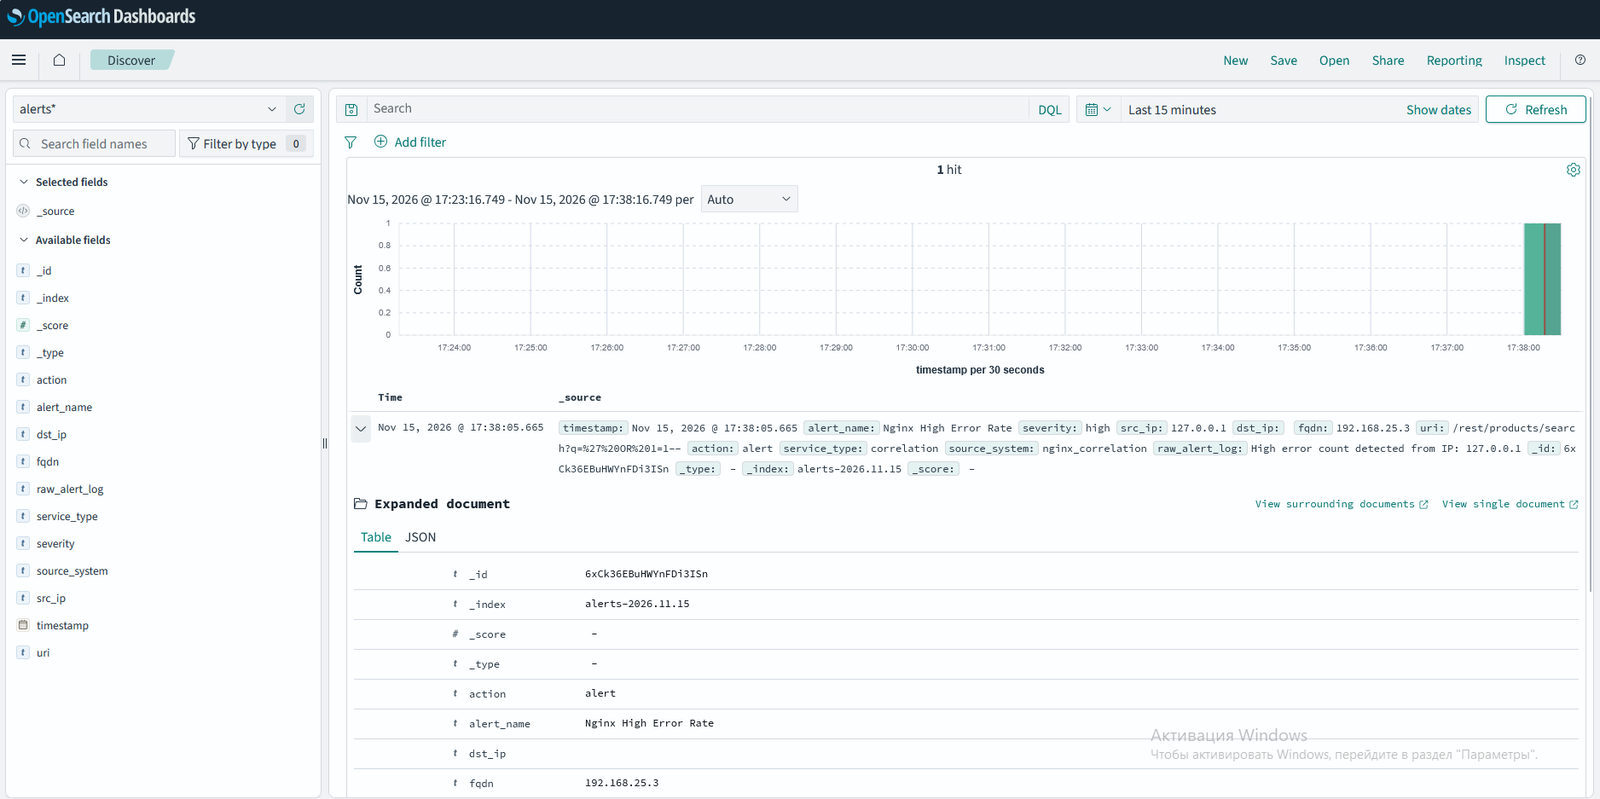
Receiving alerts in OpenSearch (Suricata):
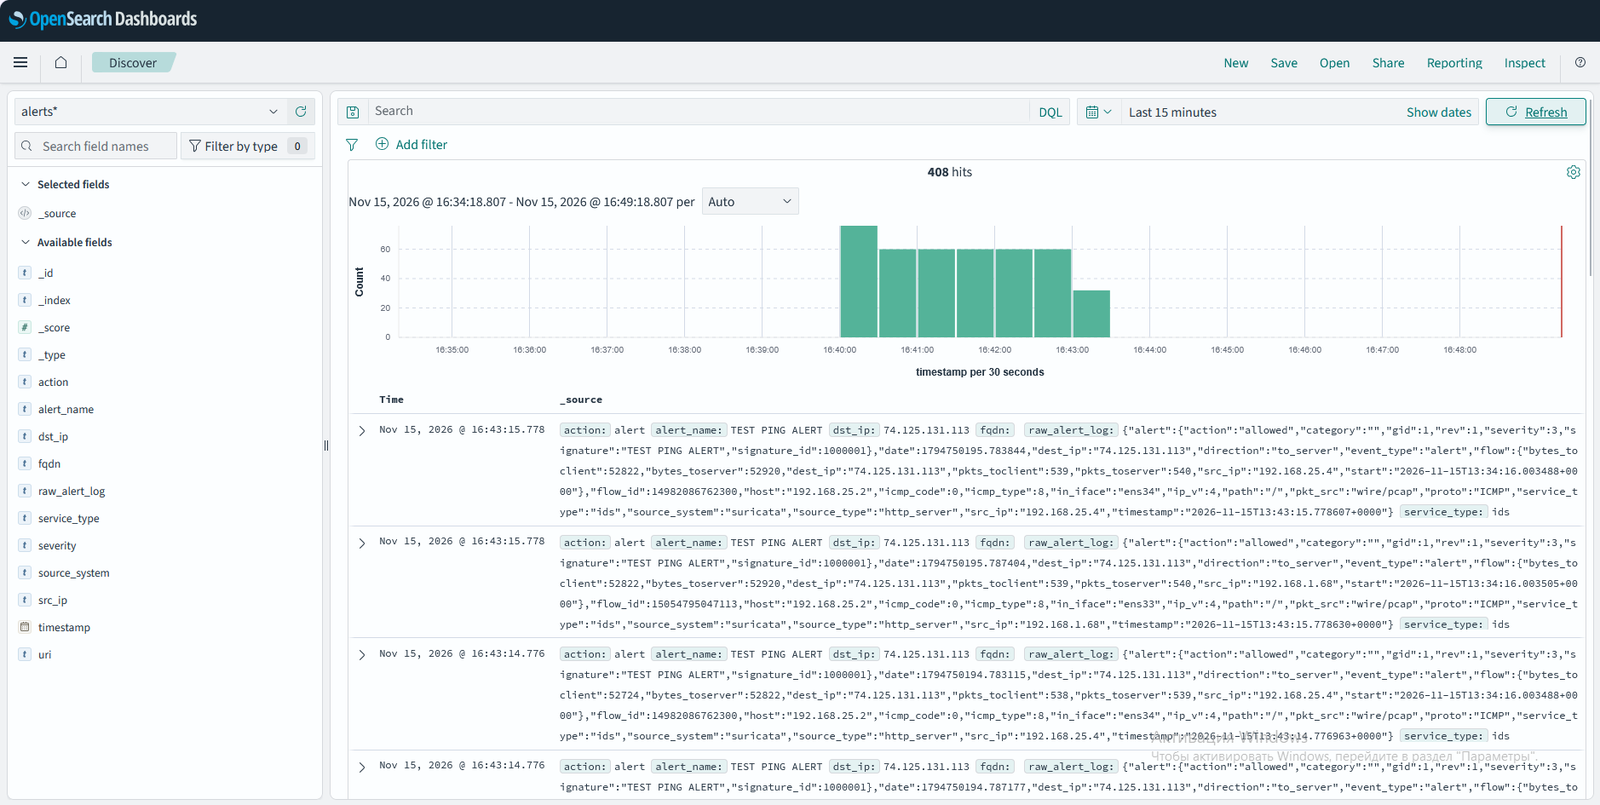
Alerts_Suricata

Created monitor for Nginx events in OpenSearch (as an example of a correlation rule):
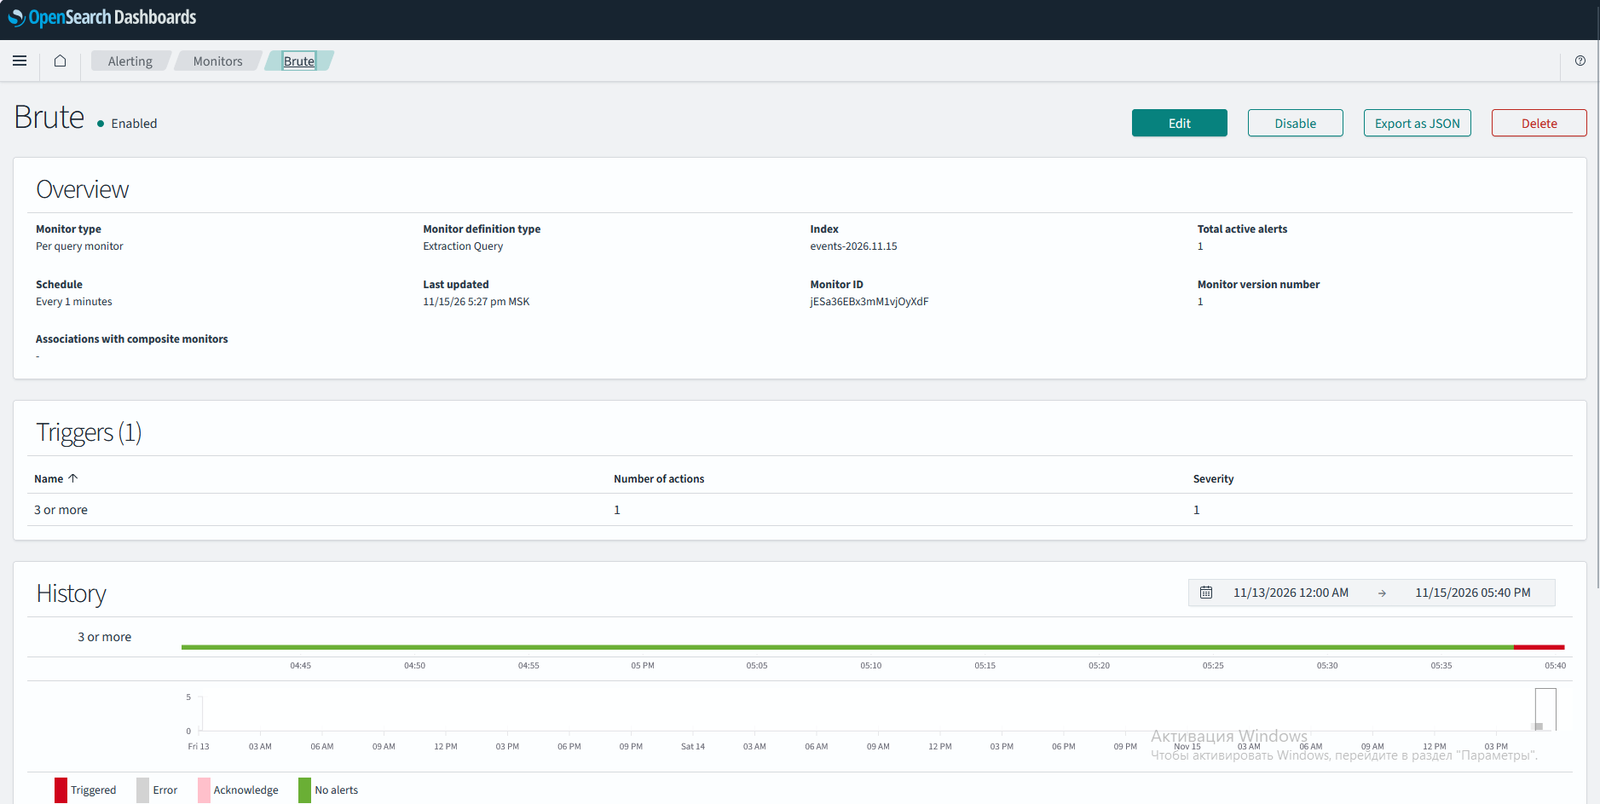
Custom_Monitor

Alert by Nginx rule in OpenSearch:

Nginx_Alert

Receiving alerts in ITSM for case management:
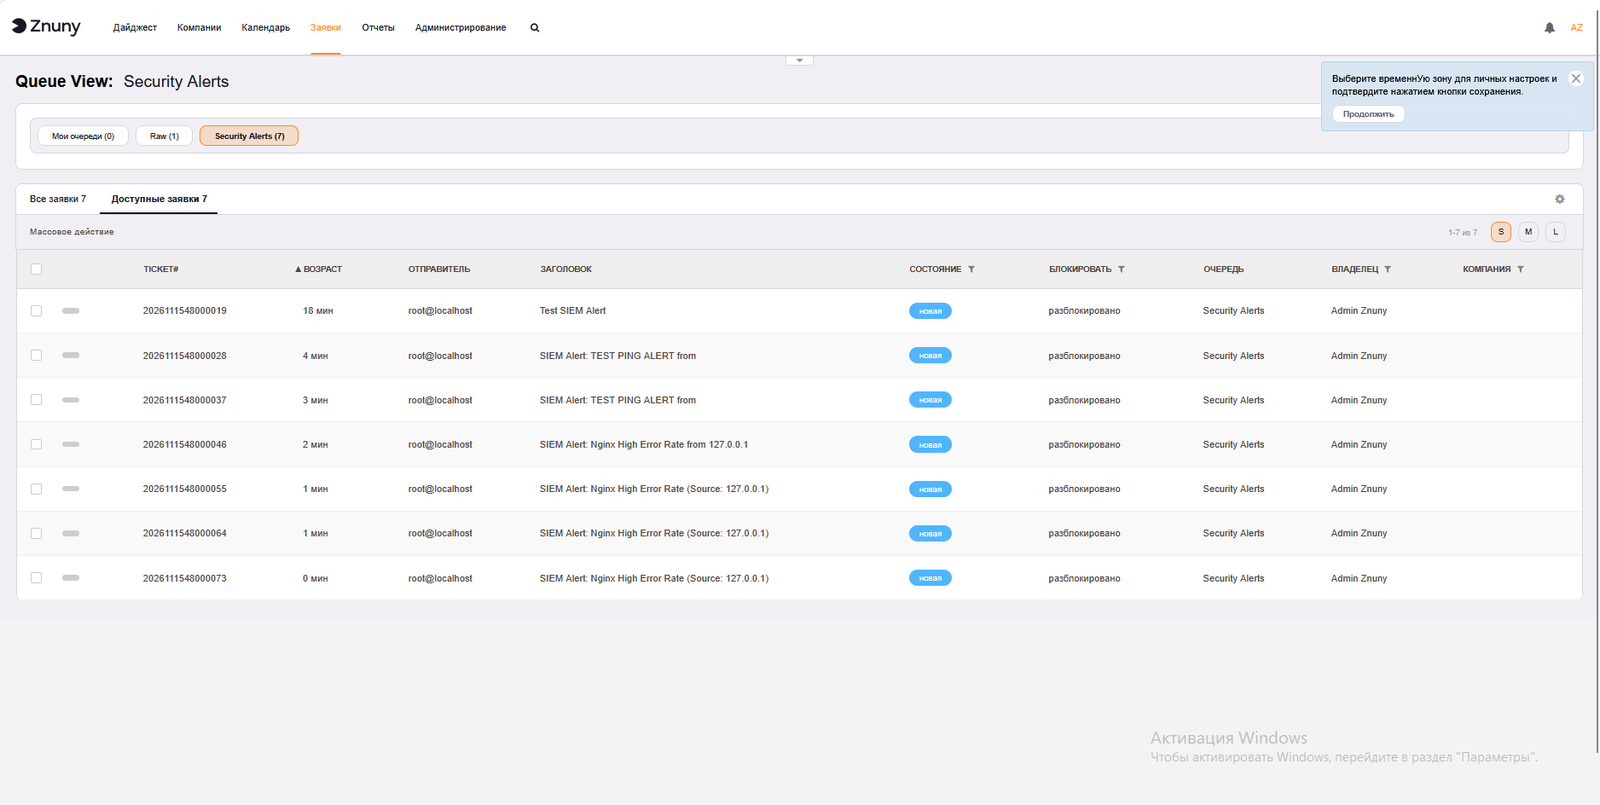
ITSM-query

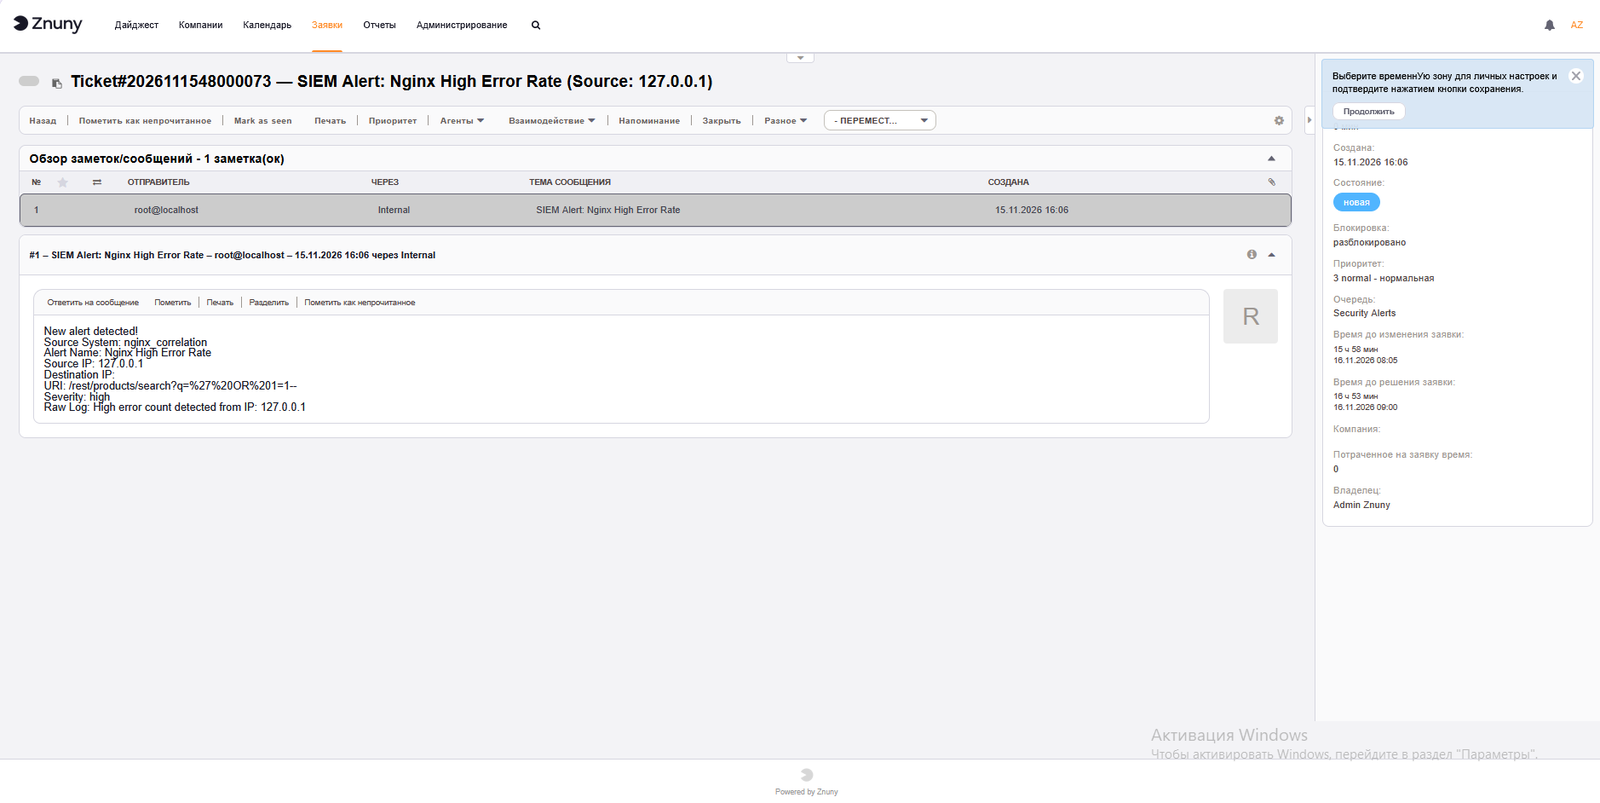
Alert in ITSM:

ITSM-alert


👤 Author:

Belov Sergey - @cybersec_road

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    491
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    462
  • 3

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    345
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    340
  • 5

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    306
  • 6

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    292

Explore all tools

Browse our collection of tools

View all tools →