
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-83834 — Analysis of a use-after-free race in FSRendezvousServer::PublishRx and ConsumeTx, where Close() can free an FSStreamReg object between mutex release and lock acquisition. | Kitploit
Tools/GitHubGitHub/wkpwn/cve-2026-83834
Memory ForensicsVulnerability AnalysisExploitation
GitHubwkpwn/cve-2026-83834

CVE-2026-83834

Analysis of a use-after-free race in FSRendezvousServer::PublishRx and ConsumeTx, where Close() can free an FSStreamReg object between mutex release and lock acquisition.

View Repository
46521 days agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

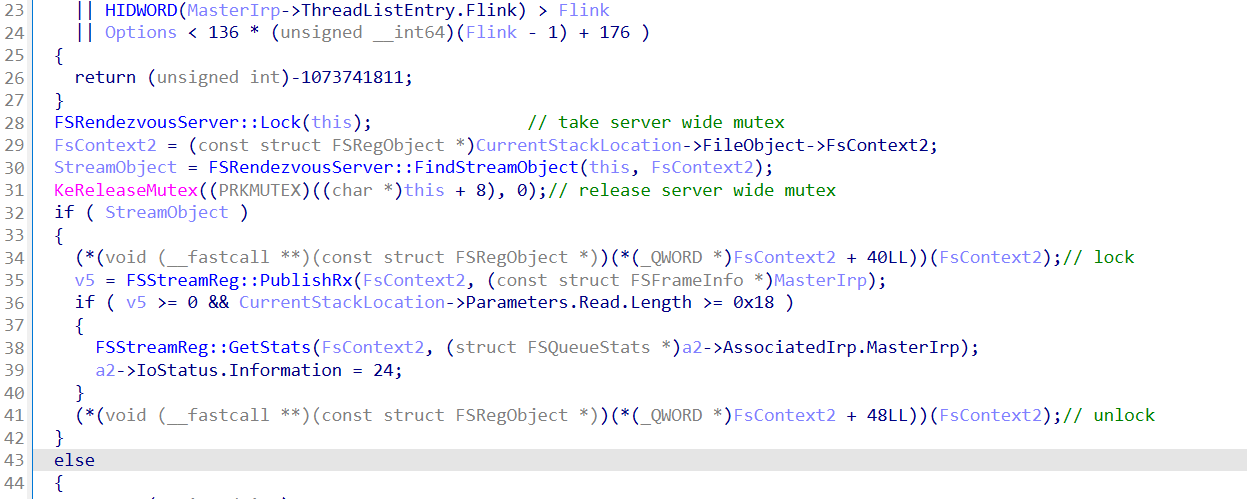
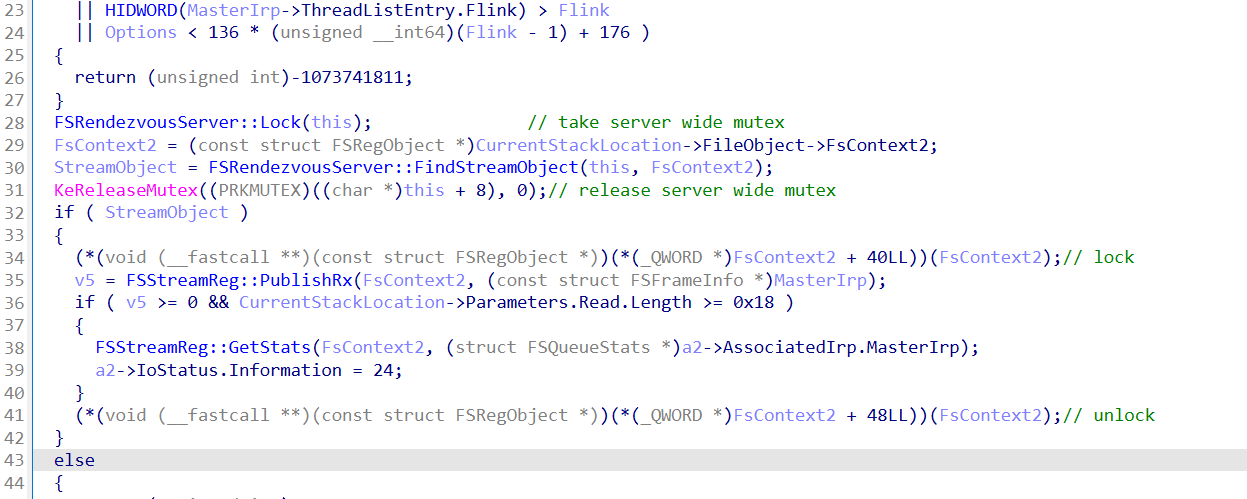
FSRendezvousServer::PublishRx and FSRendezvousServer::ConsumeTx dereference a FSStreamReg object with an identical, broken pattern: take the server mutex, confirm the object is still list-resident, drop the mutex, then take the object's own lock — with nothing in between to keep it alive.
image

Because no reference is taken, there is a narrow window between the server mutex being released and the object's own lock being taken during which FSRendezvousServer::Close() can free the object, leading to a use-after-free.

Credit: @zoverin

Download Tool