 rimbadirgantara/opac-fast-automation
automation untuk CVE-2025-65862

⚠️ Ethical & Legal Warning All materials in this repository are provided solely for:
- security research,
- learning,
- vulnerability analysis,
- and testing in environments you own or have explicit permission to test.
Exploiting, misusing bugs, or uploading malicious files to third-party servers without permission is illegal and violates Indonesian law (UU ITE) as well as international law.
The author is not responsible for any misuse of the described tools or techniques.
In SLiMS Bulian 9.7.2, there is a misconfiguration when a user (with weak credentials) uploads a plugin ZIP file.
The flow:
.php files.└── myplugin/
└── shell.php
If you manage SLiMS, look out for the following:
/plugins//plugins/ directory and remove unknown files.This script is used to:
| Flag | Function |
|---|---|
| -l | Path to a file listing target SLiMS instances |
| -f | Plugin ZIP to test (contains research payload/backdoor) |
| -o | To save results |
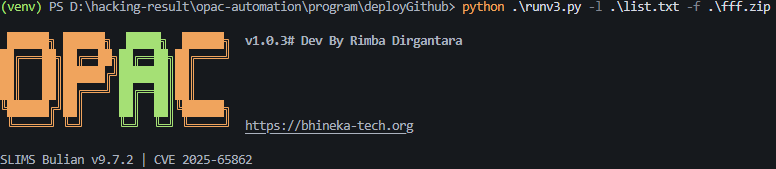
Install the following libraries before running the tool: pip install httpx beautifulsoup4 urllib3
Built-in Python libraries (no installation needed):
This repository uses a Proprietary — All Rights Reserved license to ensure the research tool is not misused by irresponsible parties.
You are not allowed to:
This repository is created as vulnerability documentation, technical analysis, and testing tool development.
Use it ethically and professionally.
