
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-29885 — Apache Tomcat CVE-2022-29885 | Kitploit
Tools/GitHubGitHub/quynhlab/cve-2022-29885
Vulnerability AnalysisExploitationWeb SecurityPenetration Testing
GitHubquynhlab/cve-2022-29885

CVE-2022-29885

Apache Tomcat CVE-2022-29885

View Repository
52224 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    647
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    421
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    389
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    333
  • 6

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    331

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2022-29885

The tool is only used for security research. It is prohibited to use the tool to launch illegal attacks, and the user is responsible for the consequences

工具仅用于安全研究以及内部自查,禁止使用工具发起非法攻击,造成的后果使用者负责

Introduce

Apache Tomcat DoS (CVE-2022-29885) Exploit

Denial of Service in EncryptInterceptor (Tomcat Cluster)

The target machine needs to start the Cluster Nio Receiver,Sending a special TCP packet will cause a Denial of Service to the target. Whether EncryptInterceptor is used or not, there is the possibility of denial of service vulnerability

Condition: Enable tomcat cluster function and use NioReceiver for communication

Any version of Tomcat will be affected. The only solution is to use a trusted network

Unsafe Config Exploit

Unsafe config: not use EncryptInterceptor

server.xml

<Cluster className="org.apache.catalina.ha.tcp.SimpleTcpCluster">
  <Channel className="org.apache.catalina.tribes.group.GroupChannel">
    <Receiver className="org.apache.catalina.tribes.transport.nio.NioReceiver"
      address="0.0.0.0"
      port="5000"
      selectorTimeout="100"
      maxThreads="6"/>
  </Channel>
</Cluster>

exploit: ./dos -h target_ip -p target_nio_port
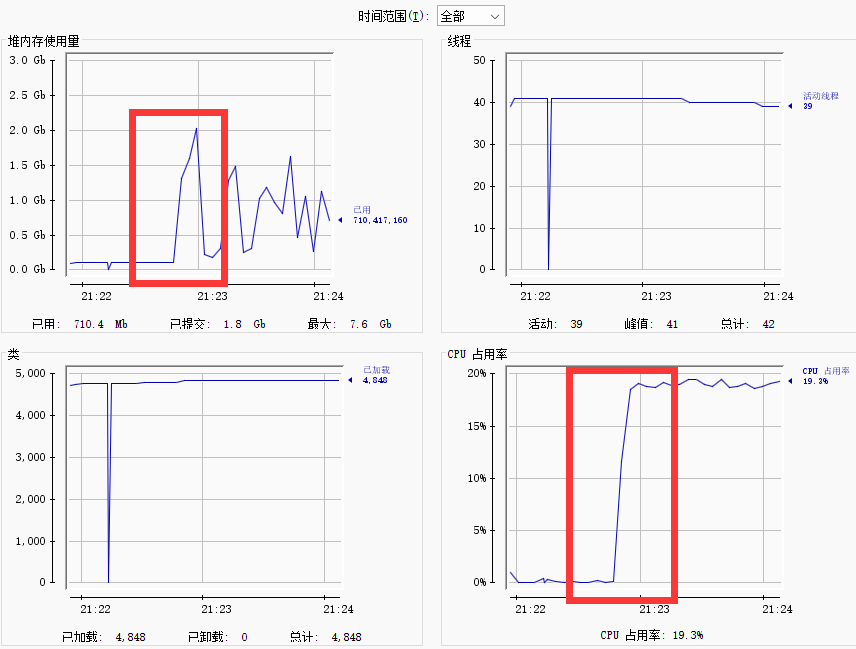
In unsafe config, you can use Safe-Config-Exploit as well

But in safe config, you can only use Safe-Config-Exploit

Safe Config Exploit

Safe config: use EncryptInterceptor

server.xml

<Cluster className="org.apache.catalina.ha.tcp.SimpleTcpCluster">
  <Channel className="org.apache.catalina.tribes.group.GroupChannel">
    <Receiver className="org.apache.catalina.tribes.transport.nio.NioReceiver"
      address="0.0.0.0"
      port="5000"
      selectorTimeout="100"
      maxThreads="6"/>
    <Interceptor className="org.apache.catalina.tribes.group.interceptors.EncryptInterceptor"
       encryptionAlgorithm="AES/CBC/PKCS5Padding"
       encryptionKey="ANY_KEY(LENGTH:32)"/>
  </Channel>
</Cluster>

exploit: ./dos -h target_ip -p target_nio_port -s
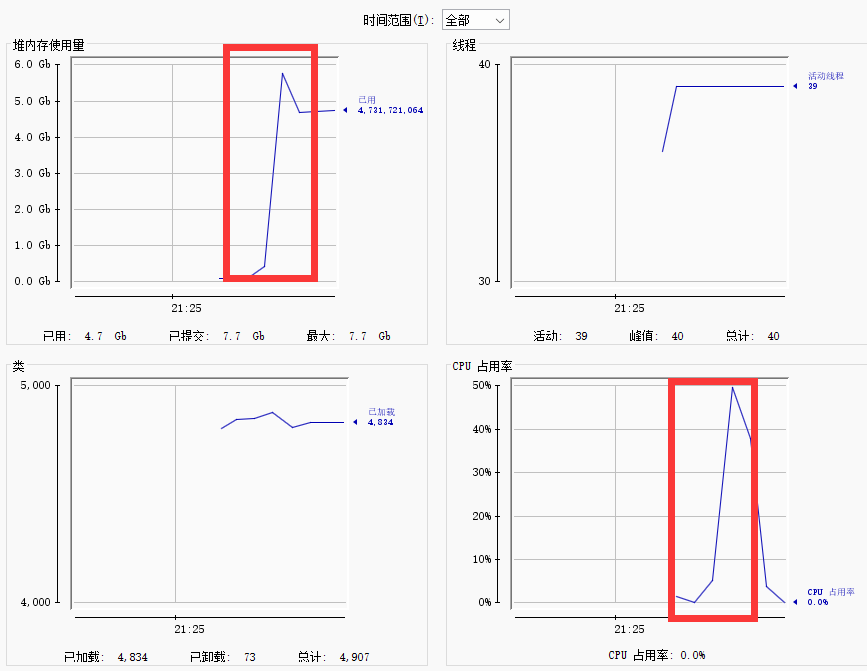
Reference

https://lists.apache.org/thread/2b4qmhbcyqvc7dyfpjyx54c03x65vhcv

Download Tool



