
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
batchOverflow — A fix for the batchOverflow bug https://medium.com/@peckshield/alert-new-batchoverflow-bug-in-multiple-erc20-smart-contracts-cve-2018-10299-511067db6536 | Kitploit
Tools/GitHubGitHub/phzietsman/batchoverflow
Static AnalysisVulnerability AnalysisCode AnalysisLearning & Education
GitHubphzietsman/batchoverflow

batchOverflow

A fix for the batchOverflow bug https://medium.com/@peckshield/alert-new-batchoverflow-bug-in-multiple-erc20-smart-contracts-cve-2018-10299-511067db6536

View Repository
328 years agoNot yet reviewed
Share

batchOverflow

Build Status

A fix for the batchOverflow bug found by the PeckShield team.

a fix

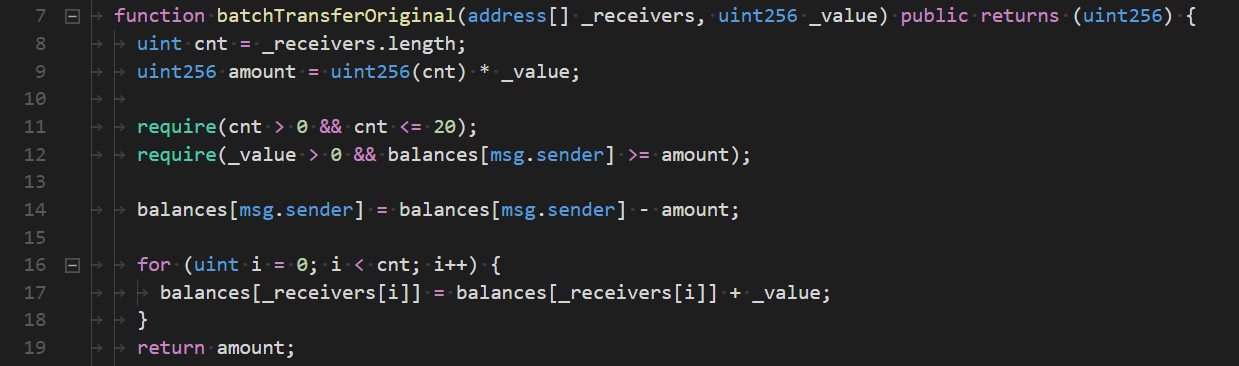
The original contract only did a check to ensure the sender has enough whatever to pay the total amount (input value x number of addresses). If an overflow ocurred this amount can be zero, which would allow the test on line 12 to pass.
execute

One possible fix is to add another test to check if the sender's balance minus the amount is less than his current balance. If a overflow ocurred the balances would be same, making it an invalid transaction. This however will still not fix the problem. If the attacker has a small balance, say 10 whatever, the attacker could craft _value to overflow to some amount smaller than the current balance they currently hold and thereby passing this gate.

Better fix would be to simply check if the total amount that transferred is greater or equal that _value. If an overflow occurred, this test would not pass. For an attacker to get past this gate they would need a minimum of a that magical number / 20, which is still a very large amount and probably impossible to get without exploiting another bug.

test it

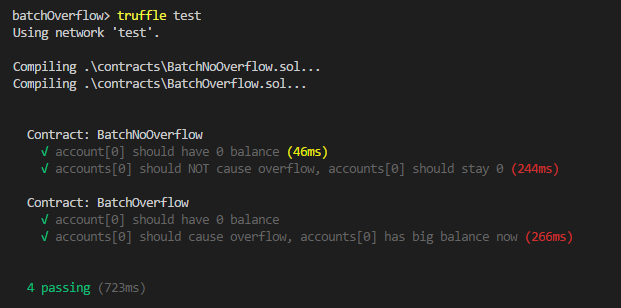
Ensure that you have truffle installed and run the truffle test command from the root of your project. It should look something like this.

execute

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →





