Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
GreatXML — GreatXML bitlocker bypass vulnerability | Kitploit
Tools/GitHubGitHub/msnightmare/greatxml
Privilege EscalationVulnerability AnalysisExploitationForensicsPost-ExploitationPenetration TestingRed TeamingIncident ResponseRepository Deleted
GitHubmsnightmare/greatxml

GreatXML

GreatXML bitlocker bypass vulnerability

The upstream repository was not found during the latest Kitploit update check. This listing remains available for reference, but it has been removed from search results.
614241103 months agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

GreatXML

GreatXML bitlocker bypass vulnerability

Steps to reproduce,

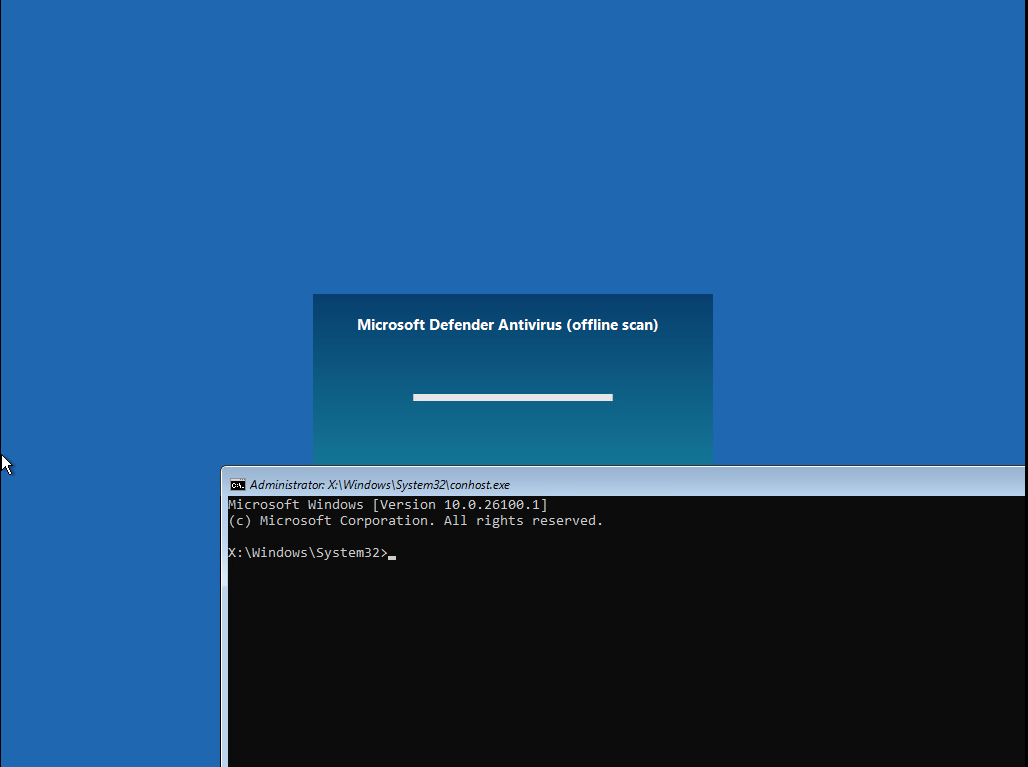
  1. If defender offline scan was initiated in the victim machine at any point then there is no need to login, the machine is automatically vulnerable. You will have to copy "unattend.xml" and "Recovery" directory to the root of the recovery partition then reboot to WinRE using shift + click on restart button, if everything was done correctly, a shell with unrestricted access to the bitlocker volume will spawn.
  2. If defender offline scan was never initiated then you have to either login and initiate it yourself or figure out a way to boot into WinRE in offline scan state (I believe it should be very possible to do so without logging in) and follow steps above

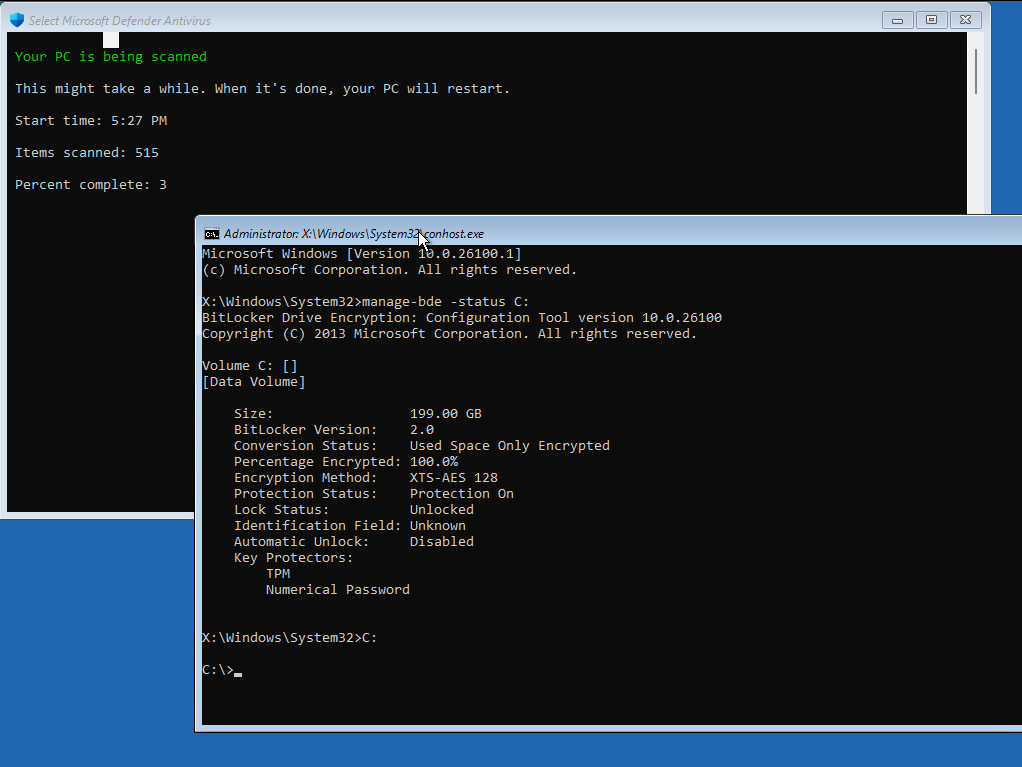
If everything is done properly, this should be the result
BottomText TopText