 mor-golan/cve-2026-112869
Proof-of-concept for CVE-2026-112869, an unauthenticated reflected XSS in the We're Open! WordPress plugin (<=2.6): a shell script verifies payload reflection and generates cross-origin auto-submit pages.

| CVE | CVE-2026-112869 |
| Plugin | We're Open! (opening-hours) |
| Affected | <= 2.6 |
| Fixed in | 2.7 |
| Severity | CVSS 7.1 High |
| Attacker needs | No account. A victim only has to open a page the attacker controls. |
| Advisory | Patchstack |
| Writeup | mor-golan.github.io/research/cve-2026-112869-opening-hours |
We're Open! registers the AJAX action we_are_open_wp_ajax for logged out visitors with its default settings. I found that the handler passes elements[0][content] through wp_kses_stripslashes() with an allowed HTML list as a second argument. That function takes only one argument and does not filter tags, so the value comes back unfiltered in a JSON response that admin-ajax.php serves as text/html. A page on any other origin can auto submit a cross site POST to this action, and the payload then runs as JavaScript in the WordPress site's origin in the visitor's browser.
1. Check the reflection. The script sends one unauthenticated POST and reports whether the payload comes back as live markup. The target comes from the first argument or the TARGET environment variable and defaults to http://localhost:8080.
chmod +x poc-opening-hours-2.6-unauth-reflected-xss.sh
./poc-opening-hours-2.6-unauth-reflected-xss.sh http://localhost:8080
# or
TARGET=http://localhost:8080 ./poc-opening-hours-2.6-unauth-reflected-xss.sh
Exit status: 0 reproduced, 1 not reproduced, 2 the request failed or the response was empty.
2. Show the script executing in a browser. The script also writes poc-oh-attacker-page.html, pointed at the target. Serve it from a different origin (a different port is enough) and open it:
python3 -m http.server 8000
# then open http://localhost:8000/poc-oh-attacker-page.html in a browser
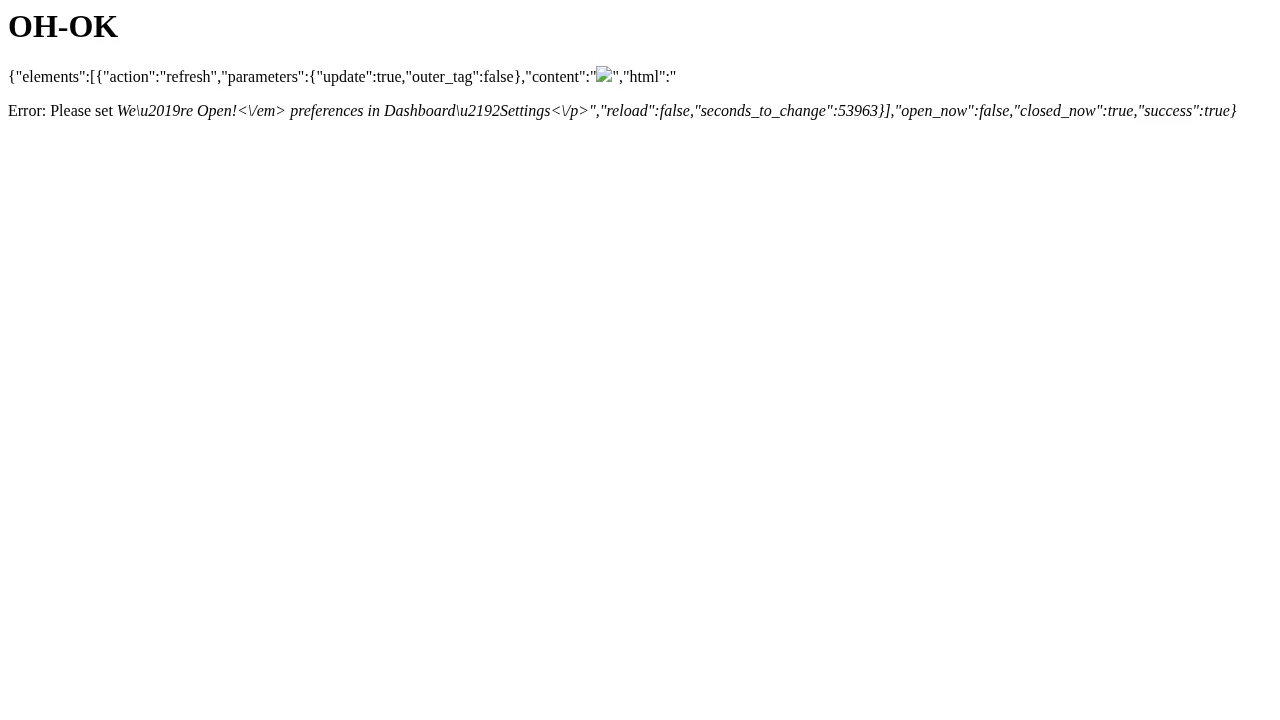
The form submits itself and the browser lands on the target's admin-ajax.php. The resulting page is headed OH-OK, the tab title reads OH-OK, window.OHPROOF === "OH-OK" and location.origin is the target. OH-OK is built from character codes inside the browser and never appears in the request, so it shows up only if the injected script ran.
The two static pages work the same way. They target http://localhost:8080, so edit the form action for another host, then serve them from a different origin and open them.
| File | Purpose |
|---|---|
poc-opening-hours-2.6-unauth-reflected-xss.sh | Sends the unauthenticated request, prints the reflected content value, writes an attacker page for the target, and exits with the result. |
poc-cross-origin-autosubmit.html | Auto submitting attacker page. The payload computes OH-OK and writes it into the page title and a heading. |
poc-reflected-xss.html | Auto submitting attacker page. The payload sets window.XSSFIRED = 1 and rewrites the page title to the site's domain. |
images/cross-origin-xss-executed.png | The page the browser landed on after the cross site delivery, headed OH-OK. |
For authorized security testing and education only. Run it only against systems you own or are permitted to test.
Found and reported by Mor Golan, Israeli CVE hunter and bug bounty hunter.






