
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Ashwesker-CVE-2025-52691 β€” CVE-2025-52691 | Kitploit
Tools/GitHubGitHub/mohammadzarnian1357/ashwesker-cve-2025-52691
Vulnerability ScannersVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubmohammadzarnian1357/ashwesker-cve-2025-52691

Ashwesker-CVE-2025-52691

CVE-2025-52691

View Repository
3210 months agoNot yet reviewed

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    951
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    683
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    427
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    392
  • 5

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    344
  • 6

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    336

Explore all tools

Browse our collection of tools

View all tools β†’
Share

🚨 CVE-2025-52691 β€” Critical SmarterMail Vulnerability

smartermail-vulnerability-divd

Status: πŸ”₯ Critical β€” Immediate action required CVSS v3.1 Score: 10.0 / 10 Disclosure Date: December 29–30, 2025


🧩 Vulnerability Summary

CVE-2025-52691 is a critical, unauthenticated arbitrary file upload vulnerability affecting SmarterTools SmarterMail Server. Exploitation can lead directly to Remote Code Execution (RCE) and full server compromise.


🎯 Key Technical Details

CategoryDetails
ProductSmarterTools SmarterMail
Affected VersionsBuilds ≀ 9406
Fixed VersionBuild 9413 or later
Attack Vector🌐 Network
Authentication Required❌ None
User Interaction❌ None
CWECWE-434 β€” Unrestricted File Upload
Impact ScopeChanged
ConfidentialityπŸ”΄ High
IntegrityπŸ”΄ High
AvailabilityπŸ”΄ High

CVSS Vector:

CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H

πŸ’₯ What an Attacker Can Do

An unauthenticated remote attacker can:

βœ… Upload arbitrary files to any server location βœ… Place malicious executables or web shells βœ… Execute arbitrary code on the mail server βœ… Gain full system control βœ… Abuse mail infrastructure for spam, phishing, or lateral movement

⚠️ Because mail servers are usually Internet-exposed, the real-world risk is extremely high.


🧨 Risk Assessment

FactorRisk
Exploit Complexity🟒 Low
Privileges Needed🟒 None
ExposureπŸ”΄ Internet-facing
Potential DamageπŸ”΄ Full compromise

Overall Risk Level: 🚨 CRITICAL


πŸ› οΈ Mitigation & Remediation (Urgent)

βœ… Immediate Actions

  1. Upgrade SmarterMail to Build 9413 or later
  2. Restrict external access until patching is complete
  3. Review server file systems for unexpected uploads
  4. Check logs for suspicious POST/upload activity
  5. Rotate credentials if compromise is suspected

πŸ•΅οΈ Exploitation Status

  • 🚫 No widely published public PoC (as of now)

  • ⚠️ High likelihood of active exploitation due to:

    • CVSS 10.0
    • Unauthenticated access
    • Internet-facing service
    • Simple attack path

🏷 Attribution

  • CVE Assigned By: Cyber Security Agency (CSA), Singapore

  • Referenced By:

    • NVD (NIST)
    • CSA Singapore
    • National CERT advisories (EU & APAC)

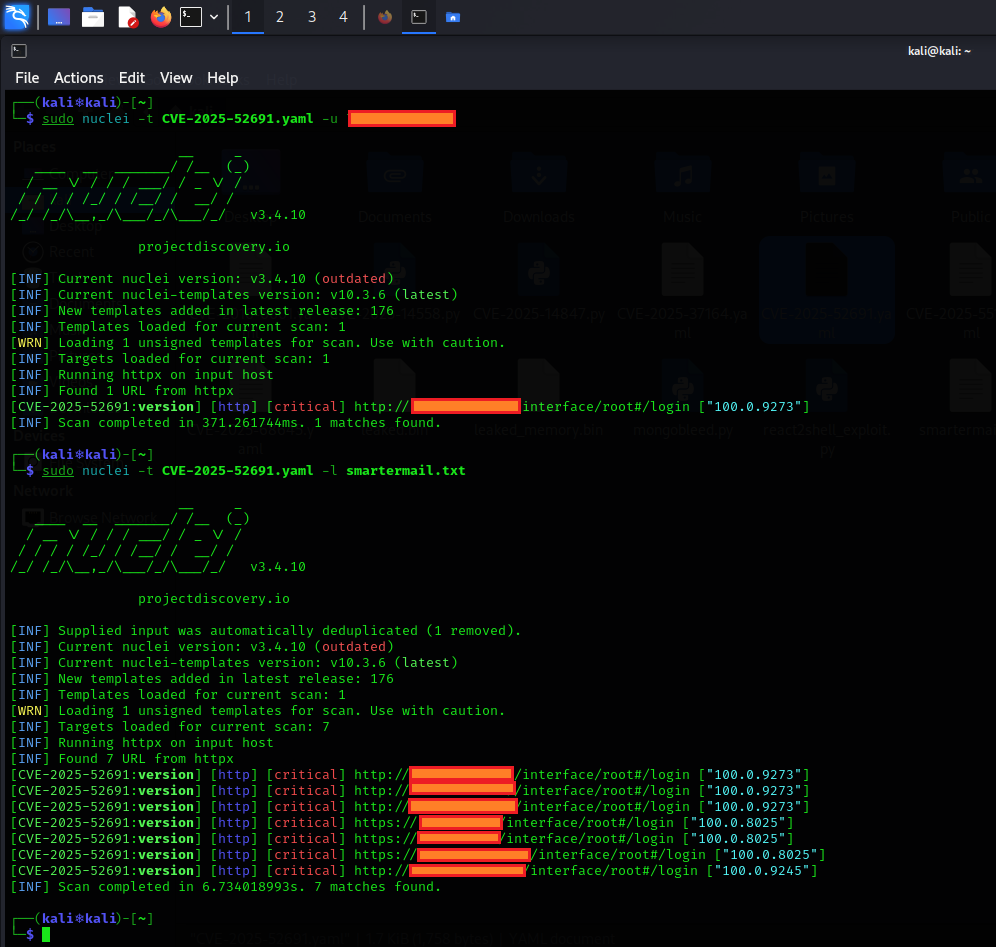
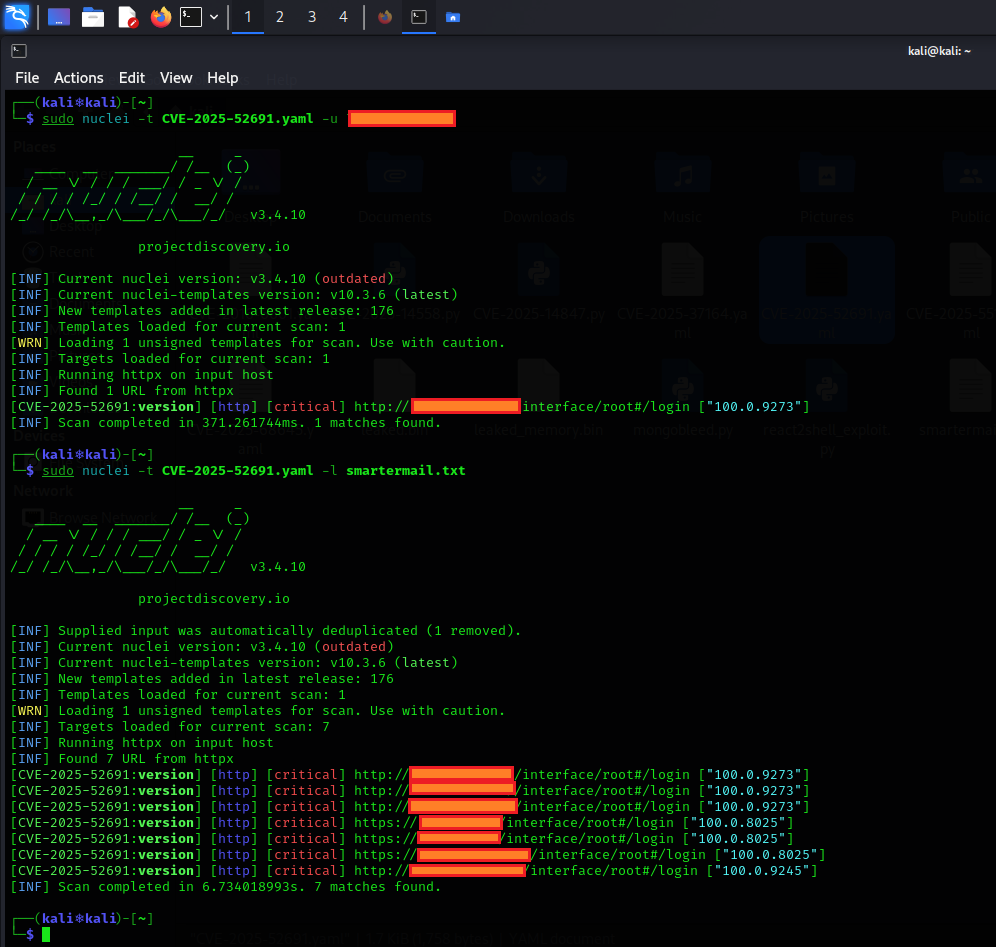
Here are the short steps to run the Nuclei detection template for CVE-2025-52691:

  1. Save the template

    Copy the YAML into a file: cve-2025-52691.yaml

  2. Install/Update Nuclei (if needed)

    go install -v github.com/projectdiscovery/nuclei/v3/cmd/nuclei@latest
    
  3. Run on a single target

    nuclei -t cve-2025-52691.yaml -u https://your-smartermail-domain.com
    
  4. Run on multiple targets (from a file called targets.txt)

    nuclei -t cve-2025-52691.yaml -l targets.txt
    
  5. Optional useful flags

    • -v β†’ see more details
    • -o results.txt β†’ save output
    • -silent β†’ show only matches

That's it! If it finds a vulnerable version (< Build 9413), it will alert you.
smartermail

Reminder: Only scan systems you own or have permission for. 😊

Download Tool