
 md-thalal/cve-2023-29489
CVE-2023-29489 is a vulnerability to exploitable in cross-site scripting ( xss ) reflect the cpanel



An exploitable reflected cross-site scripting (XSS) vulnerability has been discovered in certain versions of cPanel and was assigned with CVE-2023-29489. This vulnerability allows attackers to execute arbitrary JavaScript code without requiring authentication. The XSS vulnerability can still be exploited even if the cPanel management ports are not externally exposed. Websites on ports 80 and 443 are also susceptible to this vulnerability if they are managed by cPanel.
An issue was discovered in cPanel before 11.109.9999.116. Cross-Site Scripting can occur on the cpsrvd error page via an invalid webcall ID.
pip install CVE-2023-29489
CVE-2023-29489 -h
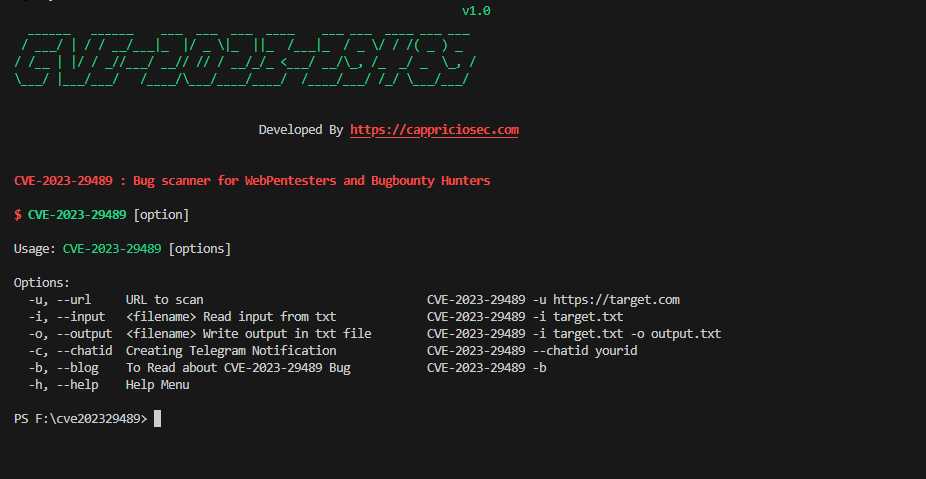
| Options | Description | Examples |
|---|---|---|
| -u, --url | URL to scan | CVE-2023-29489 -u https://target.com |
| -i, --input | Read input from txt | CVE-2023-29489 -i target.txt |
| -o, --output | Write output in txt file | CVE-2023-29489 -i target.txt -o output.txt |
| -c, --chatid | Creating Telegram Notification | CVE-2023-29489 --chatid yourid |
| -b, --blog | To Read about CVE-2023-29489 Bug | CVE-2023-29489 -b |
| -h, --help | Help Menu |
                                                                           v1.0
   _______    ________    ___   ____ ___  ___       ___  ________________
  / ____/ |  / / ____/   |__ \ / __ \__ \|__ \     |__ \<  /__  /__  <  /
 / /    | | / / __/________/ // / / /_/ /__/ /_______/ // / /_ <  / // /
/ /___  | |/ / /__/_____/ __// /_/ / __// __/_____/ __// /___/ / / // /
\____/  |___/_____/    /____/\____/____/____/    /____/_//____/ /_//_/

                              Developed By https://cappriciosec.com


CVE-2022-21371 : Bug scanner for WebPentesters and Bugbounty Hunters

$ CVE-2022-21371 [option]

Usage: CVE-2022-21371 [options]

Options:
  -u, --url     URL to scan                                CVE-2022-21371 -u https://target.com
  -i, --input   <filename> Read input from txt             CVE-2022-21371 -i target.txt
  -o, --output  <filename> Write output in txt file        CVE-2022-21371 -i target.txt -o output.txt
  -c, --chatid  Creating Telegram Notification             CVE-2022-21371 --chatid yourid
  -b, --blog    To Read about CVE-2022-21371 Bug           CVE-2022-21371 -b
  -h, --help    Help Menu


Website : https://cappriciosec.com/
Email : [email protected]






