jx0n0/yzmcmsxss
YZMCMS v3.7最新版xss漏洞 CVE-2018-8078

YZMCMS v3.7 latest version xss vulnerability
YZMCMS V3.7 Stored XSS
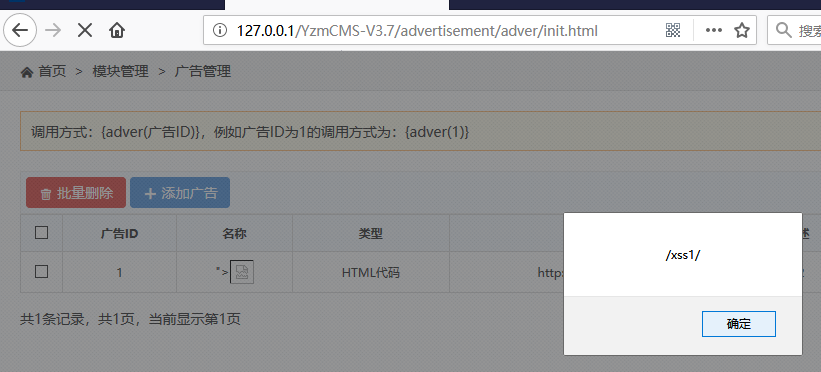
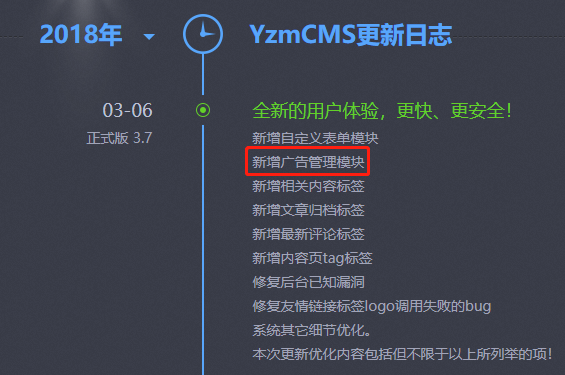
This xss exists in the newly added advertising management module in v3.7, as shown in the figure:
This xss exists in v3.7 new advertising management module, as shown in the figure:
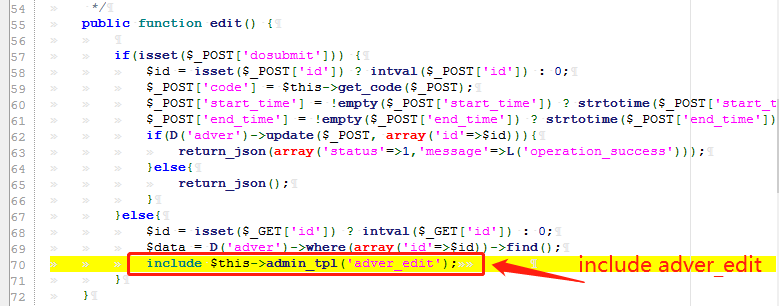
We can find the specific code of the ad management editing function in YzmCMS-V3.7\application\advertisement\controller\adver.class.php, lines 55-70, as shown in the figure:
We can find the specific code of the ad management editing function in YzmCMS-V3.7\application\advertisement\controller\adver.class.php, lines 55-70, as shown in the figure:

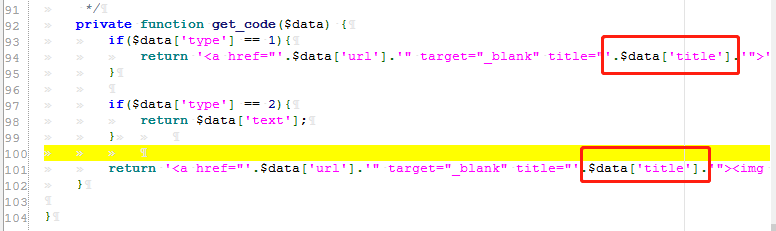
Among them, a method named getcode is called on line 59, a set of parameters is passed using the POST method, and we continue to follow the method. This method returns a $data['title'] without any filtering directly. Return the parameter to $POST_[‘code’] as shown:
Among them, a method named getcode is called on line 59, a set of parameters is passed using the POST method, and we continue to follow the method. This method returns a $data['title'] without any filtering directly. Return the parameter to $POST_[‘code’] as shown:
Let's go back to edit and continue to follow. In the edit method include includes a file called adver_edit as shown in the figure:
Let's go back to edit and continue to follow. In the edit method include includes a file called adver_edit as shown in the figure:
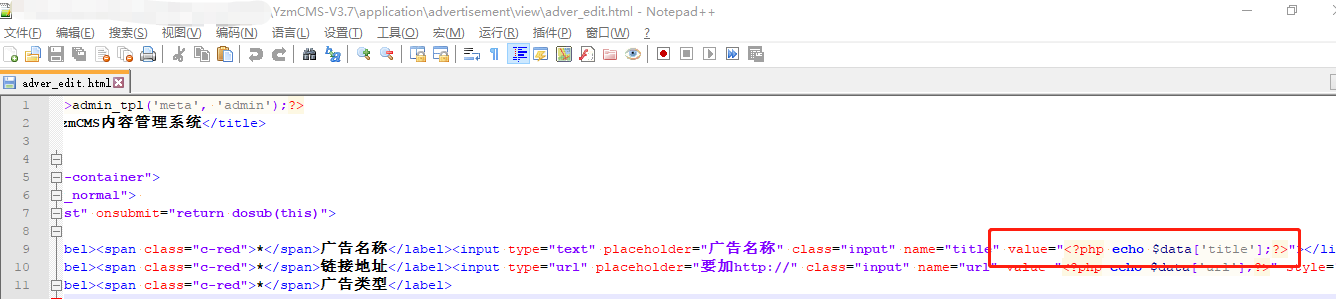
We can find the file in the path of YzmCMS-V3.7\application\advertisement\view. You can see that yzmcms does not filter any data and outputs it directly to the page, as shown in the following figure:
We can find the file in the path of YzmCMS-V3.7\application\advertisement\view. You can see that yzmcms does not filter any data and outputs it directly to the page, as shown in the following figure:
We can find this function in the background management interface, as shown in the figure:
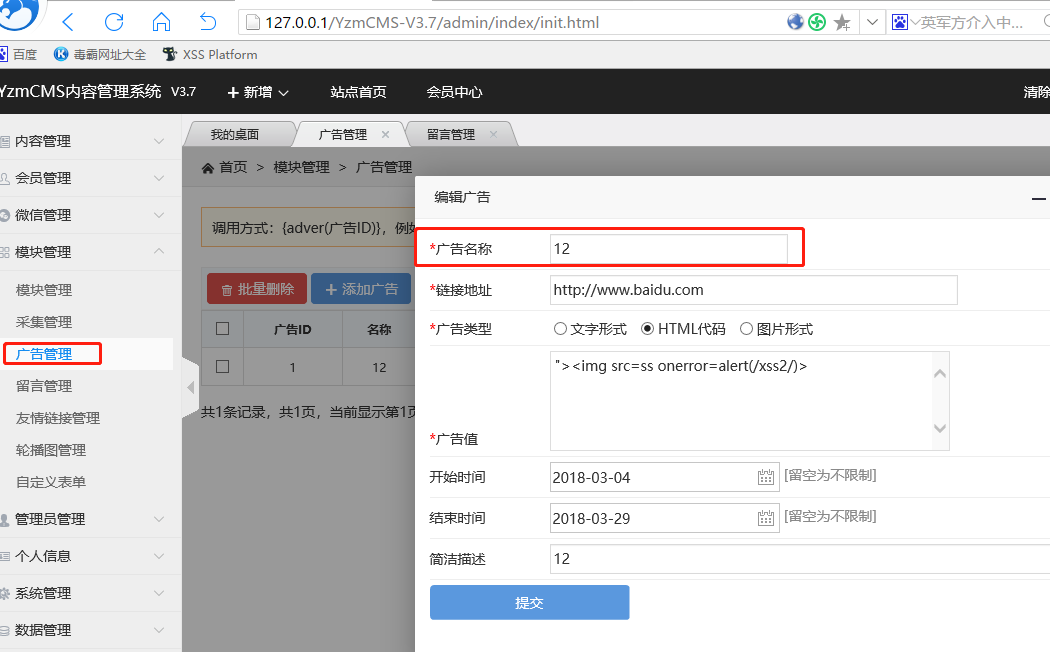
We can find this function in the background management interface, as shown in the figure:
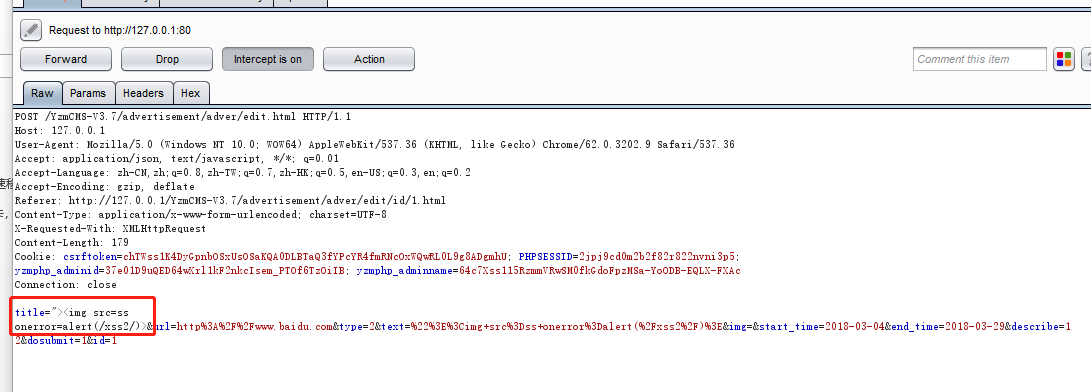
After submitting, we can use burp to intercept the data packet and change the title to ">. Click Send, as shown:
After submitting, we can use burp to intercept the data packet and change the title to ">. Click Send, as shown:
We return to the ad management interface, refresh, at this time the xss bullet is visible, as shown:
We return to the ad management interface, refresh, at this time the xss bullet is visible, as shown: