
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-4577-checker — A Bash script designed to scan multiple domains for the CVE-2024-4577 vulnerability in PHP-CGI. | Kitploit
Tools/GitHubGitHub/jeninsutradhar/cve-2024-4577-checker
ReconnaissanceVulnerability ScannersExploitationInformation GatheringWeb SecurityPenetration Testing
GitHubjeninsutradhar/cve-2024-4577-checker

CVE-2024-4577-checker

A Bash script designed to scan multiple domains for the CVE-2024-4577 vulnerability in PHP-CGI.

Share
View Repository
31292 years agoNot yet reviewed

CVE-2024-4577 Vulnerability Checker

The CVE-2024-4577 Vulnerability Checker is a Bash script designed to scan multiple domains for the CVE-2024-4577 vulnerability in PHP-CGI. This tool allows security researchers and system administrators to quickly assess whether their systems or a list of domains are potentially vulnerable to this specific security issue.

Description

In PHP versions 8.1.* before 8.1.29, 8.2.* before 8.2.20, 8.3.* before 8.3.8, when using Apache and PHP-CGI on Windows, if the system is set up to use certain code pages, Windows may use "Best-Fit" behavior to replace characters in command line given to Win32 API functions. PHP CGI module may misinterpret those characters as PHP options, which may allow a malicious user to pass options to PHP binary being run, and thus reveal the source code of scripts, run arbitrary PHP code on the server, etc.
image

Requirements

  • Bash (version 4.0 or later)
  • curl

Installation

  1. Clone the repository or download the script:
  • git clone https://github.com/JeninSutradhar/CVE-2024-4577-checker.git
  • cd cve-2024-4577-checker
  1. Make the script executable:
  • chmod +x cve_2024_4577_checker.sh

Usage

Basic Usage

./cve_2024_4577_checker.sh -f domains.txt

  • This will scan all domains listed in the domains.txt file.

Options

  • -f file: Specify a file containing a list of domains to check (one domain per line)
  • -t threads: Set the number of concurrent threads (default: 10)
  • -u user_agent: Set a custom User-Agent string
  • -i: Run in interactive mode, allowing manual input of domains
  • -h: Display the help message

Output

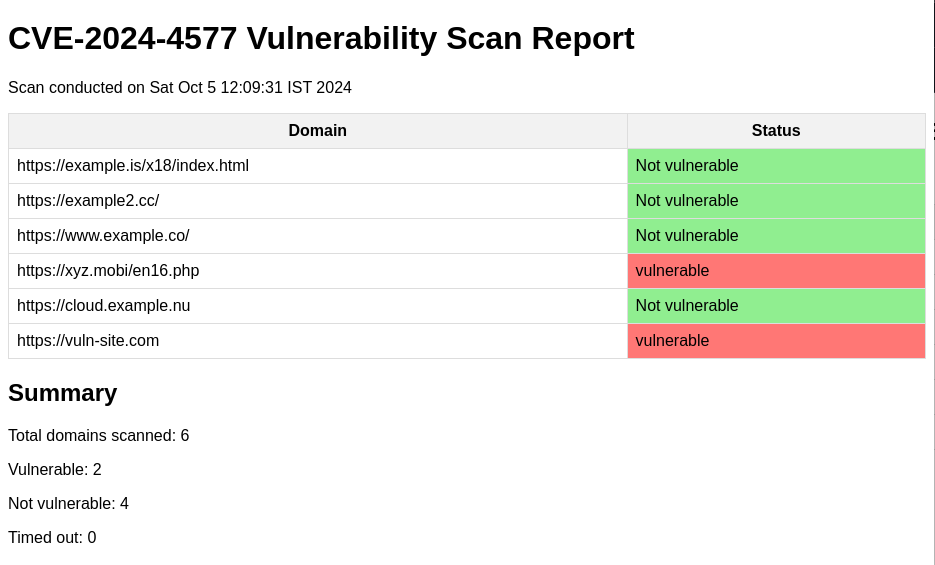
  • At the end of the scan, a summary is displayed showing:
  1. Total number of scanned domains
  2. Number of vulnerable domains
  3. Number of safe domains
  4. Number of domains that timed out
  • Additionally, two files are generated:
  1. A detailed log file (vulnerability_scan_[timestamp].log)
  2. An HTML report (vulnerability_report_[timestamp].html)

Examples

  1. Scan domains from a file:
  • ./cve_2024_4577_checker.sh -f domains.txt
  1. Scan domains with increased concurrency:
  • ./cve_2024_4577_checker.sh -f domains.txt -t 20
  1. Use a Custom User-Agent:
  • ./cve_2024_4577_checker.sh -f domains.txt -u "MyCustomUserAgent/1.0"
  1. Run in interactive mode:
  • ./cve_2024_4577_checker.sh -i

image

License

This project is licensed under the MIT License - see the LICENSE file for details.

Disclaimer

This tool is for educational and testing purposes only. Always ensure you have permission to scan the target domains. The authors are not responsible for any misuse or damage caused by this program.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    628
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    413
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    366
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    329
  • 6

    Aliens_eye

    arxhr007/aliens_eye

    AI powered OSINT engine to discover and map 7,700+ social media identities across the web

    287

Explore all tools

Browse our collection of tools

View all tools →